

Heroinn
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
command-and-controldata-exfiltrationlateral-movement+8
b23r0/heroinnA cross platform C2/post-exploitation framework.
 bishopfox/sliver
Adversary Emulation Framework
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 machine1337/telegramrat
Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
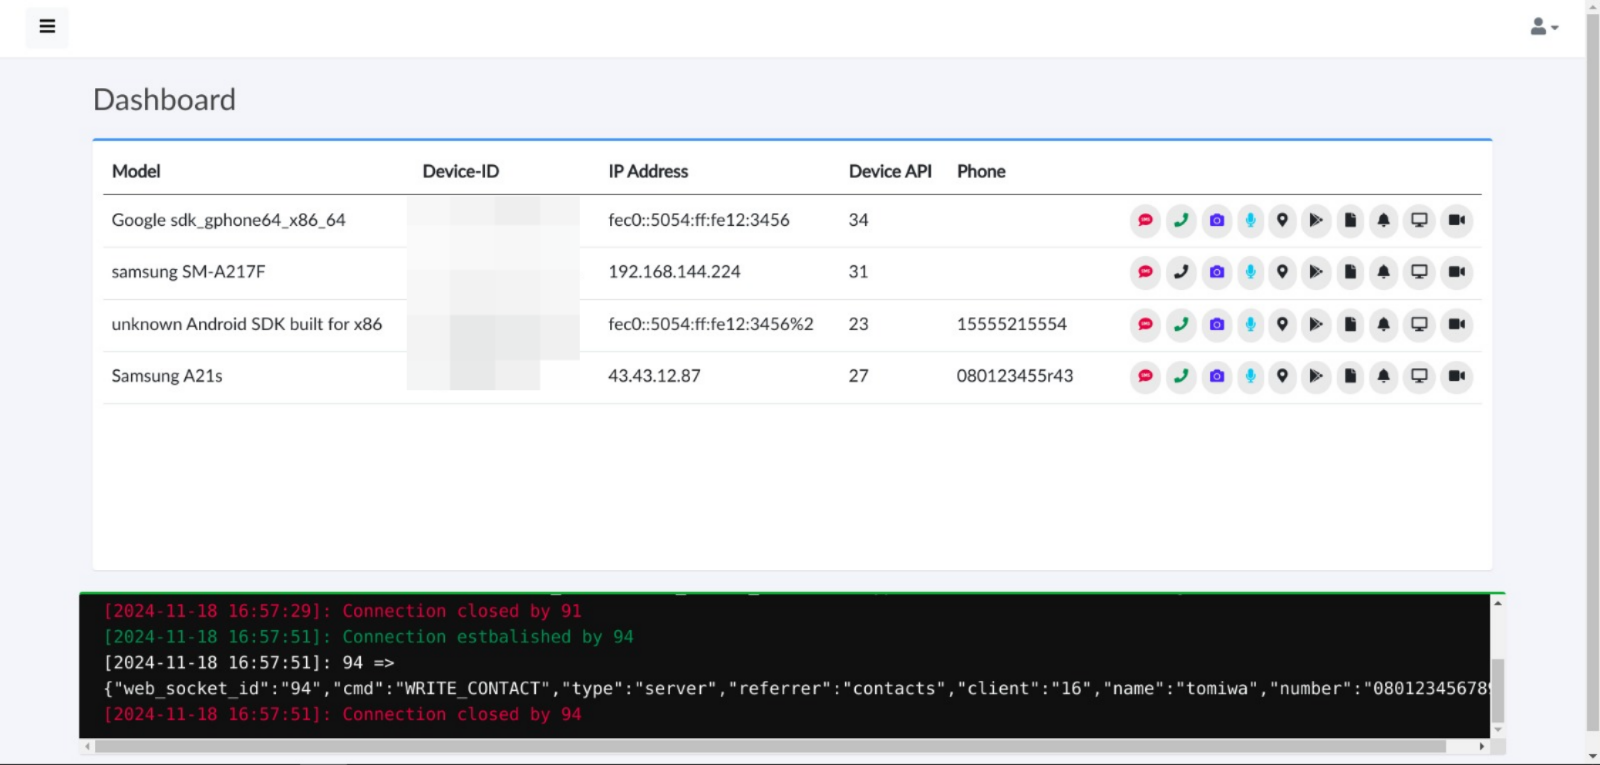 tomiwa-ot/moukthar
Android remote administration tool
 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
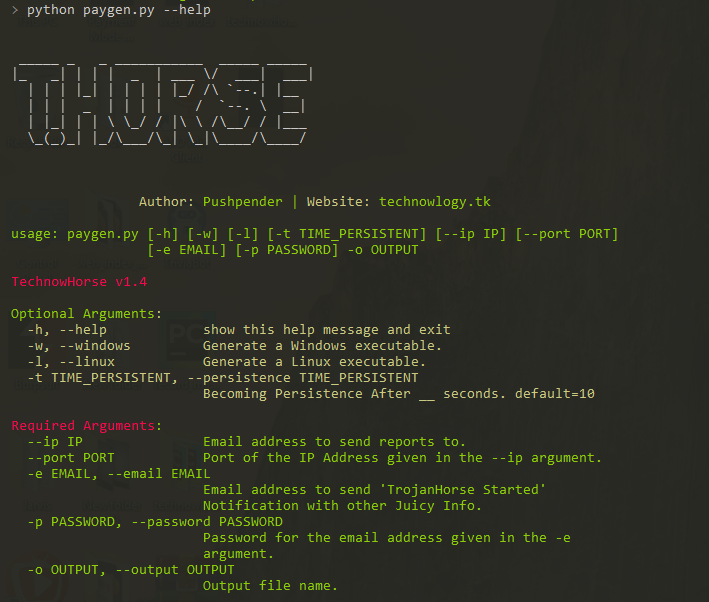 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 artbitrage/stealth-kid-rat
Stealth Kid RAT (SKR) is an open-source multi-platform Remote Access Trojan (RAT) written in C#. Released under MIT license. The SKR project is fully…
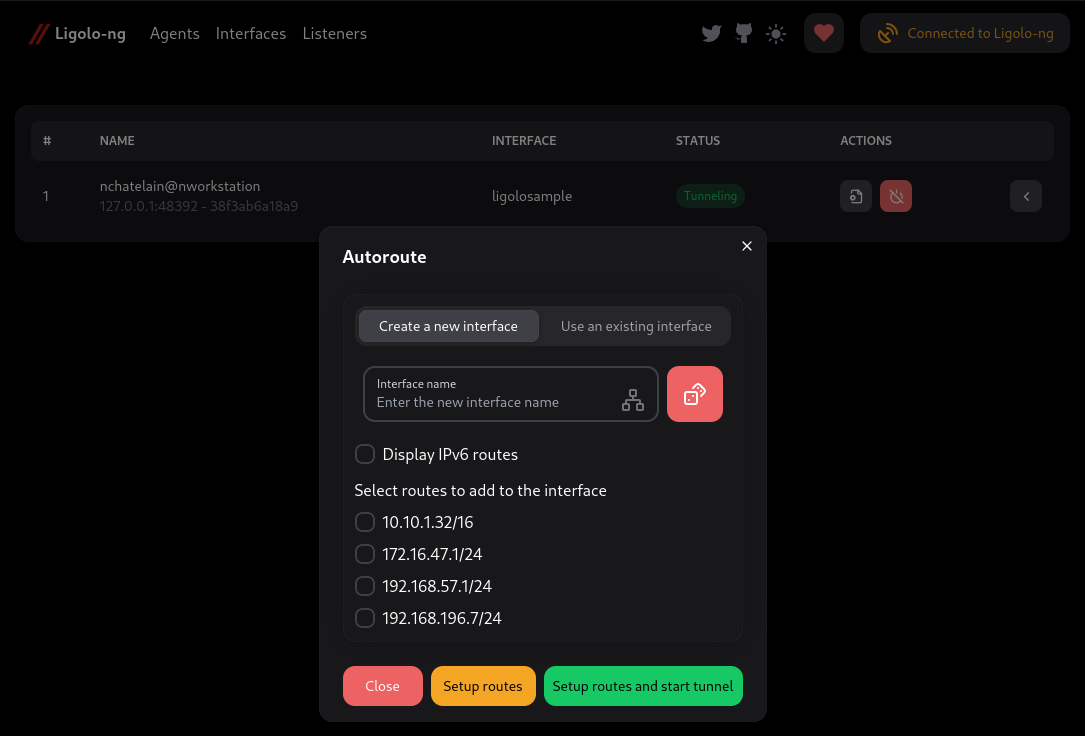 nicocha30/ligolo-ng
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 sshuttle/sshuttle
Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
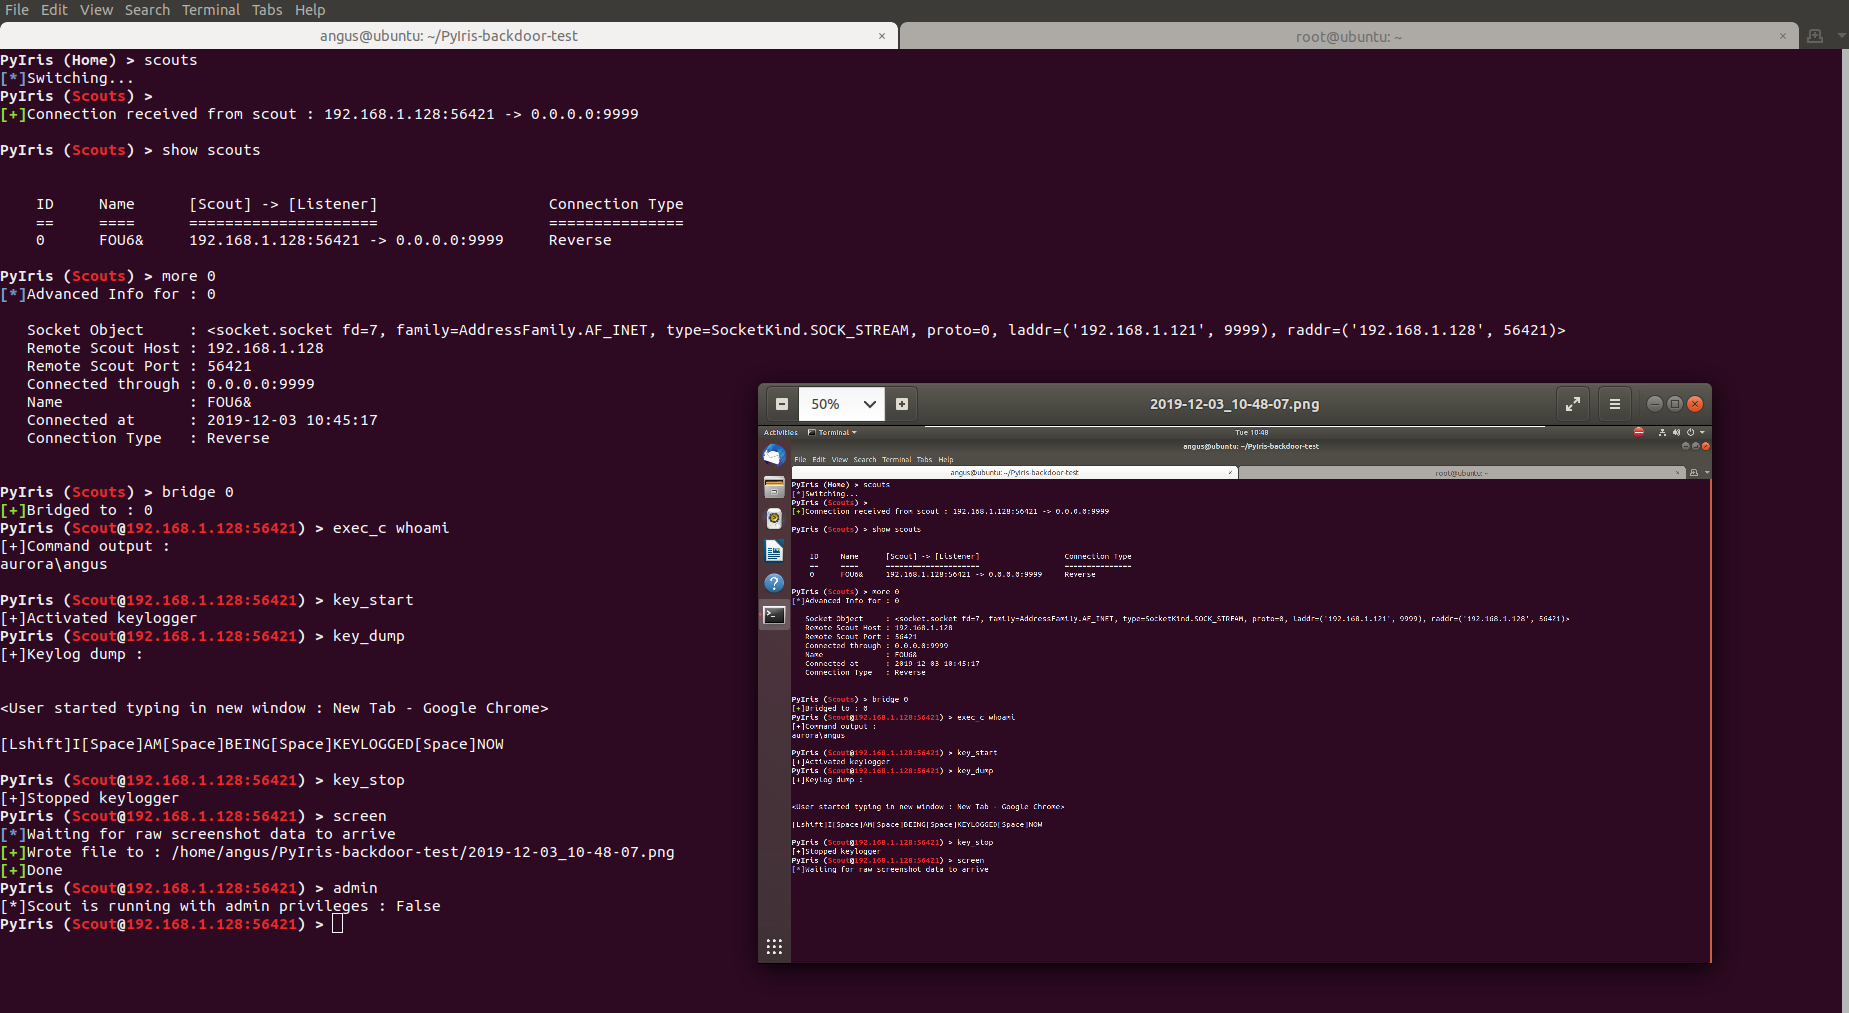 not-sekiun/pyiris
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.