

CVE-2014-6271
 0x00-0x00/cve-2014-6271
Shellshock exploitation script that is able to upload and RCE using any vector due to its versatility.
command-and-controlexploitationpayload-generation+3
3
0x00-0x00/cve-2014-6271Shellshock exploitation script that is able to upload and RCE using any vector due to its versatility.
 xl337x/cve-2023-31902
Pre-auth RCE exploit for Mobile Mouse 3.6.0.4 via TCP (port 9099) and WebSocket (port 35913) with Python scripts for unauthenticated command…
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 beichendream/cve-2022-26134-godzilla-memshell
Java-based exploit for CVE-2022-26134 that injects a Godzilla webshell into Confluence servers, enabling remote code execution with password and key…
 alessandroz/pupy
Pupy is an opensource, multi-platform (Windows, Linux, OSX, Android), multi function RAT (Remote Administration Tool) mainly written in python. It…
 34zy/microsoft-office-word-mshtml-remote-code-execution-exploit
Exploits CVE-2021-40444 in Microsoft Office Word to achieve remote code execution through the MSHTML engine by injecting malicious content into a…
 hunthubspace/cve-2024-0757-exploit
A PoC Exploit for CVE-2024-0757 - Insert or Embed Articulate Content into WordPress Remote Code Execution (RCE)
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
 shinthink/cve-2026-57517
💉 Blind SQL Injection → RCE exploit for Control Web Panel (CWP) ≤ 0.9.8.1224 — userRes POST → INTO DUMPFILE → cwpsvc shell
 rootkited/graylog-cve-2024-24824-exploit
Proof-of-concept exploit for CVE-2024-24824 demonstrating how an arbitrary class loading primitive can be transformed into remote code execution on…
 uyerr/poc_cve-2019-10149--rce
Remote Command Execution into shell from a vulnerable exim service.
 drew-alleman/cve-2020-11651
A script that exploits SaltStack CVE-2020-11651 and CVE-2020-11652 to add new users to a vulnerable Salt master by injecting entries into /etc/passwd…
 smarttfoxx/otrs-4.0.1-6.0.1-remote-command-execution
CVE-2017-16921: In OTRS 6.0.x up to and including 6.0.1, OTRS 5.0.x up to and including 5.0.24, and OTRS 4.0.x up to and including 4.0.26, an…
 nullarray/autosploit
Automated Mass Exploiter
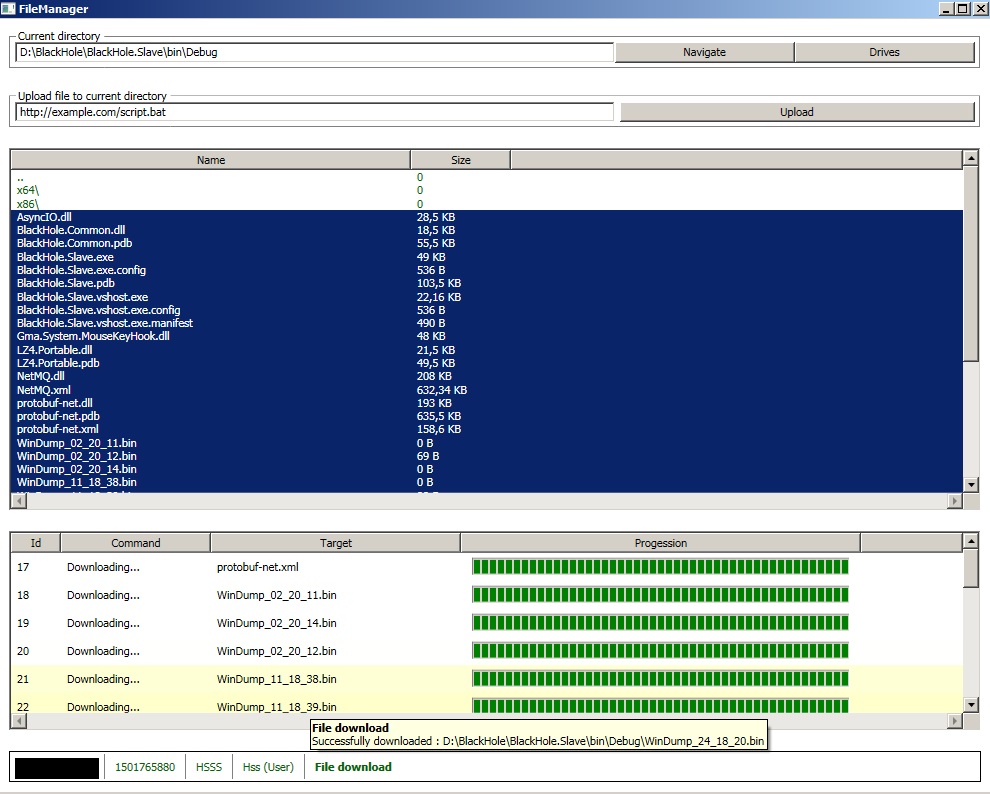 hussein-aitlahcen/blackhole
C# RAT (Remote Administration Tool)
 andreiverse/grc2
Lightweight C2 framework written in Nim for generating implants, managing listeners, and executing tasks via TCP/HTTP with a loot system for…
 0x00-0x00/-cve-2017-9805
Exploit script for Apache Struts2 REST Plugin XStream RCE (CVE-2017-9805)
 kartik2005221/cve-2025-58434-and-59528-poc
Modular PoC for CVE-2025-58434 (account takeover) and CVE-2025-59528 (RCE) in Flowise. Automates the full attack chain from unauthenticated token…