
smb-usermap
 h3x0v3rl0rd/smb-usermap
Python exploit for Samba 3.0.20-3.0.25rc3 'username map script' command injection, providing unauthenticated remote code execution and reverse shell.
exploitationpenetration-testingremote-access-tool
h3x0v3rl0rd/smb-usermapPython exploit for Samba 3.0.20-3.0.25rc3 'username map script' command injection, providing unauthenticated remote code execution and reverse shell.
 0xkn/cve-2007-2447
Python exploit for Samba CVE-2007-2447 username map script remote command execution, delivering a reverse shell payload to a configurable remote…
 wildfootw/cve-2007-2447_samba_3.0.25rc3
Exploit for Samba 3.0.0-3.0.25rc3 'Username' map script command execution vulnerability (CVE-2007-2447), enabling remote code execution.
 foudadev/cve-2007-2447
Educational exploit implementation for CVE-2007-2447 Samba 3.0.20-3.0.25rc username map script command execution vulnerability with Python SMB client…
 ziemni/cve-2007-2447-in-python
Python implementation of 'Username' map script' RCE Exploit for Samba 3.0.20 < 3.0.25rc3 (CVE-2007-2447).
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
 3x1t1um/cve-2007-2447
Python exploit for CVE-2007-2447 that triggers Samba username map script command injection to open a reverse shell on vulnerable targets.
 estebanzarate/cve-2025-47812-wing-ftp-server-7.4.3-unauthenticated-rce-poc
Proof-of-concept exploit for CVE-2025-47812: unauthenticated remote code execution in Wing FTP Server <= 7.4.3 via NULL byte injection in the…
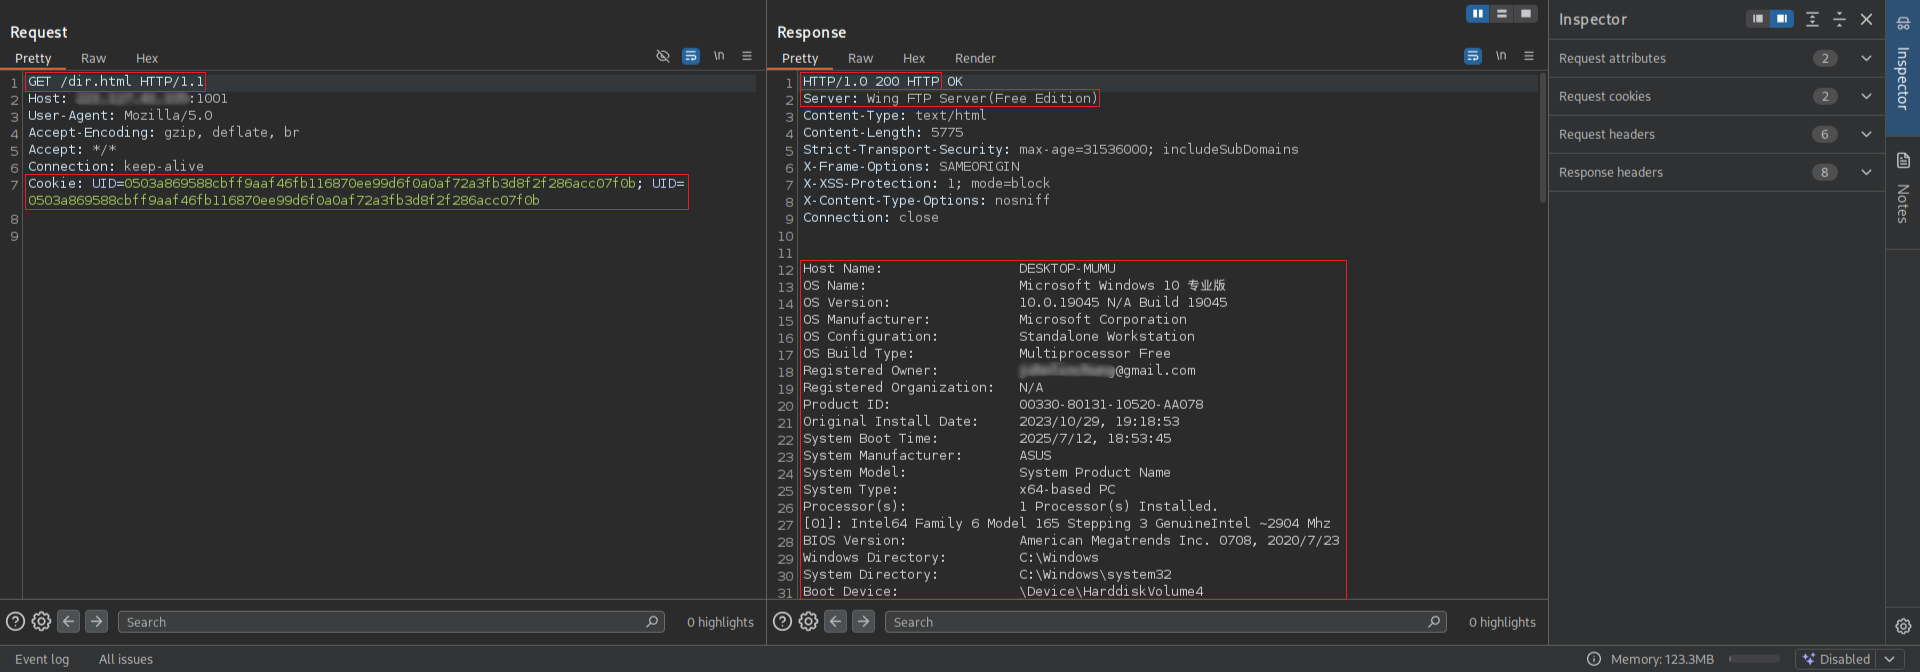 r0otk3r/cve-2025-47812
Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…
 ac8999/prtg-network-monitor-18.2.38---authenticated-remote-code-execution-cve-2018-9276
Python Exploit for CVE: 2018-9276
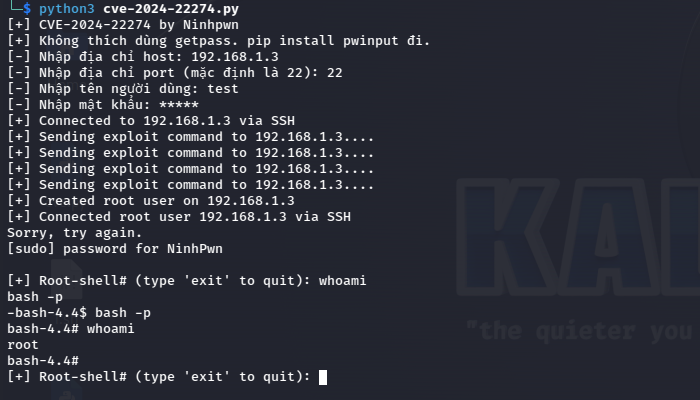 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 b33m0x00/cve-2007-2447
CVE-2007-2447 samba remote code execution
 josebarrios/cve-2007-2447
Remote Command Injection Vulnerability (CVE-2007-2447), allows remote attackers to execute arbitrary commands by specifying a Samba username…
 1d8/spybrowse
Code developed to steal certain browser config files (history, preferences, etc)
 mfernstrom/offensivepascal-cve-2011-2523
FreePascal implementation of the vsFTPD 2.3.4 CVE-2011-2523
 shivamdey/samba-cve-2007-2447-exploit
Python exploit for CVE-2007-2447 in Samba, enabling remote command execution via crafted username. Delivers reverse shell to attacker. For authorized…