
socks5
 wzshiming/socks5
Socks5/Socks5h server and client. Full TCP/Bind/UDP and IPv4/IPv6 support
general-purpose-utilitiesnetwork-securitypenetration-testing+2
1311 month ago
wzshiming/socks5Socks5/Socks5h server and client. Full TCP/Bind/UDP and IPv4/IPv6 support
 0xthirteen/sharpmove
.NET Project for performing Authenticated Remote Execution
 ilikenwf/darkagent
DarkAgent Remote Administration Tool RAT by DragonHunter
 genymobile/scrcpy
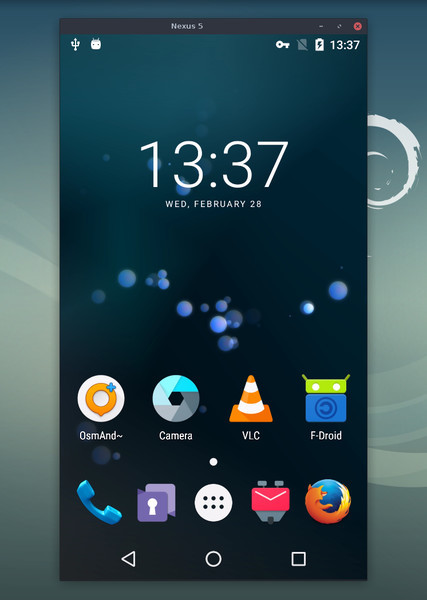
Display and control your Android device
 muhammedkayag/cve-2018-7600
PoC of CVE-2018-7600
 klaasstessens/cve-2023-46604
Exploitation of CVE-2023-44604. Using a Kali Linux VM (attacker) and a Debian 11 server VM (victim)
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
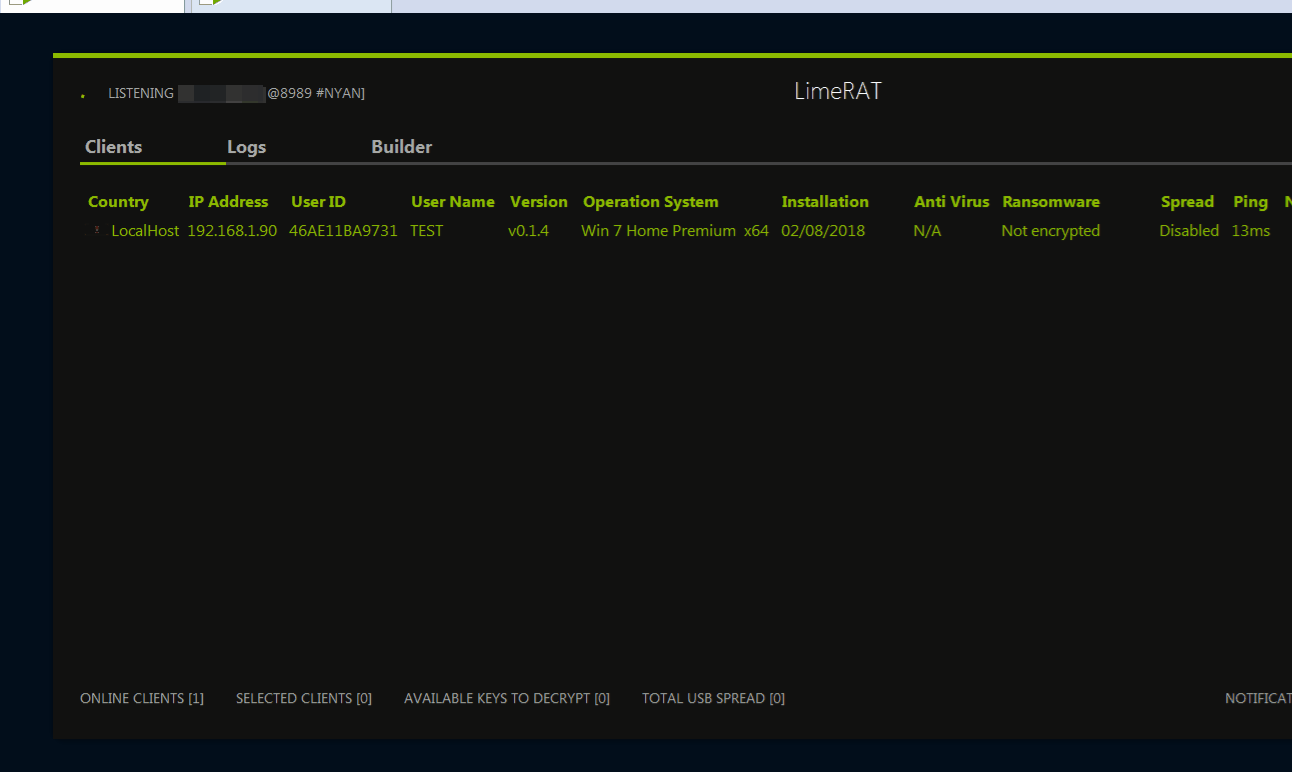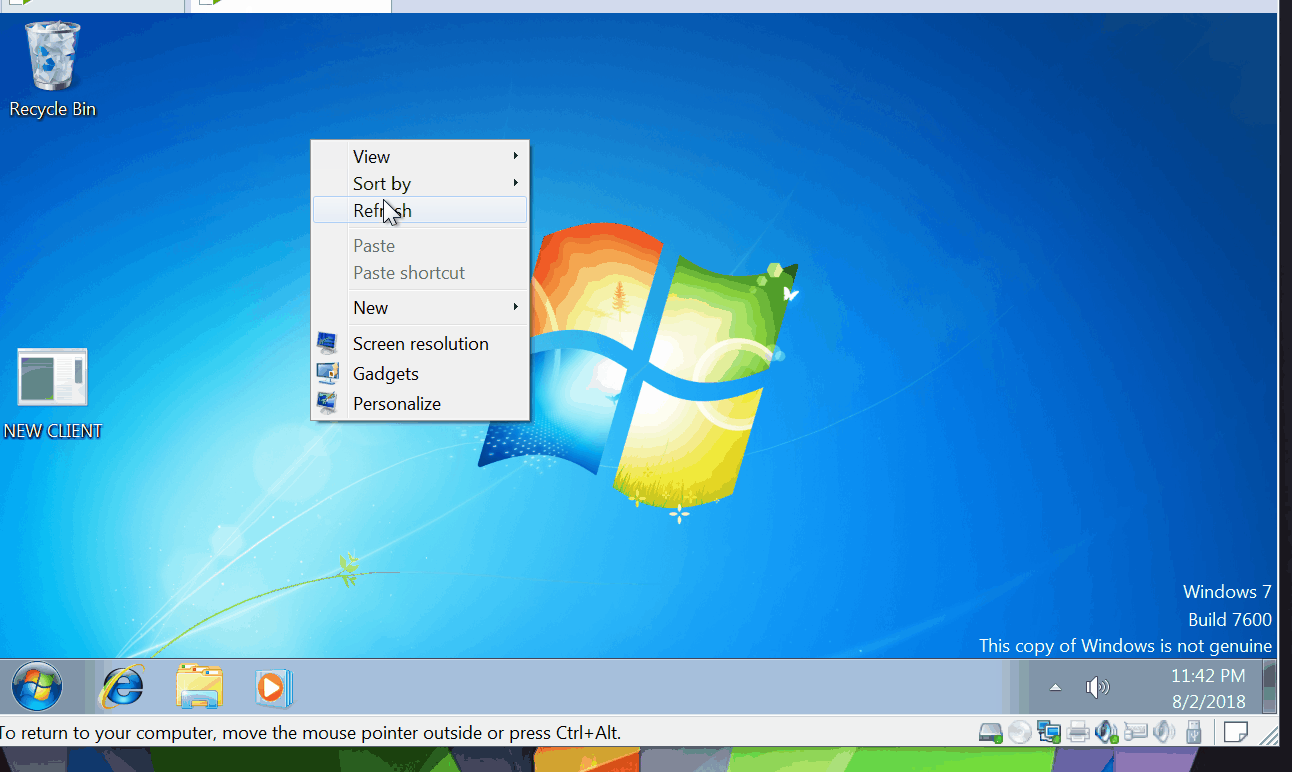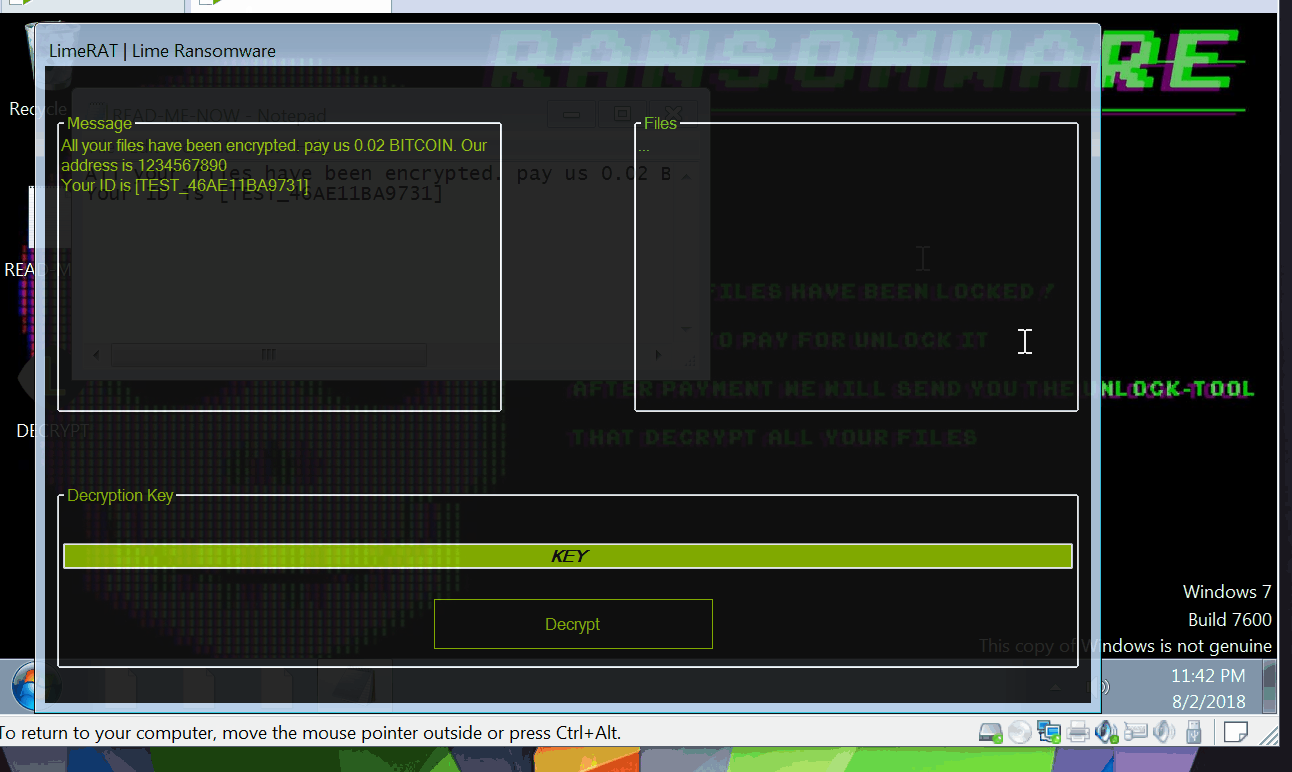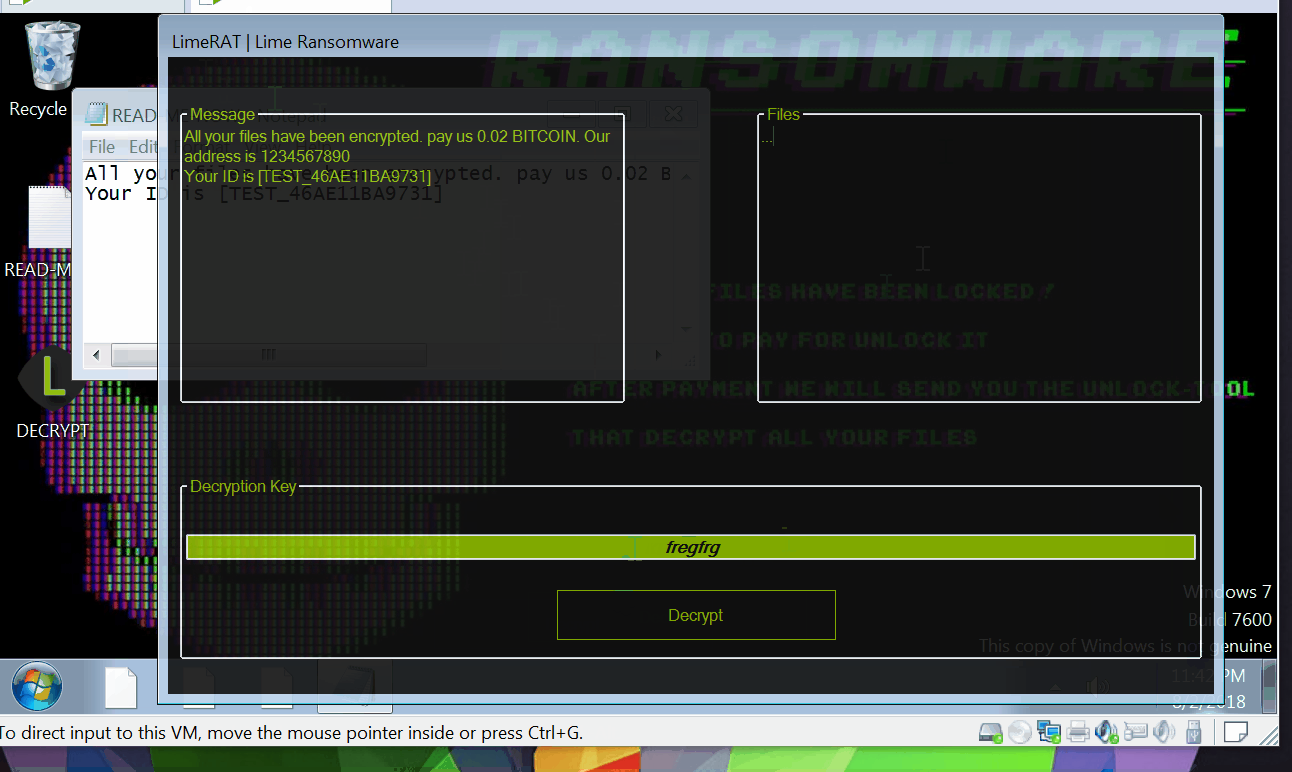 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
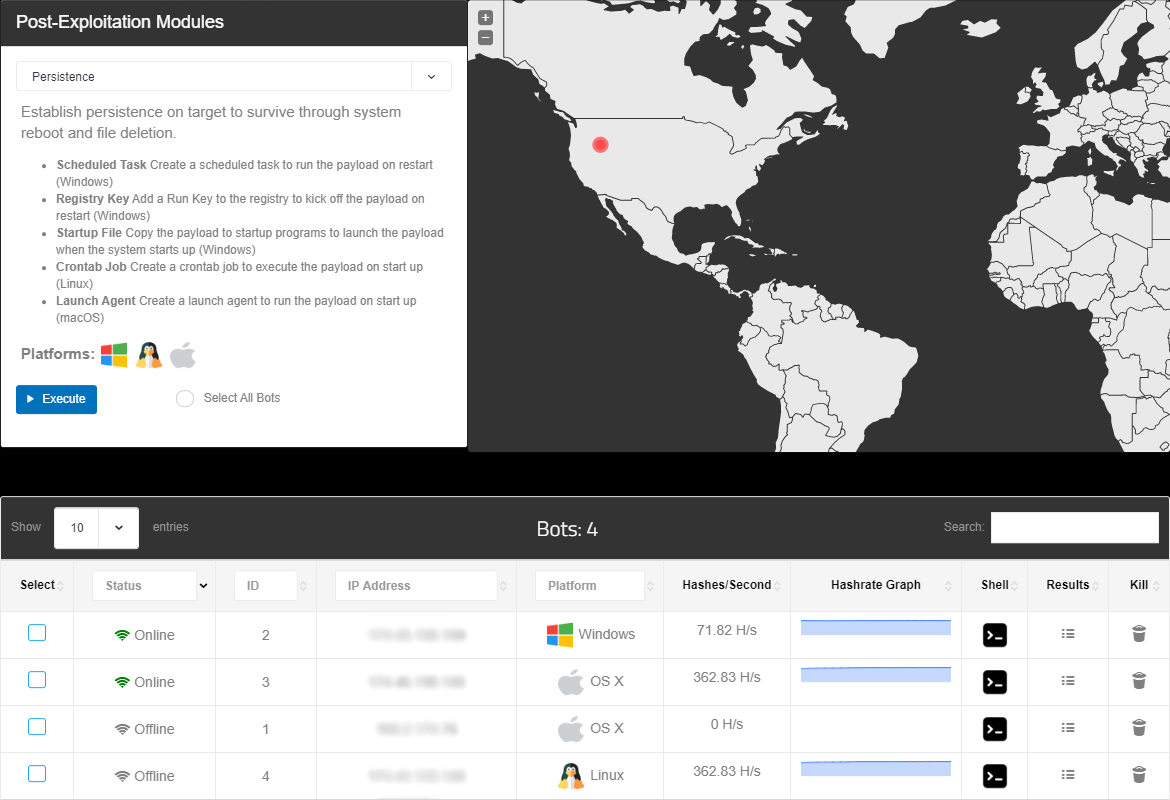 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
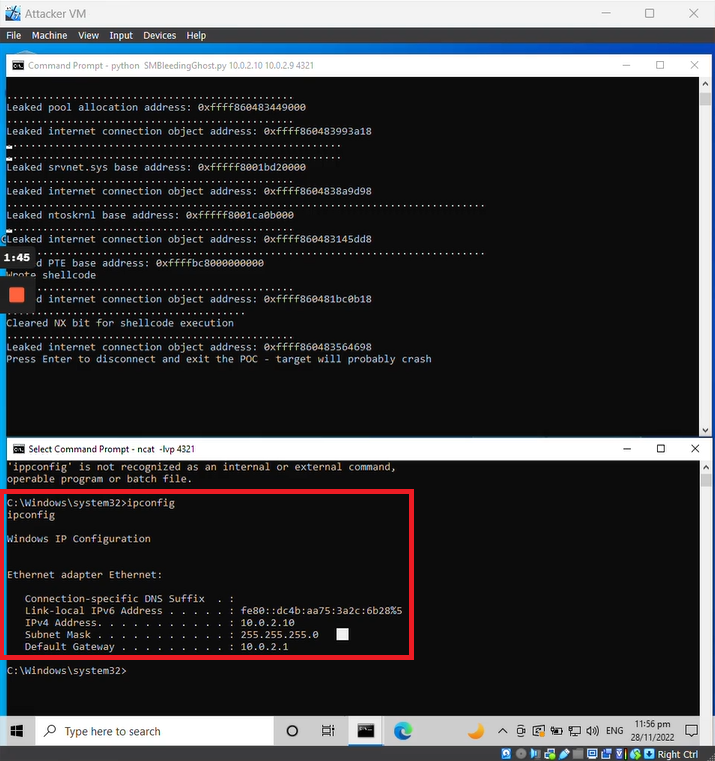 tdevworks/cve-2020-0796-smbghost-exploit-demo
Educational proof-of-concept exploit for CVE-2020-0796 (SMBGhost) demonstrating pre-auth RCE on Windows SMBv3. Includes step-by-step lab setup,…
 0xthirteen/sharprdp
Remote Desktop Protocol .NET Console Application for Authenticated Command Execution
 softdeadlock/voron-crypto
Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested
 mishakorzik/allhackingtools
All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
 sysdream/hershell
Hershell is a simple TCP reverse shell written in Go.
 geniuszly/cve-2022-45701
it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…
 afifudinmtop/cve-2021-43857-gerapy-v0.9.7
Exploit for CVE-2021-43857 in Gerapy v0.9.7, providing a reverse shell via authenticated project creation and command injection.