
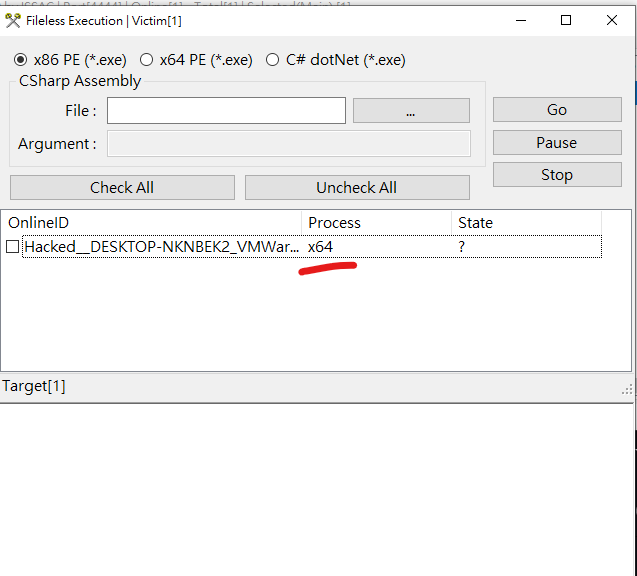
DuplexSpyCS
 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
command-and-controleducationpayload-development+5
233
iss4cf0ng/duplexspycsAn open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bishopfox/sliver
Adversary Emulation Framework
 alphaseclab/awesome-rat
RAT And C&C Resources. 250+ Open Source Projects, 1200+ RAT/C&C blog/video.
 fmd-foss/fmd-android
Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…
 ego1stoo/cve-2023-38646
Metabase open source before 0.46.6.1 and Metabase Enterprise before 1.46.6.1 allow attackers to execute arbitrary commands on the server, at the…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
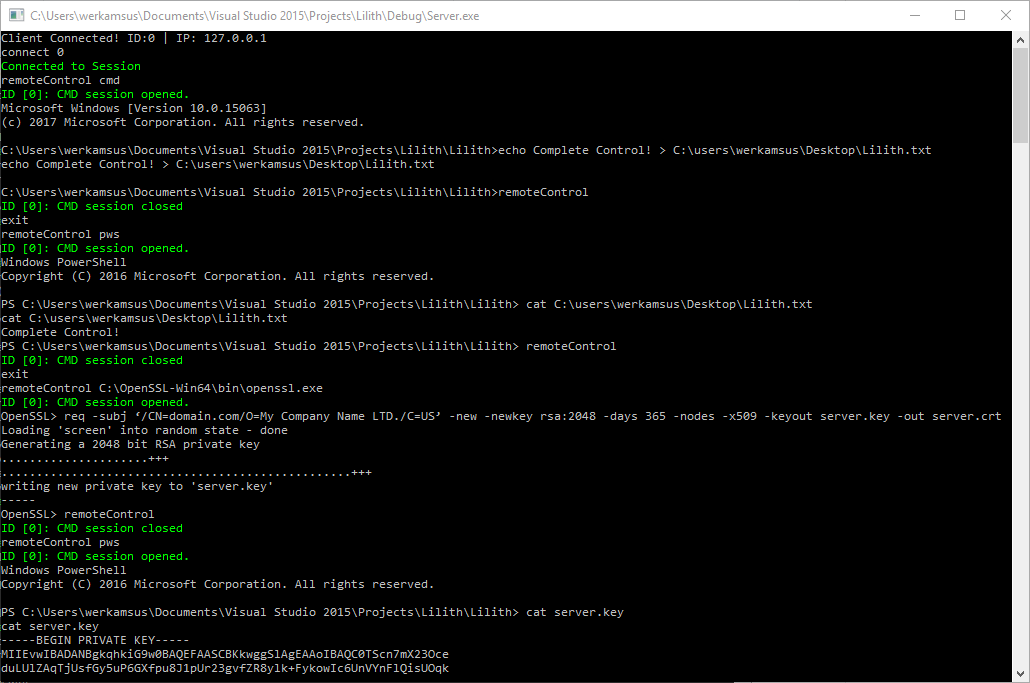 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
 shamo0/cve-2023-38646-poc
Metabase Pre-auth RCE
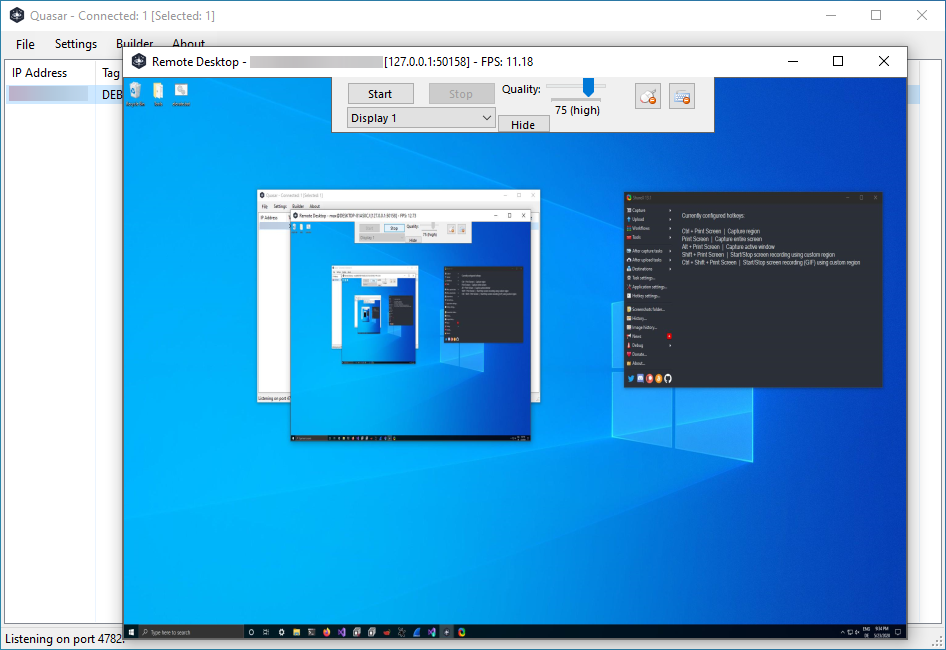 quasar/quasar
Remote Administration Tool for Windows
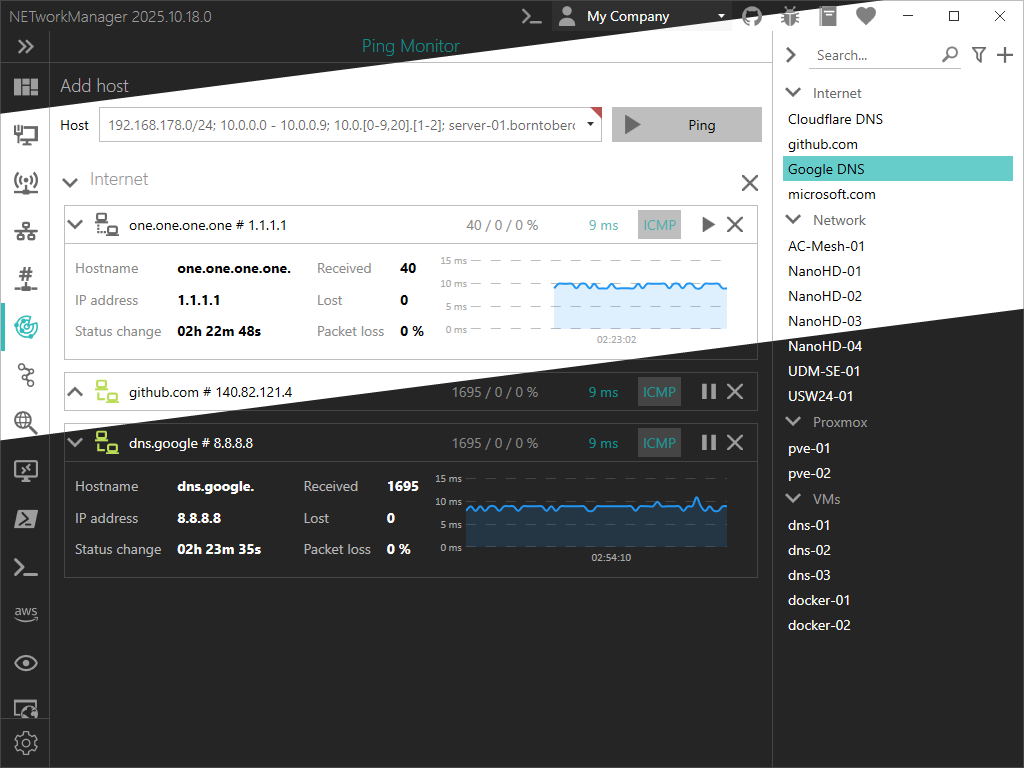 borntoberoot/networkmanager
A powerful open-source tool for managing networks and troubleshooting network problems!
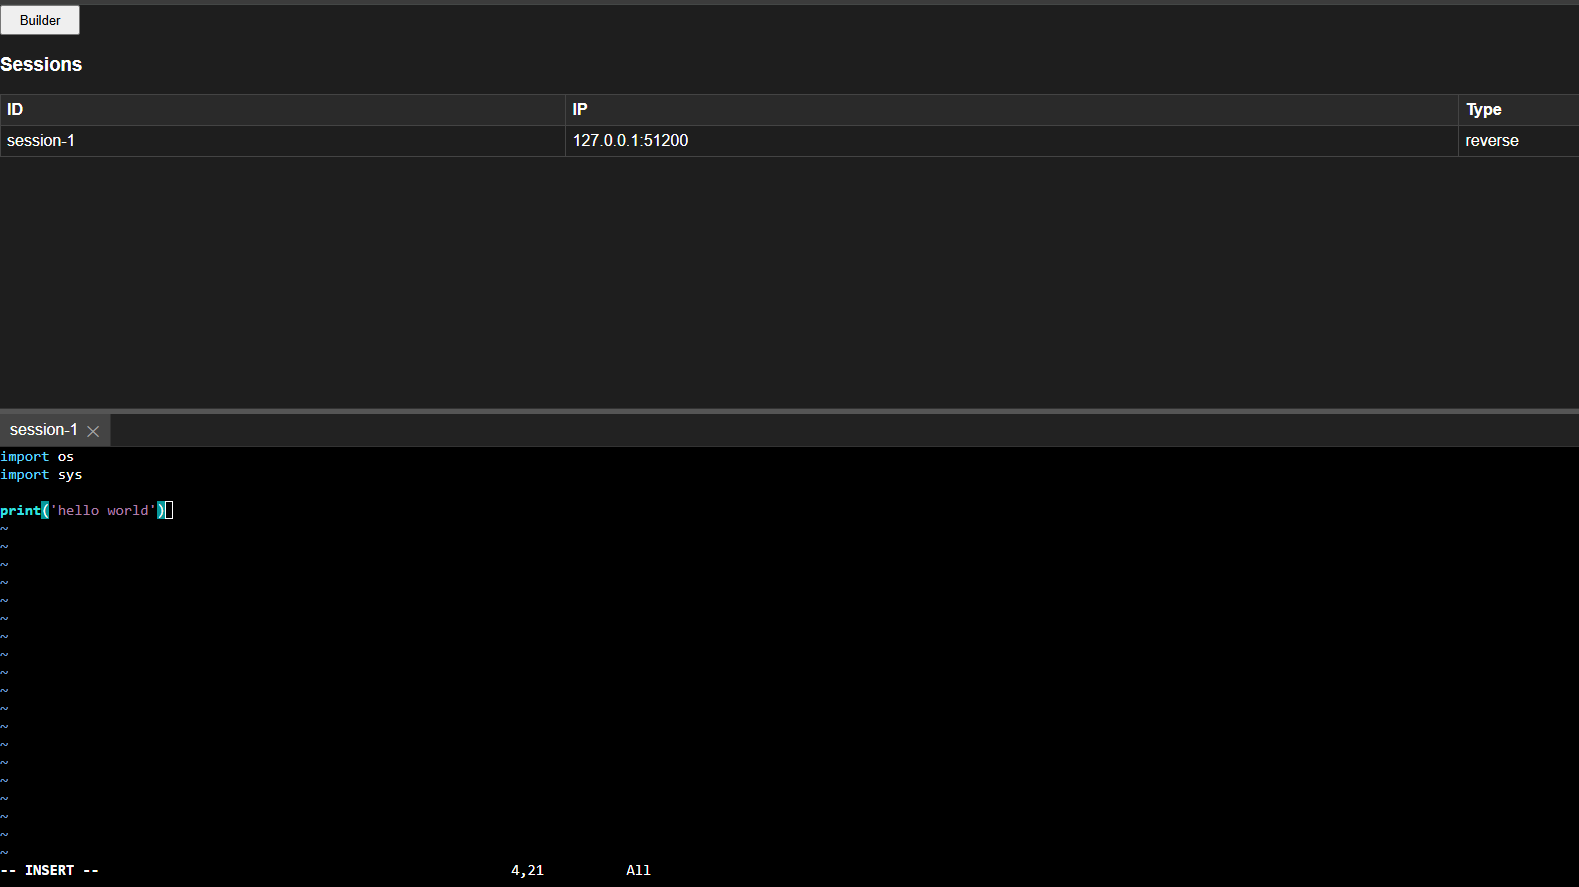 iss4cf0ng/openshell
Lightweight Go-based reverse shell management server with a web GUI for interactive shell sessions, session management, and multi-tab terminal…
 fortbridge/stylesmuggler
Python PoC reproducing CVE-2026-75650 StyleSmuggler, an unauthenticated Magento RCE via report poisoning and failed-payment rendering, with canary…
 delt-a/cve-2024-36401-poc
Unauthenticated RCE exploit for GeoServer (CVE-2024-36401) via OGC filter XPath injection. Supports reverse shell and blind command execution with…
 cc3305/cve-2025-49844
Exploit script for CVE-2025-49844, a use-after-free vulnerability in Redis Lua scripting enabling remote code execution. Targets specific Redis…
 birdm4nw/cve-2023-38646
This script is designed to exploit vulnerable Metabase software versions by providing you as attacker a shell.
 gumerzzzindo/cve-2024-47176
Python exploit for CVE-2024-47176 achieving remote command execution in CUPS cups-browsed via crafted UDP packets. Includes reverse shell payload…