Exploits_CVE-2019-19781

Remote code execution exploit for Citrix Application Delivery Controller and Gateway (CVE-2019-19781). Executes arbitrary commands on vulnerable…

Remote code execution exploit for Citrix Application Delivery Controller and Gateway (CVE-2019-19781). Executes arbitrary commands on vulnerable…

Remote code execution exploit for Citrix Application Delivery Controller and Gateway (CVE-2019-19781) that executes arbitrary commands on vulnerable…

Standalone Python 3 exploit for CVE-2017-17562 targeting GoAhead web server 2.5–3.6.5 with automated CGI endpoint discovery and reverse shell payload…

Python exploit for CVE-2022-27925 targeting Zimbra Collaboration Suite, enabling unauthenticated remote code execution and reverse shell delivery.

Proof-of-concept exploit for CVE-2025-56015, a sandbox escape and RCE in GenieACS. Automates malicious provision creation, preset mapping, and…

CVE-2019-19781 - Remote Code Execution on Citrix ADC Netscaler exploit

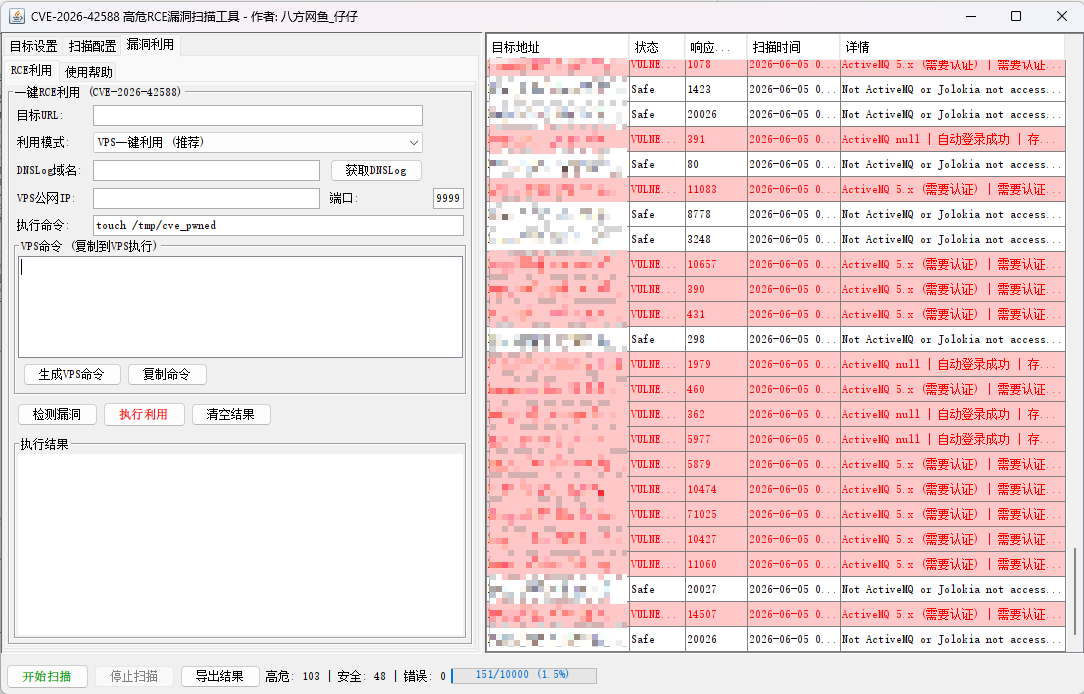
GUI-based scanner and exploit tool for CVE-2026-42588 (ActiveMQ RCE). Supports VPS payload delivery and DNSLog-based vulnerability verification with…

Exploit for CVE-2021-44228 (Log4Shell) with RMI server and payload delivery for remote code execution against vulnerable Apache Log4j instances.

Python exploit for CVE-2024-47176 achieving remote command execution in CUPS cups-browsed via crafted UDP packets. Includes reverse shell payload…

Proof-of-concept exploit for CVE-2020-8515 command injection in Draytek routers. Includes automated exploitation, reverse shell delivery, and…

Python exploit for CVE-2007-2447 targeting Samba smbd 3.0.20-Debian with reverse shell payload delivery via Netcat listener.

Exploit script for CVE-2021-25646 Apache Druid remote code execution vulnerability, using DNSLog-based out-of-band detection and automated payload…

Exploit script for Apache OFBiz CVE-2020-9496 unsafe deserialization vulnerability, enabling remote code execution via crafted XML-RPC requests with…

Authenticated RCE exploit for MotionEye <= 0.43.1b4 via client-side validation bypass on the image_file_name field. Includes reverse shell payload…

Proof-of-concept exploit for CVE-2026-20253, enabling unauthenticated remote code execution on vulnerable Splunk Enterprise instances via file write…

Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…

Python exploit for CVE-2019-19781 targeting Citrix Netscaler remote code execution vulnerability with automated payload delivery.

Python exploit for CVE-2021-22205, a remote command execution vulnerability in GitLab CE/EE. Supports single-target exploitation, batch scanning, and…