
CVE-2020-15568
 n0bugz/cve-2020-15568
A quick and easy POC for CVE-2020-15568
exploitationpenetration-testingremote-access-tool+2
n0bugz/cve-2020-15568A quick and easy POC for CVE-2020-15568
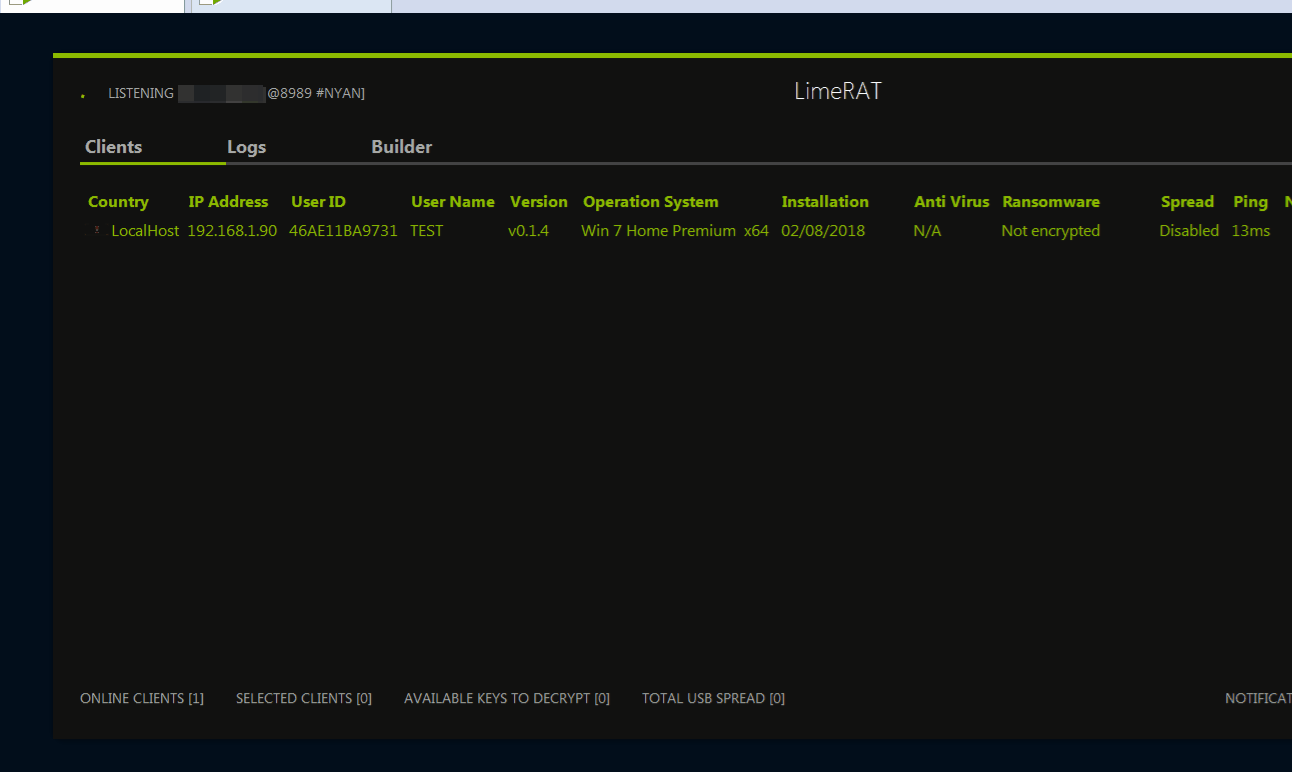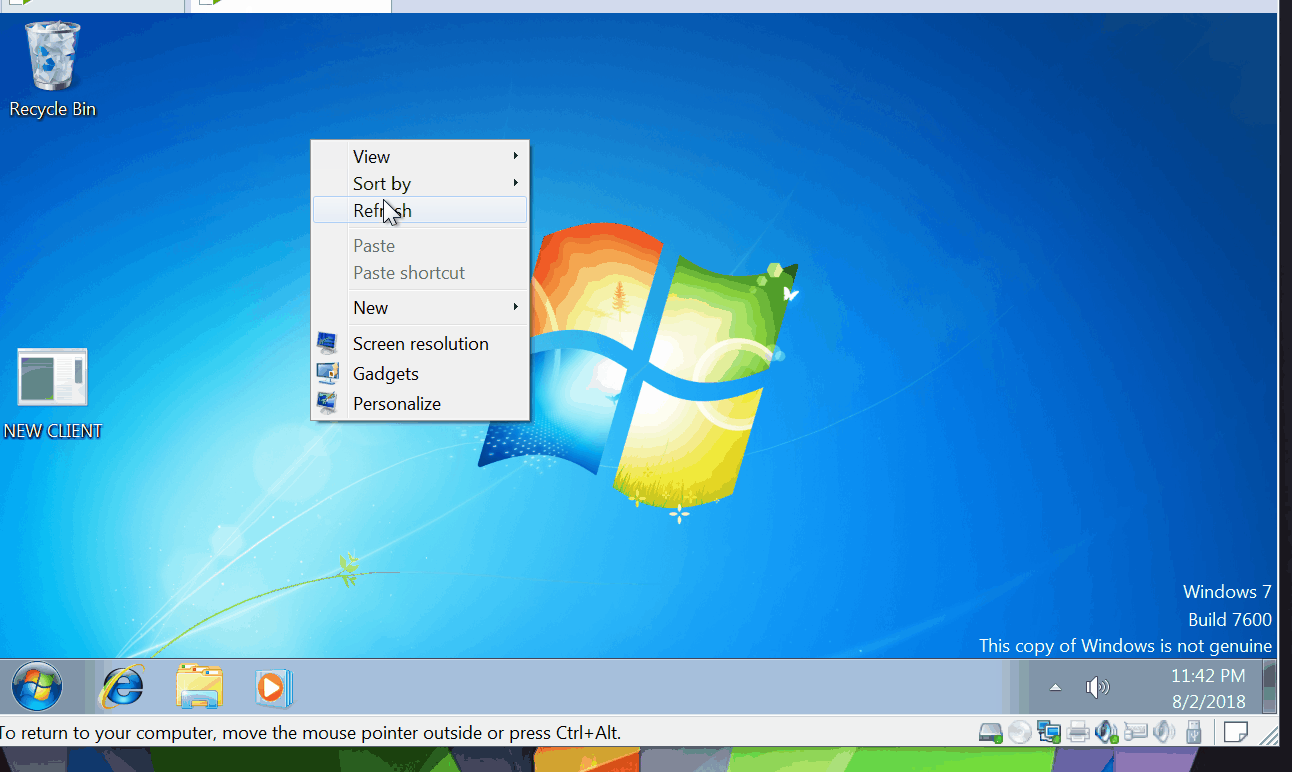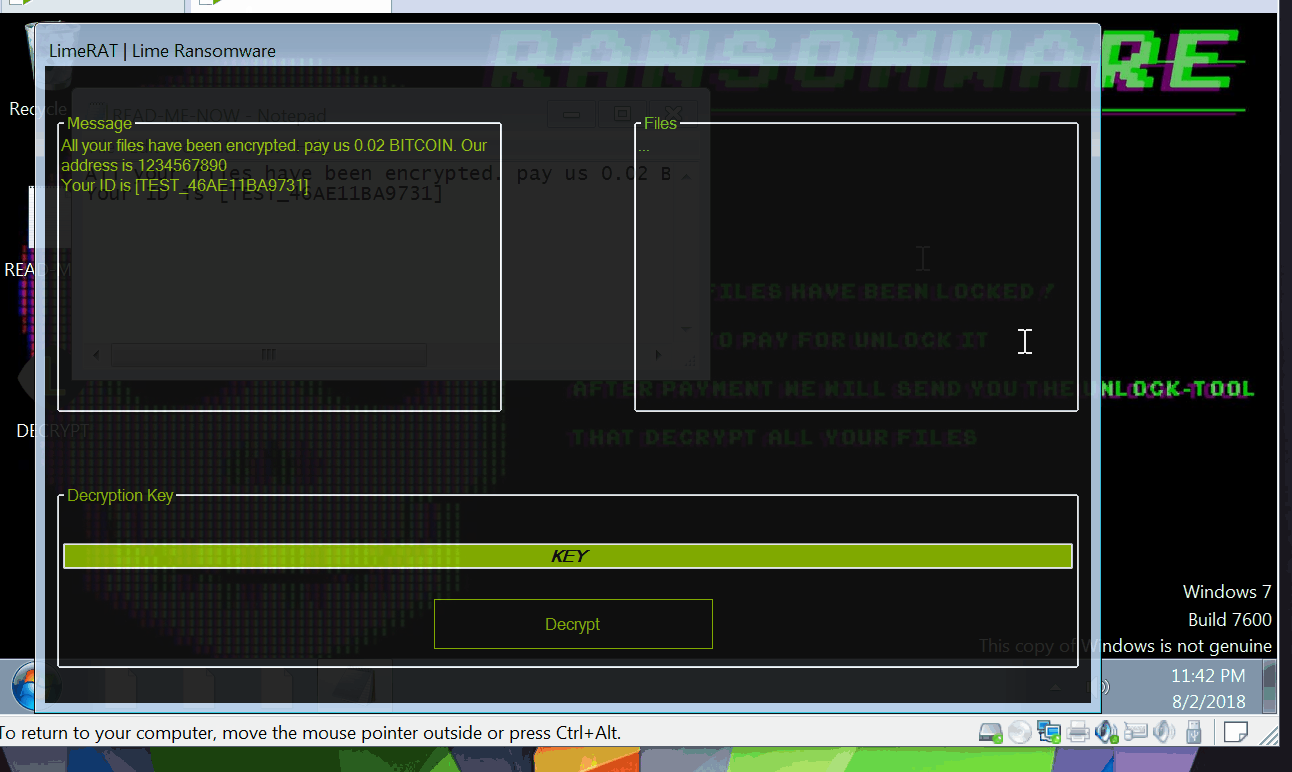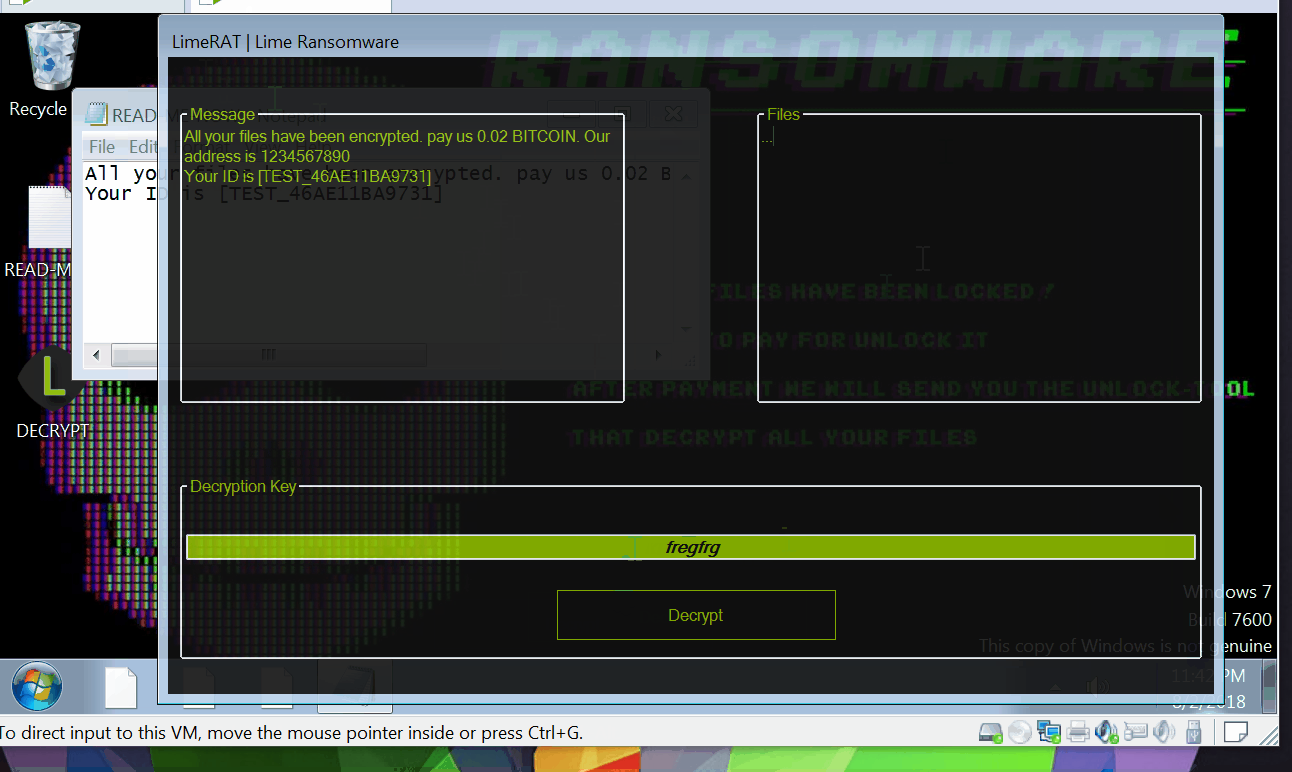 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 typetrait/pace
Remote Access Tool for Windows.
 tgadola/serval
A Netcat-style backdoor for pentesting and pentest exercises
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 ceald1/evilwinrm-ng
Go-based WinRM client for remote command execution and lateral movement on Windows systems during penetration tests.
 nullarray/autosploit
Automated Mass Exploiter
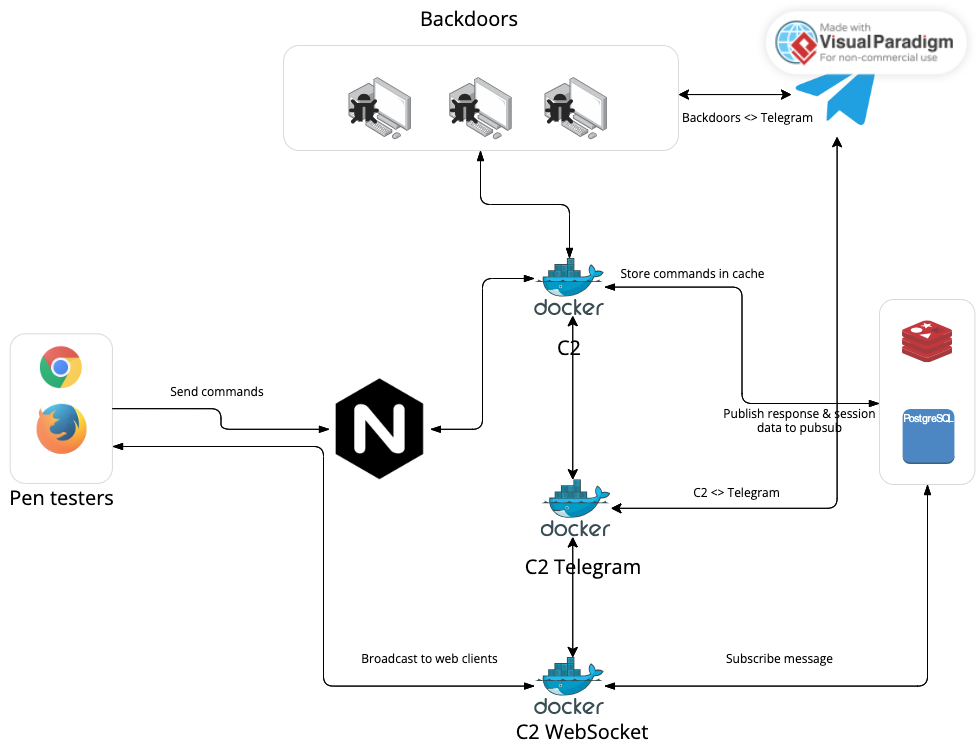 govindasamyarun/c2-cloud
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…
 rasta-mouse/pwnlift
Easy peasy file uploads
 ihhgimhana/react2shell-cve-2025-55182-poc-reverse-shell
This is an easy to use PoC script to exploit React2Shell-CVE-2025-55182 Nextjs vulnerability. This will help to gain a reverse shell.
 gurguii/cgi-bin-shellshock
[Python/Shell] - Tested in HackTheBox - Shocker (Easy) CVE-2014-6271
 g01d3nw01f/cve-2021-21315
rust noob tried write easy exploit code with rust lang
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
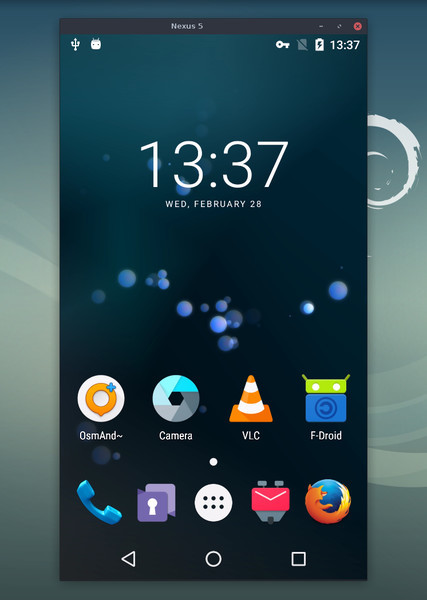 genymobile/scrcpy
Display and control your Android device
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…