
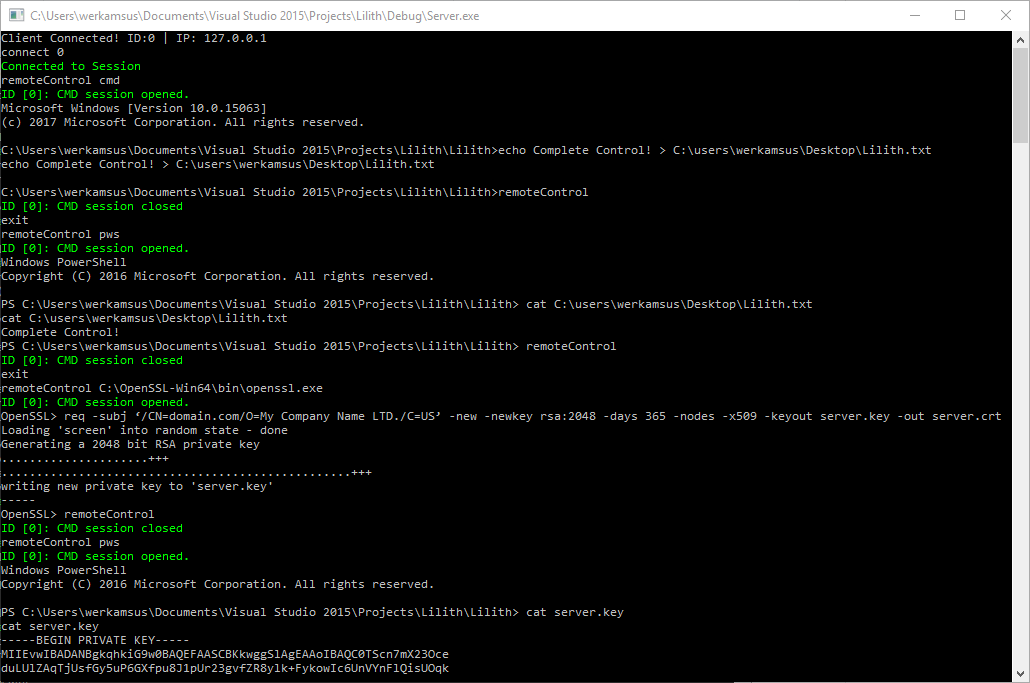
Lilith
 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
command-and-controlpayload-generationpenetration-testing+4
747
werkamsus/lilithLilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
 tiagorlampert/chaos
🔥 CHAOS is a free and open-source Remote Administration Tool that allow generate binaries to control remote operating systems.
 freerdp/freerdp
FreeRDP is a free remote desktop protocol library and clients
 androvirus/blacknet
Free advanced and modern Windows botnet with a nice and secure PHP panel developed using VB.NET.
 wqsemc/cve-2019-0708
initial exploit for CVE-2019-0708, BlueKeep CVE-2019-0708 BlueKeep RDP Remote Windows Kernel Use After Free The RDP termdd.sys driver improperly…
 absholi7ly/freerdp-out-of-bounds-read-cve-2024-32459-
The FreeRDP - Out-of-Bounds Read (CVE-2024-32459) vulnerability concerns FreeRDP, a free implementation of Remote Desktop Protocol. FreeRDP-based…
 jajangjaman/cve-2021-41160
FreeRDP is a free implementation of the Remote Desktop Protocol (RDP), released under the Apache license. In affected versions a malicious server…
 darthton/blackbone
Windows memory hacking library
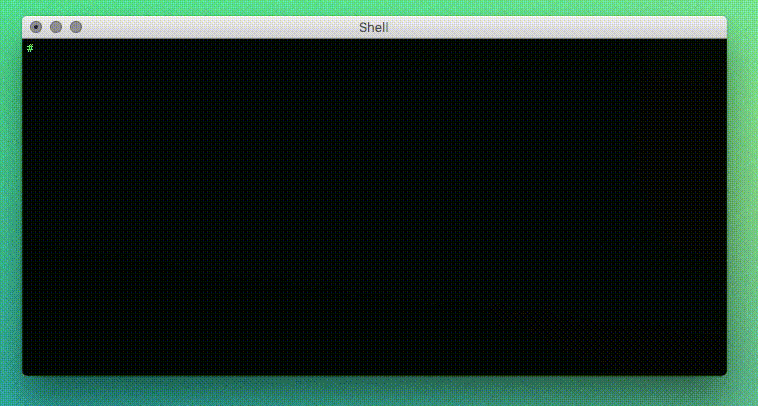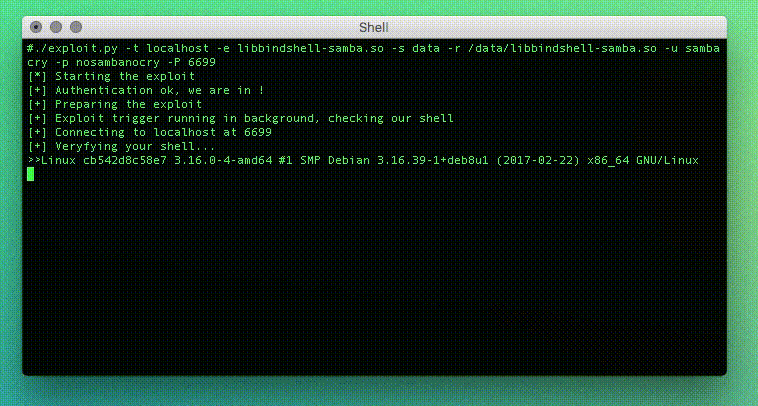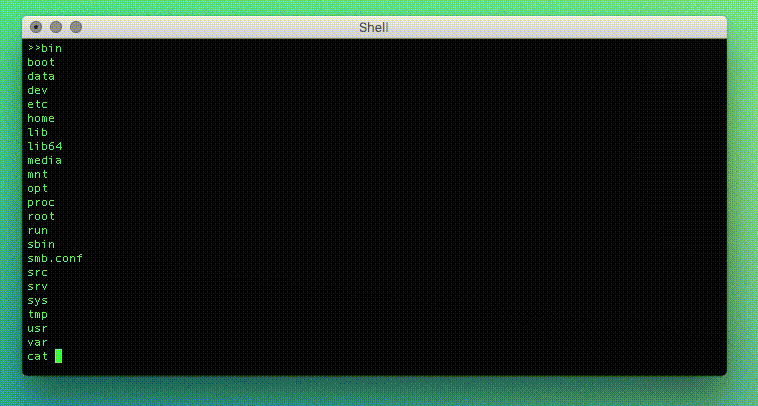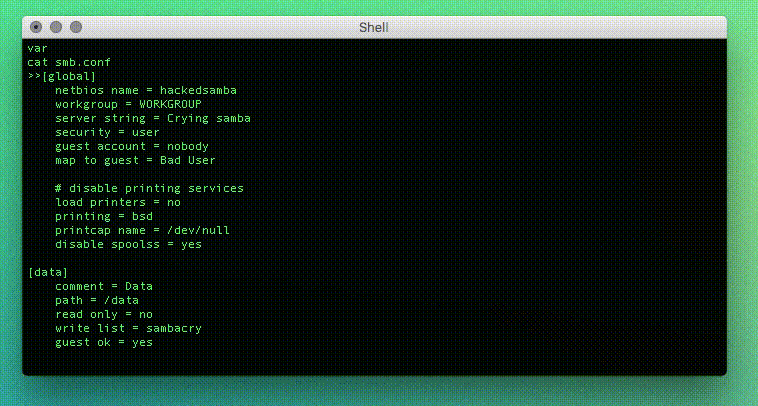 opsxcq/exploit-cve-2017-7494
SambaCry exploit and vulnerable container (CVE-2017-7494)
 them4hd1/vayne-rat
An Advanced C# .NET Rat, It’s Stable and Contains Many Features.
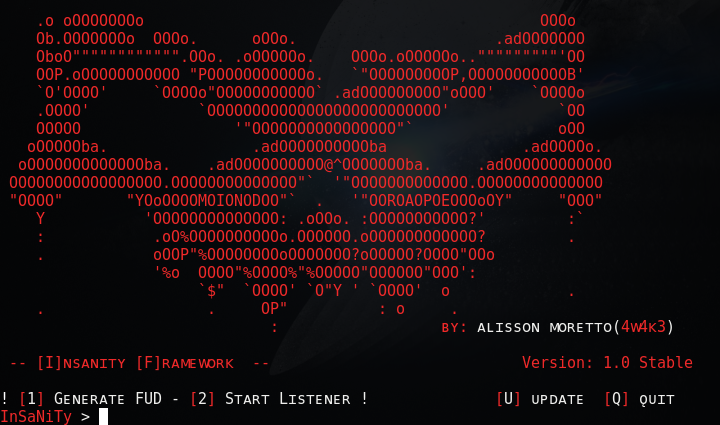 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
 bishopfox/firecat
Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 nhakobyan685/cve-2023-25136
OpenSSH 9.1 vulnerability mass scan and exploit
 dorkerdevil/cve-2020-28018
Exploit for Exim Use-After-Free (CVE-2020-28018) achieving remote code execution via memory corruption primitives, including arbitrary read/write and…
 axylisdead/cve-2023-25136_poc
CVE-2023-25136 POC written by axylisdead
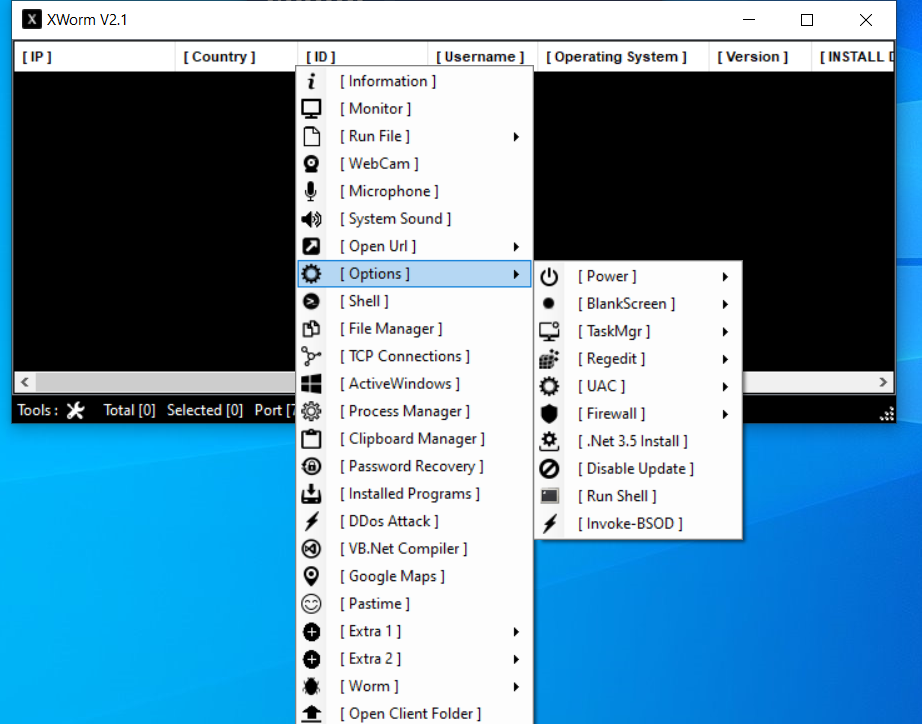
 manturever/xworm-rat
⭐️The famous XWorm RAT, version 2.1. Educational purposes only
 h4r335hr/vsftpd-234-backdoor
Dependency-free interactive Python exploit for the vsftpd 2.3.4 backdoor (CVE-2011-2523).