Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
124 results
CVE-2015-1925.RCE preview
Archived

CVE-2015-1925.RCE

GitHubdamariion/cve-2015-1925.rce

Stack-based buffer overflow in the server in IBM Tivoli Storage Manager FastBack 6.1 before 6.1.12 allows remote attackers to cause a denial of…

binary-exploitationexploitationpayload-development+3
1 month ago
CVE-2019-9810 preview
Archived

CVE-2019-9810

GitHub0vercl0k/cve-2019-9810

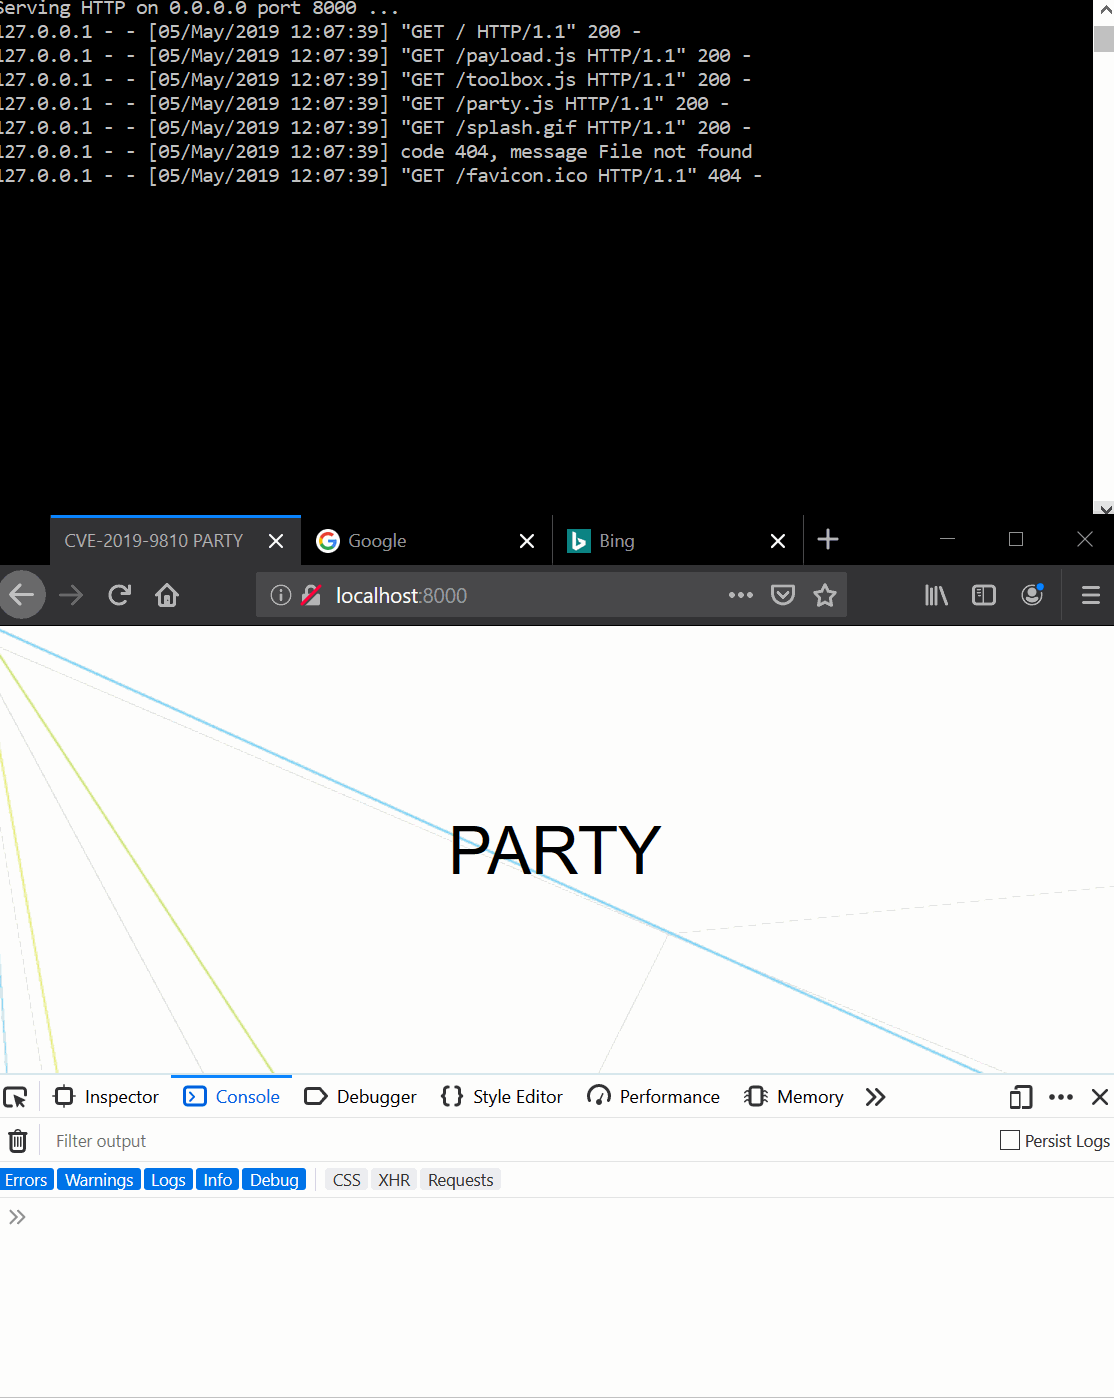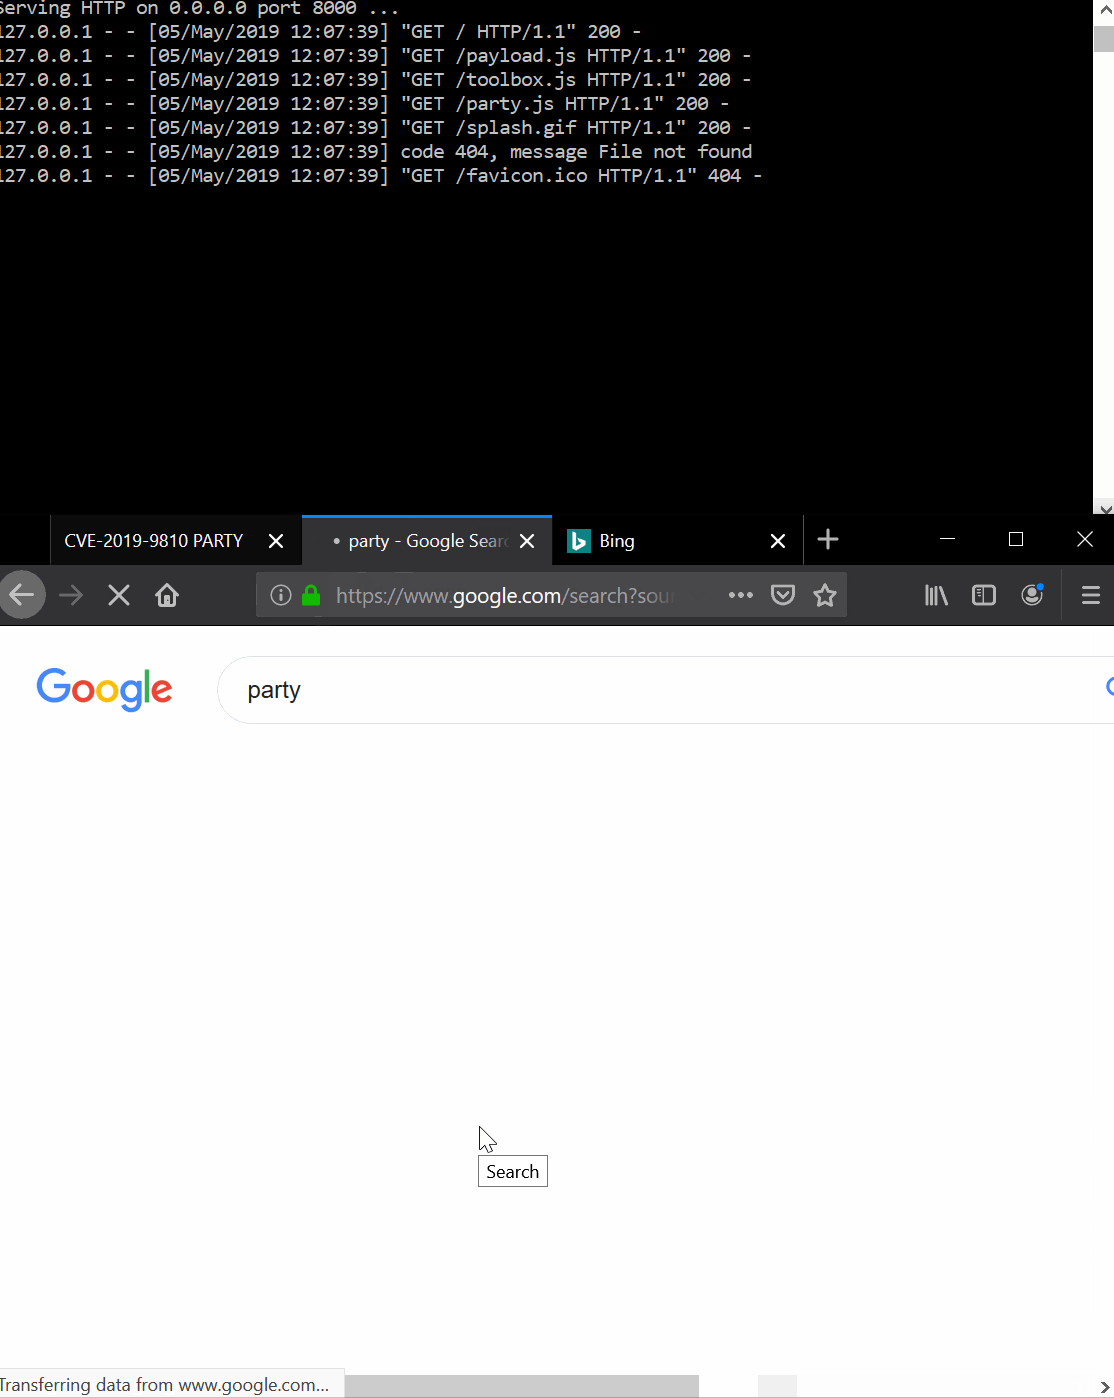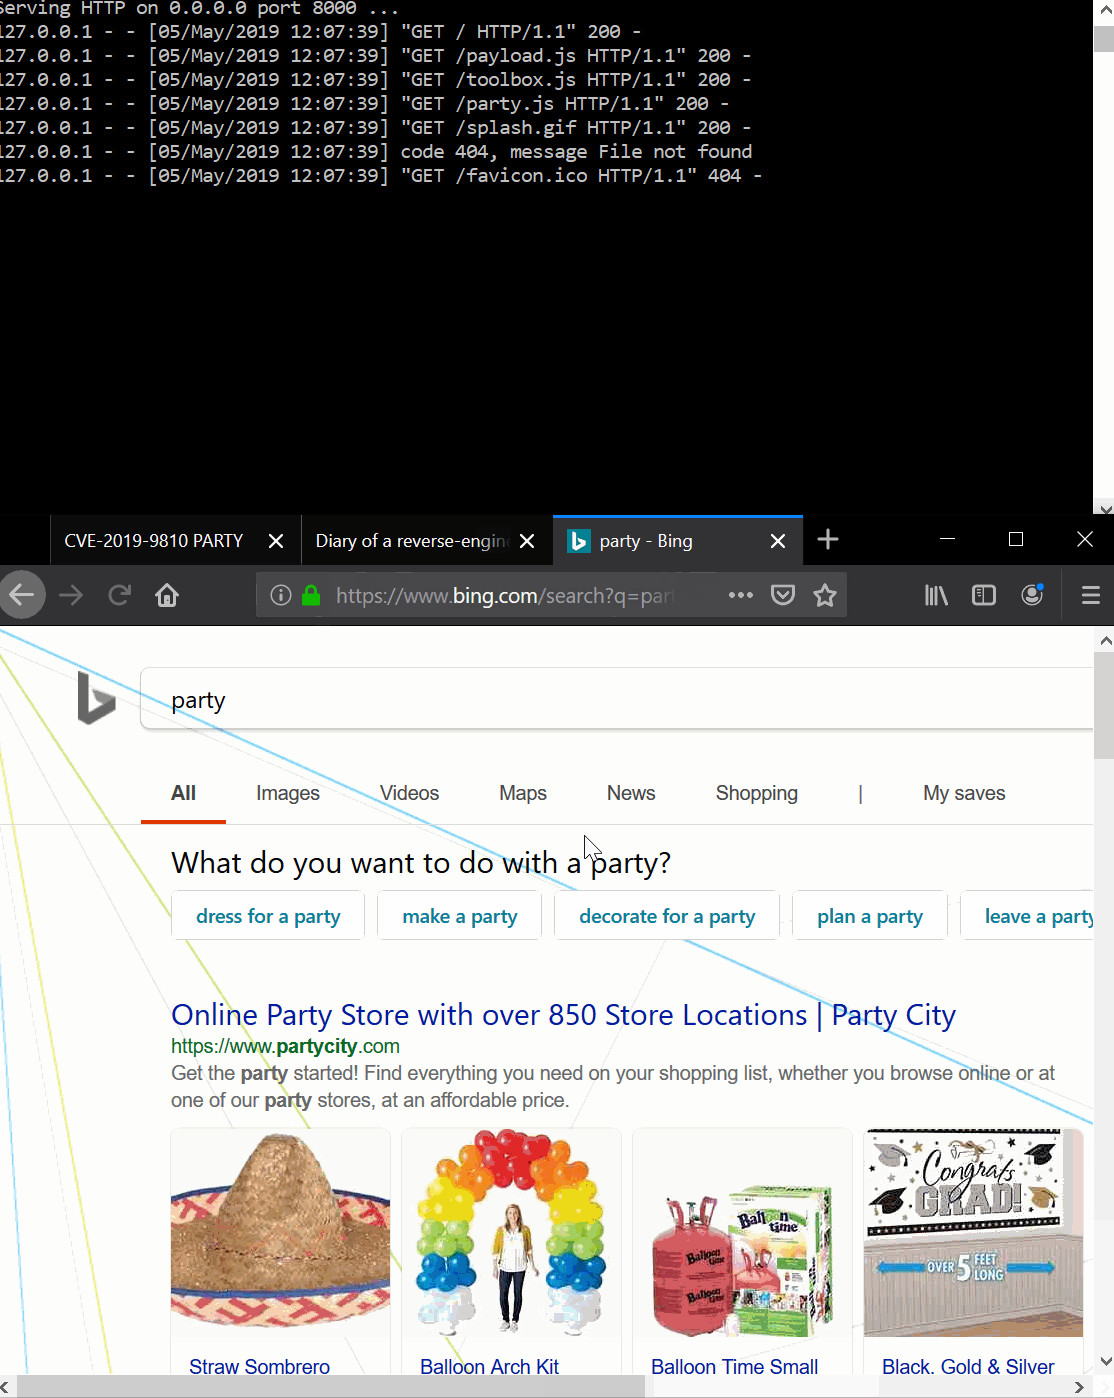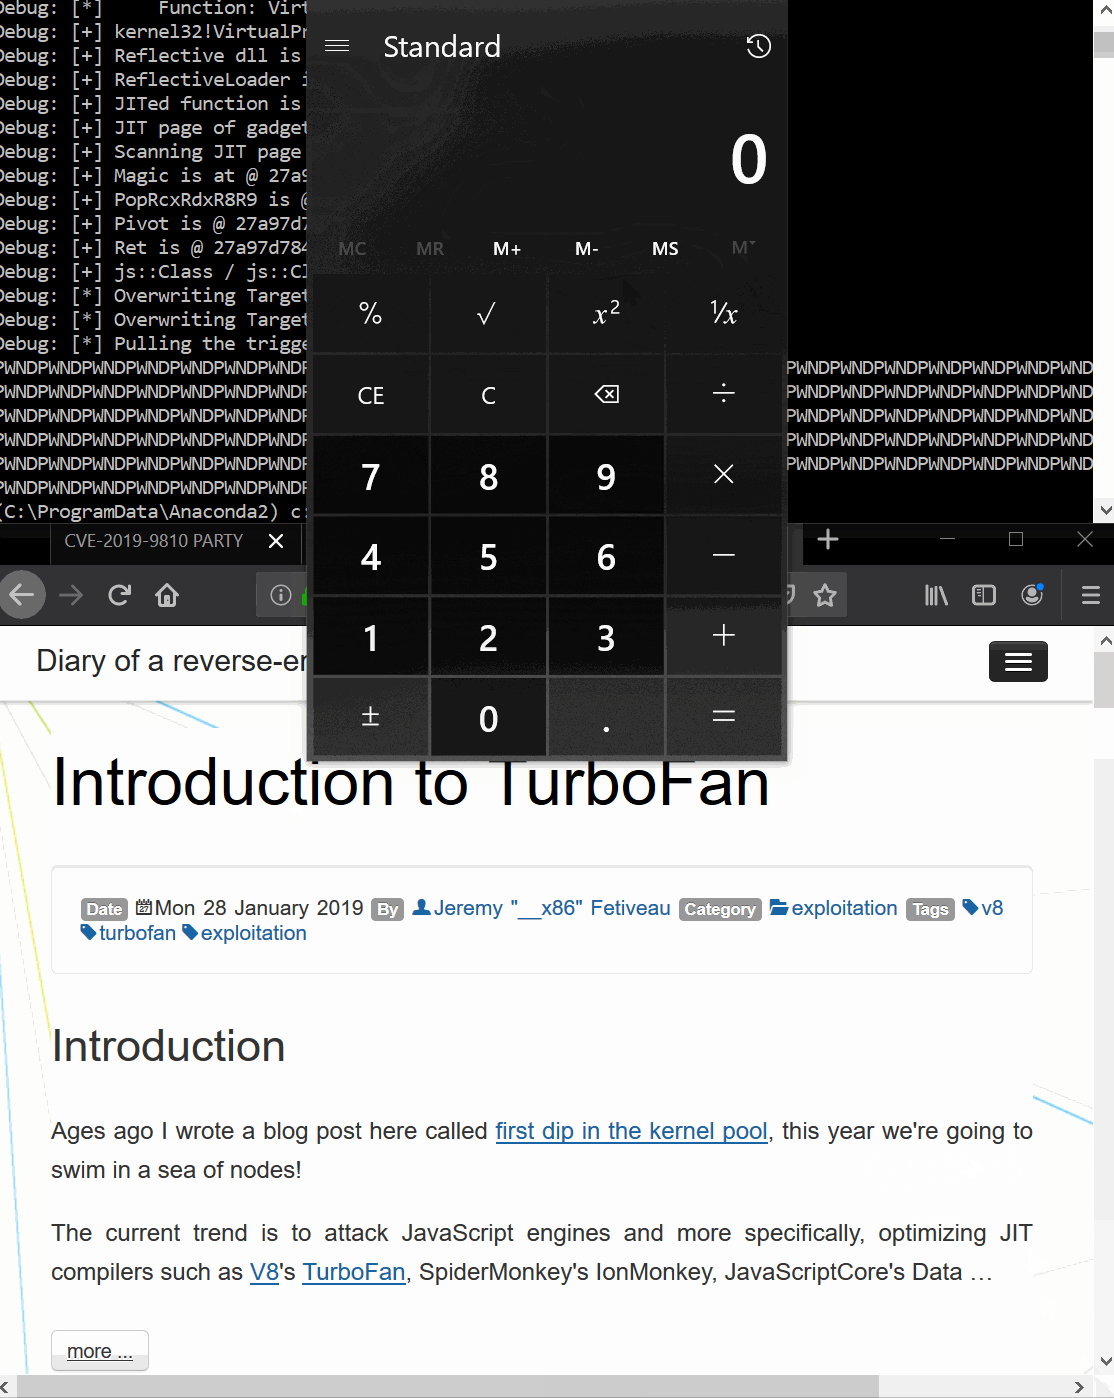
Exploit for CVE-2019-9810 Firefox on Windows 64-bit.

binary-exploitationexploitationpayload-development+3
2276 years ago
CVE-2021-31166 preview
Archived

CVE-2021-31166

GitHub0vercl0k/cve-2021-31166

Proof of concept for CVE-2021-31166, a remote HTTP.sys use-after-free triggered remotely.

binary-exploitationexploitationremote-access-tool+2
8265 years ago
CVE-2024-38077 preview
Archived

CVE-2024-38077

GitHubqi4l/cve-2024-38077

RDL的堆溢出导致的RCE

binary-exploitationexploitationpayload-development+3
2242 years ago
CVE-2018-6537.RCE preview
Archived

CVE-2018-6537.RCE

GitHubdamariion/cve-2018-6537.rce

A buffer overflow vulnerability in the control protocol of Flexense SyncBreeze Enterprise v10.4.18 allows remote attackers to execute arbitrary code…

binary-exploitationexploitationpayload-generation+4
6 months ago
CVE-2023-25610 preview
Archived

CVE-2023-25610

GitHubqi4l/cve-2023-25610

FortiOS 管理界面中的堆内存下溢导致远程代码执行

binary-exploitationcommand-and-controlexploitation+3
233 years ago
Blackbone preview

Blackbone

GitHubdarthton/blackbone

Windows memory hacking library

binary-analysisdebuggersdynamic-analysis-sandboxing+9
5.5k4 years ago
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

digital-forensicsdisk-forensicsforensics+4
5.1k2 days ago
java-stager preview

java-stager

GitHubcornerpirate/java-stager

A PoC Java Stager which can download, compile, and execute a Java file in memory.

command-and-controldynamic-code-analysiseducation+7
1078 years ago
CVE-2024-4323-Exploit-POC preview

CVE-2024-4323-Exploit-POC

GitHubskilfoy/cve-2024-4323-exploit-poc

This proof-of-concept script demonstrates how to exploit CVE-2024-4323, a memory corruption vulnerability in Fluent Bit, enabling remote code…

exploitationpayload-generationpenetration-testing+3
152 years ago
CVE-2025-55182-golang-PoC preview

CVE-2025-55182-golang-PoC

GitHubkeklick1337/cve-2025-55182-golang-poc

Go-based proof-of-concept for CVE-2025-55182, a critical RCE in React Server Components. Features vulnerability checking, command execution, memory…

command-and-controlexploitationpayload-development+6
69 months ago
cve-2019-1108 preview

cve-2019-1108

GitHublanph3re/cve-2019-1108

Proof-of-concept exploit for CVE-2019-1108, an RDP client information disclosure vulnerability that leaks memory contents via specially crafted…

binary-analysisexploitationinformation-gathering+2
26 years ago
CVE-2023-25136 preview

CVE-2023-25136

GitHubmrmtwoj/cve-2023-25136

This vulnerability is of the "double-free" type, which occurs during the processing of key exchange (KEX) algorithms in OpenSSH. A "double-free"…

exploitationinformation-gatheringnetwork-security+3
11 year ago
CVE-2025-26686-poc-A-critical-RCE-vulnerability-in-Windows-TCP-IP-stack preview

CVE-2025-26686-poc-A-critical-RCE-vulnerability-in-Windows-TCP-IP-stack

GitHubcyghtinc/cve-2025-26686-poc-a-critical-rce-vulnerability-in-windows-tcp-ip-stack

POC for CVE-2025-26686 - A critical RCE vulnerability in Windows TCP/IP stack (CVE-2025-26686) leaves sensitive memory unlocked, allowing remote…

exploitationpayload-developmentpenetration-testing+3
10 months ago
emp3r0r preview

emp3r0r

GitHubjm33-m0/emp3r0r

Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.

anti-botcommand-and-controlids-ips-evasion+10
1.8k8h 15m ago
AlanFramework preview

AlanFramework

GitHubenkomio/alanframework

A C2 post-exploitation framework

command-and-controlencryption-decryption-toolslateral-movement+7
4842 years ago
Previous1234567Next