

CVE-2024-3400
 marconesler/cve-2024-3400
Exploit for GlobalProtect CVE-2024-3400
exploitationpenetration-testingred-teaming+3
marconesler/cve-2024-3400Exploit for GlobalProtect CVE-2024-3400
 mattb709/cve-2025-34028-poc-commvault-rce
Proof-of-Concept (PoC) for CVE-2025-34028, a Remote Code Execution vulnerability in Commvault Command Center. This Python script scans single or…

 vmtyan/poc-cve-2024-23897
Proof-of-concept exploit for CVE-2024-23897 enabling remote code execution on Jenkins instances via vulnerable args4j command-line parser. Written in…
 vidura2/cve-2023-46747
Exploit script for CVE-2023-46747 (F5 BIG-IP TMUI RCE) enabling unauthenticated user creation, token retrieval, and remote command execution on…
 jagadeesh7532/-cve-2020-0796-smbghost-windows-10-smbv3-remote-code-execution-vulnerability
CVE-2020-0796 (SMBGhost) is a critical RCE vulnerability in Windows 10 SMBv3 protocol. It allows attackers to execute code remotely via crafted SMB…
 lil0xplorer/cve-2025-60787_poc
Authenticated RCE exploit for MotionEye <= 0.43.1b4 via client-side validation bypass on the image_file_name field. Includes reverse shell payload…
 ph1ns/cve-2024-39844
CVE-2024-39844 (ZNC < 1.9.1 modtcl RCE)
 delt-a/cve-2024-36401-poc
Unauthenticated RCE exploit for GeoServer (CVE-2024-36401) via OGC filter XPath injection. Supports reverse shell and blind command execution with…
 e1st/cve-2025-56015
Proof-of-concept exploit for CVE-2025-56015, a sandbox escape and RCE in GenieACS. Automates malicious provision creation, preset mapping, and…
 micheaol/distccd_rce_cve-2004-2687
Manual exploit script for CVE-2004-2687 (distccd RCE) that spawns a reverse shell via netcat without Metasploit, targeting remote hosts for…
 runt1me/cve-2025-50946
Exploit script for CVE-2025-50946
 sqldebugger/cve-2019-0708-tool
50 first stargazers will get get the tool via email
 mananispiwpiw/cve-2025-8110-poc
One-shot exploit for Gogs symlink RCE (CVE-2025-8110) that triggers a reverse shell via a single PUT request to UpdateRepoFile.
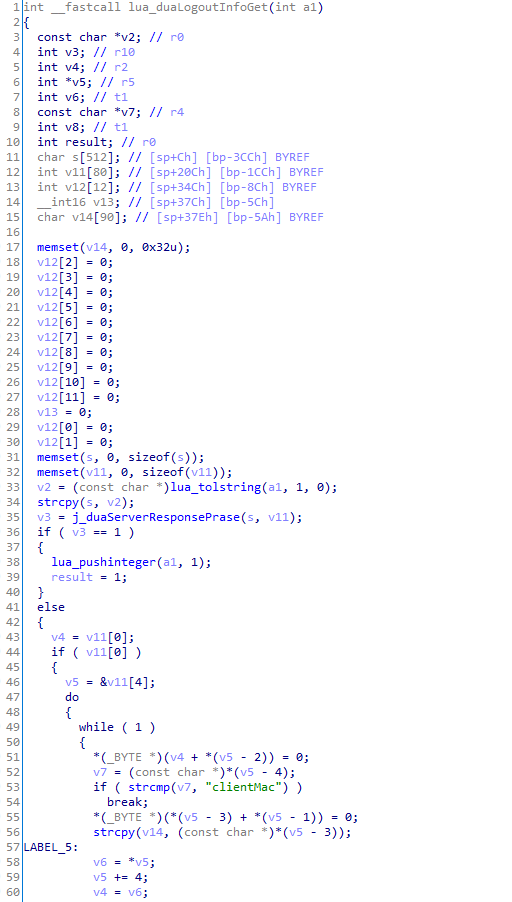 delspon/cve-2024-57376
CVE-2024-57376 exploit
 aperocky/bepr
A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.
 mbadanoiu/java-servlets-shell
JSP-less Java Servlets Backdoor inspired by https://www.redteam-pentesting.de/files/redteam-jboss.tar.gz