CVE-2024-415770-ssrf-rce

Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…

Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…

Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…

This repository contains alternative payload approaches for the InvokeAI RCE vulnerability (CVE-2024-12029) when SSH key injection fails. The…

Erlang/OTP SSH Vulnerable to Pre-Authentication RCE

Python exploit for CVE-2025-32433 targeting Erlang SSH remote code execution with reverse shell and command execution capabilities.

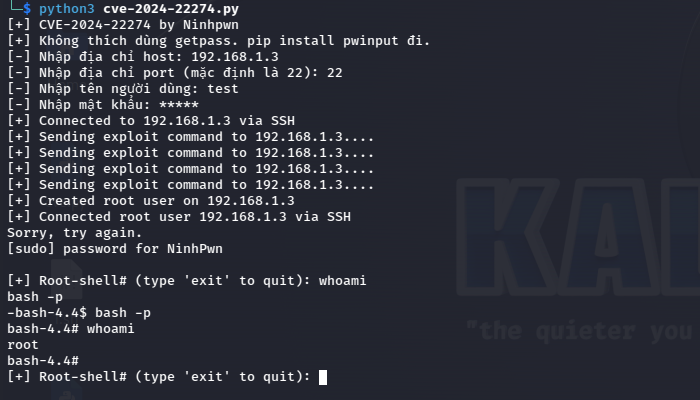
Go-based exploit for CVE-2024-22274 that creates a new user via SSH and provides a root shell on the target machine for authorized penetration…

Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.

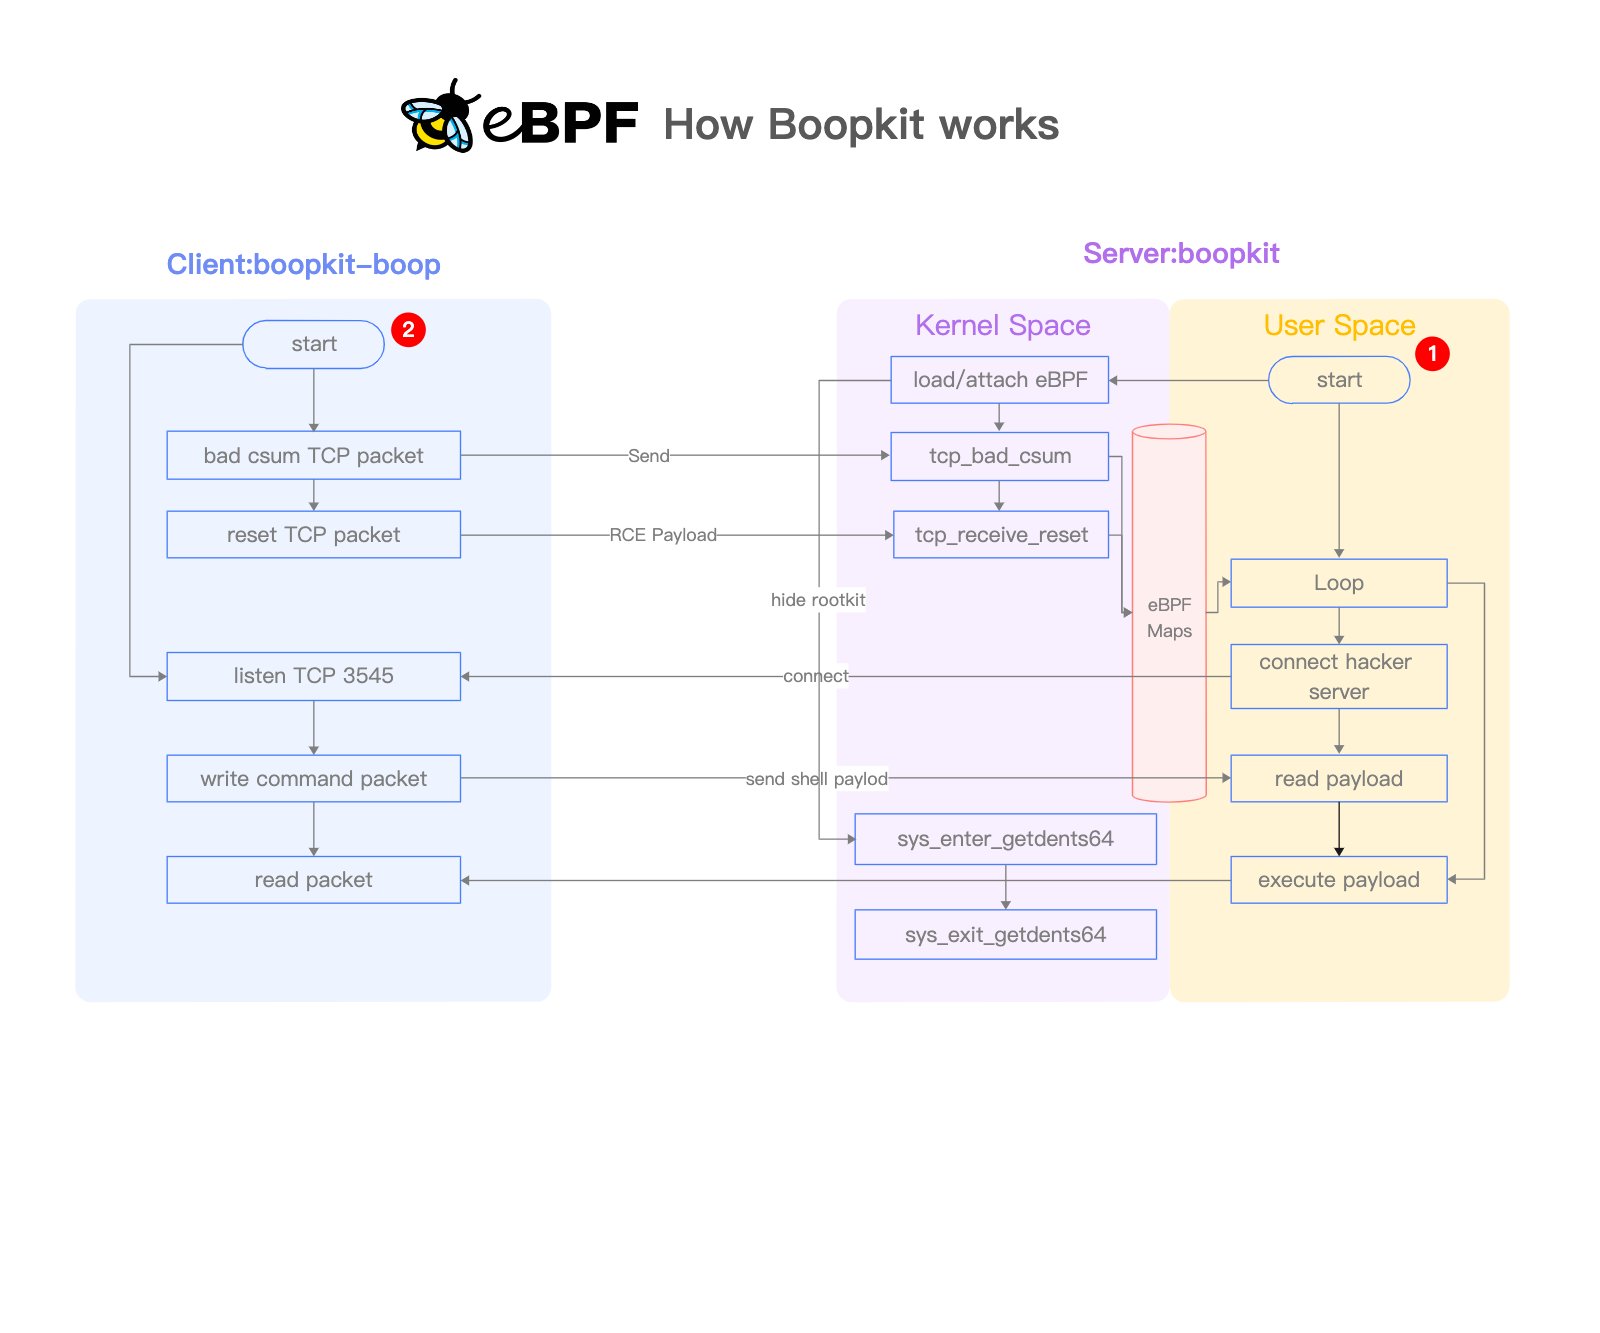
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.

SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)

Modified dropbear server which acts as a client and allows authless login

自研针对ESXI 堆栈溢出的CVE-2021-21974 POC,只支持项目给出的的目标和环境,用于学习和研究

Exploit for CVE-2014-4210 targeting WebLogic deserialization, with post-exploitation features including ransomware deployment, C2 integration, and…

CVE-2023-34039

VMware exploit