

redsnarf
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
command-and-controlexploitationhash-analysis+9
nccgroup/redsnarfRedSnarf is a pen-testing / red-teaming tool for Windows environments
 1n7erface/poclist
Vulnerability-specific PoC scripts for discovering and exploiting RCE, SQLi, XXE, SSRF, and unauthorized-access flaws in enterprise web apps and…
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 trustedsec/cve-2019-19781
This is a tool published for the Citrix ADC (NetScaler) vulnerability. We are only disclosing this due to others publishing the exploit code first.
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 nccgroup/wmicmd
A command shell wrapper using only WMI for Microsoft Windows
 rickdejager/cupshax
Quick proof-of-concept for recent CUPS exploit enabling remote code execution via PPD injection and DNS-SD printer discovery. Executes arbitrary…
 yasserjanah/cve-2020-5902
exploit code for F5-Big-IP (CVE-2020-5902)
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
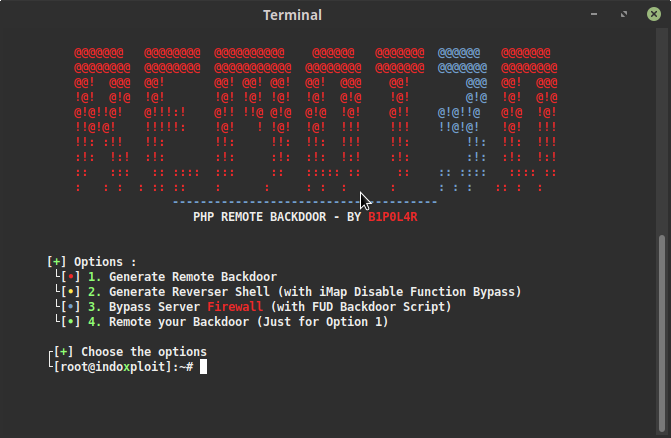 makiraid/remot3d
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
 649/pingpon-exploit
Exploit for Mass Remote Code Execution on GPON home routers (CVE-2018-10562) obtained from Shodan.
 behzadmagzer/auto-postxploit
Windows Auto Post Exploitation - For ReD Team
 truekas/ls-poc
Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.
 mosaedh/cve-2022-32548-rce-poc
Python-based proof-of-concept exploit for CVE-2022-32548, an unauthenticated remote code execution vulnerability in DrayTek routers via buffer…
 nulltrace0x/cve-2025-31324
Proof-of-concept exploit for CVE-2025-31324, a remote code execution vulnerability in SAP NetWeaver, with Shodan dorks for target discovery and…
 nullbytesuitedevs/cve-2019-0708
PoC exploit for BlueKeep (CVE-2019-0708)
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…