
cve-2019-0708-exp
 jaky5155/cve-2019-0708-exp
Exploit for CVE-2019-0708 (BlueKeep) targeting Windows RDP vulnerabilities in XP and 7, enabling remote code execution for penetration testing.
exploitationpayload-generationpenetration-testing+2
30
jaky5155/cve-2019-0708-expExploit for CVE-2019-0708 (BlueKeep) targeting Windows RDP vulnerabilities in XP and 7, enabling remote code execution for penetration testing.
 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
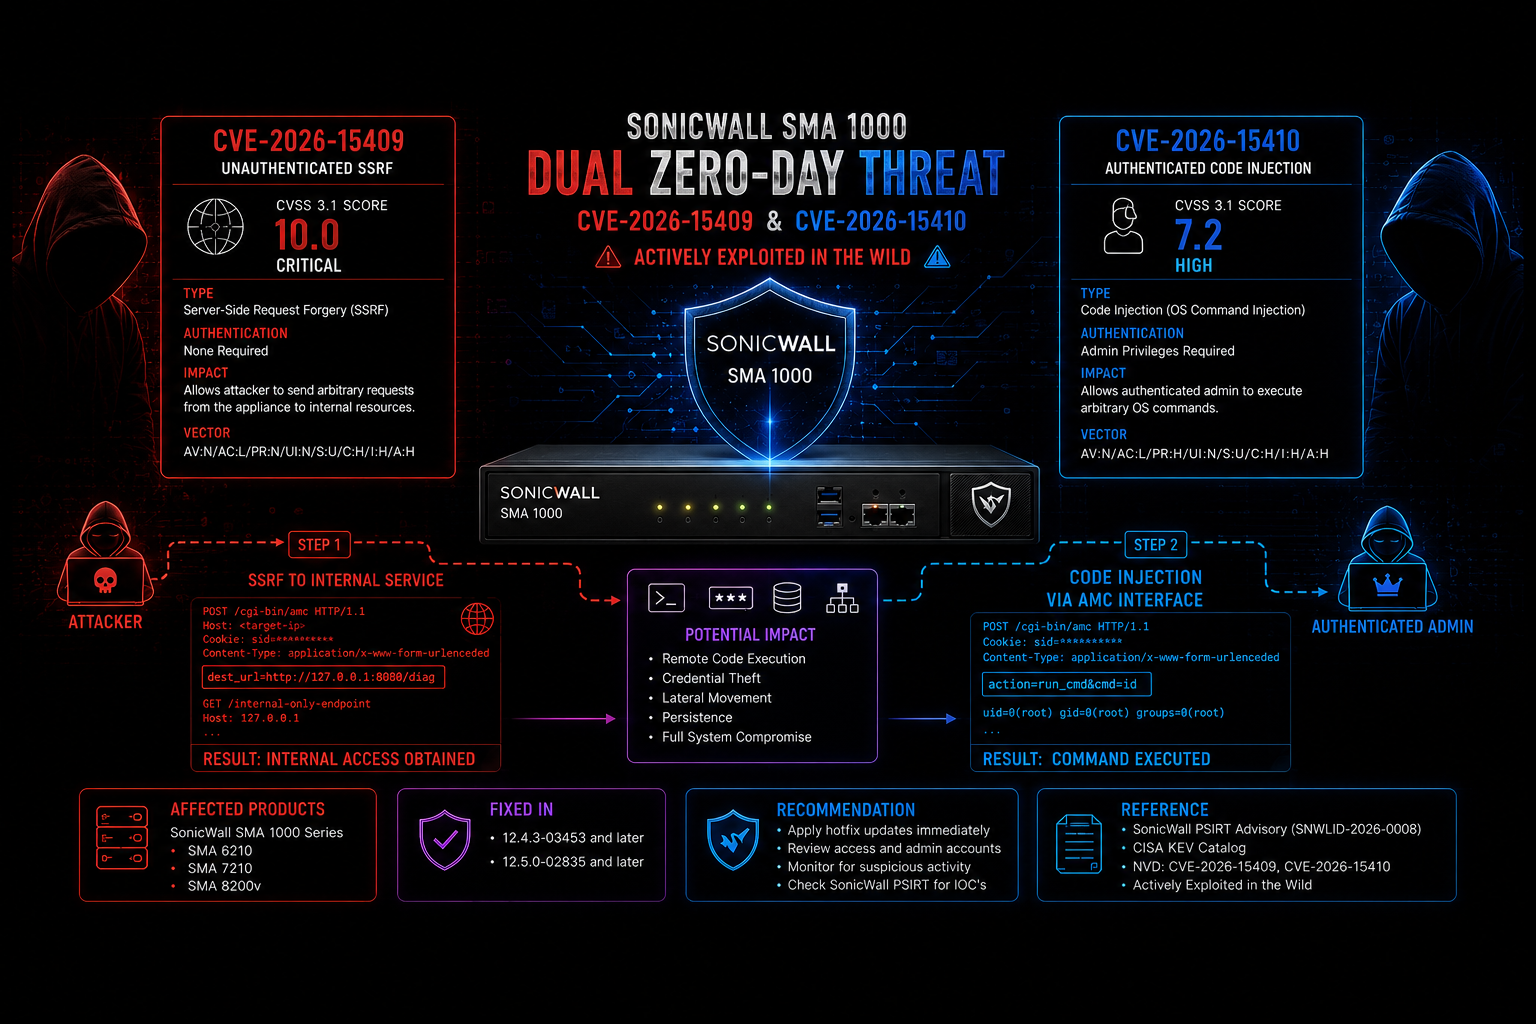 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 ze0r/cve-2019-0708-exp
Exploit for CVE-2019-0708 (BlueKeep) targeting RDP vulnerability in Windows systems, enabling remote code execution for penetration testing and…
 bardlaudian/cve-2018-9276
CVE-2018-9276 — PRTG Network Monitor < 18.2.39 Authenticated RCE. For educational purposes and authorized penetration testing only.
 hackerj0e/cve-2019-0708
Exploit for CVE-2019-0708 (BlueKeep) targeting RDP vulnerability in legacy Windows systems, enabling remote code execution for penetration testing…
 mishaqdev/cve-2010-2075-analysis
Technical writeup and penetration testing report for CVE-2010-2075, demonstrating UnrealIRCd backdoor exploitation and remediation.
 qianniaoge/cve-2020-14882_exploit_gui
GUI-based exploit tool for CVE-2020-14882 targeting Oracle WebLogic servers. Supports reverse shell payload generation, proxy configuration, and…
 givemefivw/cve-2019-12725
Python-based exploit for CVE-2019-12725 targeting ZeroShell remote command execution vulnerability. Designed for penetration testing and educational…
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
 ilixm/poc-rce-cve-2025-55182
Advanced RCE exploitation toolkit for React Server Components vulnerabilities. Features multiple pre-built payloads, Shodan integration for target…
 faizanali8232/cve-exploit-research-development
A professional Python tool designed for educational penetration testing, demonstrating SSH vulnerabilities (CVE-2008-0166 / CVE-2008-1657) with…
 ianxtianxt/ssocks-0.0.14
SOCKS proxy for port forwarding and RDP tunneling, enabling lateral movement and remote access in penetration testing scenarios.
 pywc/cve-2019-0708
Python-based exploit for CVE-2019-0708 (BlueKeep) targeting RDP vulnerability in legacy Windows systems for authorized penetration testing.
 lamsonbinh/cve-2018-20250
Exploit script for CVE-2018-20250 (WinRAR ACE path traversal) with integrated Metasploit payload generation and reverse shell delivery for…
 mustafa1986/cve-2024-22274-rce
Go-based exploit for CVE-2024-22274 that creates a new user via SSH and provides a root shell on the target machine for authorized penetration…
 olingo99/cve-2019-15107
Proof-of-concept exploit for CVE-2019-15107, delivering a reverse shell via a crafted Perl payload for educational penetration testing.
 h3x0v3rl0rd/freepbx-reverse-shell-module
Exploit module for FreePBX delivering a reverse shell payload to achieve remote command execution and persistent shell access, designed for…