

eximrce-CVE-2019-10149
 cowbe0x004/eximrce-cve-2019-10149
simple python socket connection to test if exim is vulnerable to CVE-2019-10149. The payload simply touch a file in /tmp/eximrce.
exploitationpenetration-testingremote-access-tool+2
14
cowbe0x004/eximrce-cve-2019-10149simple python socket connection to test if exim is vulnerable to CVE-2019-10149. The payload simply touch a file in /tmp/eximrce.
 gunyakit/cve-2025-24813-poc-exploit
Proof-of-concept exploit for Apache Tomcat deserialization RCE (CVE-2025-24813). Uploads a crafted session file via PUT request and triggers…
 nxploited/cve-2026-1555
WebStack <= 1.2024 - Unauthenticated Arbitrary File Upload
 bridgeralderson/cve-2025-69212-poc
OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 jayanaxhf/filessh
A fast and convenient TUI file browser for remote servers
 tomadimitrie/cve-2026-54424
Exploiting Parsec for Windows to gain SYSTEM privileges
 mchoudhary15/cve-2022-22029-nfs-server-
Proof-of-concept exploit for CVE-2022-22029, a Windows NFS remote code execution vulnerability. Includes PowerShell commands to disable NFSV3 as a…
 nudttan91/webmin-cve-2022-0824-enhanced-exploit
Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…
 vulncheck-oss/cve-2025-0364
CVE-2025-0364: BigAnt Server RCE Exploit
 archive-puma/securitynotfound
Stealthy PHP webshell disguised as a 404 error page with AJAX console, hidden command execution via Referrer header, and preconfigured actions for…
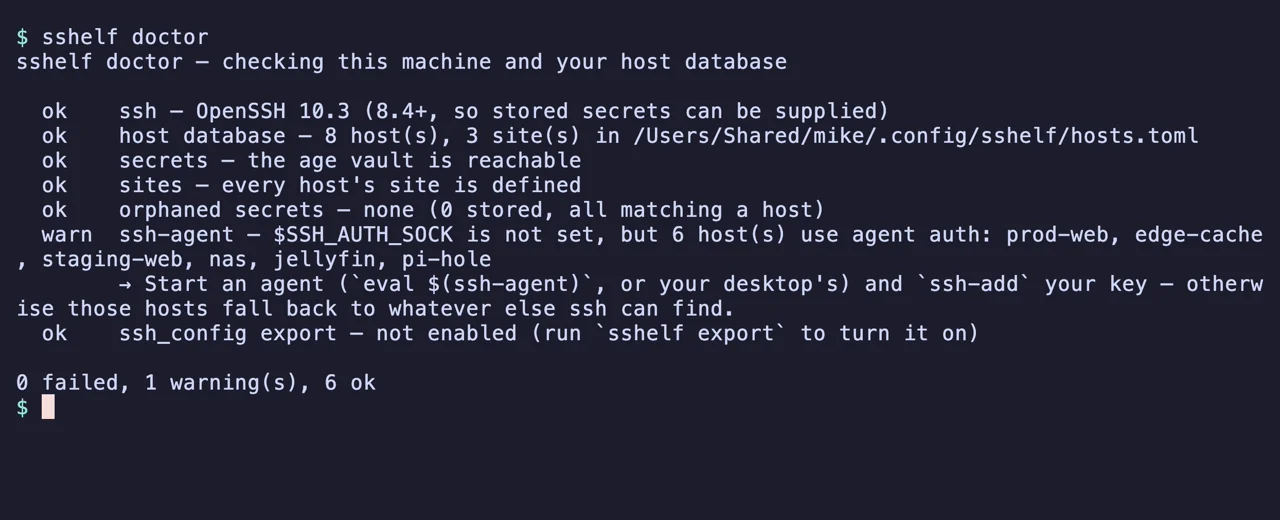 max-rh/sshelf
Fast terminal UI for your SSH hosts: fuzzy-search and connect in two keystrokes, dual-pane SFTP file transfer, and background port forwarding. Keeps…
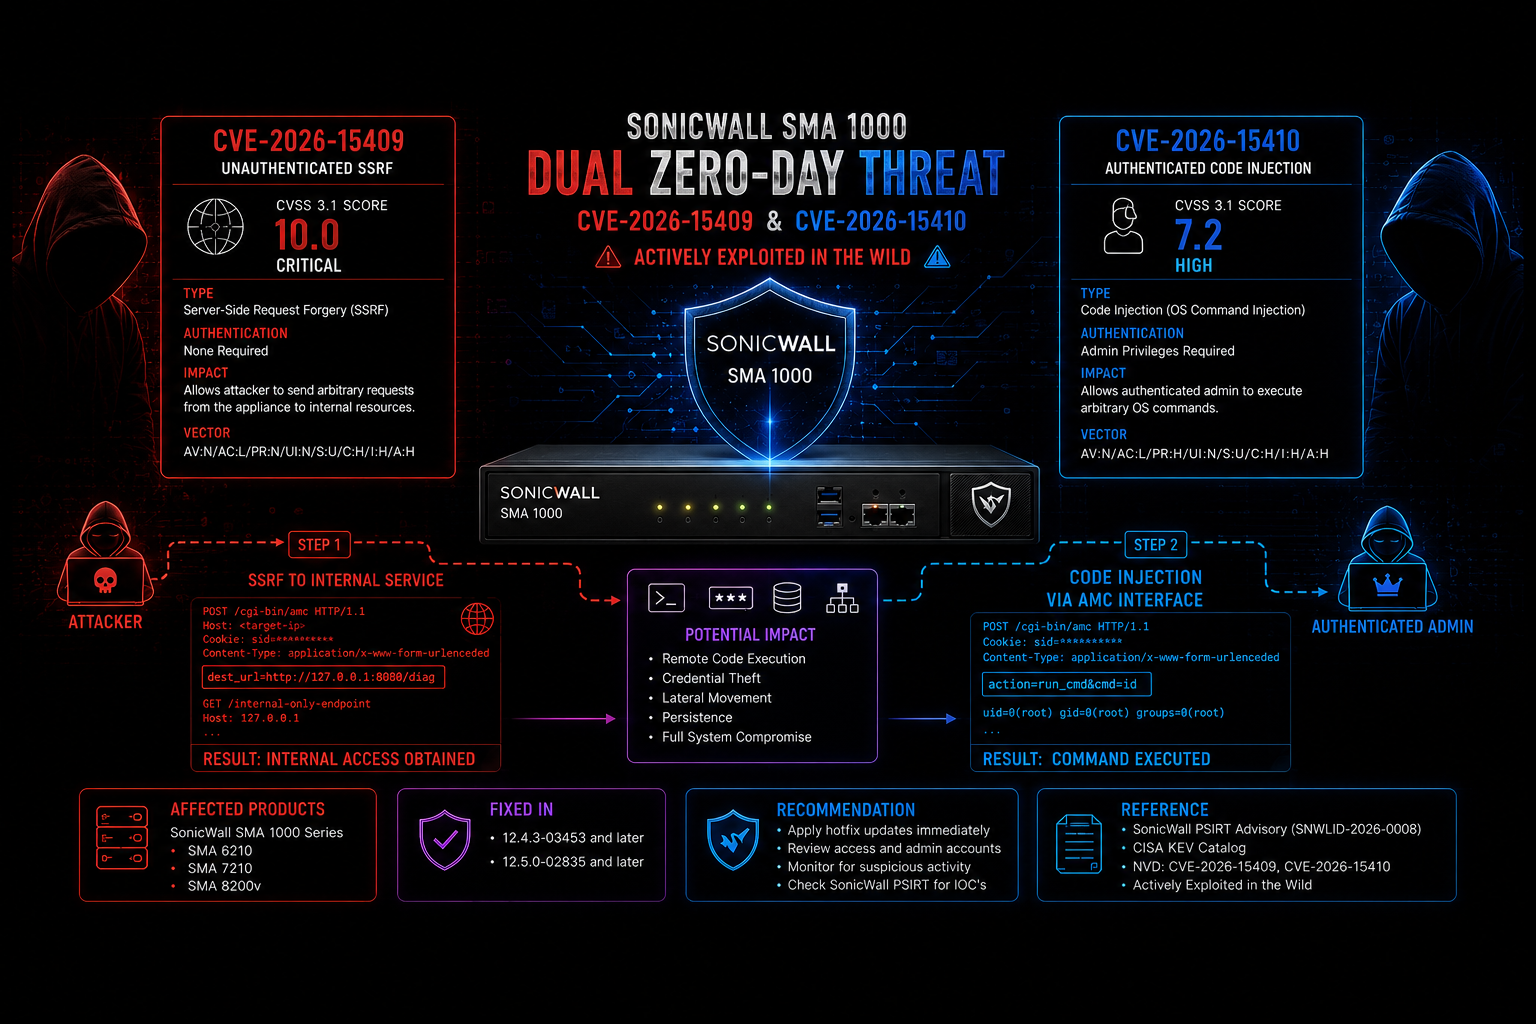 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 smit-shah-gg/phone-deck
Self-hosted control deck and remote desktop for Linux workstations over Tailscale, featuring WebRTC streaming, voice control with local LLM, scene…
 hev0x/cve-2021-26828_scadabr_rce
Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…
 dexit/cve-2022-1329
CVE-2022-1329 exploit for WordPress Elementor plugin (3.6.0-3.6.2) enabling authenticated remote code execution via missing capability check and…
 jinhao-l/poc-for-cve-2020-28948-cve-2020-28949
Proof-of-concept exploit for CVE-2020-28948 and CVE-2020-28949 targeting PHAR deserialization and inclusion vulnerabilities in Archive_Tar, enabling…