
CANalyse
 kartheeklade/canalyse
A vehicle network analysis and attack tool.
exploitationhardware-hackingremote-access-tool
kartheeklade/canalyseA vehicle network analysis and attack tool.
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 sinsinology/cve-2023-34039
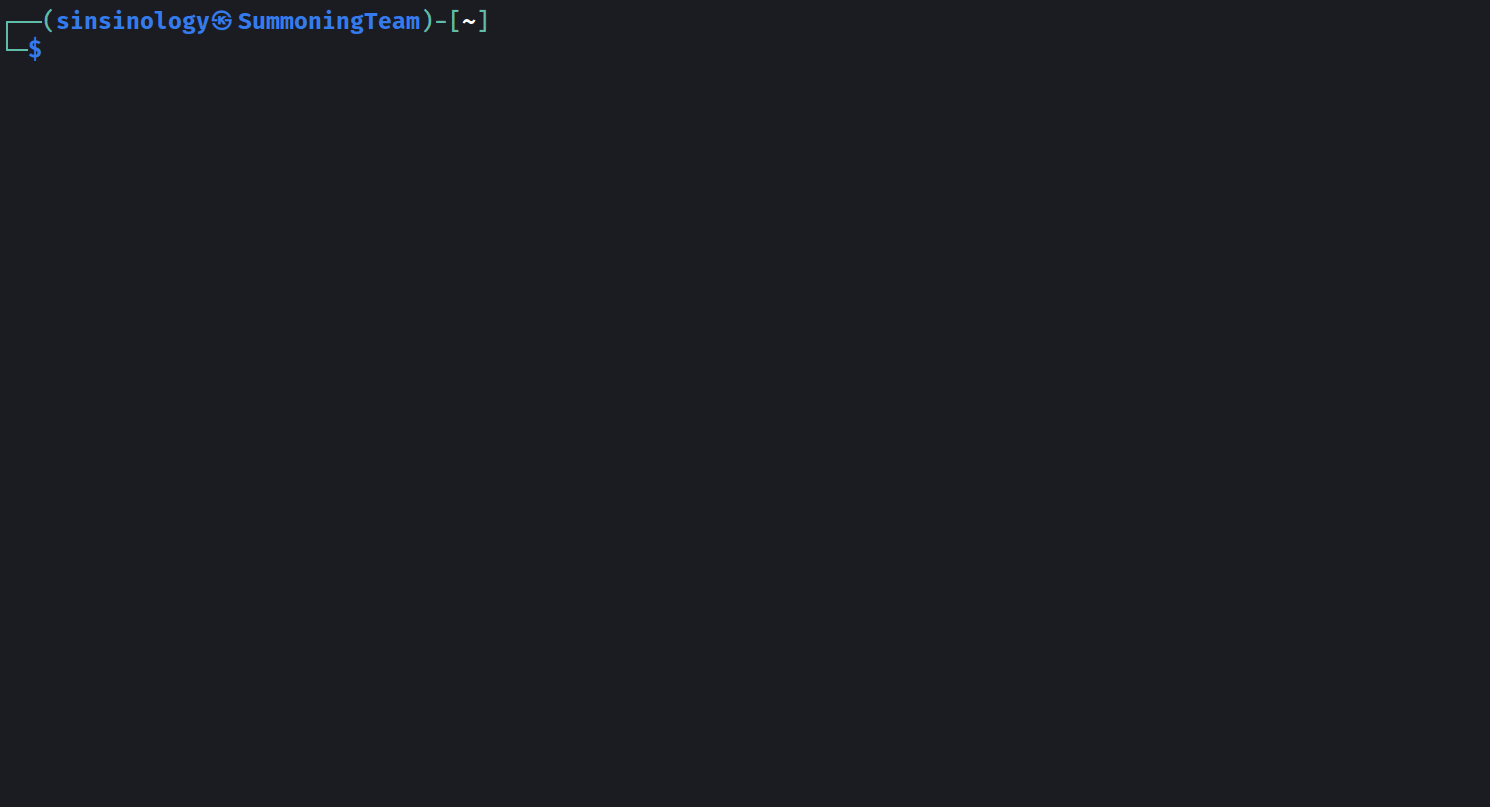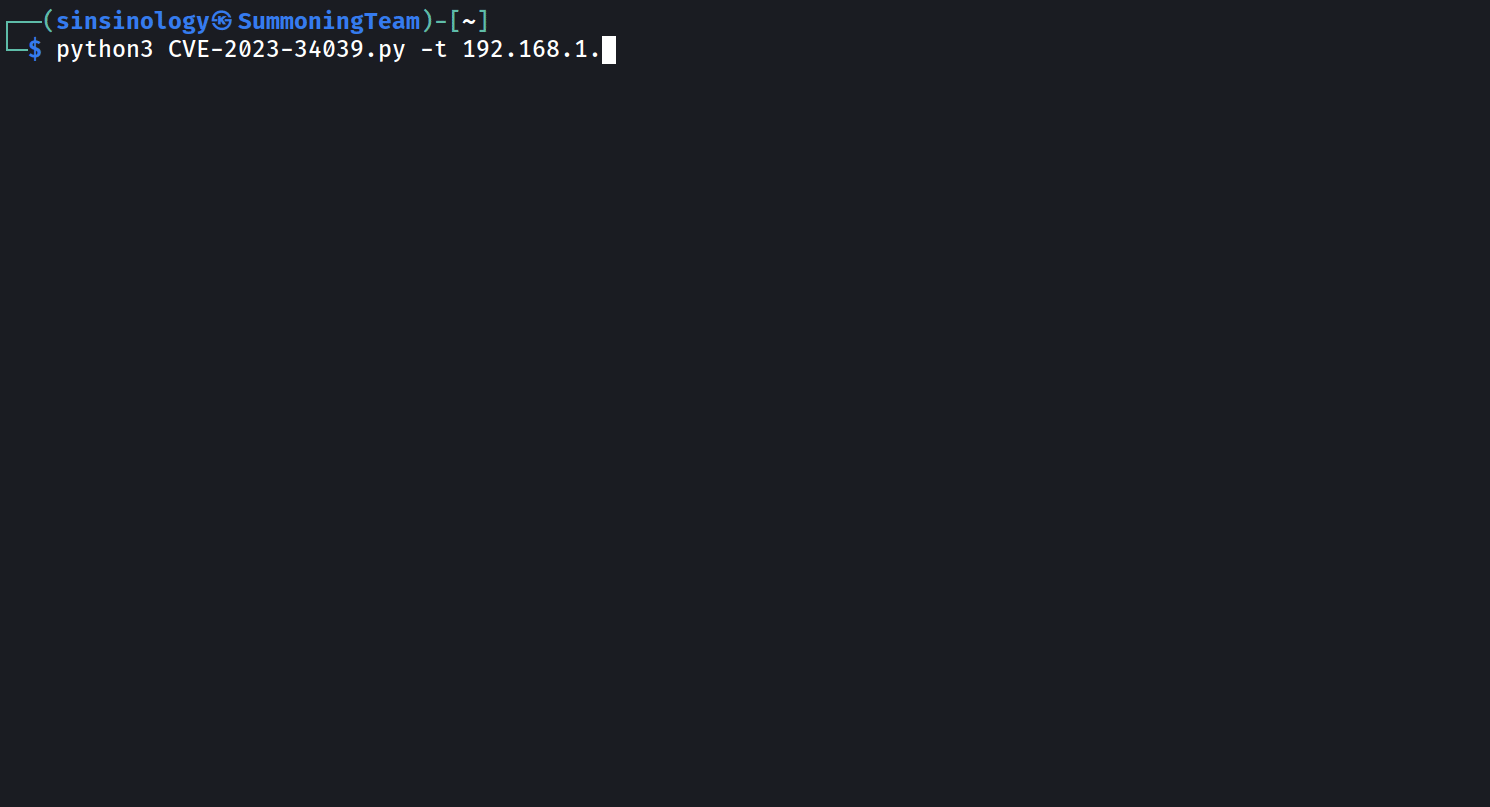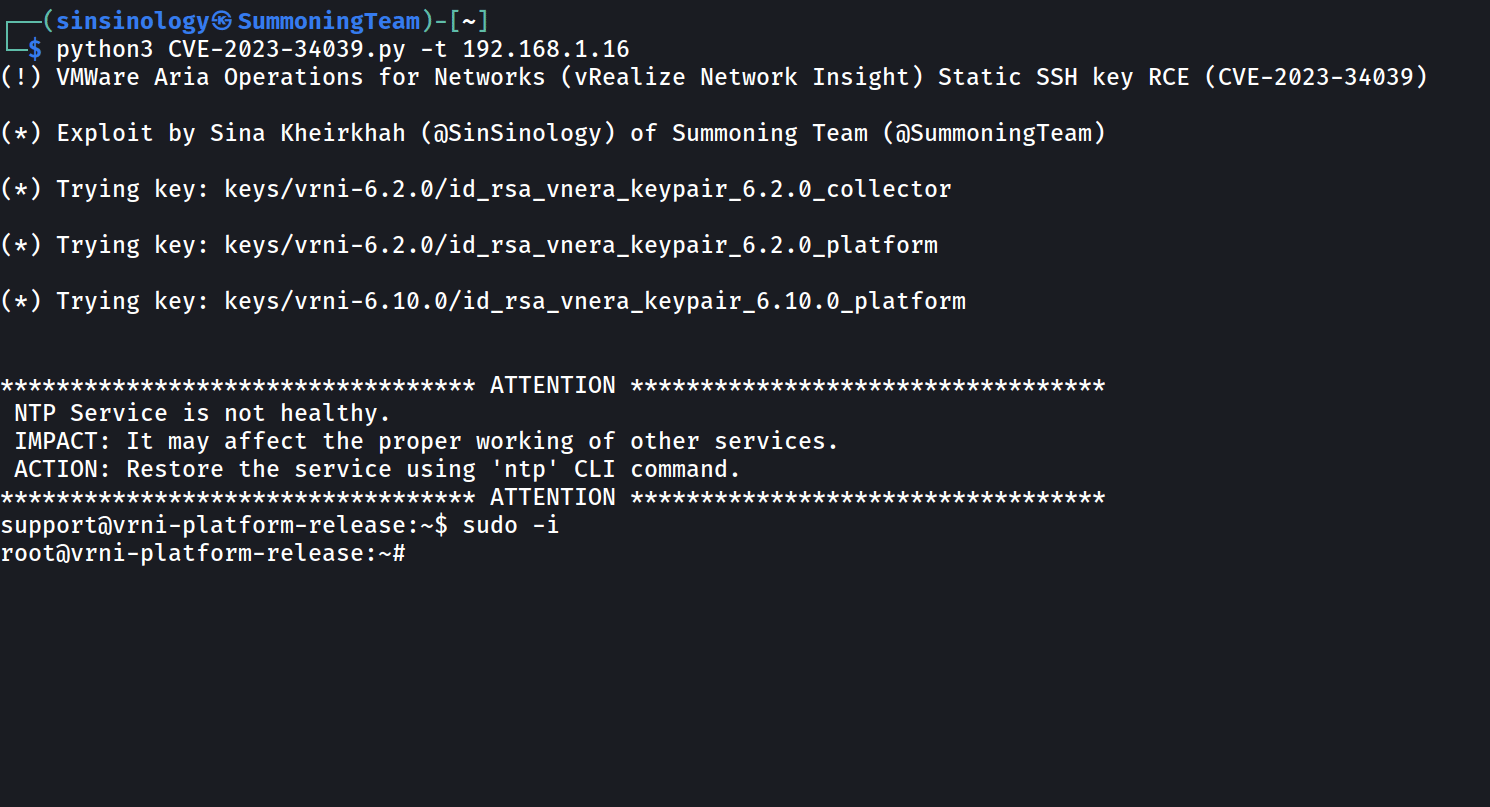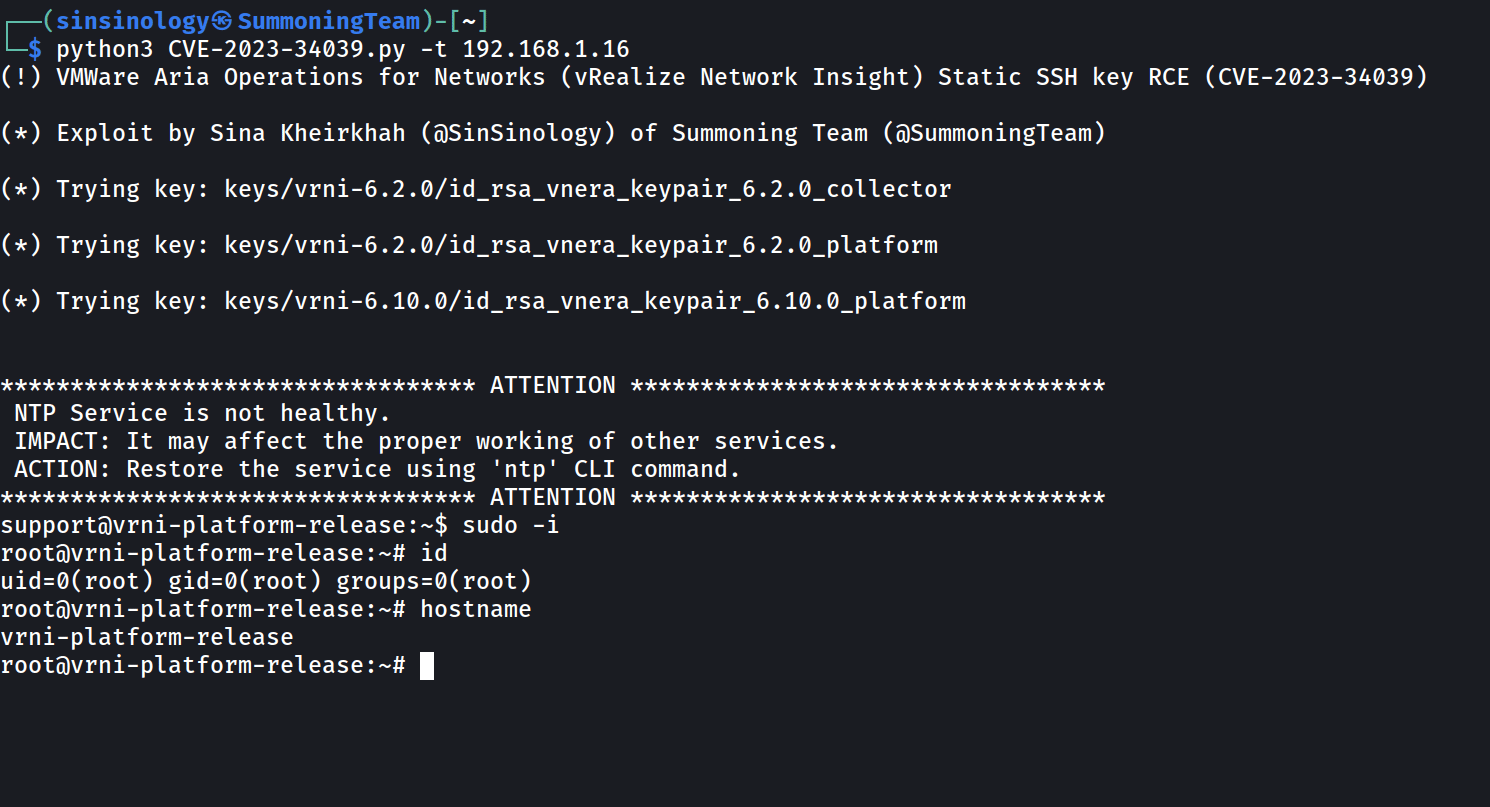
VMWare Aria Operations for Networks (vRealize Network Insight) Static SSH key RCE (CVE-2023-34039)
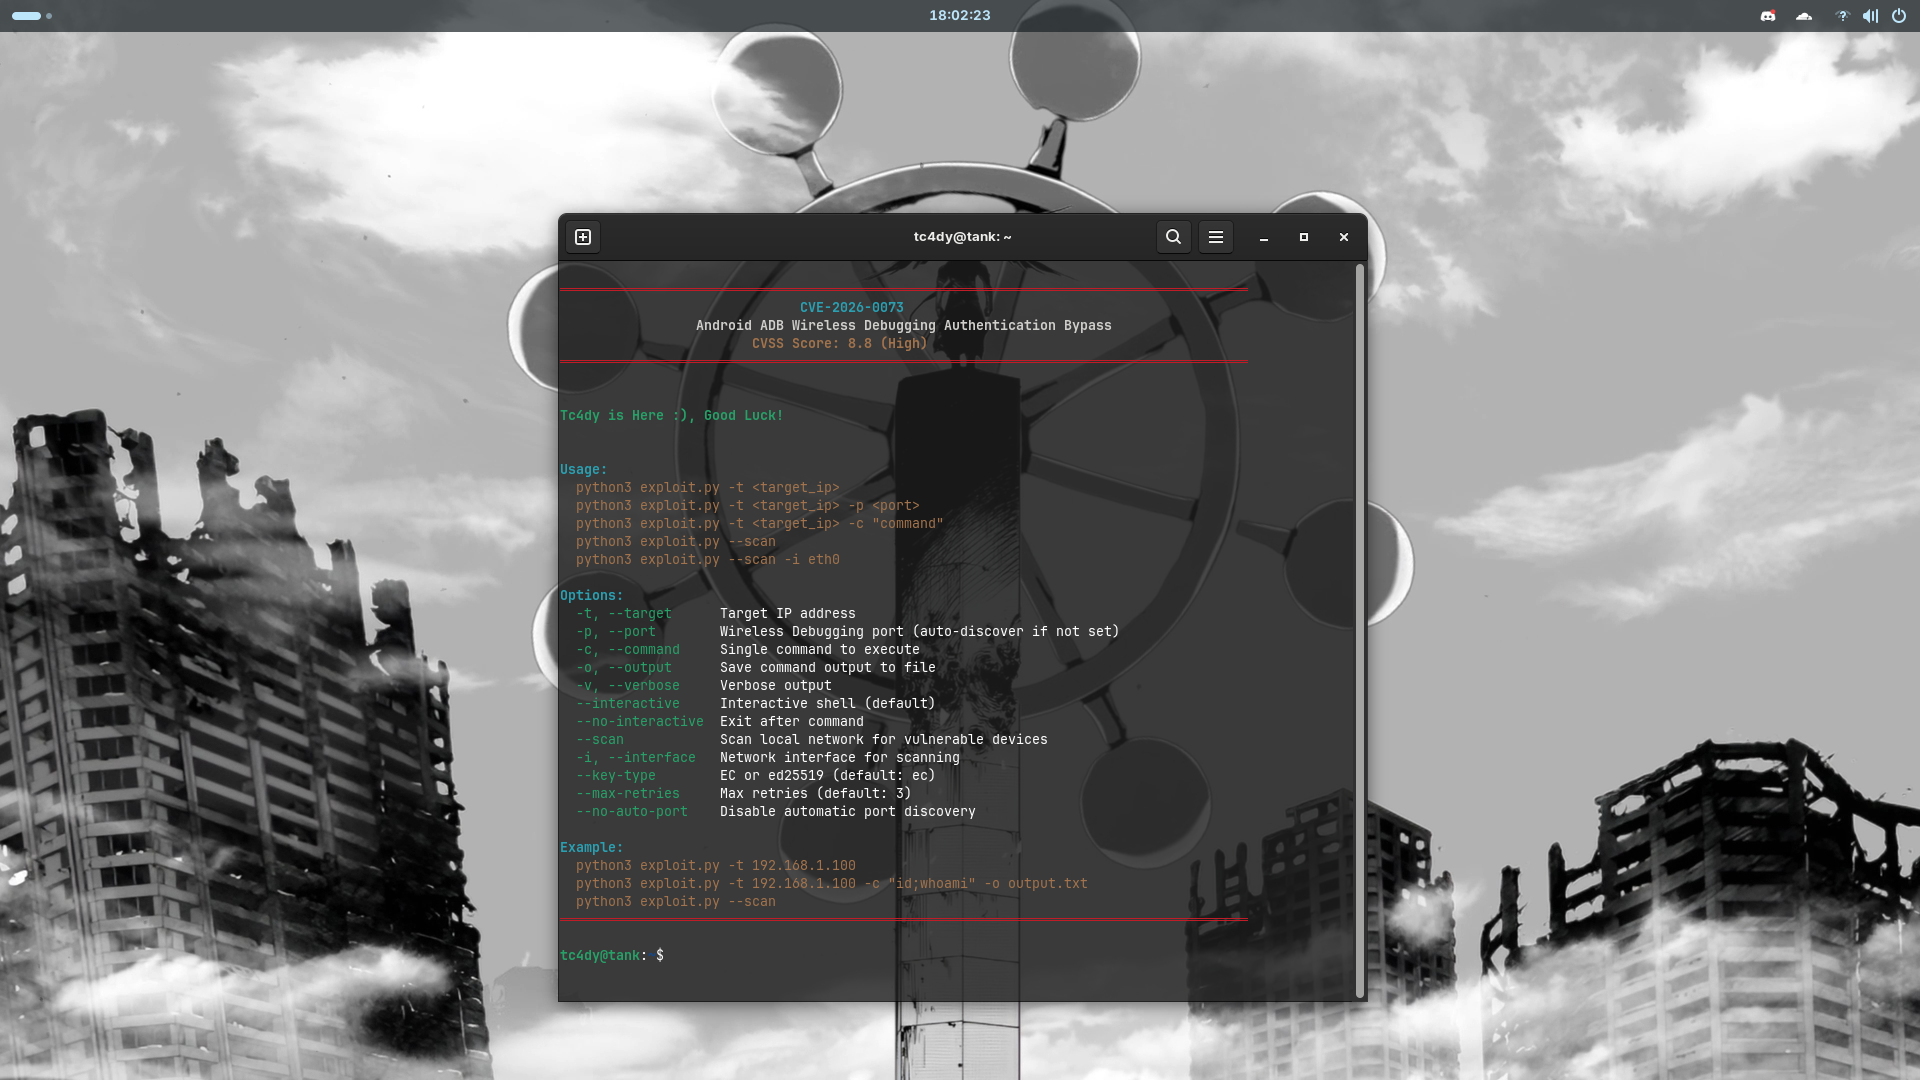 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 fortra/cve-2022-30136
Windows Network File System Remote exploit for CVE-2022-30136
 hoav18/cve-2021-22941
Python exploit for CVE-2021-22941 targeting Citrix ShareFile RCE with shell and ping options for remote command execution and network probing.
 omer-efe-curkus/cve-2025-32433-erlang-otp-ssh-rce-poc
The vulnerability allows an attacker with network access to an Erlang/OTP SSH server to execute arbitrary code without prior authentication.
 machine1337/smtpshell
A simple Reverse Shell that can communicate through Gmail SMTP or any other SMTP to evade network restrictions
 bardlaudian/cve-2018-9276
CVE-2018-9276 — PRTG Network Monitor < 18.2.39 Authenticated RCE. For educational purposes and authorized penetration testing only.
 jiansiting/cve-2019-3719
Proof-of-concept exploit for CVE-2019-3719, a remote code execution vulnerability in Dell SupportAssist. Executes arbitrary payloads against…
 miko550/cve-2023-20887
VMWare vRealize Network Insight Pre-Authenticated RCE (CVE-2023-20887)
 geniuszly/cve-2022-45701
it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…
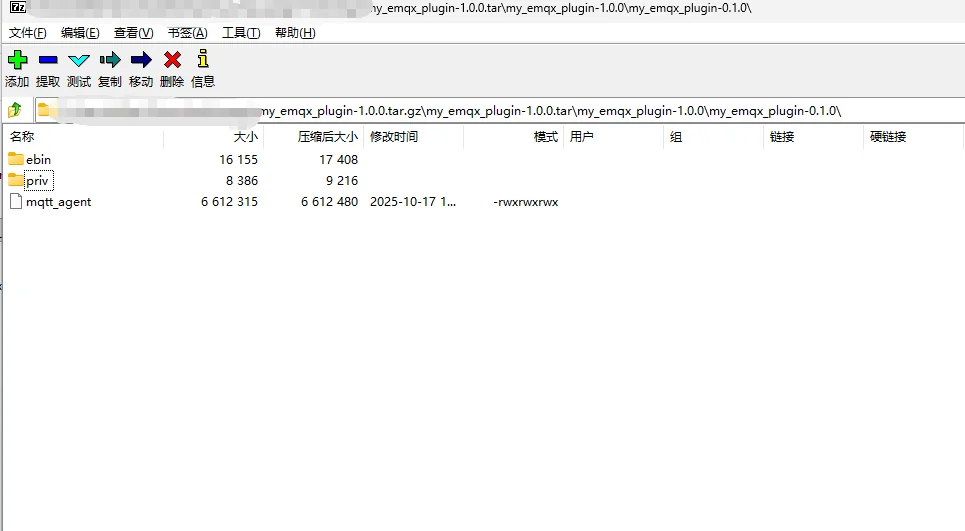 f1r3k0/cve-2025-52136
Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…
 zorvithonleo/exploit-cve-2014-4210-
Exploit for CVE-2014-4210 targeting WebLogic deserialization, with post-exploitation features including ransomware deployment, C2 integration, and…
 h0j3n/cve-2020-23934
Python exploit script for CVE-2020-23934, achieving authenticated remote code execution on PRTG Network Monitor via crafted multipart form-data…
 mrterrestrial/cve-2023-50564
This script exploits the file upload feature in Pluck CMS v4.7.18 to upload a malicious PHP file, enabling remote access via a reverse shell. Once…
 cyghtinc/cve-2025-26686-poc-a-critical-rce-vulnerability-in-windows-tcp-ip-stack
POC for CVE-2025-26686 - A critical RCE vulnerability in Windows TCP/IP stack (CVE-2025-26686) leaves sensitive memory unlocked, allowing remote…
 mr-r00t11/cve-2024-23692
Rejetto HFS (HTTP File Server) is a simple web file server that facilitates file sharing over a network or the internet.