

Arduino-Netcat-Backdoor
 davidkowalk/arduino-netcat-backdoor
*Proof of concept* Attacks a Windows machine running Windows 7 or later, creating a persistent Backdoor.
command-and-controlexploitationhardware-hacking+7
5
davidkowalk/arduino-netcat-backdoor*Proof of concept* Attacks a Windows machine running Windows 7 or later, creating a persistent Backdoor.
 netspi/cve-2025-4660
PoC for CVE-2025-4660 demonstrating exploitation of the Forescout SecureConnector on Windows
 luantak/torat
ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
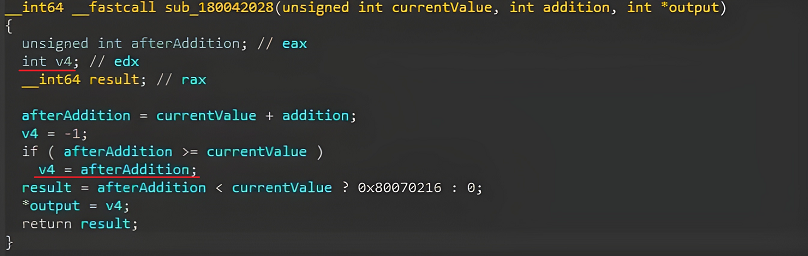 mr-alperen/cve-2022-26810
Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…
 nccgroup/wmicmd
A command shell wrapper using only WMI for Microsoft Windows
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 softdeadlock/voron-crypto
Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested
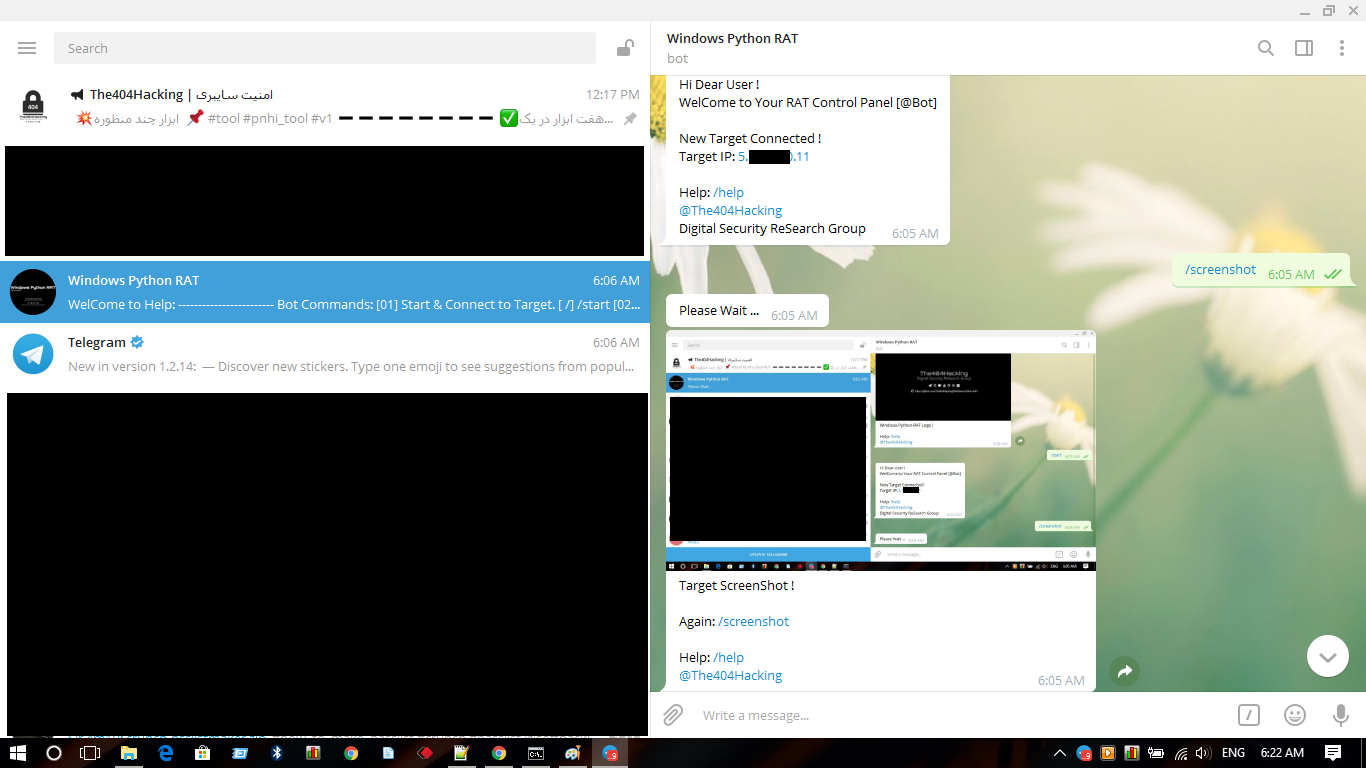 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
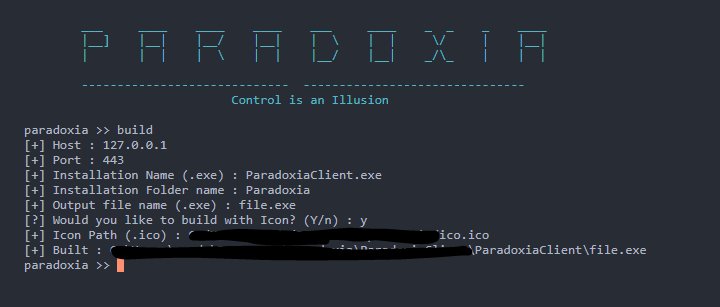 quantumcore/paradoxiarat
ParadoxiaRat : Native Windows Remote access Tool.
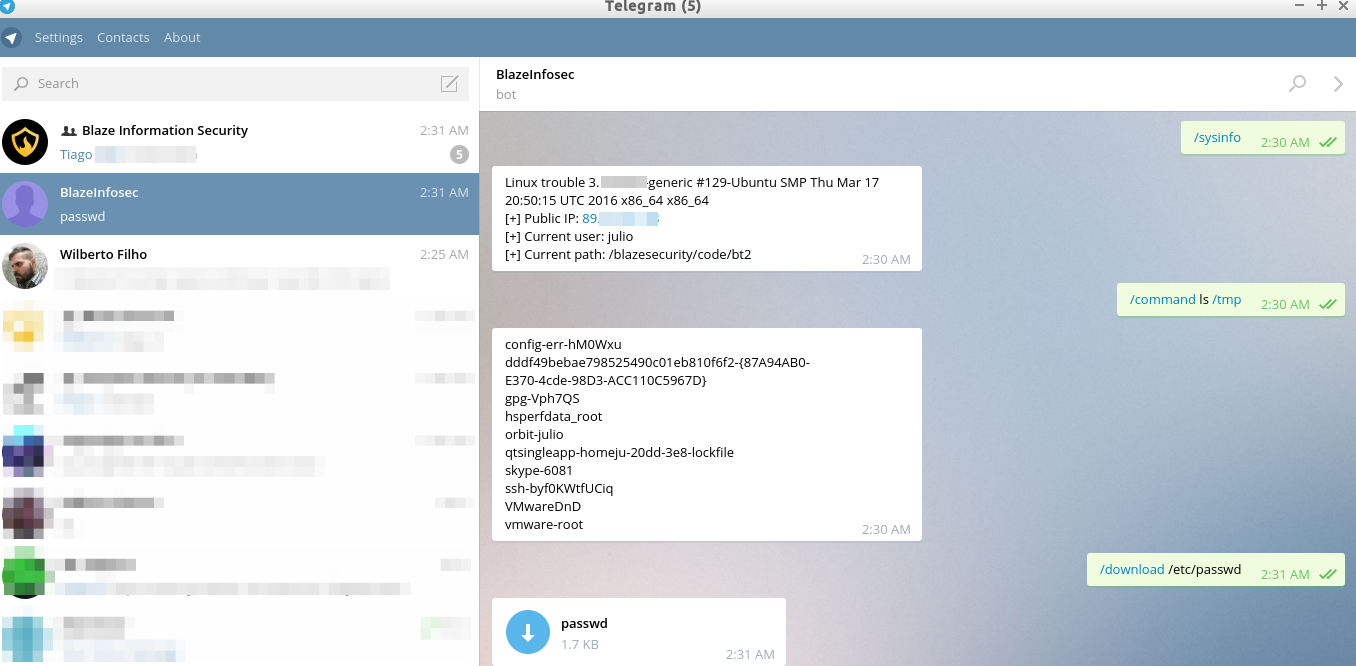 blazeinfosec/bt2
Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 mvrozanti/rat-via-telegram
Windows Remote Administration Tool via Telegram
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 ghostpack/sharpwmi
SharpWMI is a C# implementation of various WMI functionality.
 them4hd1/vayne-rat
An Advanced C# .NET Rat, It’s Stable and Contains Many Features.
 thatcherclough/betterbackdoor
A backdoor with a multitude of features.
 redsiege/cimplant
C# port of WMImplant which uses either CIM or WMI to query remote systems