
c2s
 j3ssie/c2s
Command and Control server on Slack
command-and-controlpenetration-testingpost-exploitation+2
j3ssie/c2sCommand and Control server on Slack
 sshuttle/sshuttle
Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 maldevel/gdog
A fully featured Windows backdoor that uses Gmail as a C&C server
 aiminsun/cve-2021-36260
command injection vulnerability in the web server of some Hikvision product. Due to the insufficient input validation, attacker can exploit the…
 maldevel/canisrufus
A stealthy Python based Windows backdoor that uses Github as a command and control server
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 lnxg33k/webhandler
Bash simulator to control a server using PHP system functions.
 jas502n/cve-2018-3191
Exploit for CVE-2018-3191 targeting Oracle WebLogic Server via T3 protocol, enabling unauthenticated remote code execution with JNDI payload…
 thehermione/cve-2023-28231
DHCP Server Remote Code Execution impact: 2008 R2 SP1 до Server 2019
 calfcrusher/maccaronic2
A proof-of-concept Command & Control framework that utilizes the powerful AsyncSSH Python library which provides an asynchronous client and server…
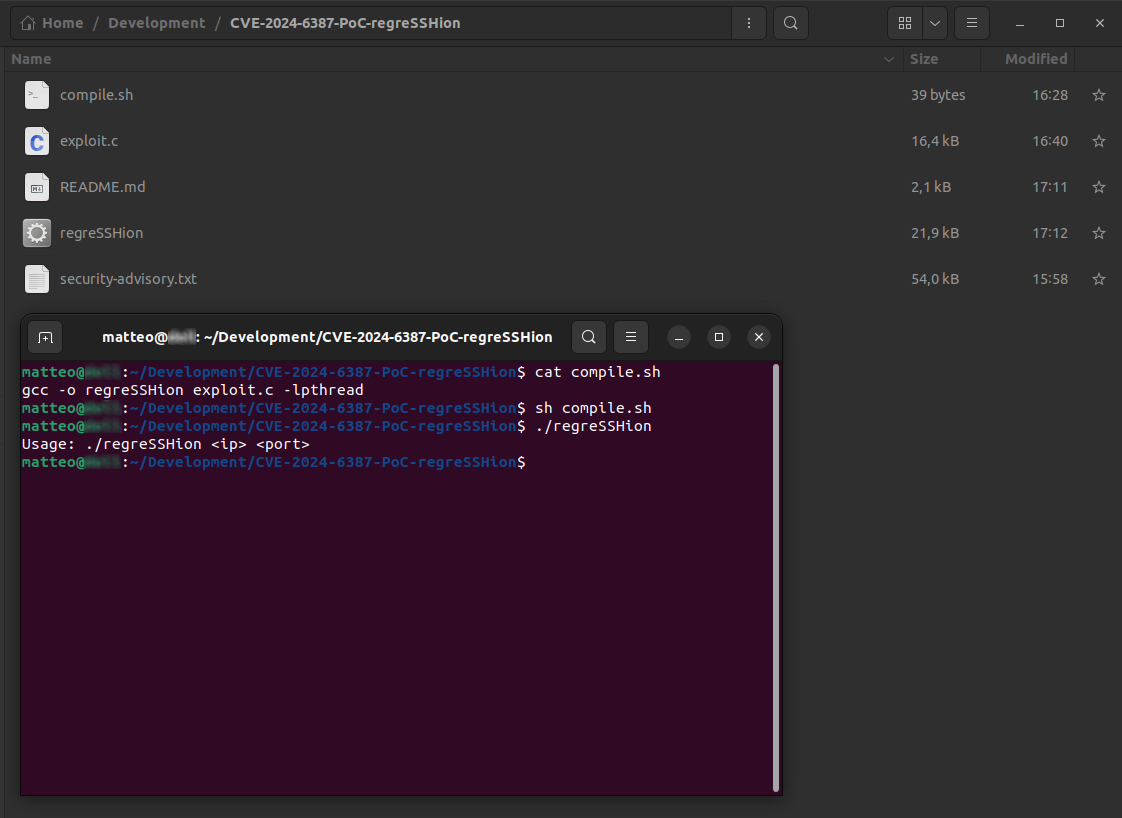 xonoxitron/regresshion
CVE-2024-6387 (regreSSHion) Exploit (PoC), a vulnerability in OpenSSH's server (sshd) on glibc-based Linux systems.
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 4m3rr0r/cve-2025-47812-poc
Wing FTP Server Remote Code Execution (RCE) Exploit (CVE-2025-47812)
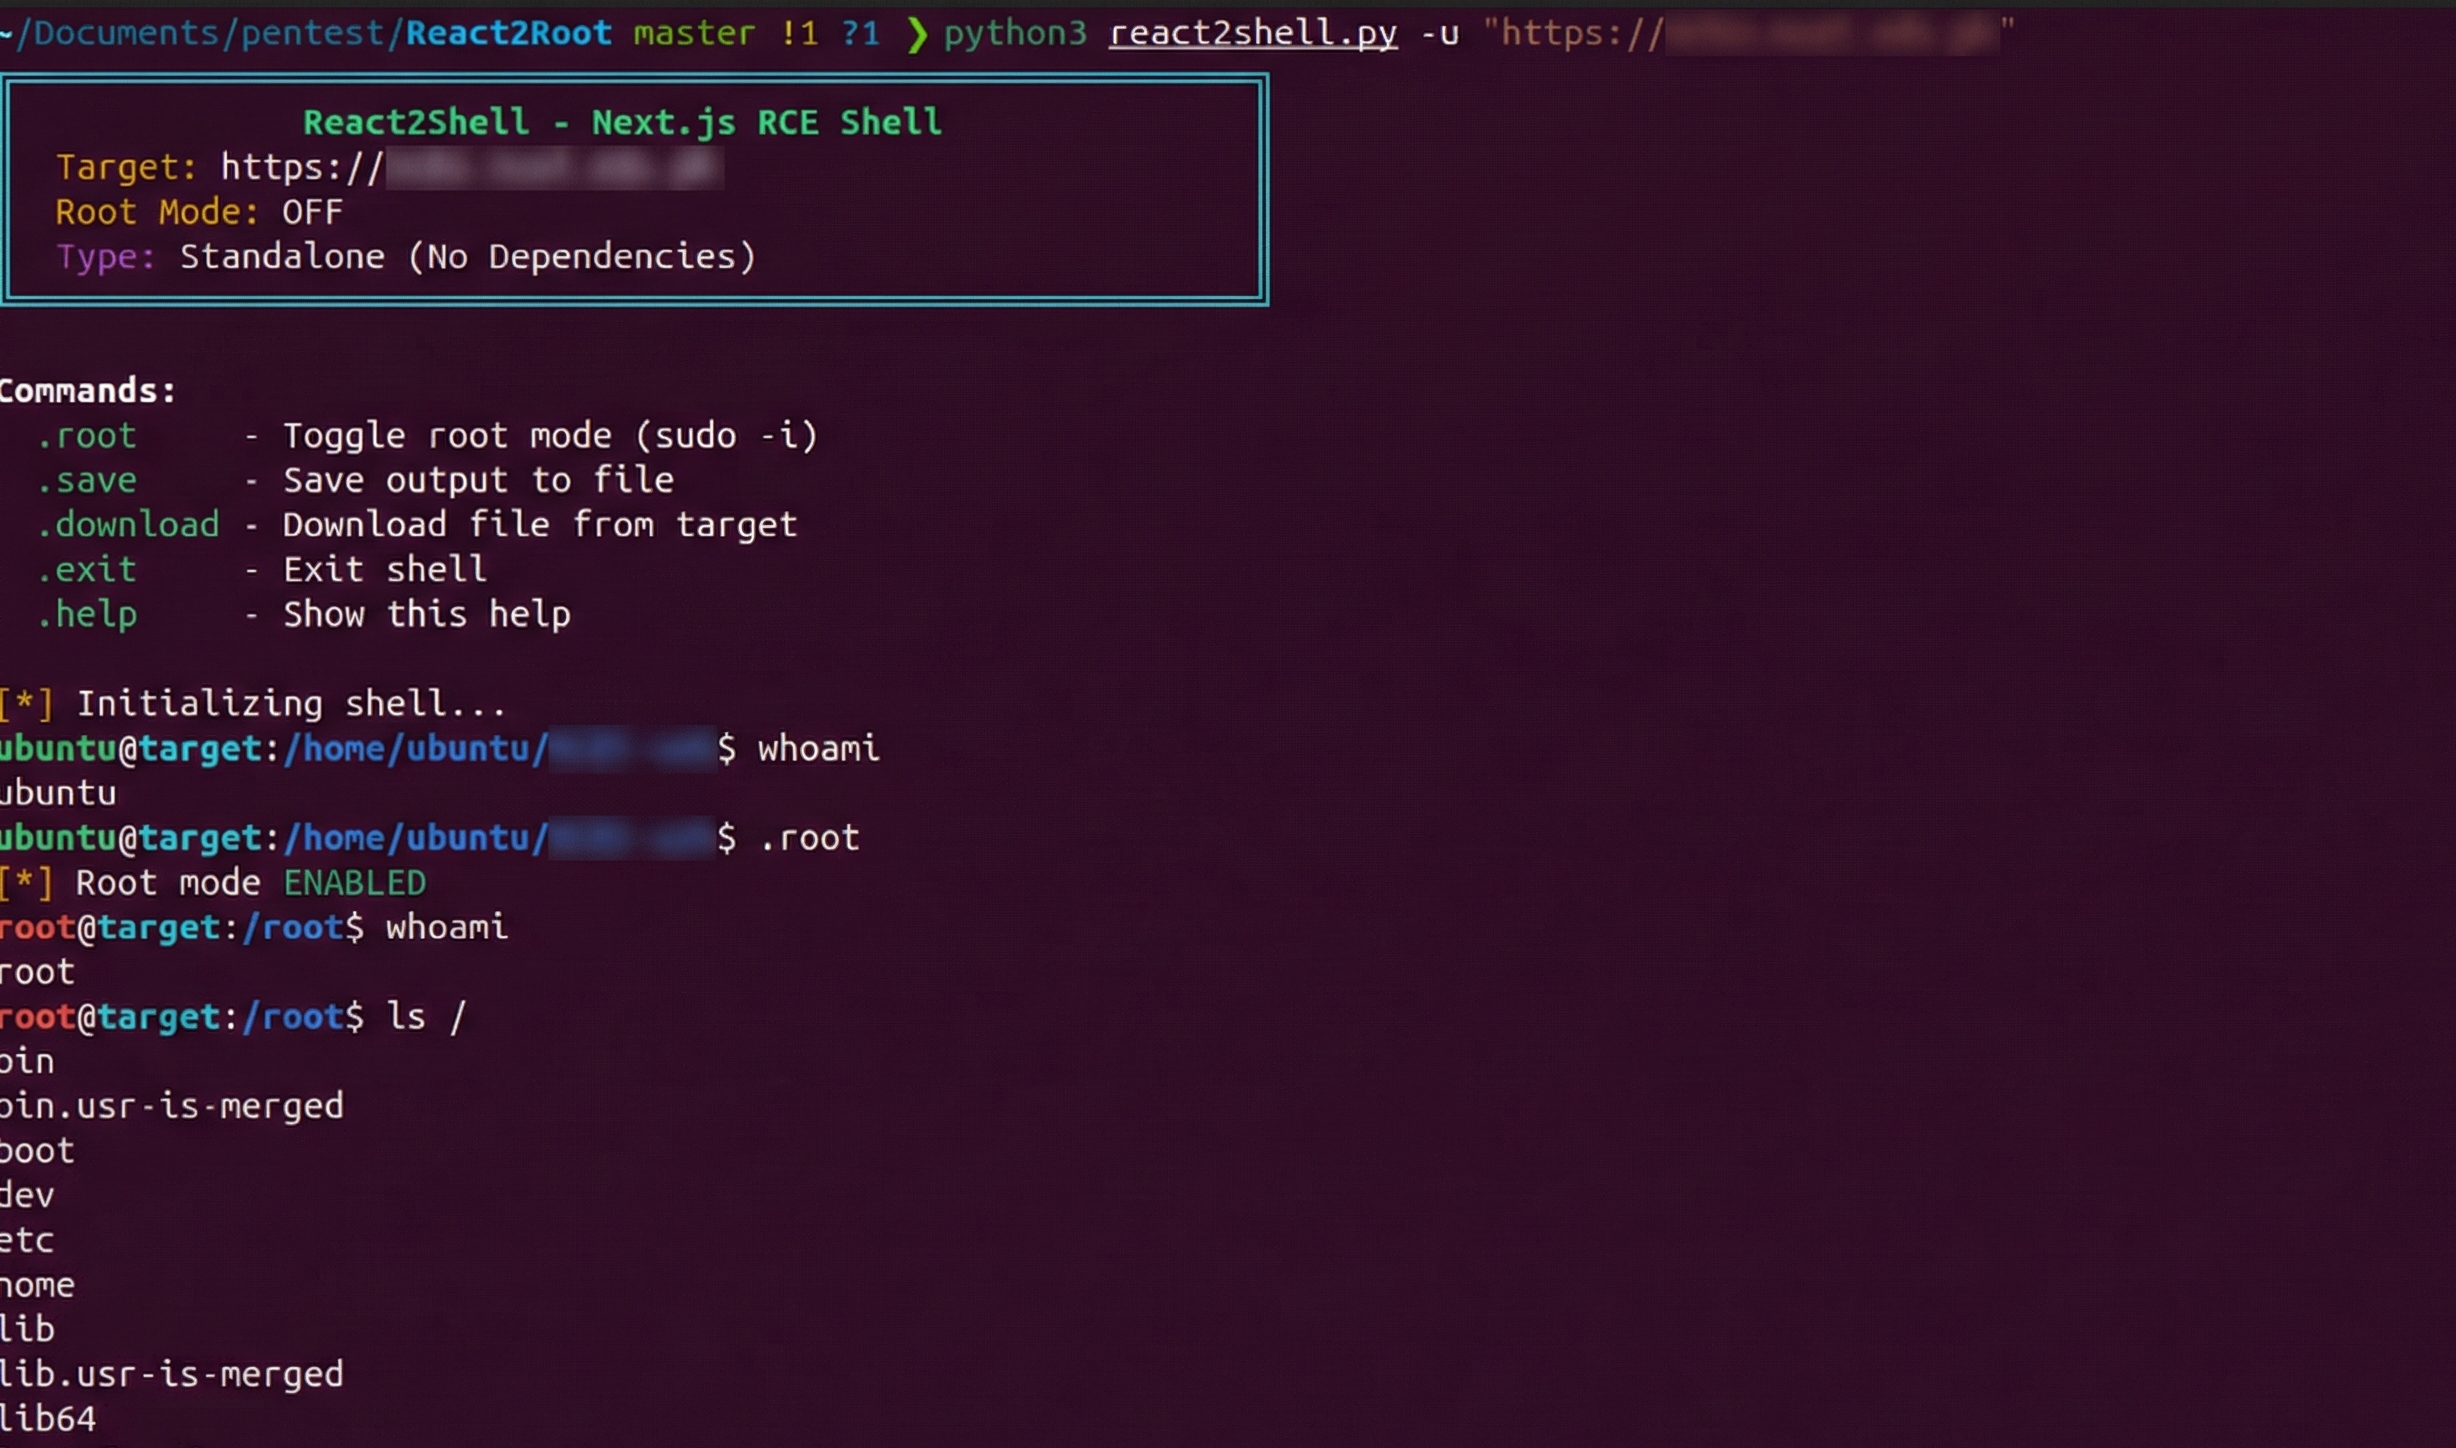 xalgord/react2shell
Advanced Exploitation Toolkit for Next.js Server Actions (CVE-2025-55182)
 casp3r0x0/cve-2026-34159
0 Click RCE exploit for CVE-2026-34159 Lama.cpp RPC server
 kljunowsky/cve-2024-27348
Proof-of-concept exploit for unauthenticated remote code execution in Apache HugeGraph Server via Groovy injection. Supports single and multi-target…