CVE-2025-55182-shellinteractive

Interactive shell for exploiting CVE-2025-55182 in React Server Components, enabling remote command execution, file transfer, and vulnerability…

Interactive shell for exploiting CVE-2025-55182 in React Server Components, enabling remote command execution, file transfer, and vulnerability…

PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…

Proof-of-concept exploit for CVE-2026-102489 in Zammad: chains a WebSocket session leak into authenticated session hijacking and unauthenticated…

Proof-of-concept and lab pack for CVE-2026-77991, a privileged PHP file-write RCE in Joomla Event Manager through 5.0.0, with Docker lab and witness…

Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…

Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.

Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…

Path Traversal -> RCE in Laranode < 1.2.1 (CWE-22). PoC + advisory writeup.

PoC script for CVE-2026-26026 GLPI versions 11.0.0 through 11.0.5

Proof-of-concept exploit for CVE-2026-78159, an unauthenticated RCE in The Events Calendar WordPress plugin via the parse_array widget classes sink.

Proof-of-concept exploit and lab reproduction pack for CVE-2026-18937, an unauthenticated RCE in the Broken Link Checker WordPress plugin before…

Python 3 PoC for CVE-2026-102427, an unauthenticated upload RCE in OrdaSoft Joomla CCK (com_os_cck) via task=getContent and site/uploader.php using a…

Reproduction and root cause analysis of CVE-2026-39987 Marimo pre-auth WebSocket RCE in a local Docker lab.

Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…

CraftCMS has an RCE vulnerability via relational conditionals in the control panel

Craft CMS RCE via relational conditionals in the control panel

Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.

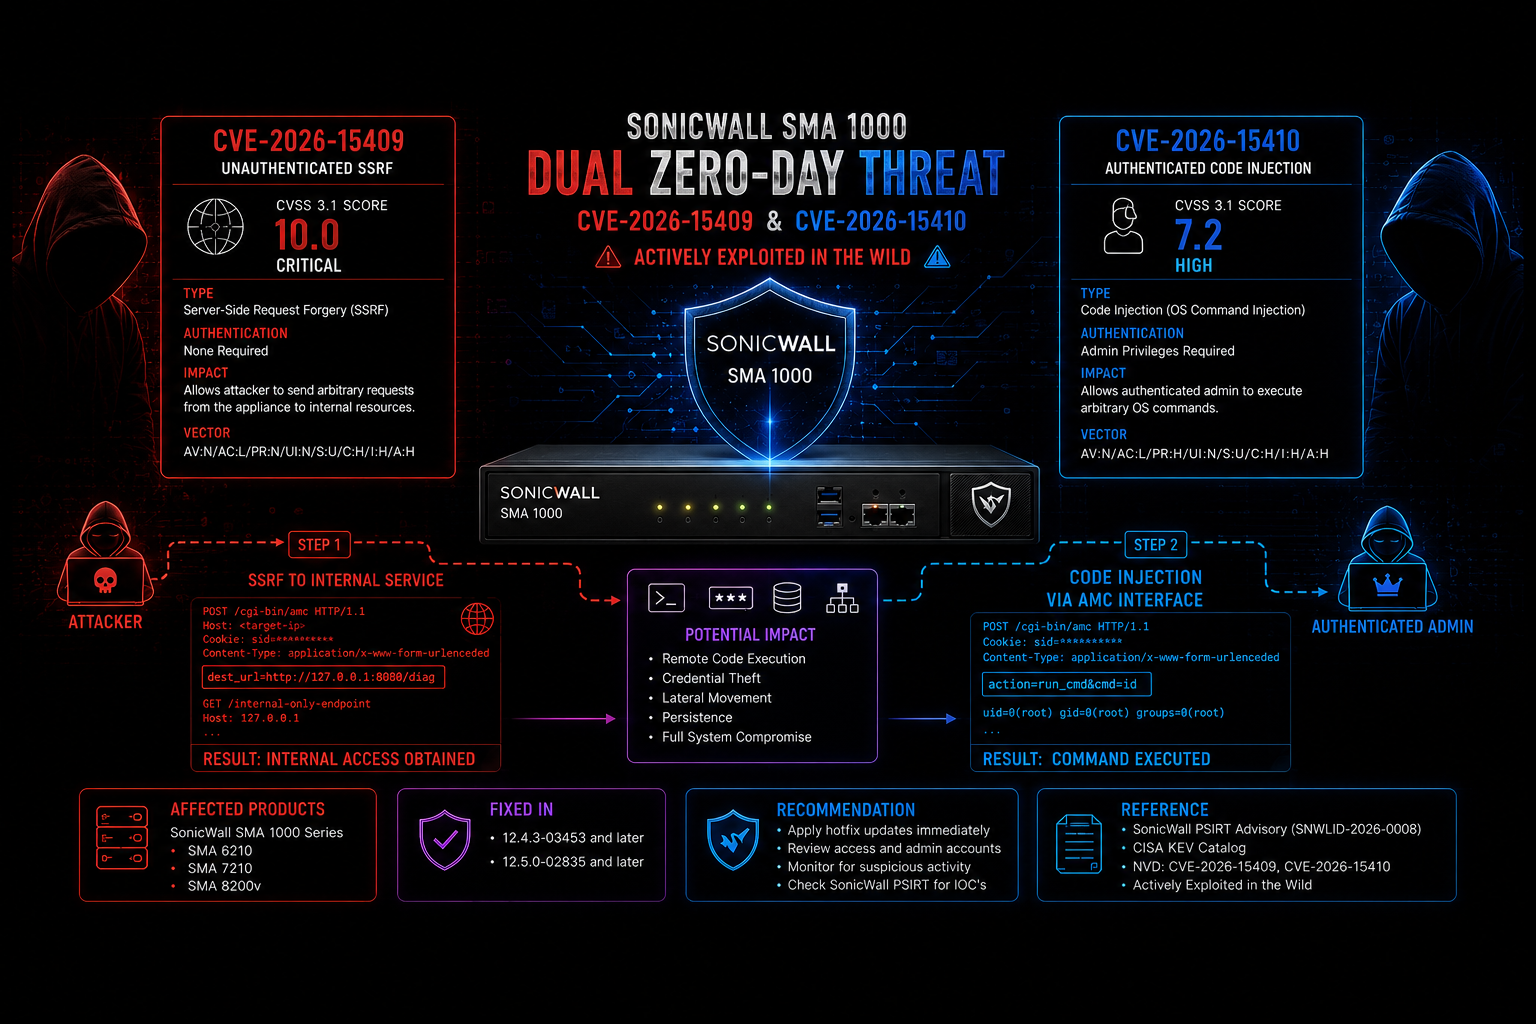
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…