
sshuttle
 sshuttle/sshuttle
Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
command-and-controldata-exfiltrationdns-analysis+6
13.6k
sshuttle/sshuttleTransparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
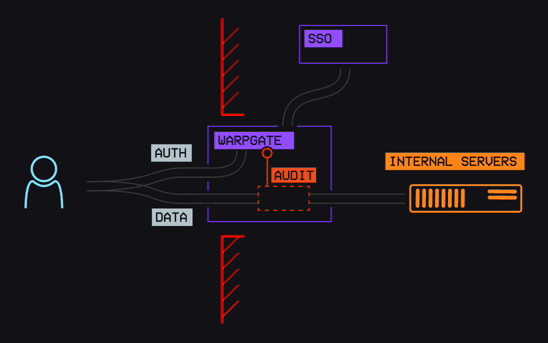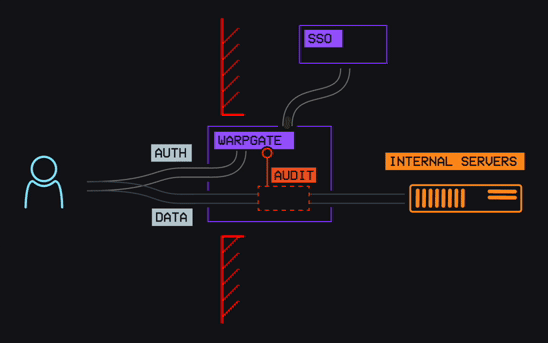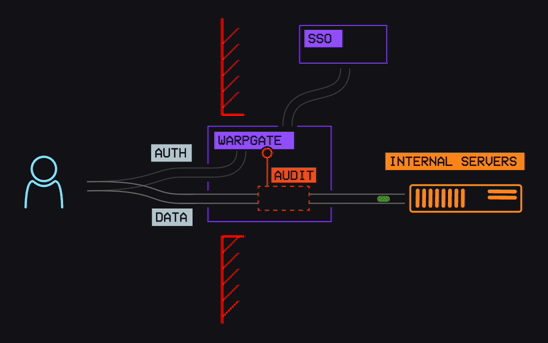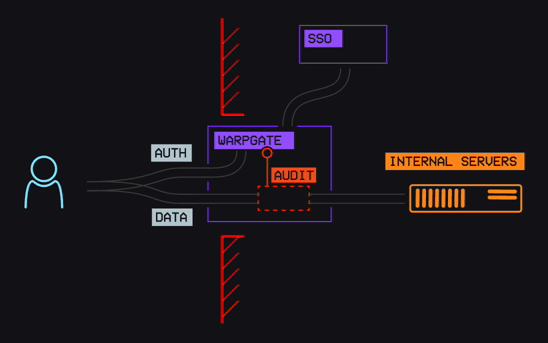 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
 openssh/openssh-portable
Portable OpenSSH
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 borntoberoot/networkmanager
A powerful open-source tool for managing networks and troubleshooting network problems!
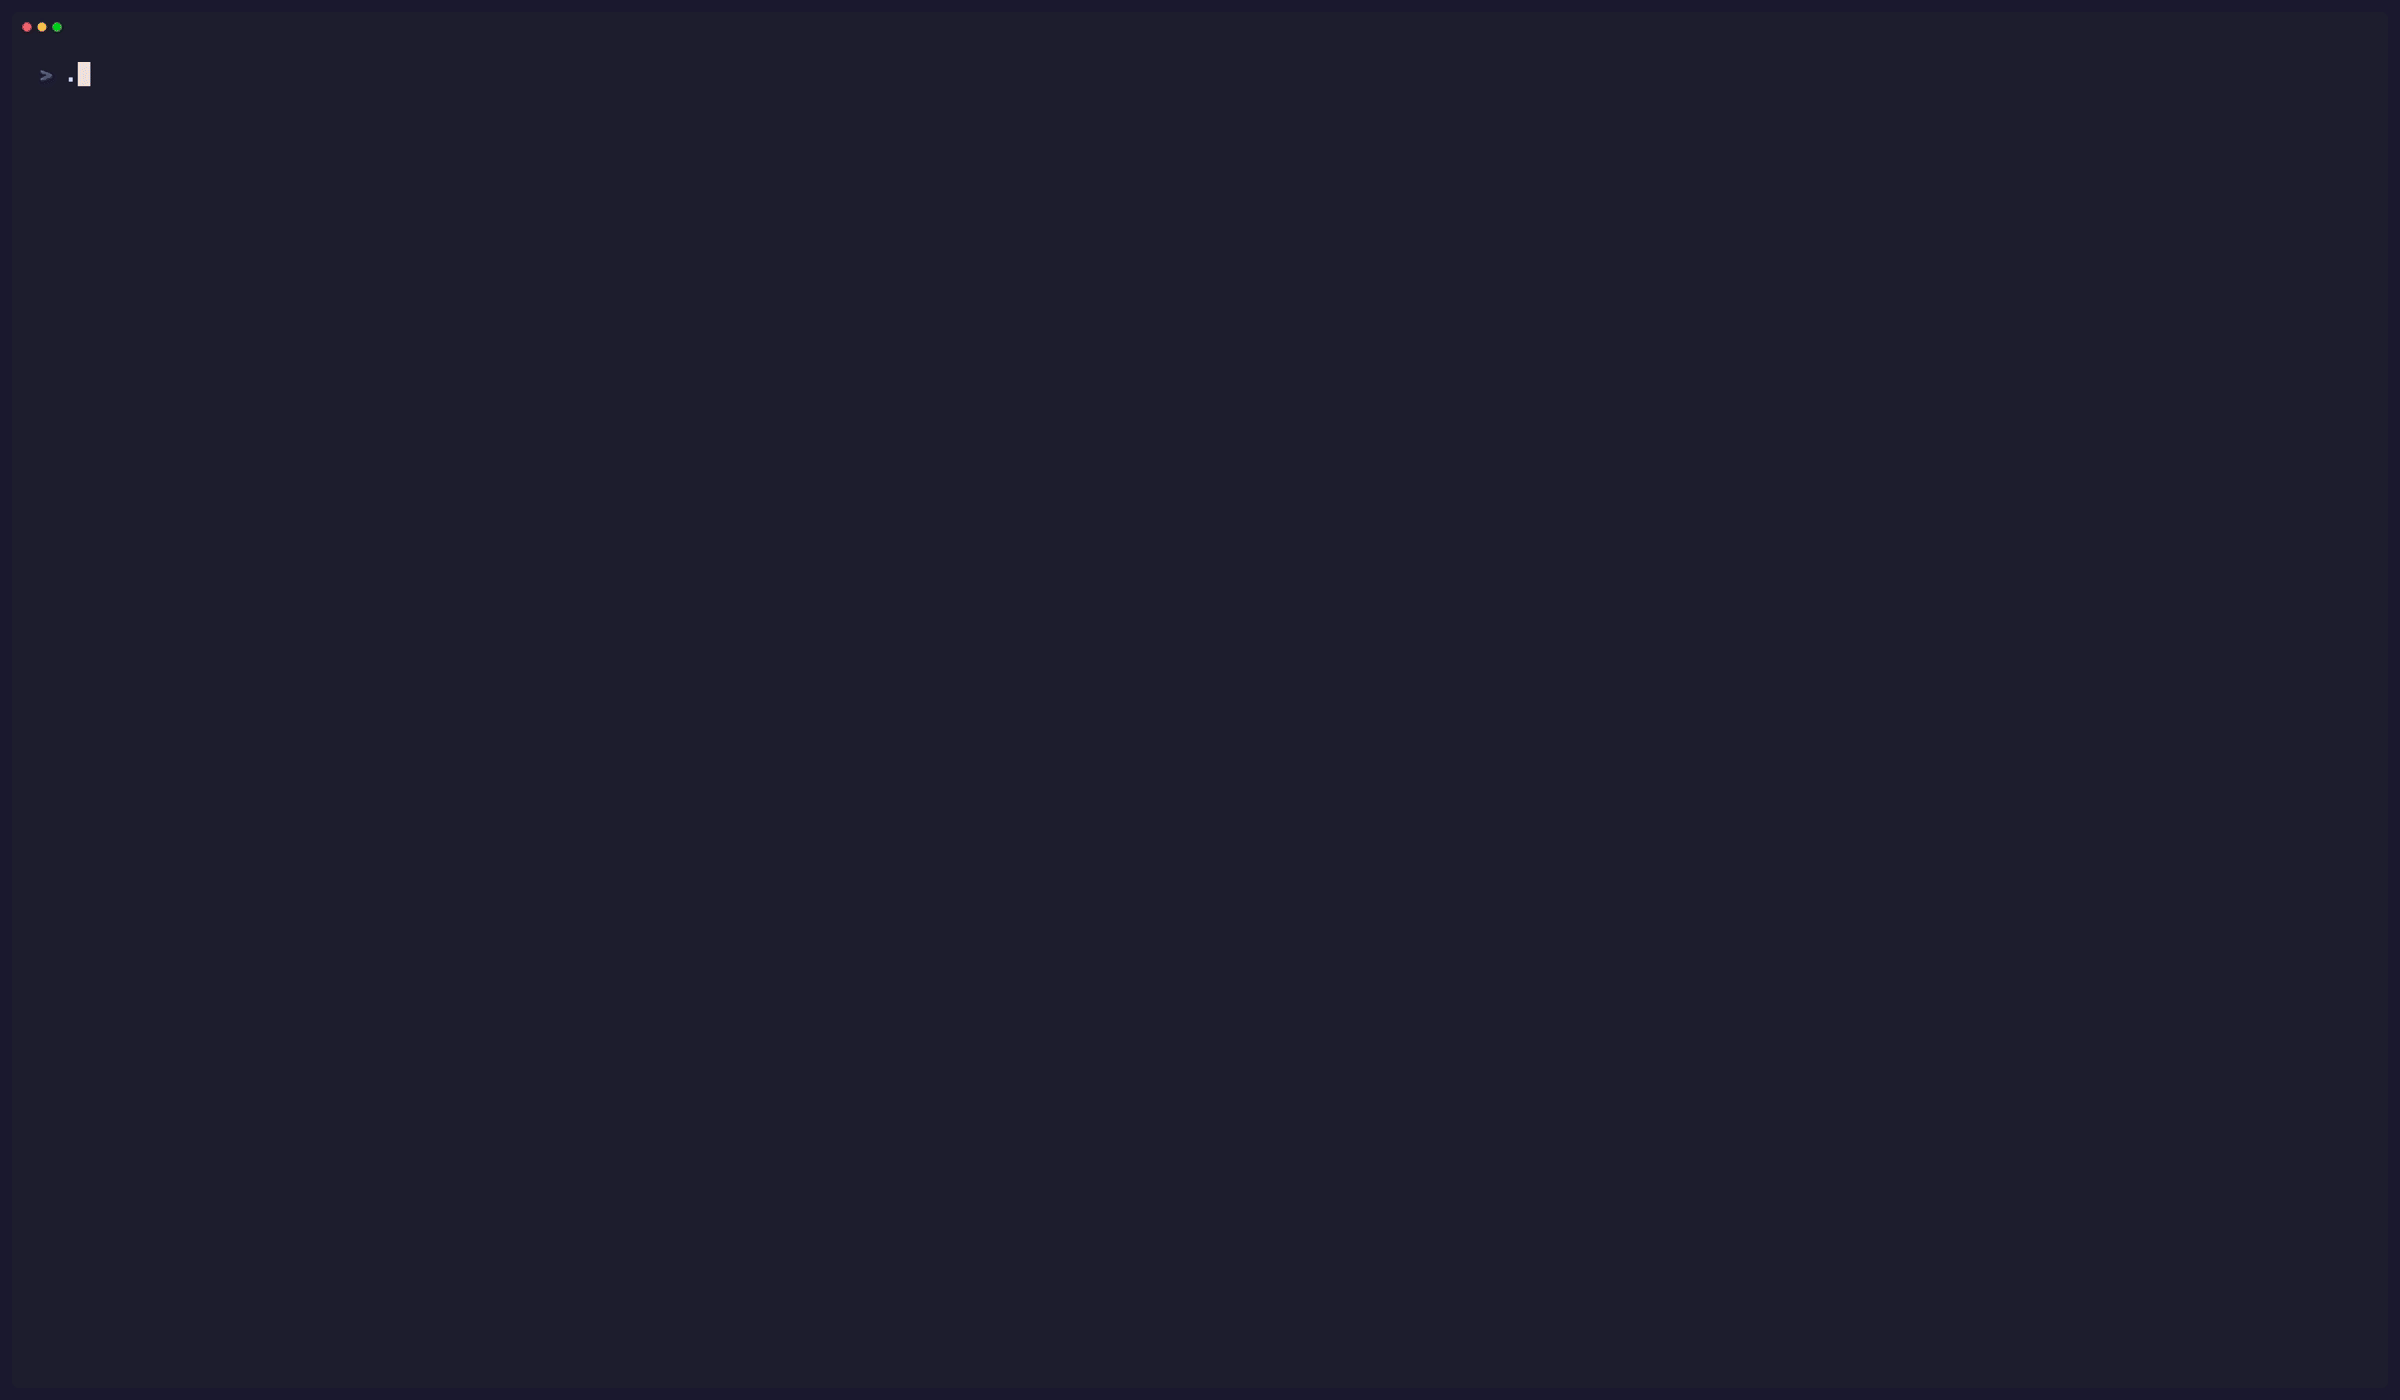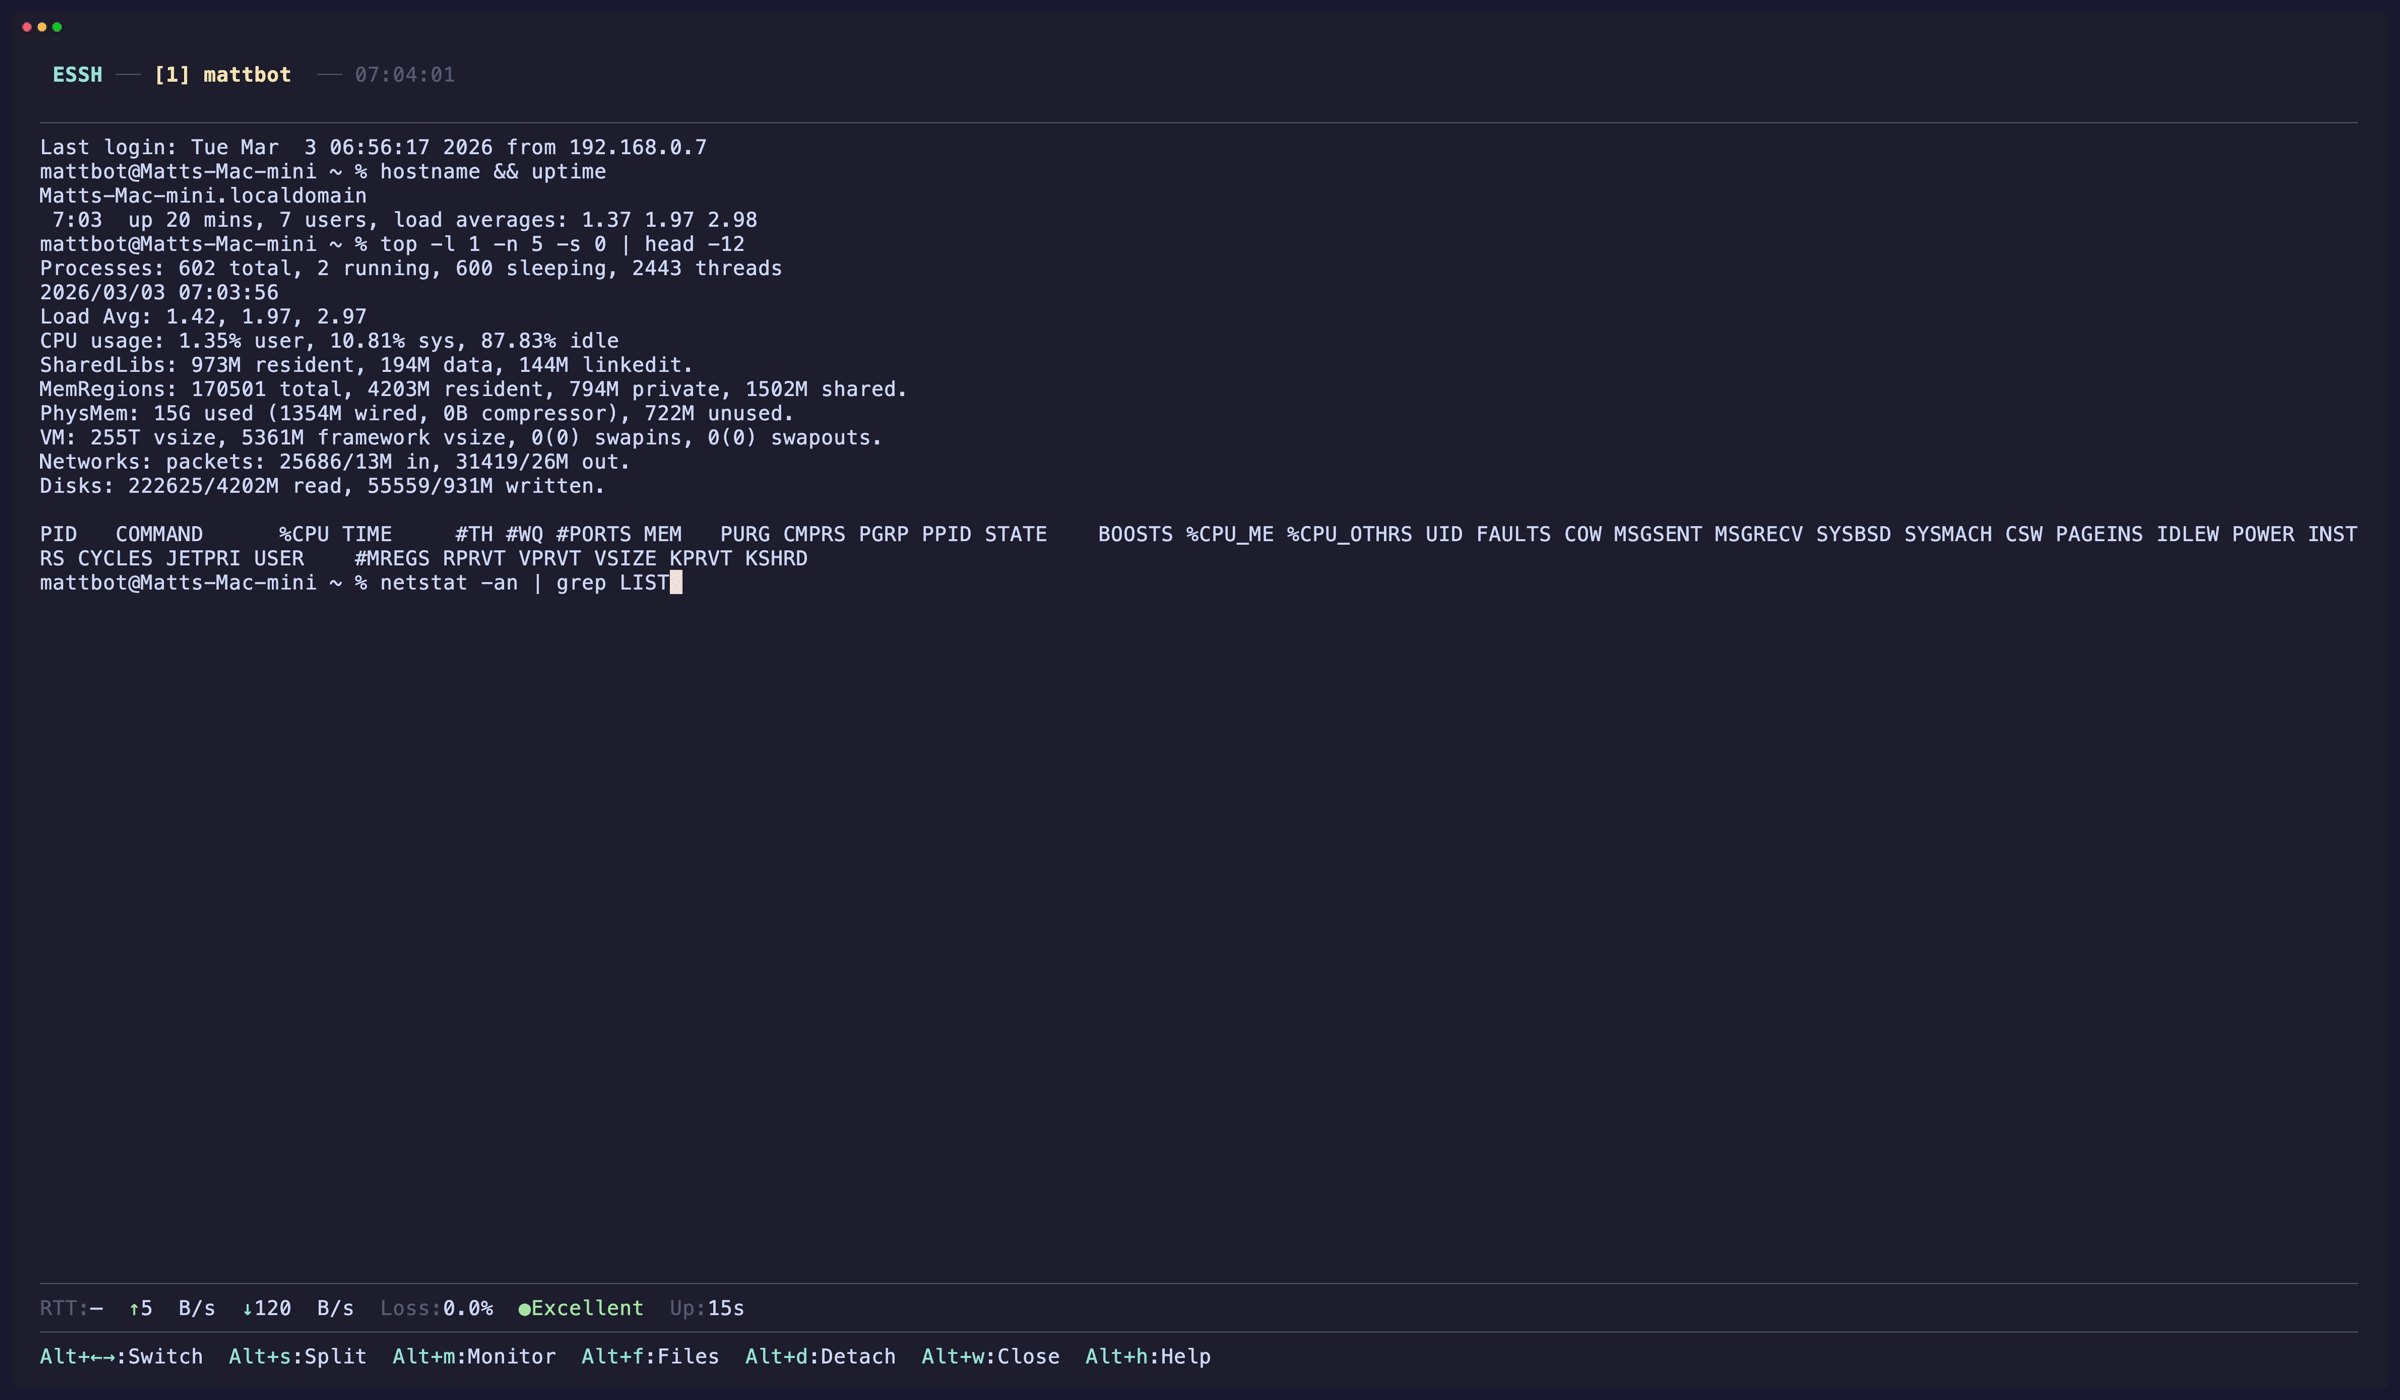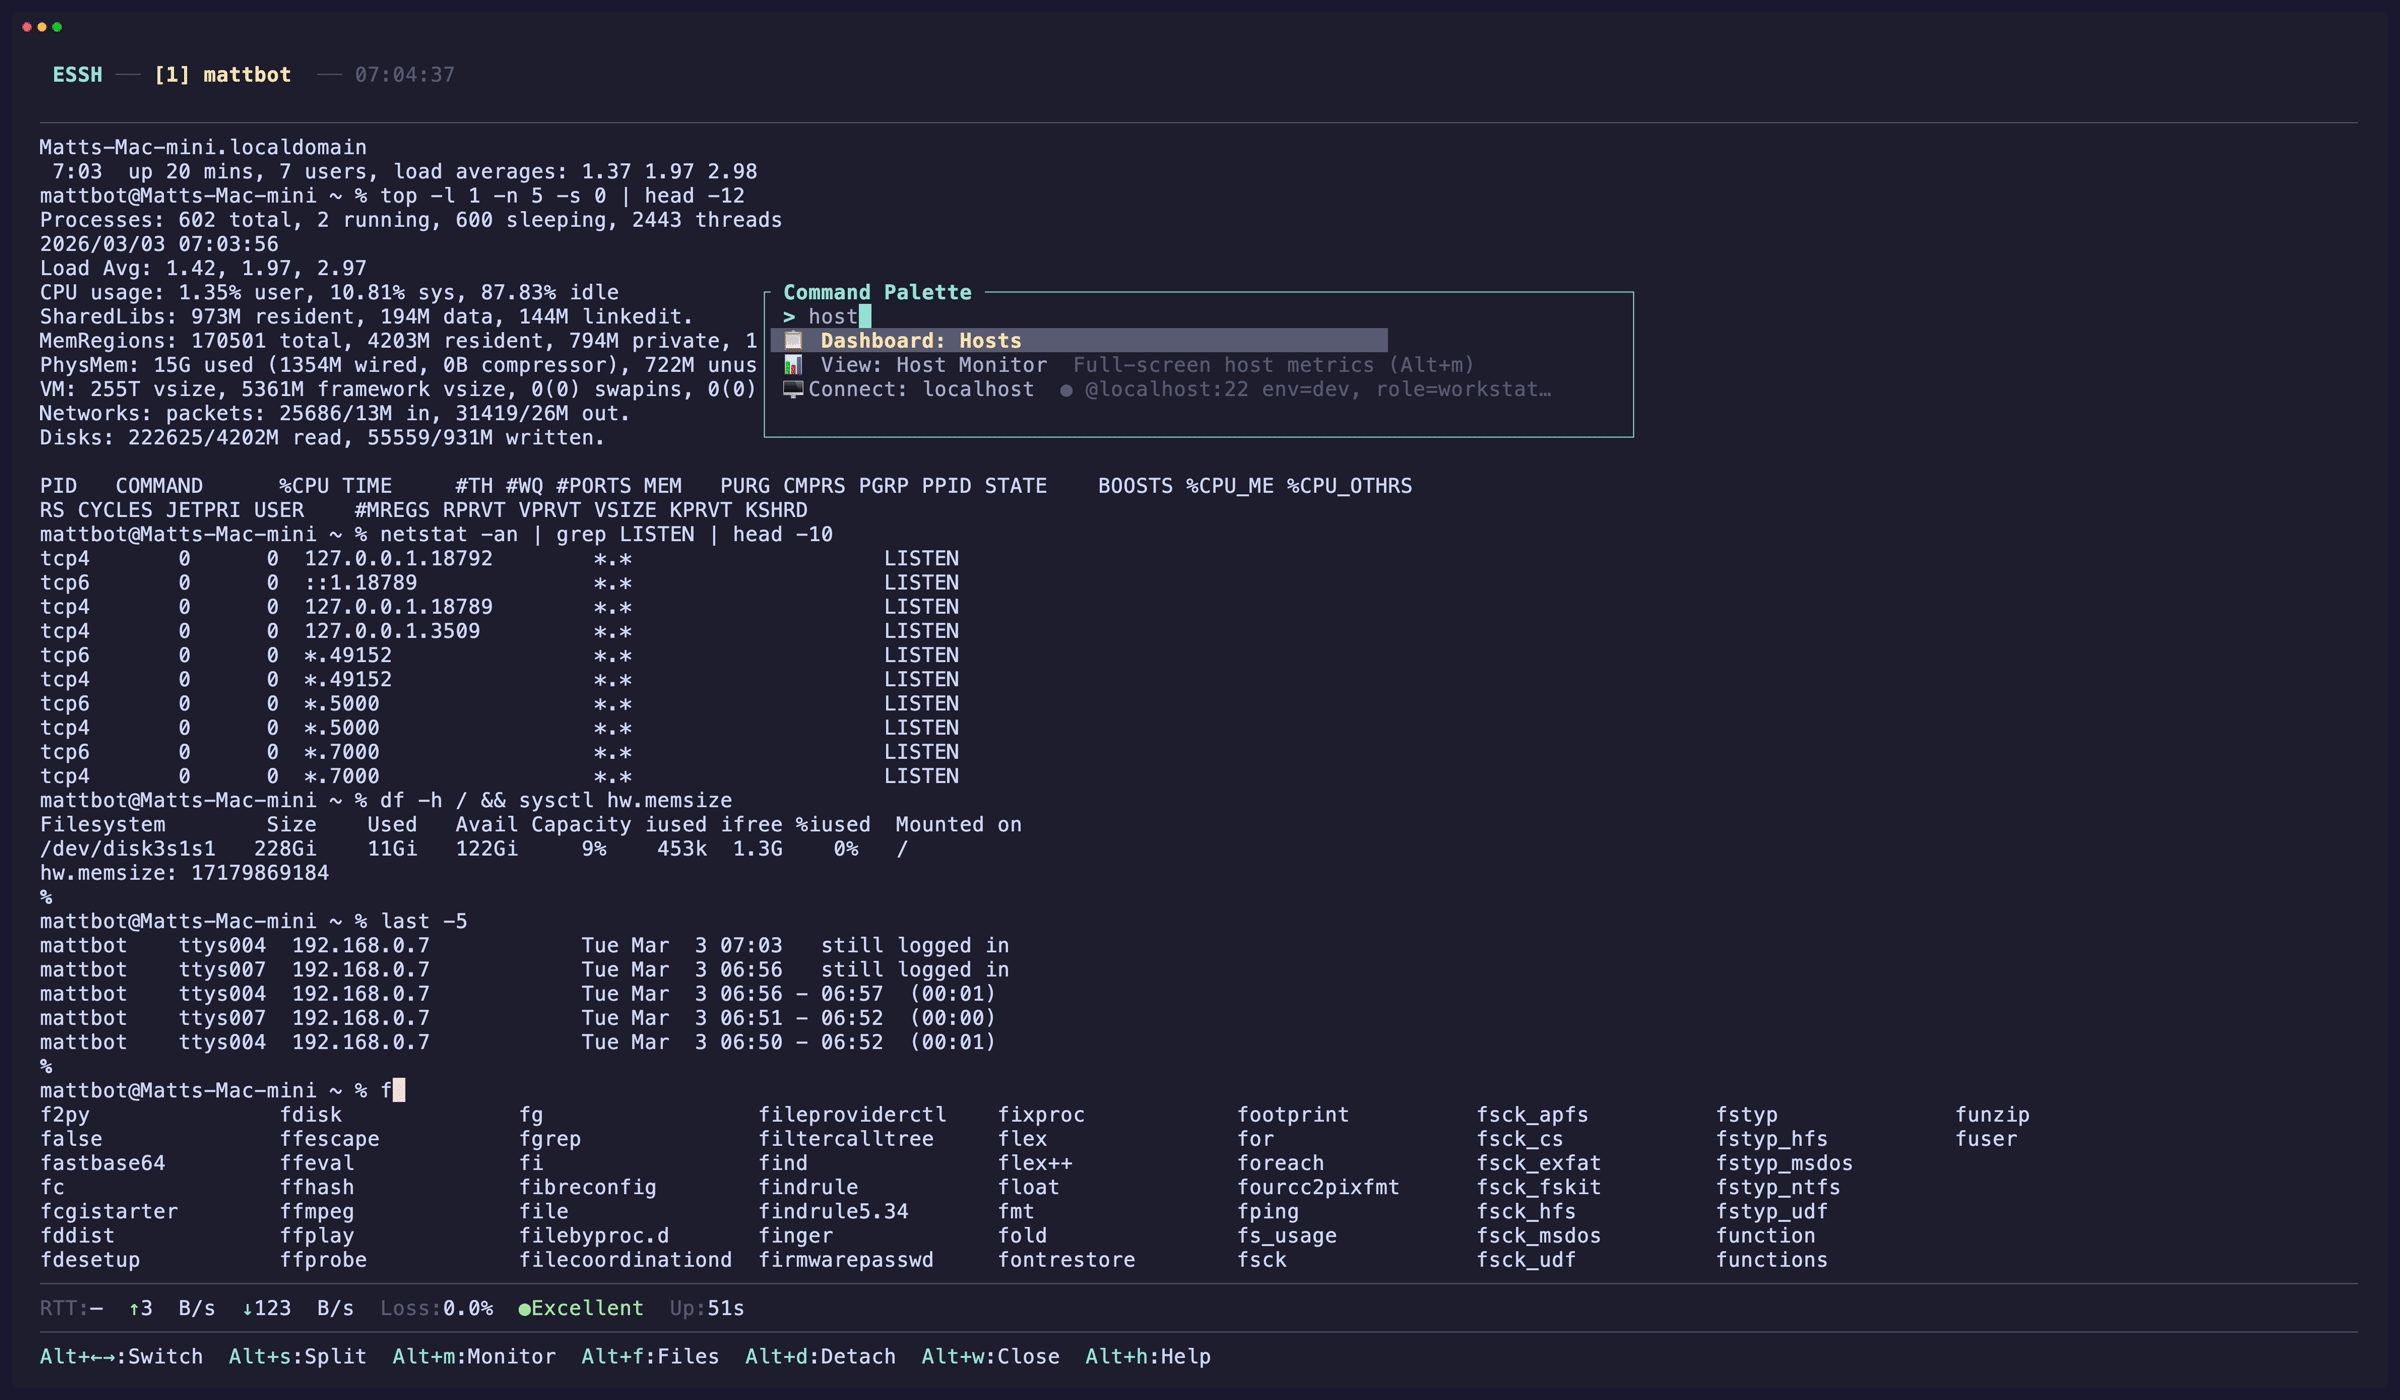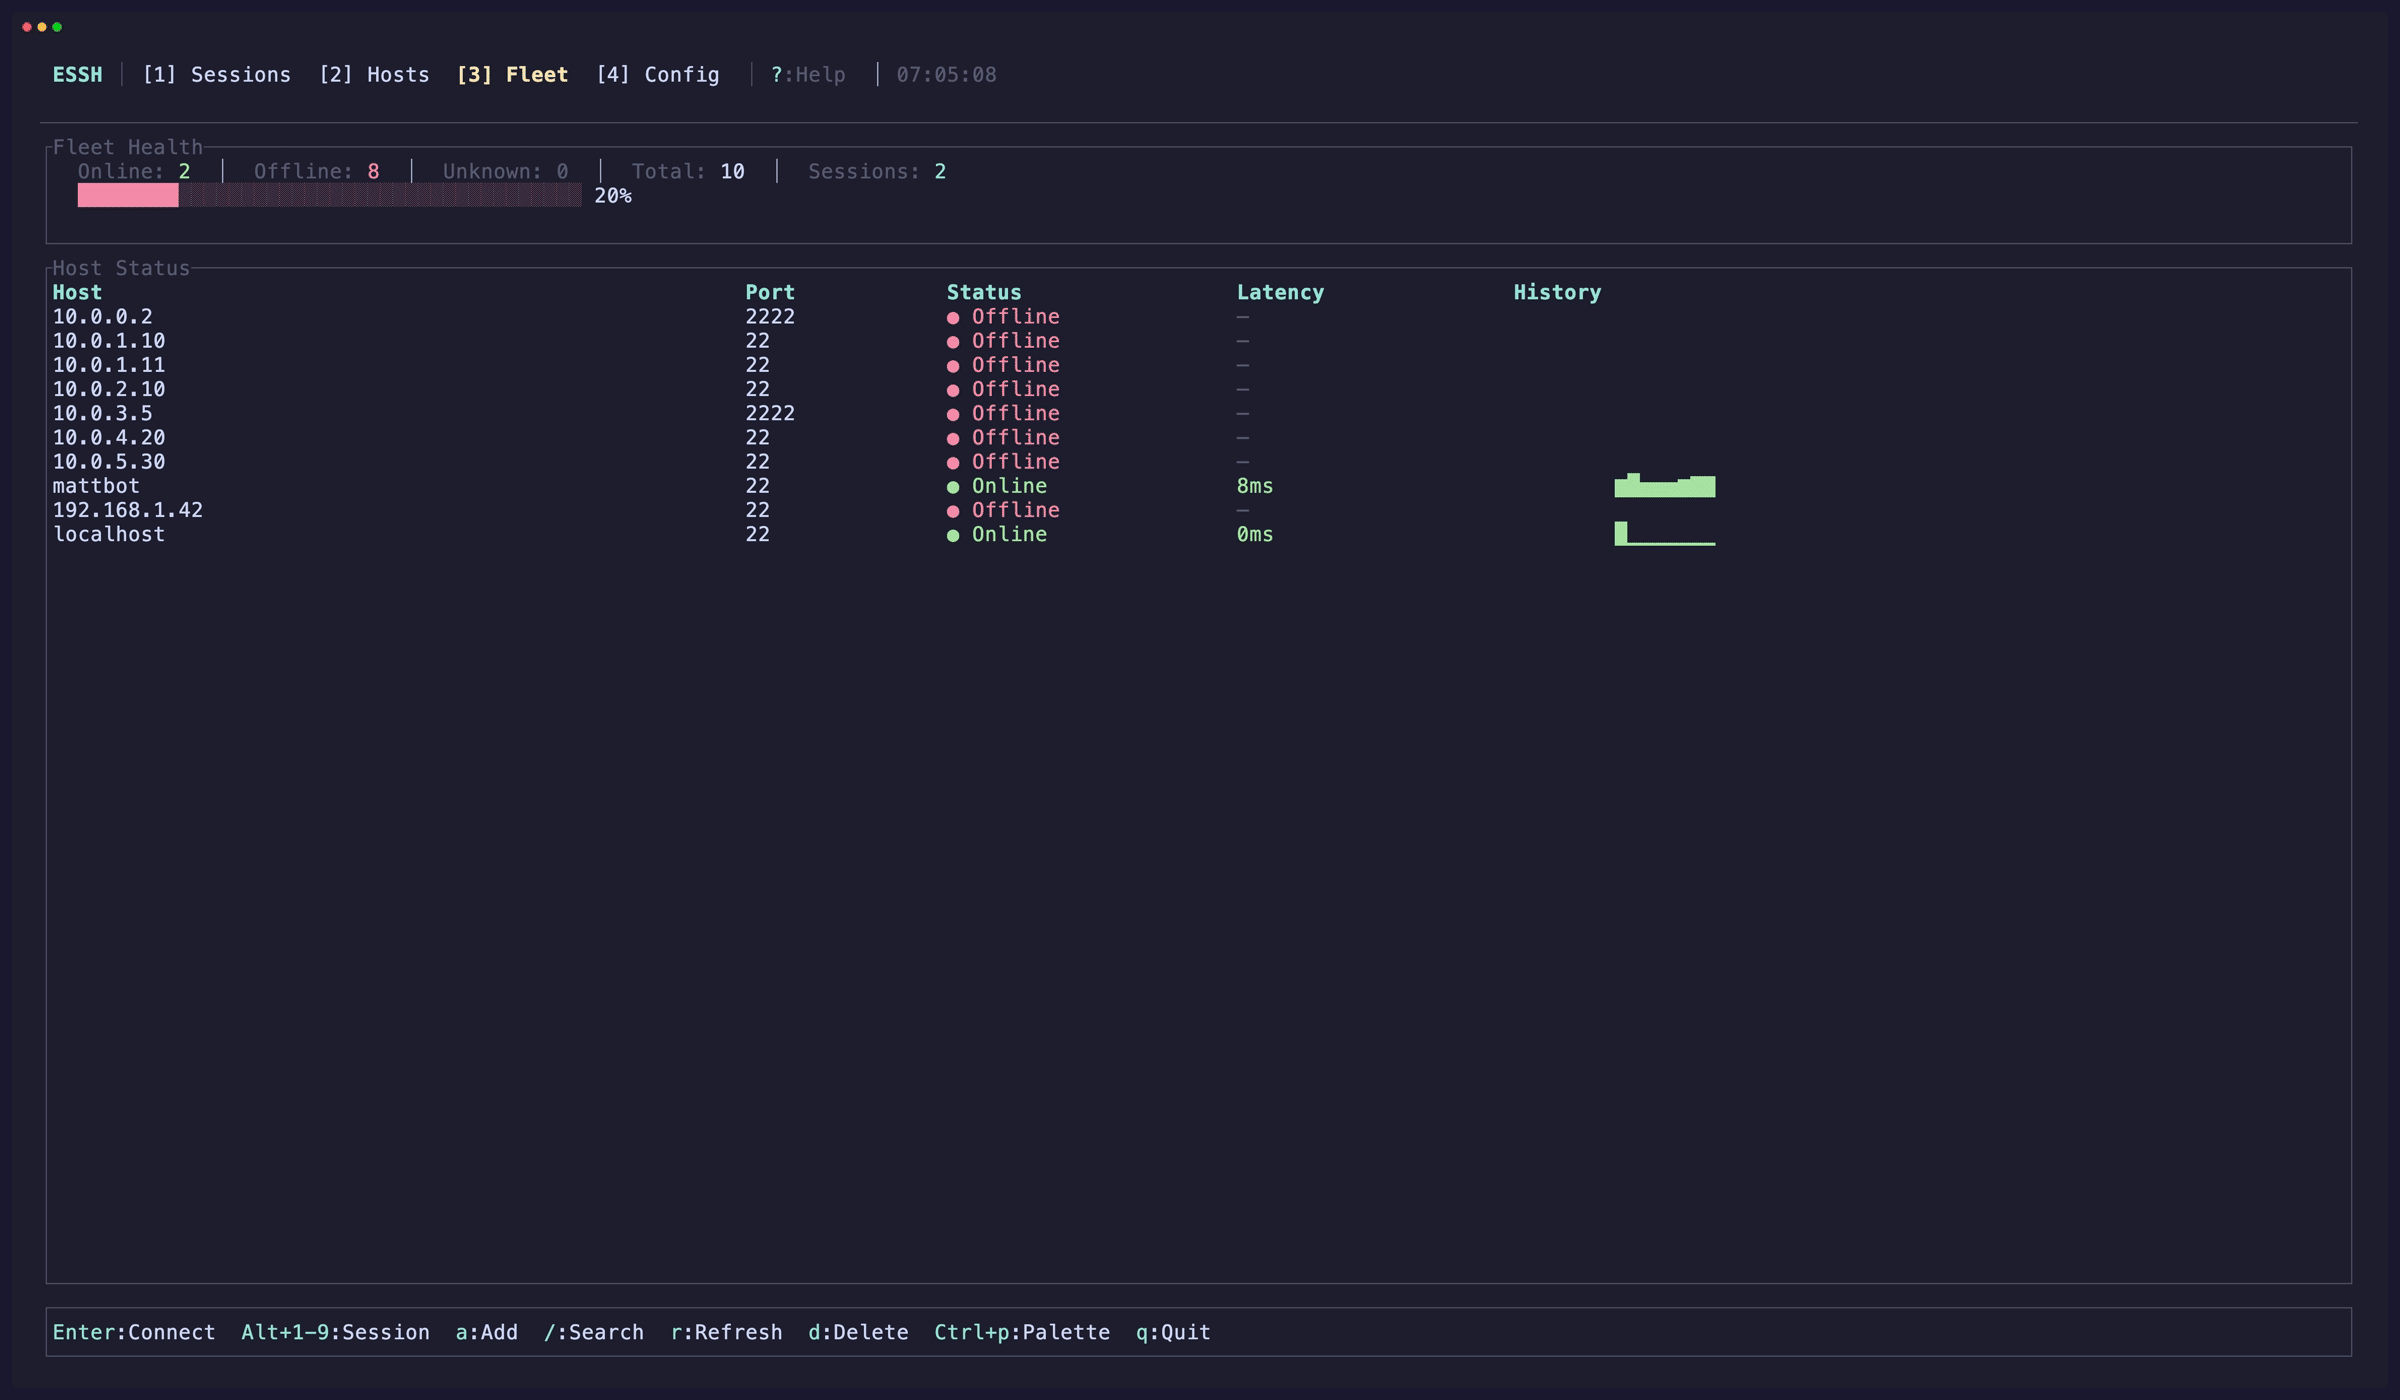 matthart1983/essh
Enhanced SSH client with TUI — manage connections, keys, and sessions
 bastillion-io/bastillion
Bastillion gives you a clean, browser-based way to manage SSH access across all your systems—like a bastion host with a friendly dashboard.
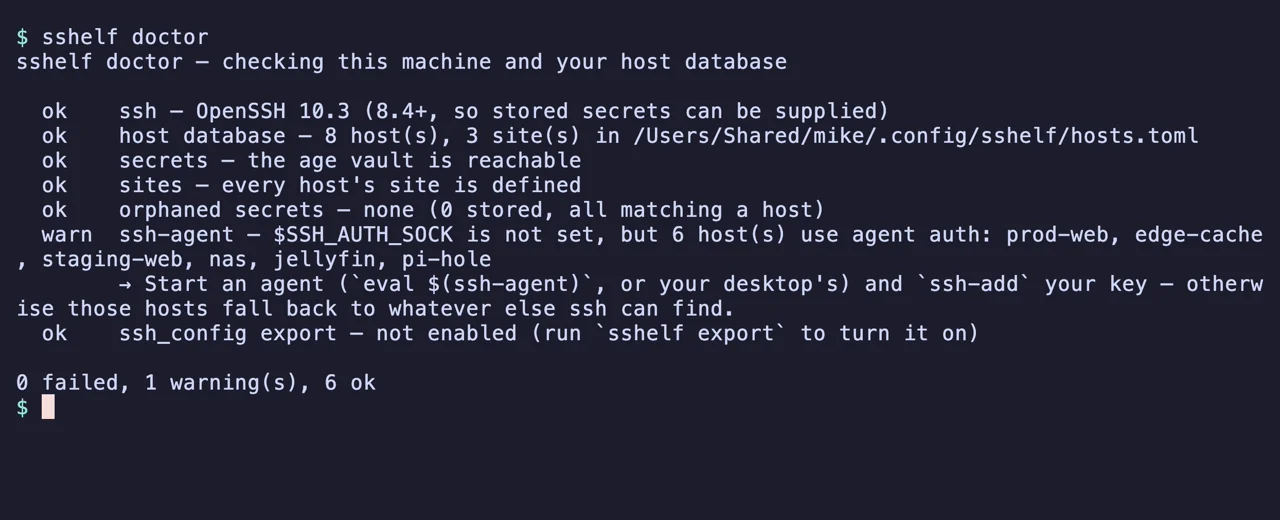 max-rh/sshelf
Fast terminal UI for your SSH hosts: fuzzy-search and connect in two keystrokes, dual-pane SFTP file transfer, and background port forwarding. Keeps…
 apple/swift-nio-ssh
SwiftNIO SSH is a programmatic implementation of SSH using SwiftNIO
 mwiede/jsch
fork of the popular jsch library
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
 jayanaxhf/filessh
A fast and convenient TUI file browser for remote servers
 razureink/cve-2025-32433-erlang_ssh_rce_reproduction
Reproduction of cve-2025-32433-erlang_ssh_rce_reproduction
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 aiyakami/cve-2021-21974
自研针对ESXI 堆栈溢出的CVE-2021-21974 POC,只支持项目给出的的目标和环境,用于学习和研究
 chuzoux/cve-2025-32433-exploit-edited
Based on the original version:https://github.com/vulhub/vulhub/blob/master/erlang/CVE-2025-32433/exploit.py Replace Unicode checkmark with ASCII…