

sliver-gui
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
command-and-controlexploitationlateral-movement+6
224
mr-in4inci3le/sliver-guiA desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
 jackalkarlos/evilahenk
CVE-2026-6508 LiderAhenk Merkezi Yönetim Sistemi mimarisinde, uç birimler (agents) arası tüm istemcilerin birbirleri üzerinde 'root' yetkisiyle kod…
 tomadimitrie/cve-2026-54424
Exploiting Parsec for Windows to gain SYSTEM privileges
 synacktiv/dcomillusionist
DCOM in memory and fileless lateral movement techniques through .Net deserilization
 jacobtaylor3/cve-2021-21220
Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.
 diegovargasj/cve-2025-65753
Proof-of-concept exploit for CVE-2025-65753: remote code execution on Gryphon Guardian access point via improper TLS certificate validation, enabling…
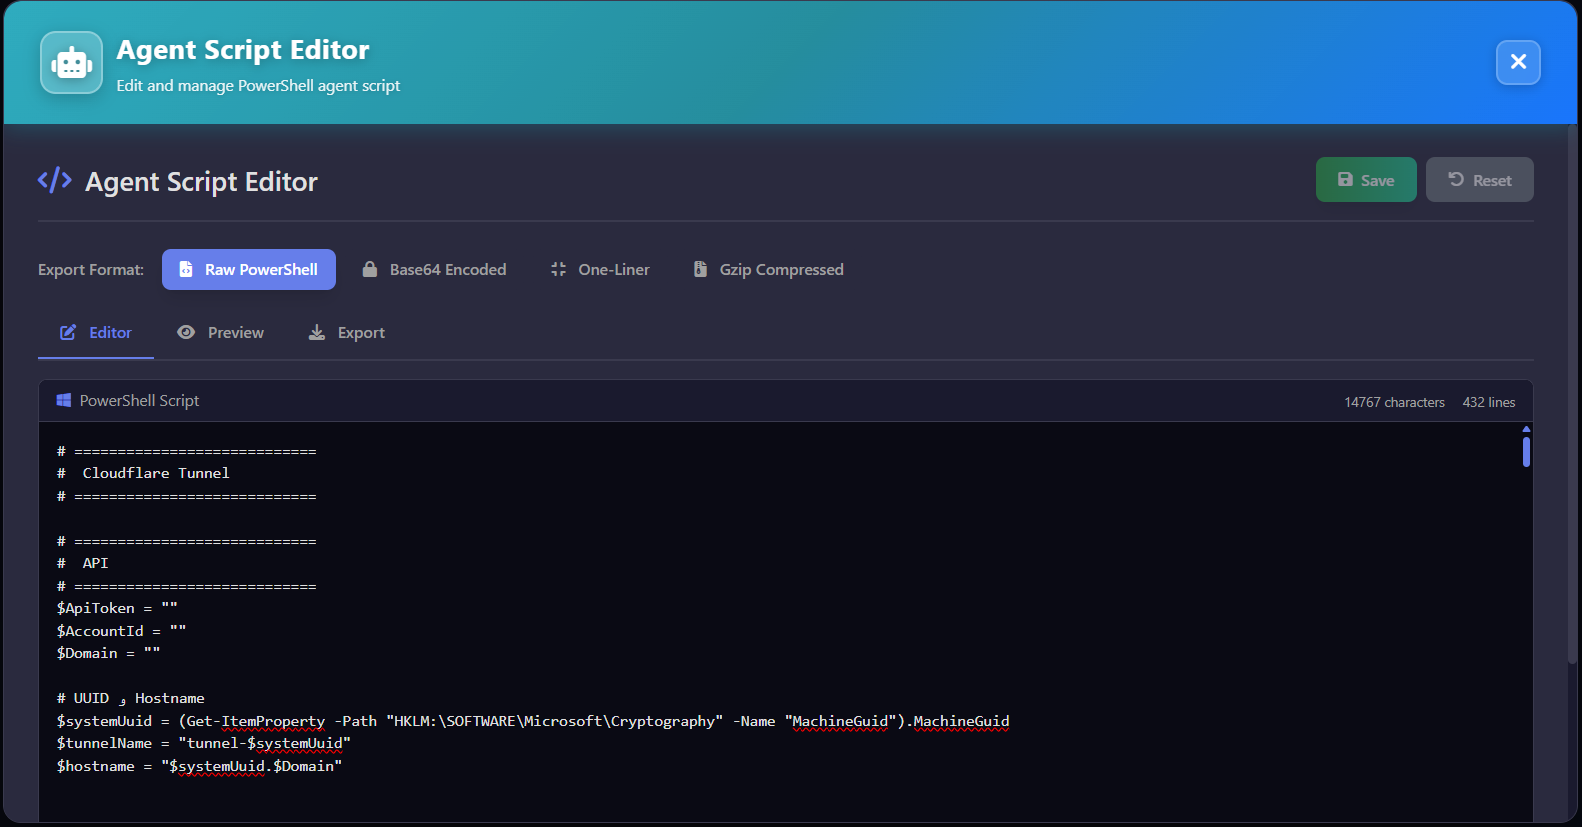 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
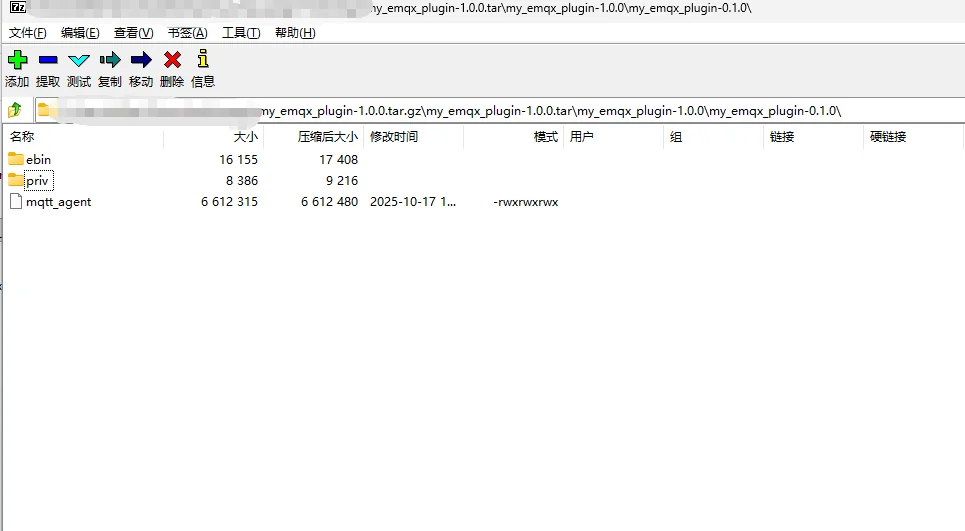 f1r3k0/cve-2025-52136
Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 vin01/poc-proxycommand-vulnerable
Proof of conept to exploit vulnerable proxycommand configurations on ssh clients (CVE-2023-51385)
 mr-un1k0d3r/scshell
Fileless lateral movement tool that relies on ChangeServiceConfigA to run command
 gar-re/cve-2022-24644
Proof-of-concept exploit for CVE-2022-24644, demonstrating unauthenticated remote code execution via DNS spoofing against KeyMouse Windows 3.08…
 gar-re/cve-2022-28944
Proof-of-concept exploit for unauthenticated remote code execution in EMCO Software products via DNS spoofing and malicious update injection.
 auduongxuan/cve-2022-26809
Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.
 alvinsmith-eroad/cve-2018-9276
CVE-2018-9276 PRTG < 18.2.39 Reverse Shell (Python3 support)
 3t4n/samba-3.0.24-cve-2007-2447-vunerable-
Vulnerable Samba 3.0.24 environment for reproducing CVE-2007-2447 command execution, intended for exploit testing and security research.