

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
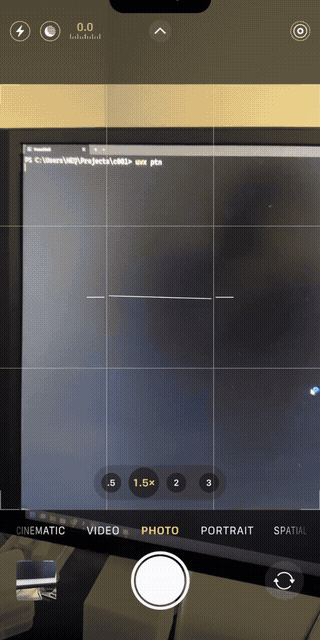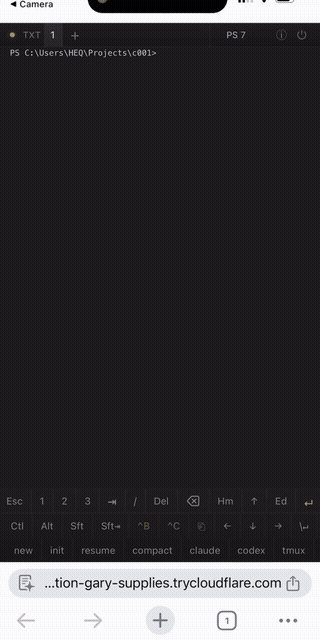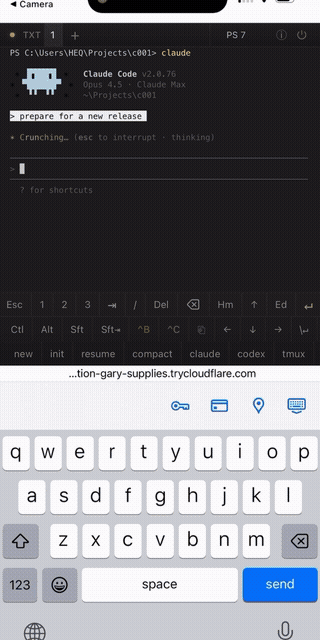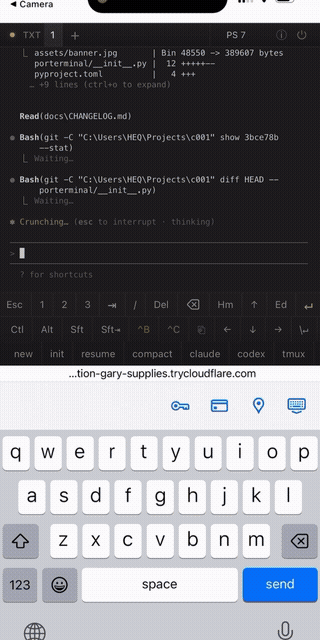 lyehe/porterminal
Quick n' dirty web/mcp terminal tunneling your phone & pc
 gabrielunknown/cve-2026-73570
Zimbra SNMP Notification OS Command Injection — Unauthenticated RCE via SMTP exploit (Poc)
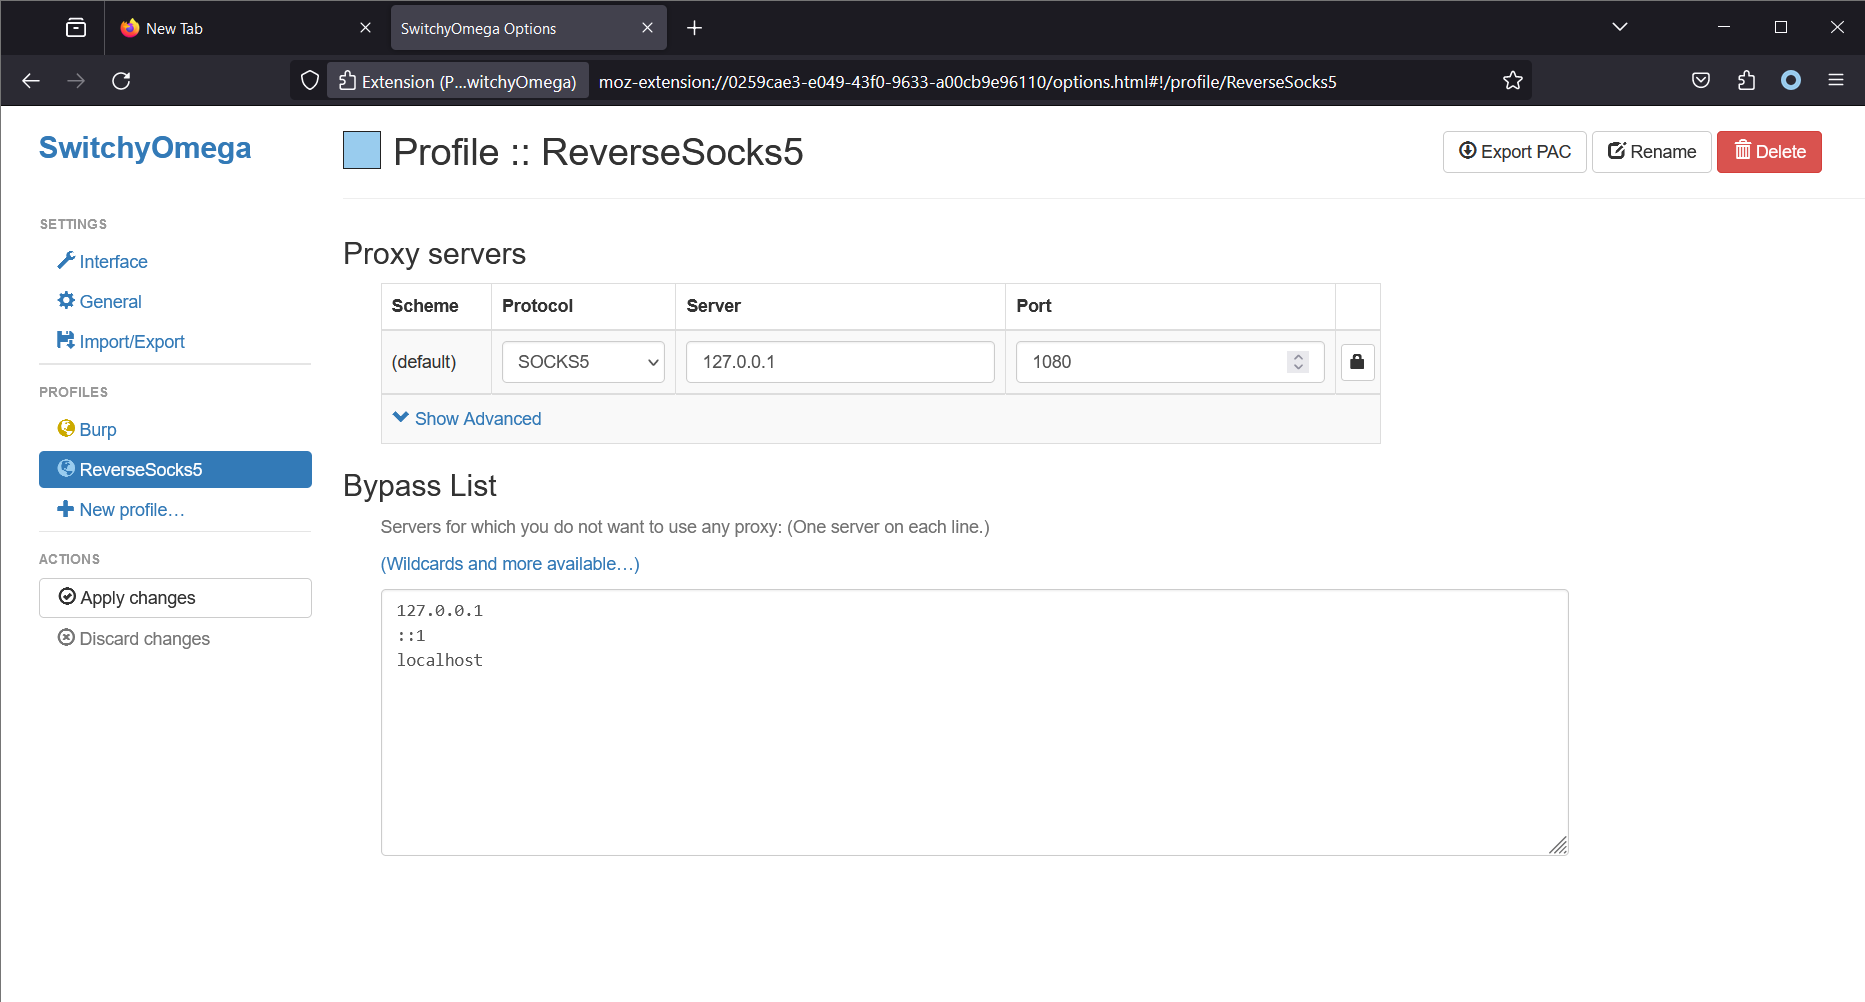 acebond/reversesocks5
Single executable reverse SOCKS5 proxy written in Golang.
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 0xcyp1337/cve-2026-44402
Exploit for CVE-2026-44402 targeting Voltronic Power SNMP Web Pro 1.1, enabling unauthenticated remote code execution via malicious firmware upload.…
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 nirvanasec/cve-2026-34197-poc
Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via Jolokia's addNetworkConnector, with technical notes and reverse shell…
 cyberalp0/smartermail-cve-2026-24423
Exploit for CVE-2026-24423 — a critical unauthenticated RCE in SmarterMail's ConnectToHub API. Affects all builds prior to 9511.
 ahseven/cve-2026-33017-poc-reverse-shell
Exploit for CVE-2026-33017, an unauthenticated RCE in Langflow, enabling reverse shell via malicious CustomComponent payload.
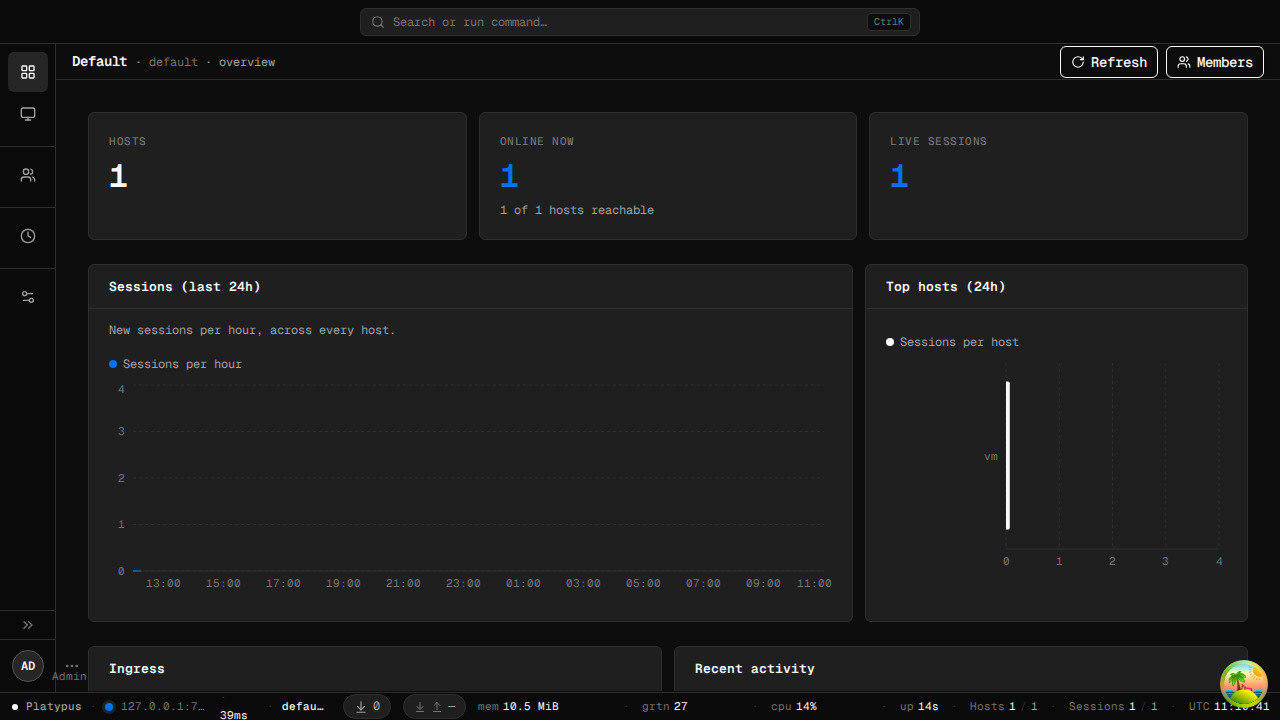 wangyihang/platypus
:hammer: A modern, cross-platform machine manager
 lincolino/lab-annie
Automates exploitation of CVE-2020-13160, a critical remote code execution vulnerability in AnyDesk 5.5.2, enabling penetration testers to validate…
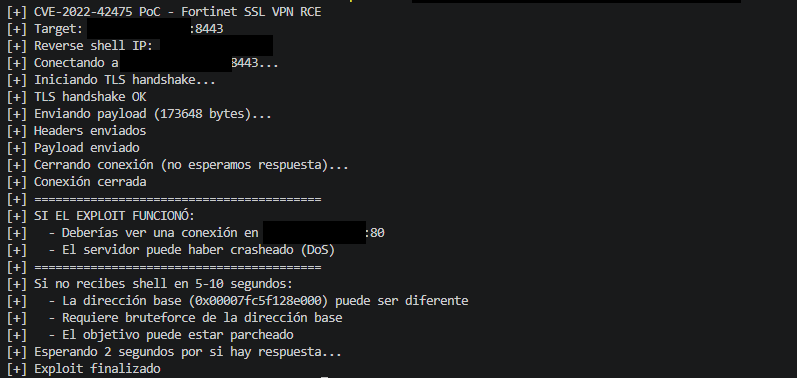 ull0a/cve-2022-42475-poc
Proof of Concept (PoC) for research and controlled laboratory validation of CVE-2022-42475, a critical heap-based buffer overflow vulnerability…
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 0xdak/cve-2026-9198_exploit
Unauthenticated RCE exploit for Langflow OSS chaining auto_login JWT bypass with validate/code exec() to achieve remote command execution and reverse…
 remmons-r7/rapid7-cve-2026-15409
This repo contains a proof-of-concept exploit for CVE-2026-15409. It establishes non-root remote code execution on SonicWall SMA 1000 by implementing…