
FMD Android
 fmd-foss/fmd-android
Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…
android-securitydata-recoverydefensive-tools+3
529
fmd-foss/fmd-androidFind your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…
 lautarovculic/ioscpy
Now you can mirror and control your jailbroken iPhone over USB
 threatexpert/gonc
Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 richlegrand/bitbang-cli
Establish secure remote access to a machine with interactive shell, file transfer, and web proxy over end-to-end encrypted peer-to-peer WebRTC, using…
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
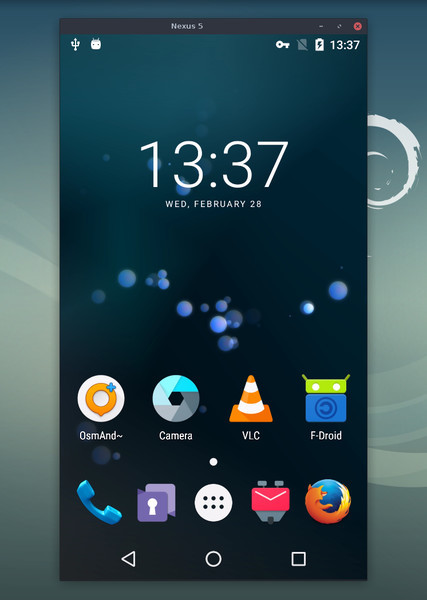 genymobile/scrcpy
Display and control your Android device
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 michaeladamgroberman/cve-2026-13768
CVE-2026-13768: Privileged iothubowner IoT Hub credential — fleet enumeration, device RCE, home-network pivot — Gardyn (ICSA-26-183-03)
 unnaim/adbhijacker
A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 redpack-kr/cve-2024-5243-pwn2own-toronto-2023
Pre-authentication Remote Code Execution exploit for TP-Link Omada ER605 router via DDNS client daemon (cmxddnsd)
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 entysec/ghost
Ghost Framework is an Android post-exploitation framework that exploits the Android Debug Bridge to remotely access an Android device.
 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 workabhiwin09/cve-2024-47176
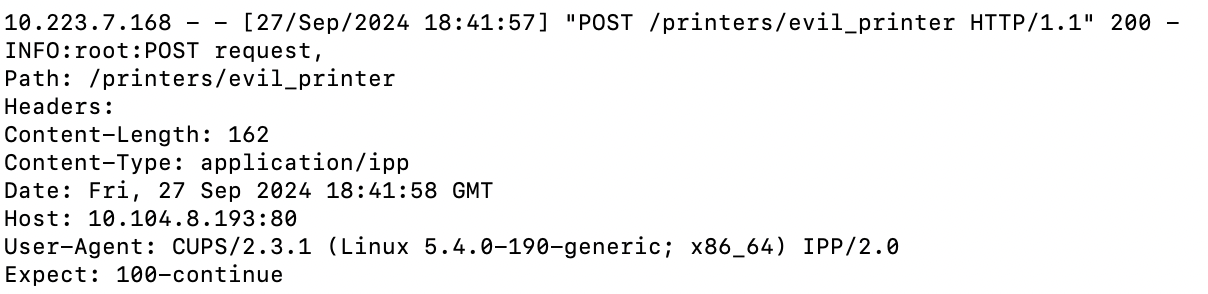
CUPS Browsd Check_CVE-2024-47176