
hiphp
 yasserbdj96/hiphp
PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…
command-and-controlpayload-generationremote-access-tool+1
225
yasserbdj96/hiphpPHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…
 showy-headteacher114/cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 mishaqdev/cve-2010-2075-analysis
Technical writeup and penetration testing report for CVE-2010-2075, demonstrating UnrealIRCd backdoor exploitation and remediation.
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 h4r335hr/vsftpd-234-backdoor
Dependency-free interactive Python exploit for the vsftpd 2.3.4 backdoor (CVE-2011-2523).
 byteforgefr/cve-2011-2523
VsFTPd 2.3.4 Backdoor Command Execution
 tc-xonor/cve-2010-2075
CVE-2010-2075 exploit
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
 haxrob/bpfdoor-controller-source
Source code for a BPFDoor backdoor controller supporting TCP, UDP, ICMP, and HTTPS covert communication channels with magic packet activation,…
 brettsm/vsftpd2.3.4-backdoor-exploit
vsftpd 2.3.4 Backdoor Exploit (CVE-2011-2523)
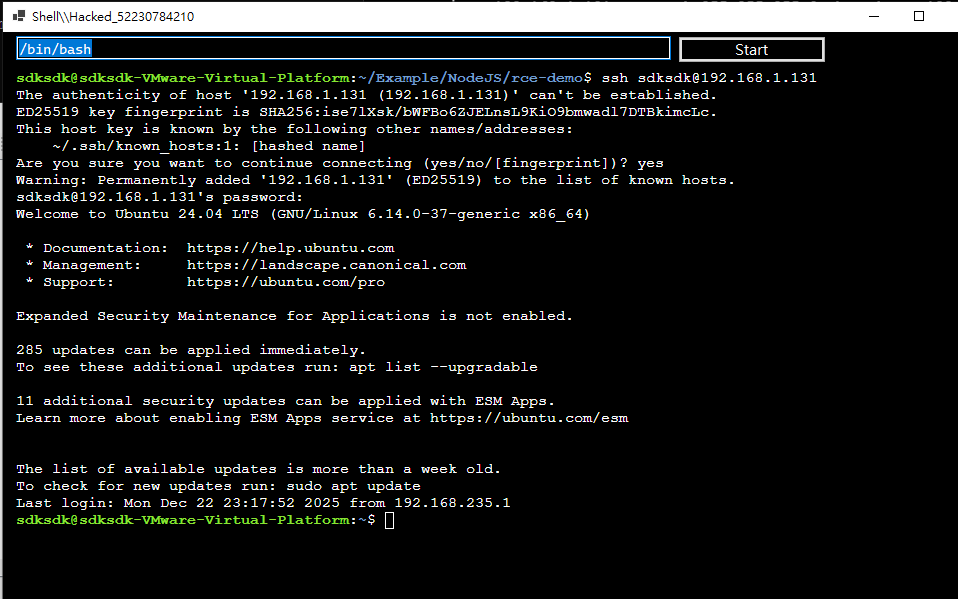 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
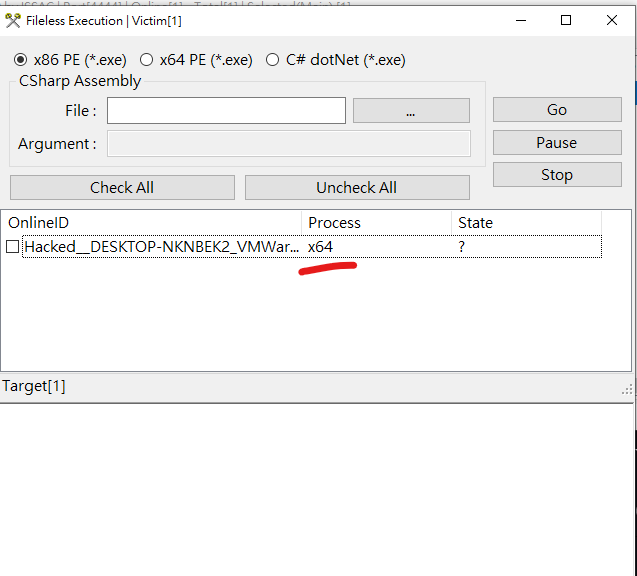 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
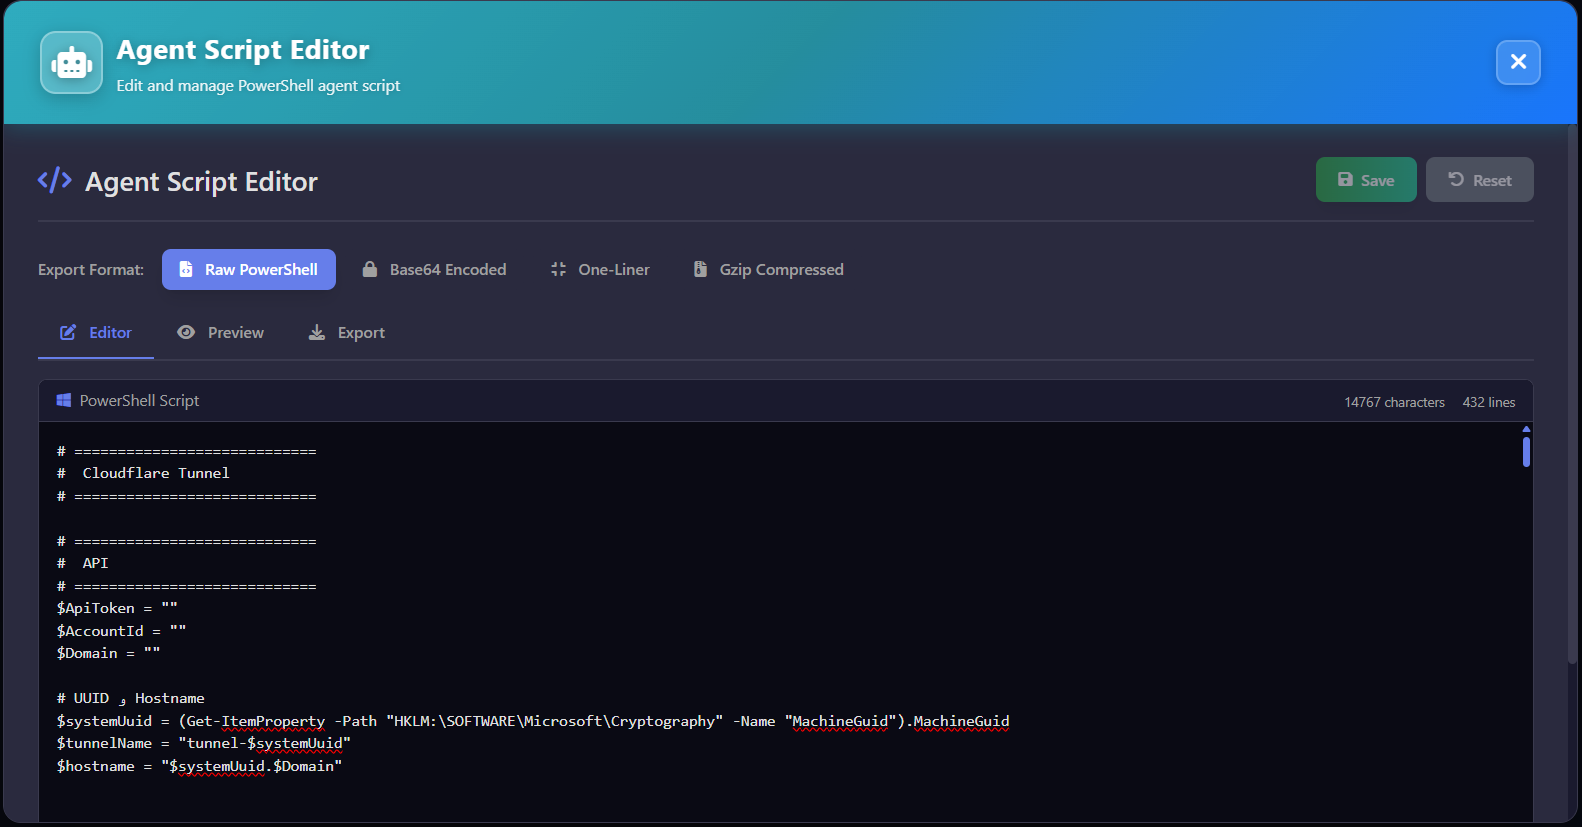 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 useru1k/php-8.1.0-dev-exploit
Exploit for the PHP 8.1.0-dev backdoor vulnerability (CVE-2021-21707)
 diego-tella/codeine
Linux LKM Rootkit
 bolivarj/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution