
FreeRDP
 freerdp/freerdp
FreeRDP is a free remote desktop protocol library and clients
authentication-authorizationencryption-decryption-toolsnetwork-security+2
13.7k
freerdp/freerdpFreeRDP is a free remote desktop protocol library and clients
 pomerium/pomerium
Identity-aware reverse proxy that delivers zero-trust access to internal apps and services via context-aware policy, continuous verification, and no…
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 warp-tech/warpgate
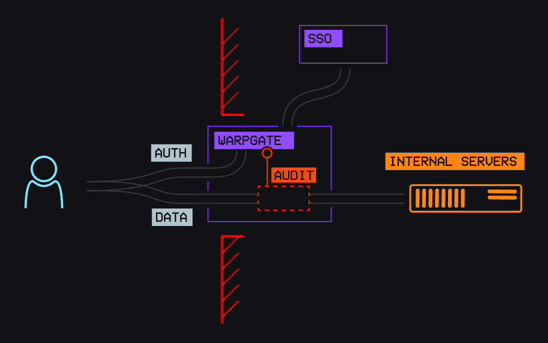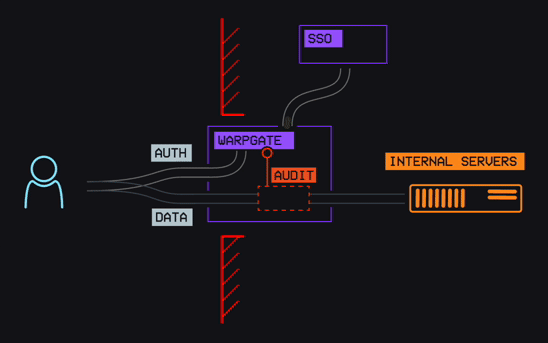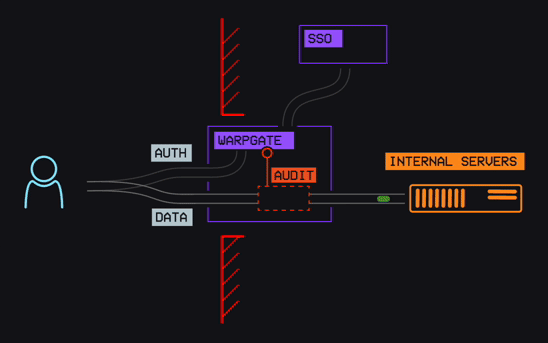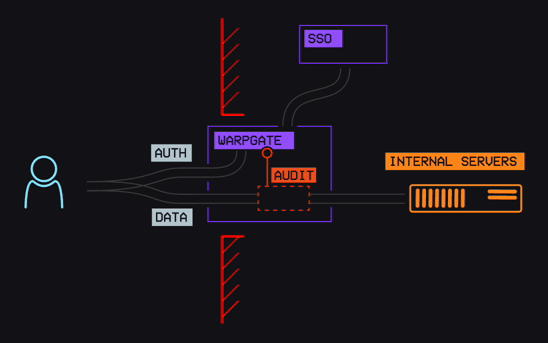
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
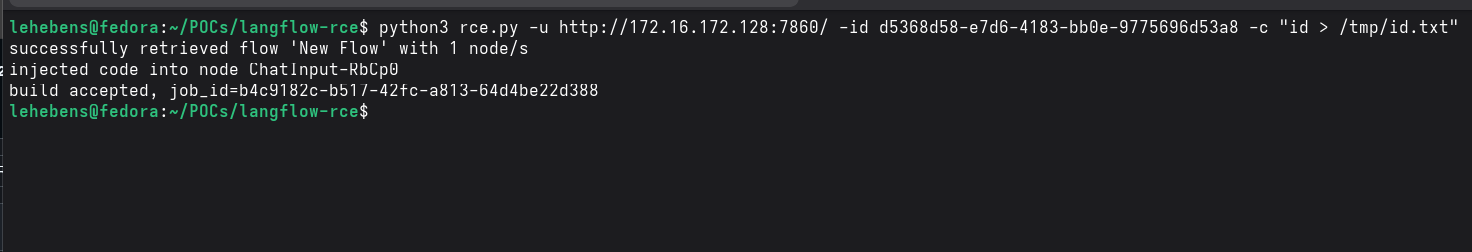 lukehebe/ibm-langflow-cve-2026-48519-poc
Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.

 openvpn/openvpn
Secure tunneling daemon implementing VPN protocols with TLS encryption, certificate authentication, and routing/firewall configuration for private…
 openssh/openssh-portable
Portable OpenSSH
 pritunl/pritunl
Provides distributed enterprise VPN connectivity using OpenVPN, with centralized management, authentication, and encrypted tunnels for cloud and…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 bastillion-io/bastillion
Bastillion gives you a clean, browser-based way to manage SSH access across all your systems—like a bastion host with a friendly dashboard.
 yasserbdj96/hiphp
PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…
 rh33t/cve-2026-33439-poc
PoC for CVE-2026-33439, a pre-auth RCE in OpenAM via unsafe Java deserialization.
 mfahdk/cve-2026-39987_rce_poc
Python proof-of-concept for CVE-2026-39987, exploiting an unauthenticated WebSocket terminal endpoint to achieve remote command execution and reverse…
 showy-headteacher114/cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.
 arensballiu/cve-2026-33017-langflow-rce
Proof-of-concept for CVE-2026-33017, demonstrating unauthenticated remote code execution in vulnerable Langflow versions through malicious…