
CVE-2026-104826
 kiwknr/cve-2026-104826
Proof-of-concept exploit chain for CVE-2026-104826, a path traversal in DropzoneFileExplorer's chunked upload handler that writes a PHP webshell for…
exploitationpenetration-testingremote-access-tool+3
1
kiwknr/cve-2026-104826Proof-of-concept exploit chain for CVE-2026-104826, a path traversal in DropzoneFileExplorer's chunked upload handler that writes a PHP webshell for…
 heapframe/seetong-ts81xxd3x-rce
CVE-2026-100886 | Unauthenticated Remote Code Execution toolkit.
 wvllxe/cve-2026-100520-laranode-path-traversal
Path Traversal -> RCE in Laranode < 1.2.1 (CWE-22). PoC + advisory writeup.
 murrez/cve-2026-13249
Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…
 yym8538/cve-2026-21858
Docker-based PoC environment and exploit script for CVE-2026-21858, an n8n 1.120.4 arbitrary file read and RCE flaw, providing secret extraction and…
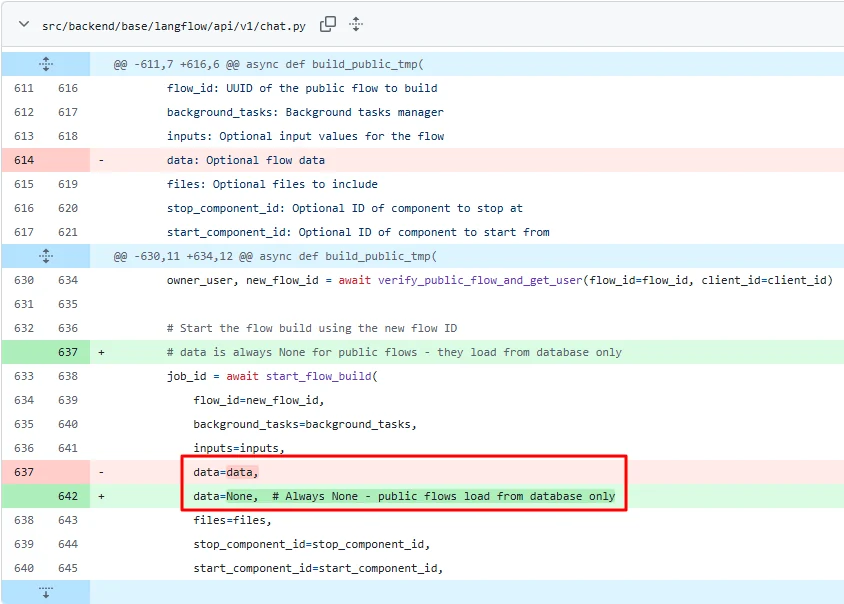 yym8538/cve-2026-33017
Proof-of-concept exploit for CVE-2026-33017, an unauthenticated RCE in Langflow's build_public_tmp endpoint, injecting a malicious custom component…
 k3ystr0k3r/metis
Modular Python exploitation framework with a Metasploit-style console, auto-registering Exploit and Auxiliary modules, tri-state checks, and multiple…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 eqstlab/cve-2026-49869
PoC and Docker lab for CVE-2026-49869, an unauthenticated RCE in Kestra OSS via an AuthenticationFilter path bypass that allows flow creation and…
 eqstlab/cve-2026-6951
Proof-of-concept exploit for CVE-2026-6951, a simple-git --config filter bypass enabling RCE via the Git ext protocol, with a Docker lab and reverse…
 yym8538/cve-2026-40897
Proof-of-concept exploit for CVE-2026-40897, a Math.js expression parser sandbox bypass enabling remote code execution via crafted payloads and a…
 laarana12/cve-2026-39987-marimo-preauth-rce
Reproduction and root cause analysis of CVE-2026-39987 Marimo pre-auth WebSocket RCE in a local Docker lab.
 dennisdgr/cve-2026-44011-poc
Authenticated Craft CMS RCE PoC for CVE-2026-44011
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88772
Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88771
Detection artifact generator for Citrix NetScaler CVE-2026-88771, exploiting a pre-auth command injection to achieve remote code execution against…
 yym8538/cve-2026-5027
Proof-of-concept exploit for CVE-2026-5027, a path traversal and arbitrary file write in Langflow's /api/v2/files endpoint, with Docker lab and…
 crowsec-edtech/cve-2026-87902
Python PoC exploiting CVE-2026-87902, an unauthenticated path traversal in WordPress locate_template() leading to LFI and PEAR-based RCE, with safe…
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.