CVE-2026-21962_Java_GUI_Exploit_Tool

Java GUI tool for exploiting CVE-2026-21962, an unauthenticated RCE in Oracle WebLogic Proxy Plug-In, enabling multi-target command execution via…

Java GUI tool for exploiting CVE-2026-21962, an unauthenticated RCE in Oracle WebLogic Proxy Plug-In, enabling multi-target command execution via…

Identity-aware reverse proxy that delivers zero-trust access to internal apps and services via context-aware policy, continuous verification, and no…

Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level

Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software

DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…

Establish secure remote access to a machine with interactive shell, file transfer, and web proxy over end-to-end encrypted peer-to-peer WebRTC, using…

Socks5/4/4a Proxy support for Remote Desktop Protocol / Terminal Services / Citrix / XenApp / XenDesktop

A SOCKS proxy for Citrix.

GUI-based exploit tool for CVE-2020-14882 targeting Oracle WebLogic servers. Supports reverse shell payload generation, proxy configuration, and…

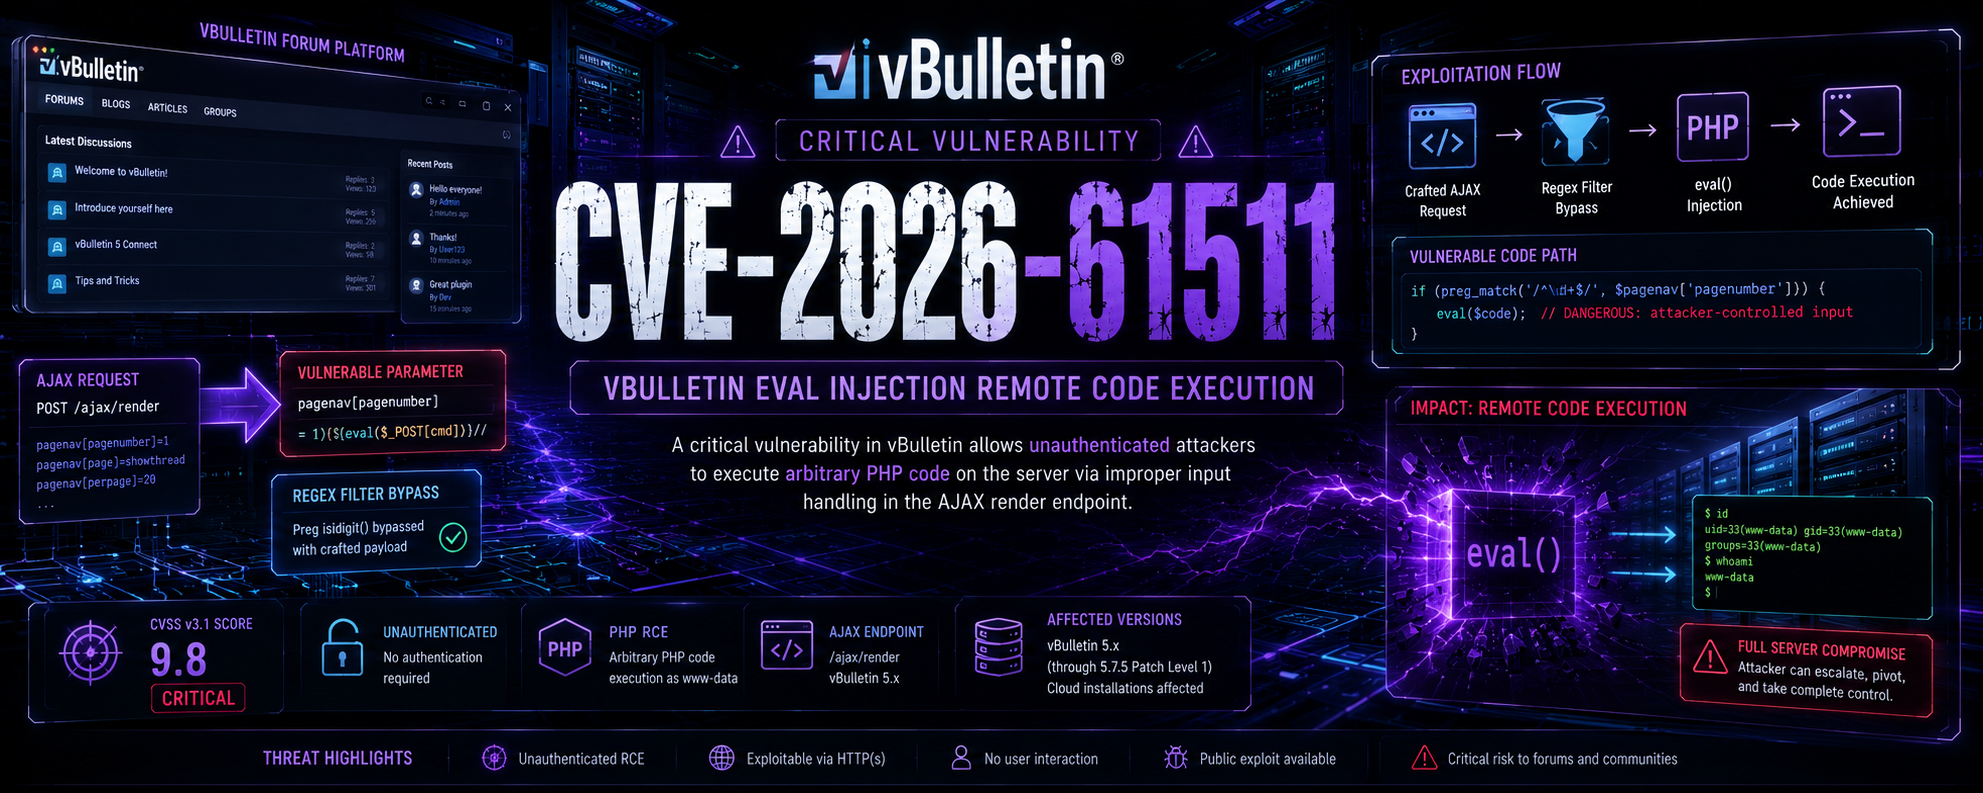
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…

Authenticated Remote Command Execution - Webmin <= 1.910

Pre-authentication remote code execution exploit for React Server Components and Next.js via deserialization vulnerability. Supports single-target…

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…

Wrong project! You should head over to http://github.com/sshuttle/sshuttle

Powershell C2 Server and Implants

Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…

Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…

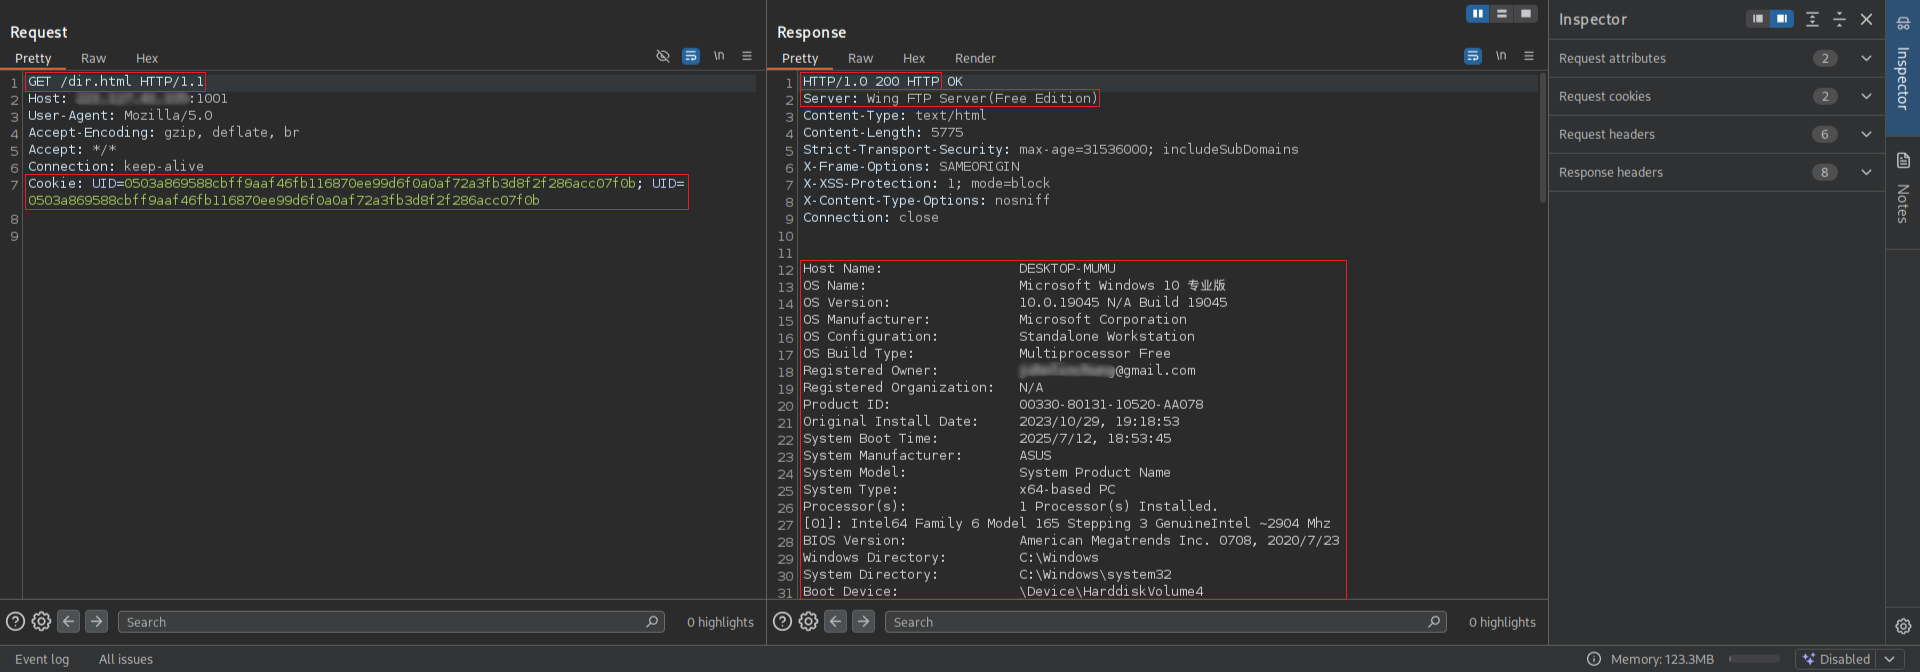
Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…