
Project-CVE-2026-33017
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
command-and-controlexploitationpayload-development+6
1
e4zyy/project-cve-2026-33017CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 eladshamir/rpc-backdoor
A basic emulation of an "RPC Backdoor"
 darkcodersc/subseven
SubSeven Legacy Official Source Code Repository
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
 samyk/poisontap
Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…
 mbadanoiu/java-servlets-shell
JSP-less Java Servlets Backdoor inspired by https://www.redteam-pentesting.de/files/redteam-jboss.tar.gz
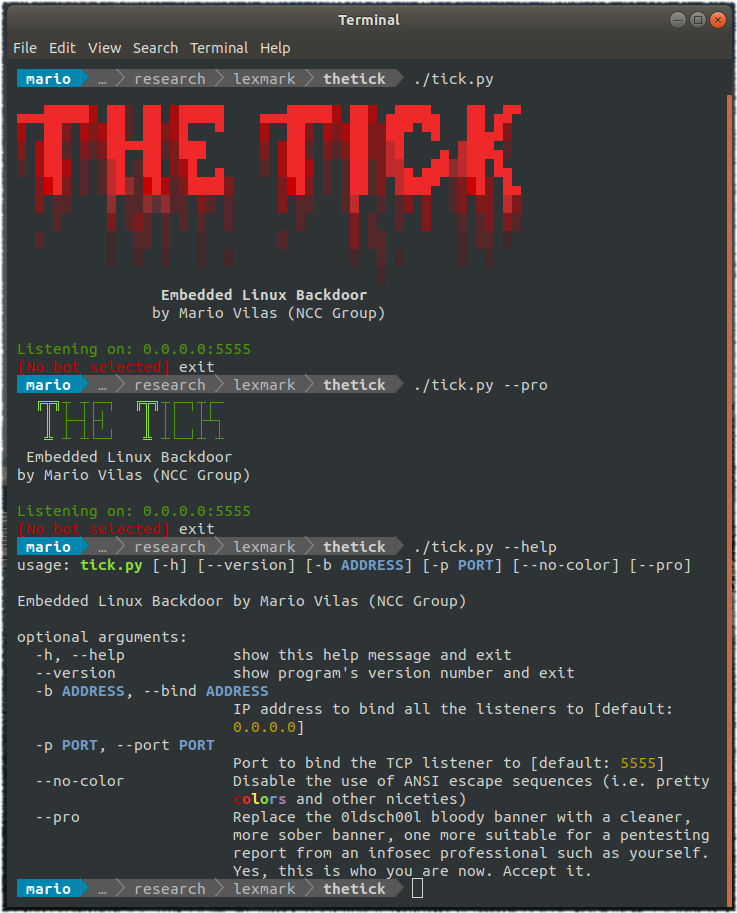 nccgroup/thetick
A simple embedded Linux backdoor.
 synacktiv/ccmmessagingbackdoor
Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.
 coldfusionx/php-8.1.0-dev_webshell-rce
PHP 8.1.0-dev WebShell Remote Code Execution
 flast101/php-8.1.0-dev-backdoor-rce
PHP 8.1.0-dev Backdoor System Shell Script
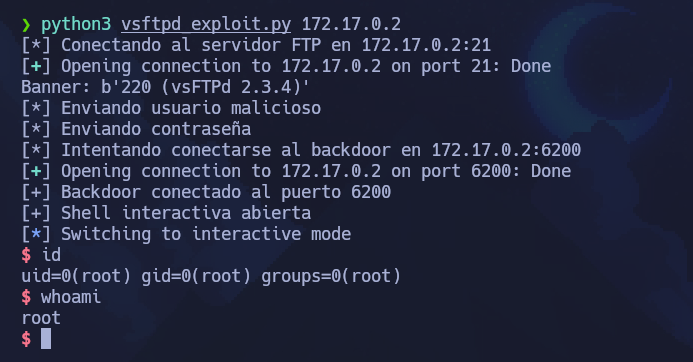 lychi3/vsftpd-backdoor
Exploit hecho en python para vsftpd 2.3.4 | CVE-2011-2523
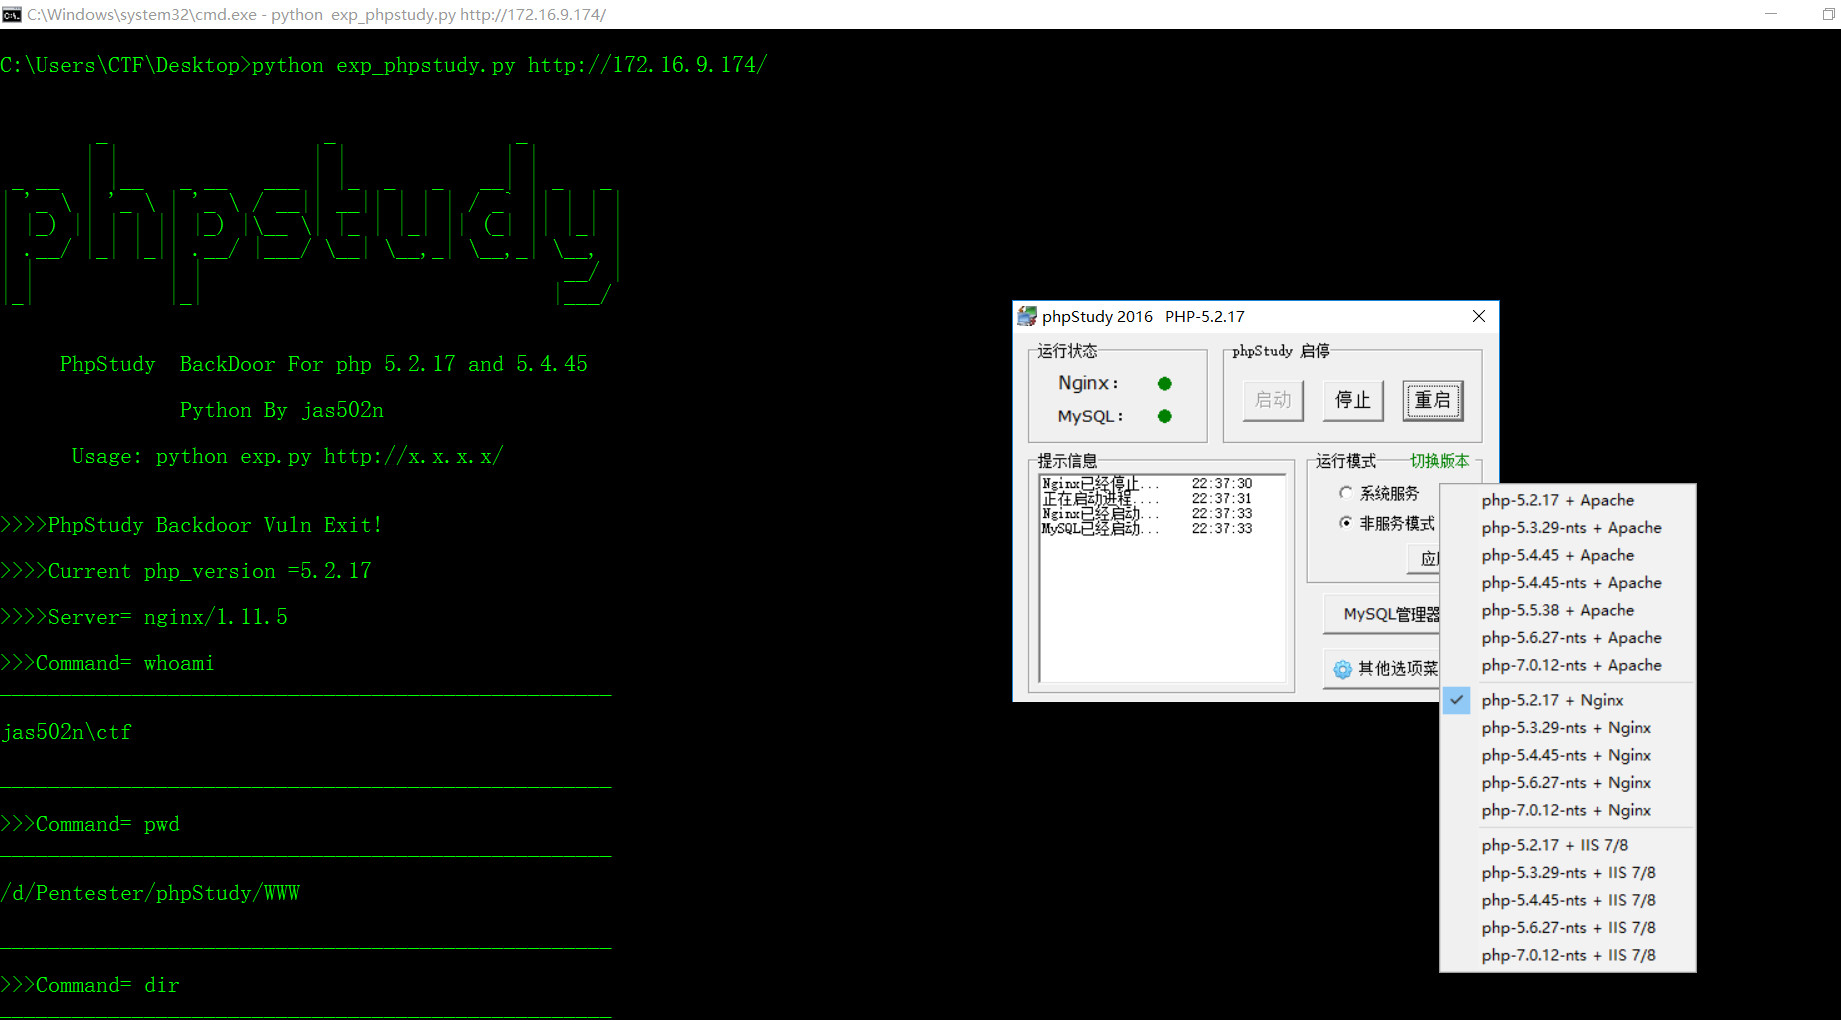 jas502n/phpstudy-backdoor
phpstudy dll backdoor for v2016 and v2018
 nccgroup/sshession
The SSH Multiplex Backdoor Tool
 diego-tella/codeine
Linux LKM Rootkit
 infodox/tsh-sctp
TinySHell port to SCTP