

CVE-2026-48907
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
exploitationpayload-developmentpenetration-testing+6
noname-elv/cve-2026-48907Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
 ull0a/cve-2026-50751
Bypass de autenticación por certificado en la VPN Remote-Access de Check Point (IKEv1).
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 aboubacar70/lab1-metasploitable
Exploitation des vulnérabilités sur la version vsftpd 2.3.4 du service ftp (CVE-2011-2523)
 mki9/cve-2026-39987_exploit
Exploit for Marimo pre-auth RCE via WebSocket auth bypass, providing interactive shell access on affected versions.
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
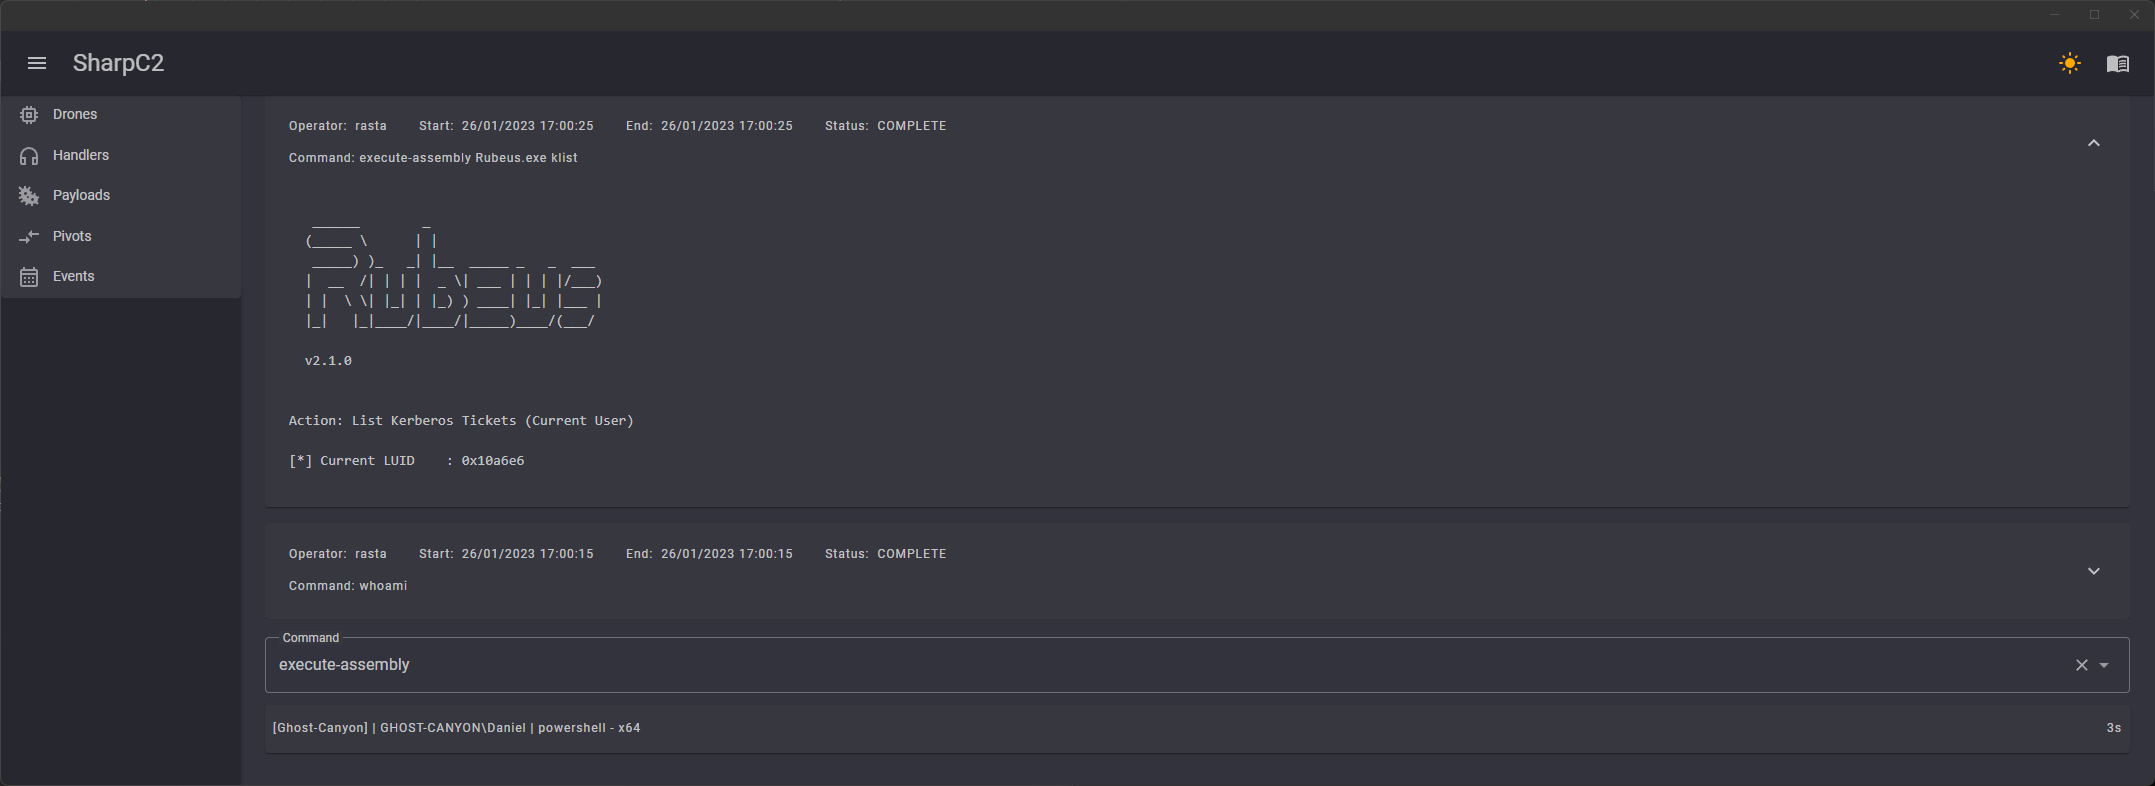 rasta-mouse/sharpc2
Command and Control Framework written in C#
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 frostsaberx/cve-2019-0708
CVE-2019-0708 With Metasploit-Framework Exploit
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
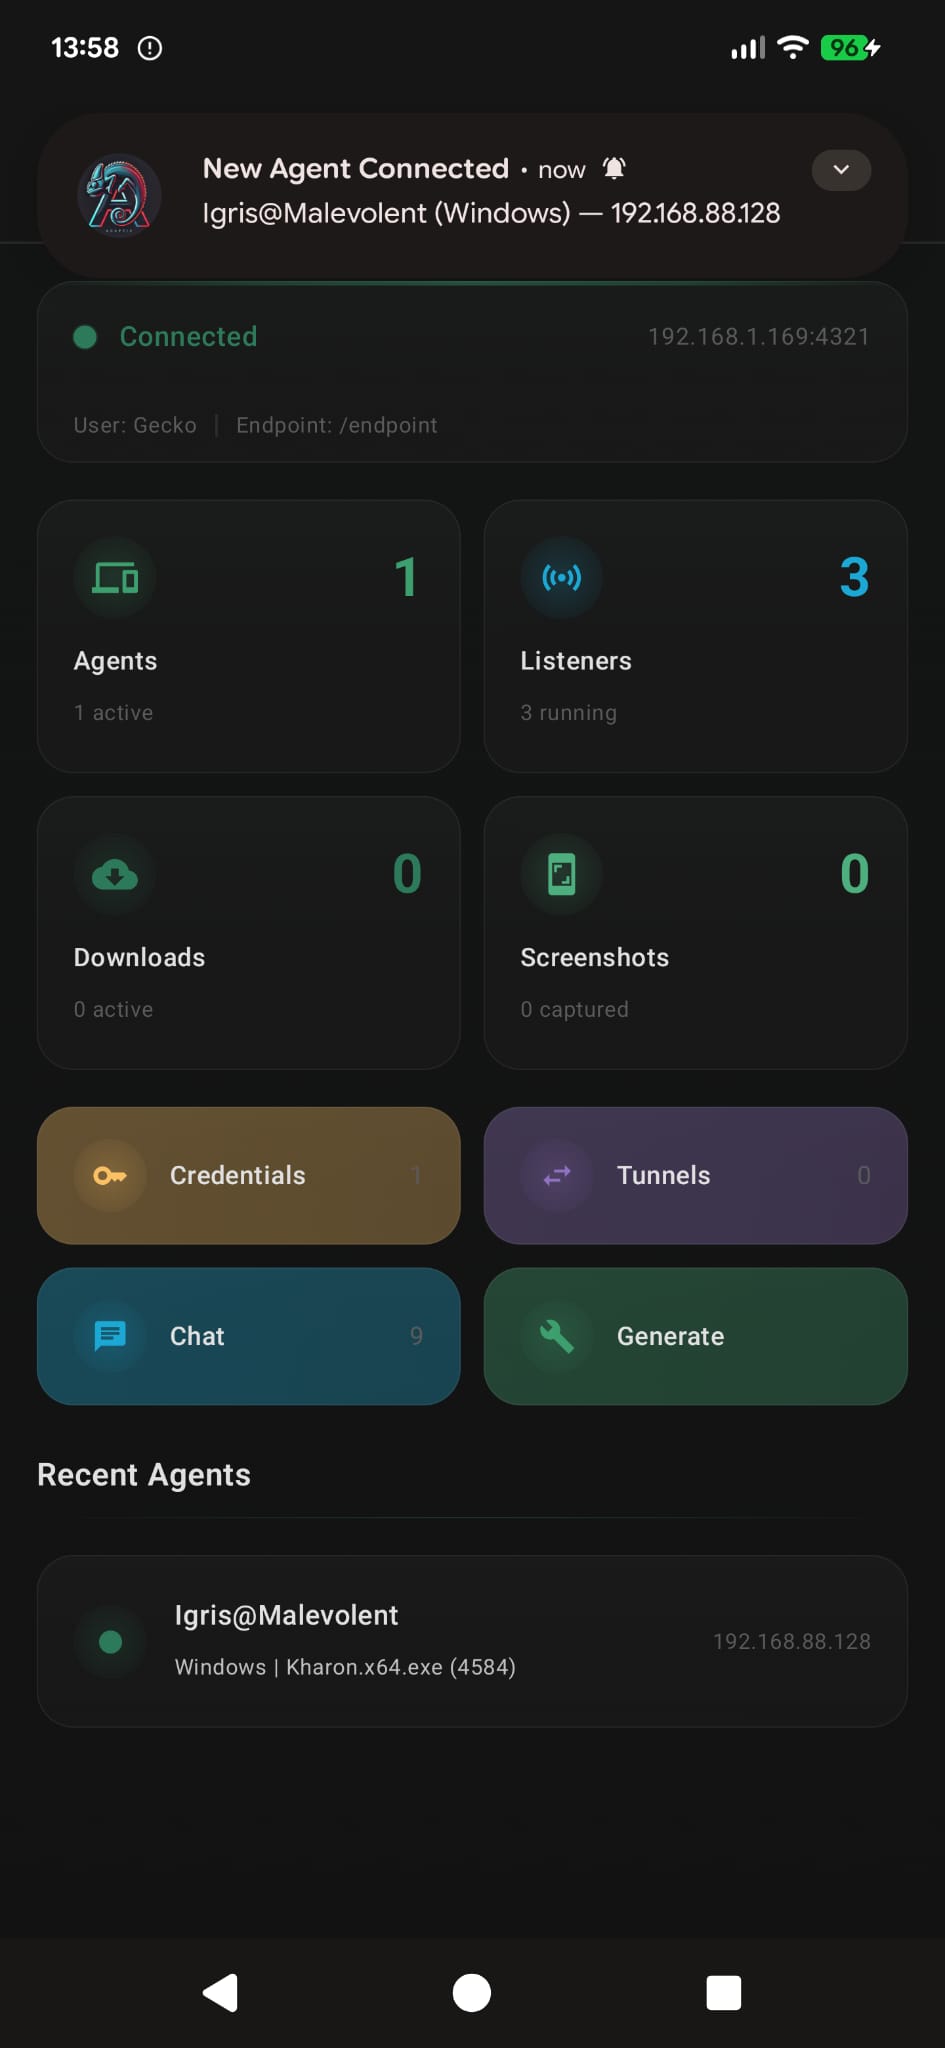 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…