samsung_tizen_tv_root

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

Small, portable embeddable SSHv2 client and server library in C with SCP, SFTP, port forwarding, and post-quantum key exchange for embedded and IoT…

CVE-2026-100886 | Unauthenticated Remote Code Execution toolkit.

Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…

Python proof-of-concept scripts for the MikroTrick MikroTik RouterOS SSH takeover chain (CVE-2026-67279, CVE-2026-86060, CVE-2026-67276) for…

Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…

Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…

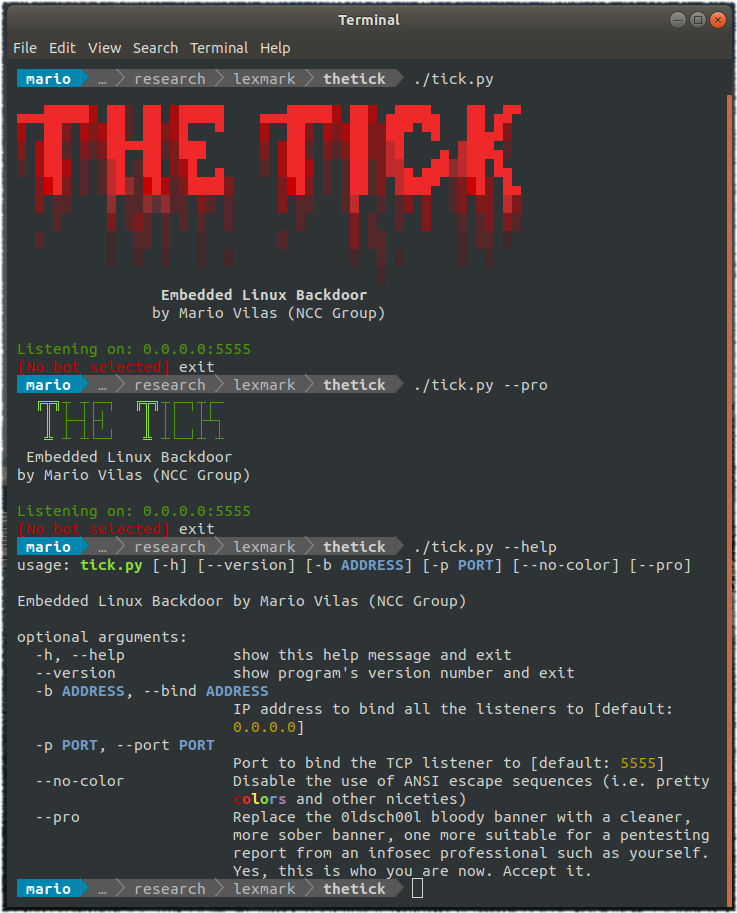
A simple embedded Linux backdoor.

Final OBJECTIVE:BIOS ROOTKIT AND RSHELL USING BIOS NETWORKING STACK

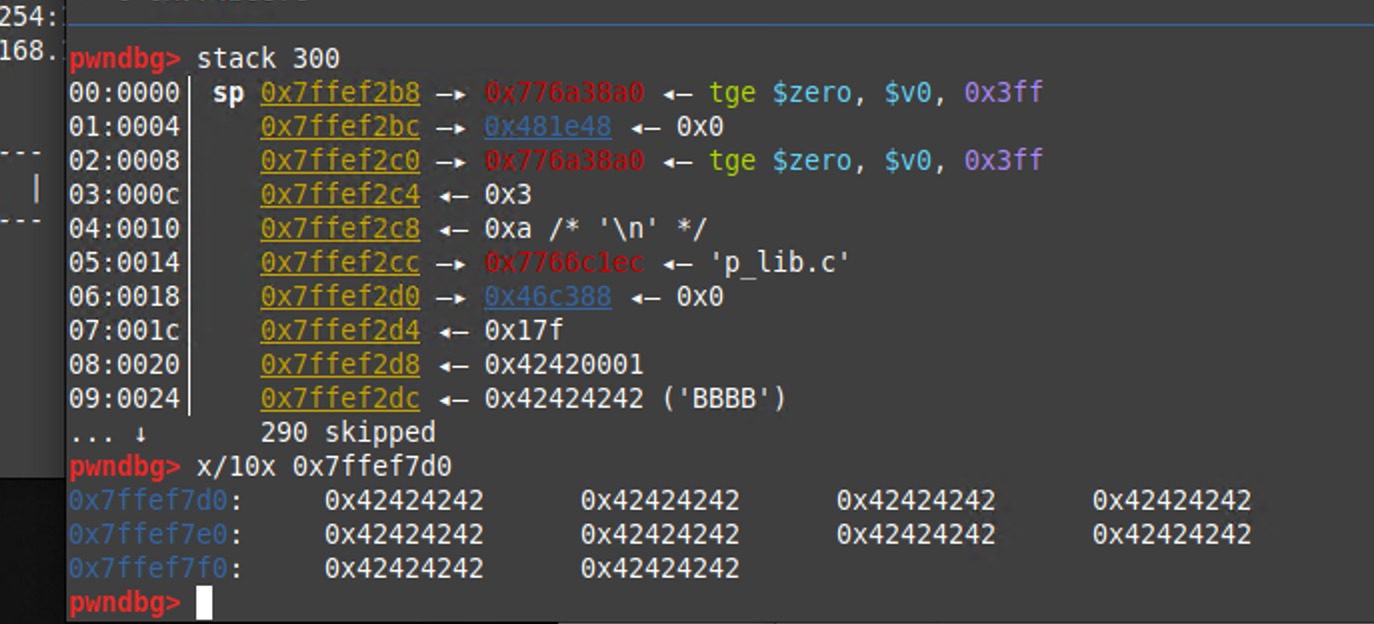
Exploit used against the Netgear R6700v3 during Pwn2Own Austin 2021

Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)

This is POC of CVE-2024-29671

Exploits for Tenda Ac8v4 stack-based overflow to Remote-Code Execution via Mipsel Ropping (CVE-2023-33669 - CVE-2023-33675)

Here is the CVE-2025-65817

CVE-2026-38422 — Remote Code Execution via Combined Buffer Overflows in Tasmota fetch_jpg() (Tasmota <= 15.3.0.3)

CVE-2026-13768: Privileged iothubowner IoT Hub credential — fleet enumeration, device RCE, home-network pivot — Gardyn (ICSA-26-183-03)

Exploit for TP-Link AX10/AX1500 stack buffer overflow in CWMP (TR-069) enabling remote code execution via ret2libc with ASLR bypass. Includes…

CVE-2025-57174 Unauthenticated Remote Command Execution